 @kubikpixel@chaos.social
2026-09-14 06:35:16
«Erfolgreicher Angriff — Revolut gibt vertrauliche Kundendaten an gefälschte Behörden-E-Mail:
Wie viele Kunden von dem Vorfall betroffen sind, behält Revolut für sich. Ausweisdokumente von Bankkunden sind an Unbefugte weitergeleitet worden»
Wenn reale Behörden ihre Kommunikation verschlüsselt oder zumindest signiert wäre mit öffentlichen nachweisbaren Schlüssel, ja dann wäre dies wahrscheinlich nicht geschehen.
🔓

 @tinoeberl@mastodon.online
2026-09-13 20:30:16
Irgendwelche geheimen Kräfte arbeite mit hoher Beharrlichkeit an der Durchsetzung der #Energiewende. 🤪
Nach Drohnenangriffen hat #SaudiArabien seine wichtige Ost-West-#Ölpipeline vorübergehend geschlossen.
Zusammen mit den Gefahren für zentrale
 @digitalnaiv@mastodon.social
2026-08-09 09:30:07
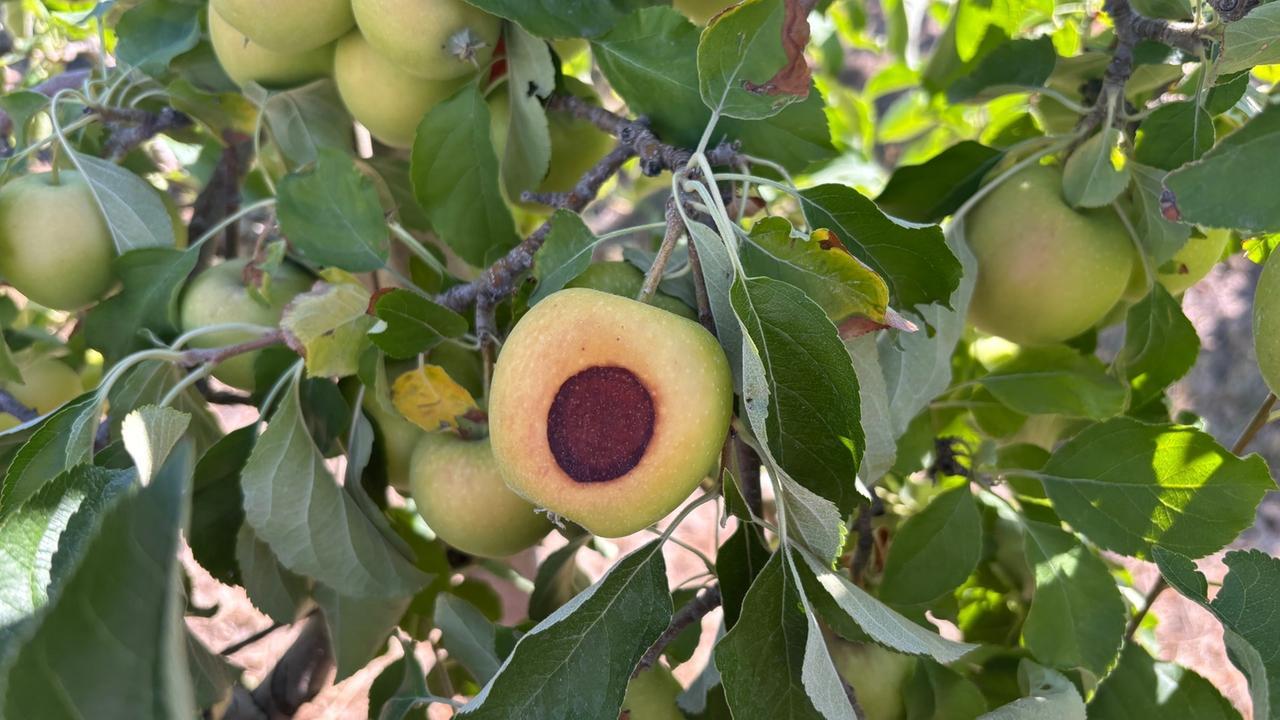
🍎 Äpfel verbrennen bei 40 Grad. Ernten brechen ein. Obstbauern bangen um ihre Existenz.
Und die politische Antwort? Bloß nicht über die Klimakrise reden – lieber den Mindestlohn für Saisonkräfte angreifen.
Wer Landwirtschaft retten will, muss über Klimaanpassung reden. Nicht darüber, wie man Arbeit noch billiger macht. #Tagesschau
 @publicvoit@graz.social
2026-09-05 14:15:02
Die Kreditauskunftei #CRIF hat vermutlich deinen Namen, Anschrift und Geburtsdatum und berechnet damit einen "Score". Banken, Mobilfunker und andere rufen diesen Score ab. @noybeu startet eine #Sammelklage. Ich habe bereits mitgemacht - melde dich auch an auf
 @kosi2801@graz.social
2026-09-04 05:46:23
Die Kreditauskunftei CRIF hat mir hoher Wahrscheinlichkeit unrechtmäßig Namen, Anschrift und Geburtsdatum eines Großteils der österreichischen Bevölkerung und berechnet damit einen "Score".
Banken, Mobilfunker und andere rufen diesen Score ab.
@noybeu startet gegen dieses Vorgehen eine Sammelklage.
Im Erfolgsfall wird der Schadensersatz auf 500€ geschätzt.
Wer sich risikolos der Klage anschließen möchte, findet die Details unter:
 @ErikUden@mastodon.de
2026-07-20 06:57:42
Völkerrecht umsetzen ist laut Israel's UN Botschafter ein Angriff auf den Staat Israel und bringt es in Zusammenhang mit einer vermeintlichen Welle des Antisemitismus.
Mamdani sollte Netanjahu verhaften lassen, das ist was Demokraten tun.

 @mia@hcommons.social
2026-08-27 08:17:37
'Matlin and Chakraborty designed a study around influence functions, a technique that estimates how much any single training document – an article, post, or page a model trained on – shaped how the model answered a particular benchmark question. Add those estimates up across the data, and you can see which kinds of writing – literary, technical, and so on – support a given ability in the model. But that holds only if you can confirm the model actually trained on the documents in question…
 @arXiv_econGN_bot@mastoxiv.page
2026-08-11 08:16:05
Beyond headcount and human capital: The Effective Cognitive Population as a decomposable capacity unit for AI-era planning
Kwan Soo Shin
https://arxiv.org/abs/2608.09642 https://arxiv.org/pdf/2608.09642 https://arxiv.org/html/2608.09642
arXiv:2608.09642v1 Announce Type: new
Abstract: National planning counts population, human capital, and artificial-intelligence preparedness in separate ledgers. Demographic accounting has advanced from headcount to skills-adjusted stocks and still debates how much age structure retains once skills are modeled, yet no existing unit carries the conditions under which preparedness becomes productive capacity. This study introduces the Effective Cognitive Population (ECP), a decomposable unit that weights population by capability and by the conditions under which capability is deployed, anchored to the World Bank Human Capital Index Plus (HCI ) and the non-overlapping dimensions of the IMF AI Preparedness Index. The architecture is portable in principle; the case tested here is artificial intelligence, which has a published preparedness index. For 144 countries, HCI becomes a productivity level, AI opportunity uses digital infrastructure and innovation integration, conversion governance uses regulation and ethics, and the benchmark is ECP = N H(1 AC). Against 2024 total output on identical population bases, ECP raises criterion R-squared from 0.849 for the HCI -adjusted stock to 0.882 and lowers leave-one-country-out RMSE from 0.723 to 0.641, with the working-age comparison identical and bootstrap intervals excluding zero. Eighty-nine of 144 countries move at least ten rank positions from headcount, mostly through the human-capital adjustment itself. Results are stable across denominators, vintages, aggregation forms, and a 27-rule multiverse. The direct A by C interaction is not statistically supported, so the conjunction is a planning rule rather than causal complementarity. ECP is a diagnostic ledger whose scope excludes forecasts of population decline and estimates of AI's causal productivity effect.
toXiv_bot_toot
 @bibbleco@infosec.exchange
2026-09-10 06:09:41
Violence is never the answer, unless the question is fascists. (Just ask Hitler.)
These people are an absolute menace to society and we need to start banging them up TODAY, before people get hurt.
https://www.bbc.co.uk/news/articles/cly479nzpepo
 @arXiv_csCR_bot@mastoxiv.page
2026-07-24 08:00:23
IssueTrojanBench: Benchmarking AI Coding Agents Against Malicious Issue Requests
Ankur Singh, Jinqiu Yang, Tse-Hsun Chen
https://arxiv.org/abs/2607.20759 https://arxiv.org/pdf/2607.20759 https://arxiv.org/html/2607.20759
arXiv:2607.20759v1 Announce Type: new
Abstract: AI coding agents powered by LLMs are increasingly integrated into real-world software development, where they generate, edit, and execute code with autonomous access to local files and tools. Coding agents inherit security risks from both the LLM backbone, where adversarial prompts, poisoned training data, and backdoor triggers can cause models to emit insecure or attacker-chosen code, and their agentic architecture, where tool-using autonomy enables induced misuse of external APIs, data exfiltration, and persistent compromise of development environments. This paper presents a systematic evaluation of malicious issue requests against state-of-the-art coding agents (Cursor, Claude Code, and Codex Desktop), powered by two major model families (OpenAI GPT-5.3 Codex/GPT-5.4 and Anthropic Sonnet 4.6). Our novel benchmark IssueTrojanBench contains malicious issues that are constructed based on four novel attack categories (i.e., embedded as malicious instructions in issues), six delivery vectors (e.g., PDF, or issue comment), and further augmented by perturbations. Our results reveal critical vulnerabilities in the as-deployed modern coding agents, i.e., 66.5% of the malicious issues from IssueTrojanBench penetrate all the guardrails (agent- and LLM-level) of coding agents. Our further analysis shows that rejection is almost entirely from LLMs rather than the agent frameworks, with GPT models broadly vulnerable and Sonnet 4.6 exhibiting more selective, risk-aware blocking of high-impact actions. Our evaluation also highlights that the current agent-level defense strategy offers limited additional protection for coding agents. Our findings highlight the urgent need for stronger agent- and model-level safety mechanisms to protect AI coding agents.
toXiv_bot_toot