 @fanf@mendeddrum.org
2026-08-05 17:42:04
from my link log —
Don't stop early: Case-folding source code at memory speed.
https://github.blog/engineering/architecture-optimization/dont-stop-early-case-folding-source-code-at-memory-speed/
sa…
@fanf@mendeddrum.orgfrom my link log —
Don't stop early: Case-folding source code at memory speed.
https://github.blog/engineering/architecture-optimization/dont-stop-early-case-folding-source-code-at-memory-speed/
sa…
 @keithp@fosstodon.org
Found an issue with Risc-V ILP32E ABI in GCC today and am looking for guidance.
ILP32E stack need only be aligned to 4-bytes, however types wider than 4 bytes are listed as having wider alignment requirements in current GCC source.
So, when you take the address of an 8-byte value on the stack which is not 8-byte aligned and try to use it with -fsanitize=undefined, you get a UB fault.
Question: Is this a bug in ubsan? Or should all type alignment restrictions be relaxed unde…
 @maxheadroom@hub.uckermark.social
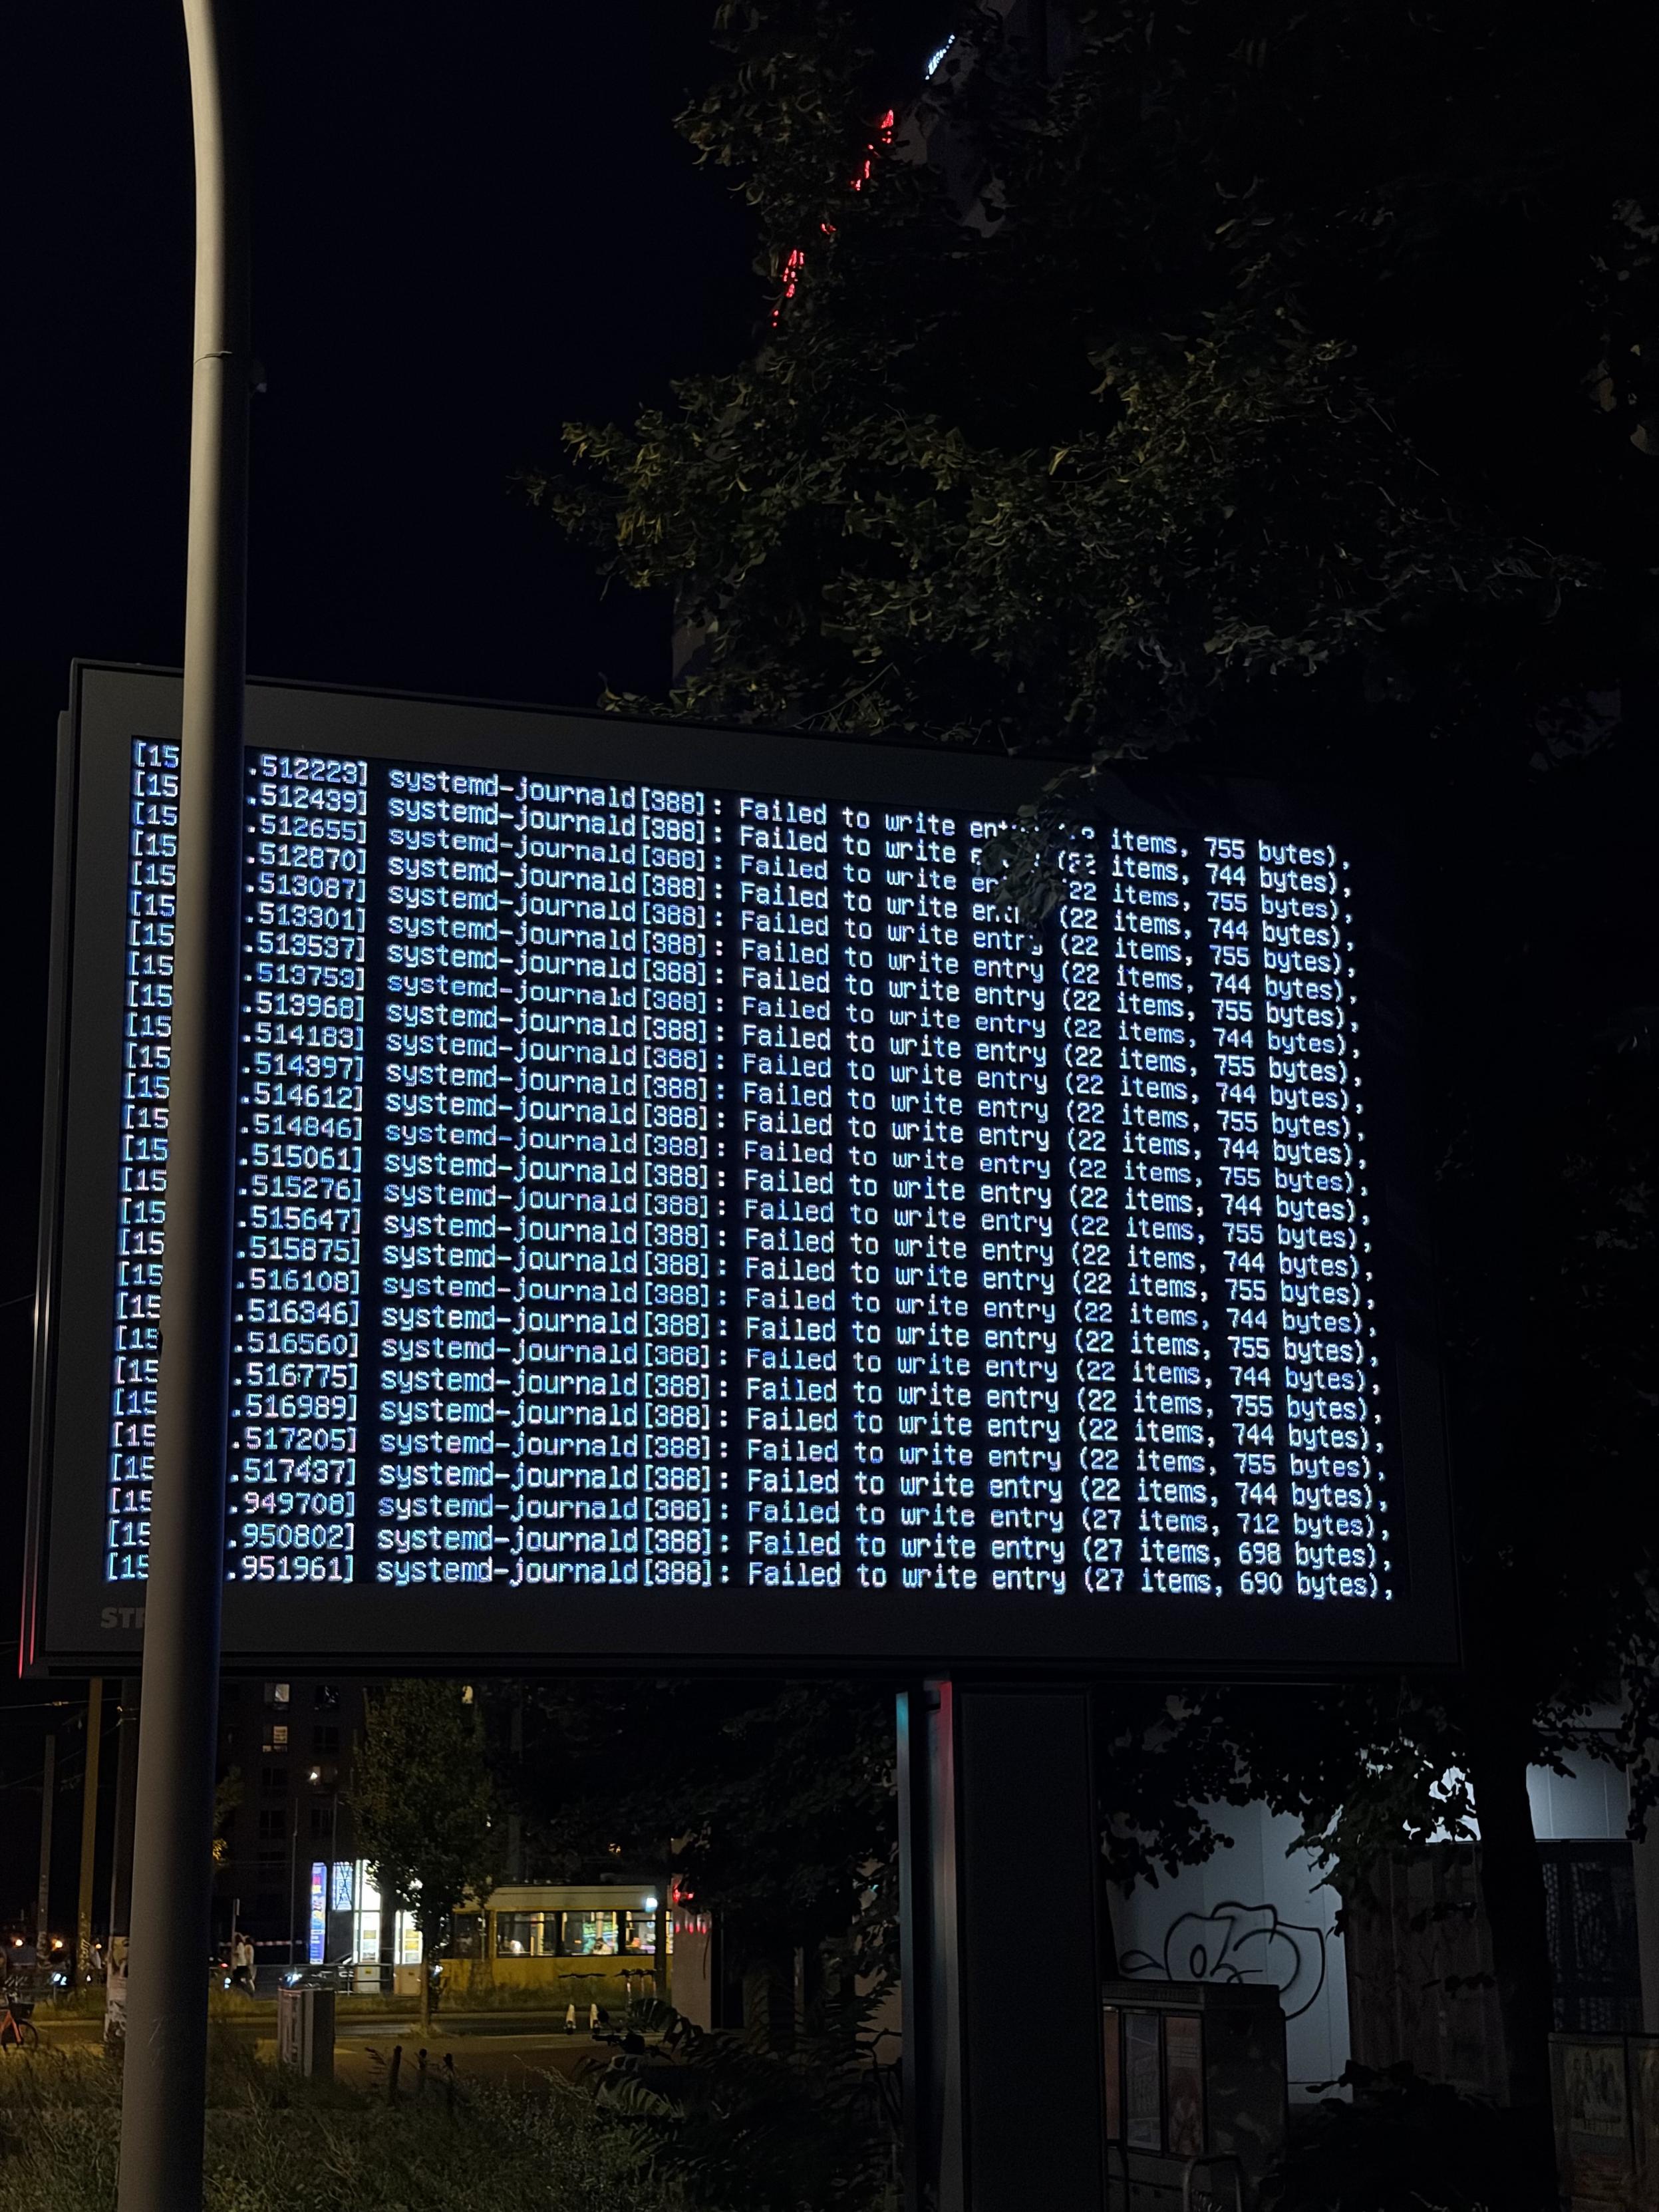
Linux is running large advertising campaigns now in Berlin #diday #dutgemacht #linux
 @jamesthebard@social.linux.pizza
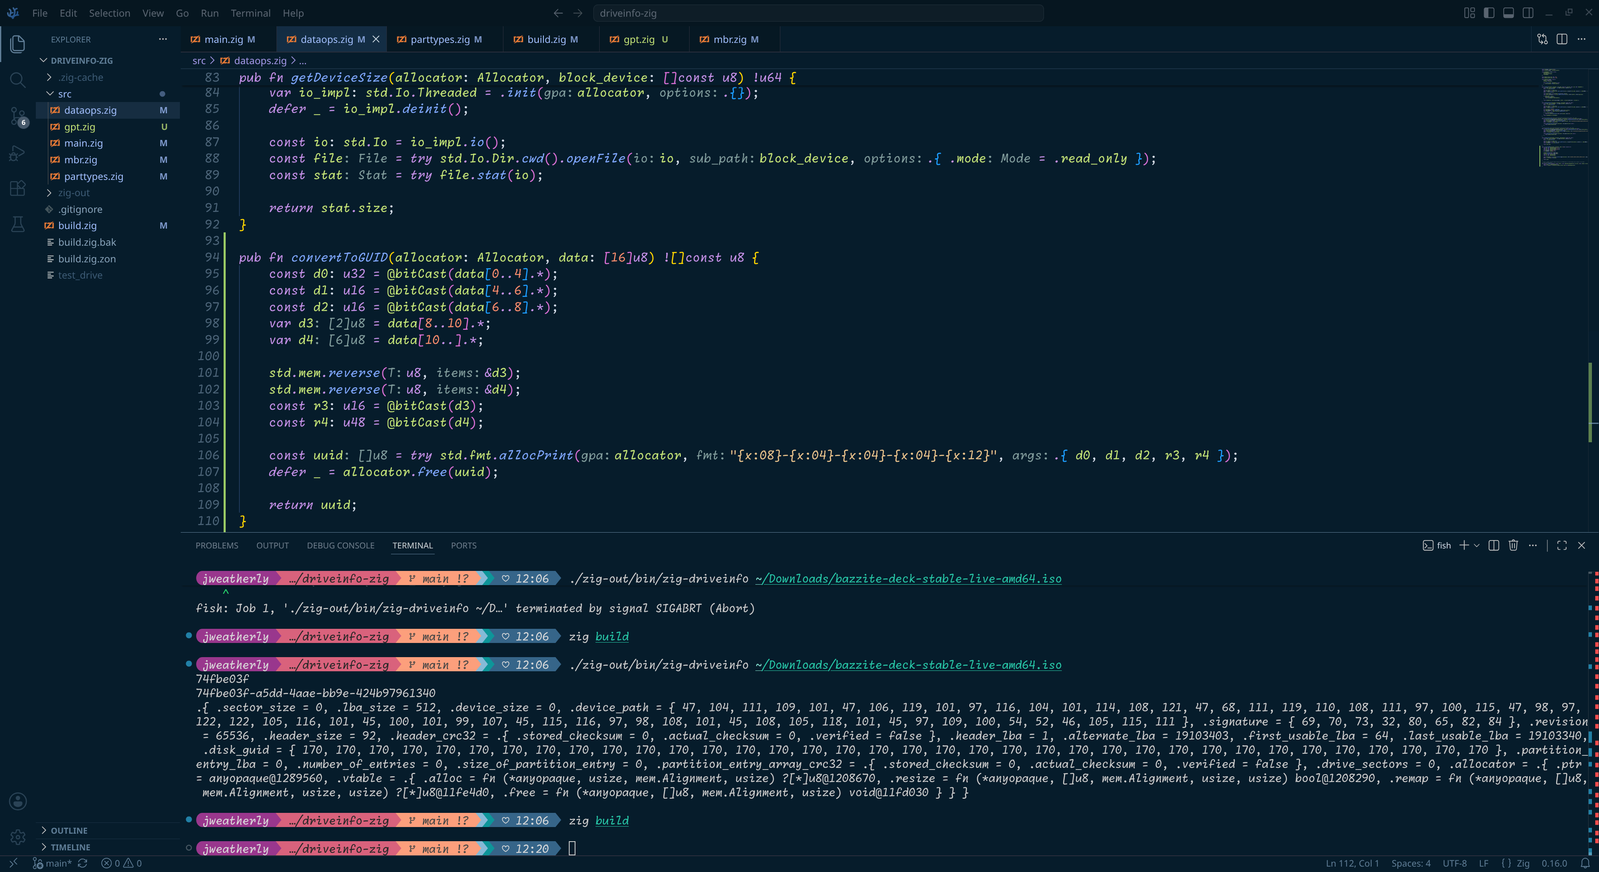
Sometimes, you just need a nice standard-sized unsigned integer of exactly 48 bits...also, I think I hate UUIDs.
#zig #programming
 @fanf@mendeddrum.org
from my link log —
Historical notes on computer word and byte sizes.
https://www.cs.columbia.edu/~smb/blog/2023-03/2023-03-07.html
saved 2023-03-08
 @pimterry@toot.cafe
Coming soon to a Node.js near you: a small issue I spotted on Friday and fixed with a tiny little change now makes every typical small API response with Node.js ~10% faster for free: https://github.com/nodejs/node/pull/65466 🚀
Specifically, this applies anywhere you do `res.end(string)`…
 @chiraag@mastodon.online
Mini Crossword Easy #60: Byte-Sized
⬛⬜⬜⬜⬛
⬜⬜⬜⬜⬜
⬜⬜⬜⬜⬜
⬜⬜⬜⬜⬜
⬛⬜⬜⬜⬛
30s | No reveals!
Top 20% time!
Play free at minicrossword.com/
 @arXiv_csCR_bot@mastoxiv.page
AuthProbe: Specification-Driven, Multi-Identity Detection of Broken Object-Level Authorization in Recruitment API
Jay Barach
https://arxiv.org/abs/2607.20574 https://arxiv.org/pdf/2607.20574 https://arxiv.org/html/2607.20574
arXiv:2607.20574v1 Announce Type: new
Abstract: Broken Object-Level Authorization (BOLA), also known as Insecure Direct Object Reference (IDOR), has topped the OWASP API Security ranking since 2019 and is the root cause of some of the largest exposures of applicant data in recruitment technology. The defining feature of this flaw class is that a malicious request is byte-for-byte indistinguishable from a legitimate one, which is precisely why web application firewalls and single identity scanners fail to catch it. We present AuthProbe, an open-source, black-box scanner that detects BOLA and IDOR in HTTP APIs by driving its tests from an OpenAPI specification and by acting under two or more identities that the operator controls. AuthProbe discovers, for each identity, the objects that identity legitimately owns, then attempts to read one identity's objects while authenticated as another and confirms a leak by comparing the response against a ground-truth fetch by the true owner. It also walks predictable identifiers to expose enumeration and reports missing authentication and existence oracles. The tool returns a severity-thresholded exit code and machine-readable reports so that it can gate a continuous integration build. On a synthetic recruitment API in which the McHire failure class is reproduced, AuthProbe detects every planted cross-identity read with no false positives on a hardened counterpart, and its running time grows linearly with the number of objects under test. AuthProbe is released under the Apache 2.0 license with an authorized-use guardrail.
toXiv_bot_toot
 @michabbb@social.vivaldi.net
🔒 Every tool is read-only; the single live path passes URLs and redirects through an SSRF guard — public hosts only, ports 80/443, byte-capped body, no JS execution
📄 MIT licensed, every screen credits and links its source
🌐 https://github.com/Nutlope/inspo
 @cdp1337@social.bitsnbytes.dev @fanf@mendeddrum.org
from my link log —
Historical notes on computer word and byte sizes.
https://www.cs.columbia.edu/~smb/blog/2023-03/2023-03-07.html
saved 2023-03-08
 @cyrevolt@mastodon.social
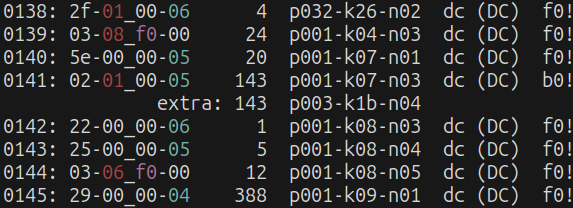
Another bit (literally :)) figured out:
bit 6 in byte 2 tells us if the file entry is extended, with another size and path.
To learn about figuring out such bits and more, come visit my file analysis #workshop at @… - the schedule is now live:
https://talks.mrmcd.net/2026/talk/KBWSRK/
Thanks to @… for hosting us today! :3