 @PwnieFan@infosec.exchange
2026-09-13 17:21:00
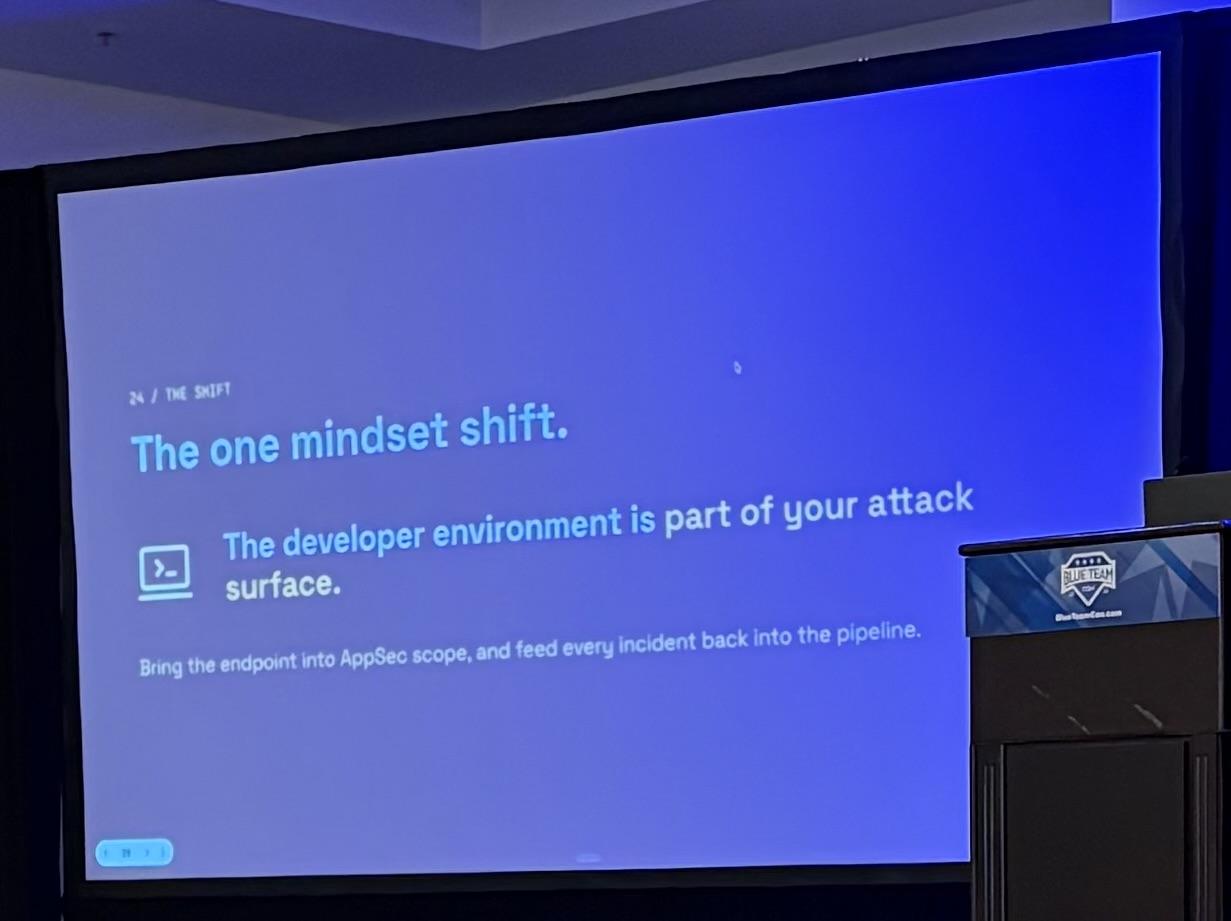
Glad to see this callout from Bansal at #BlueTeamCon - this has been true for awhile
 @PwnieFan@infosec.exchange
Glad to see this callout from Bansal at #BlueTeamCon - this has been true for awhile
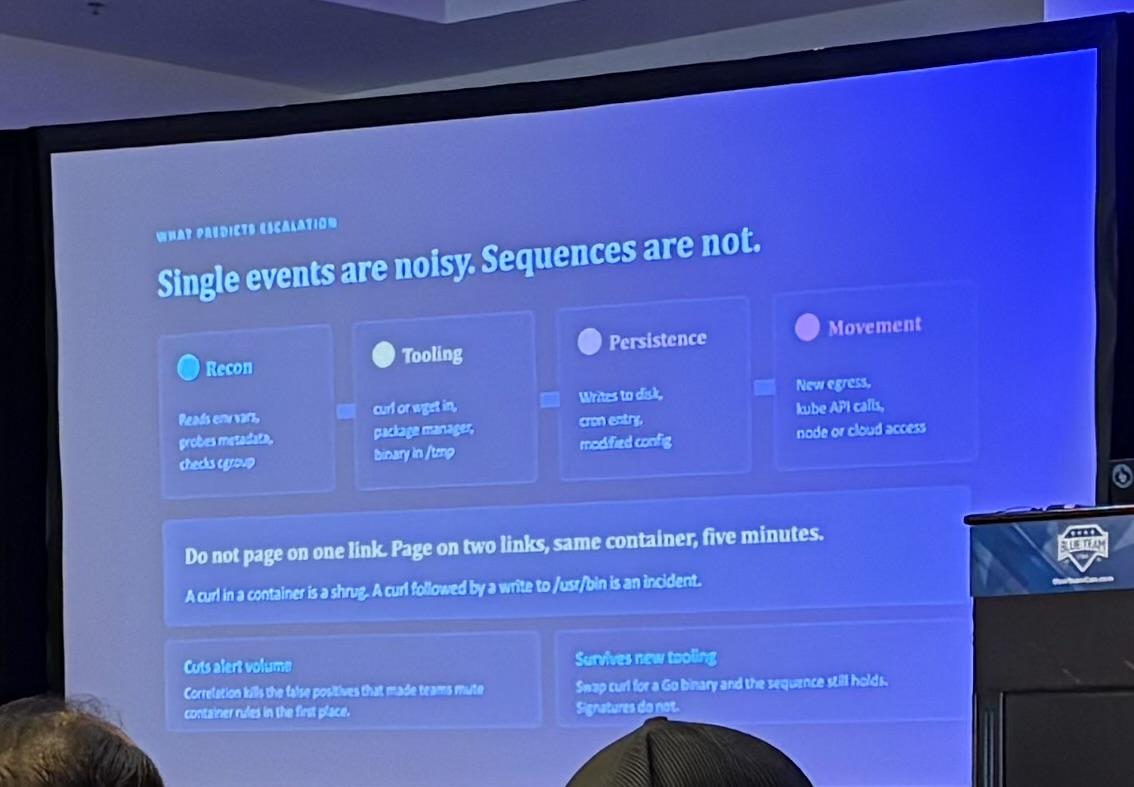
@PwnieFan@infosec.exchangeGood general note for detection from Patel at #BlueTeamCon
 @PwnieFan@infosec.exchange
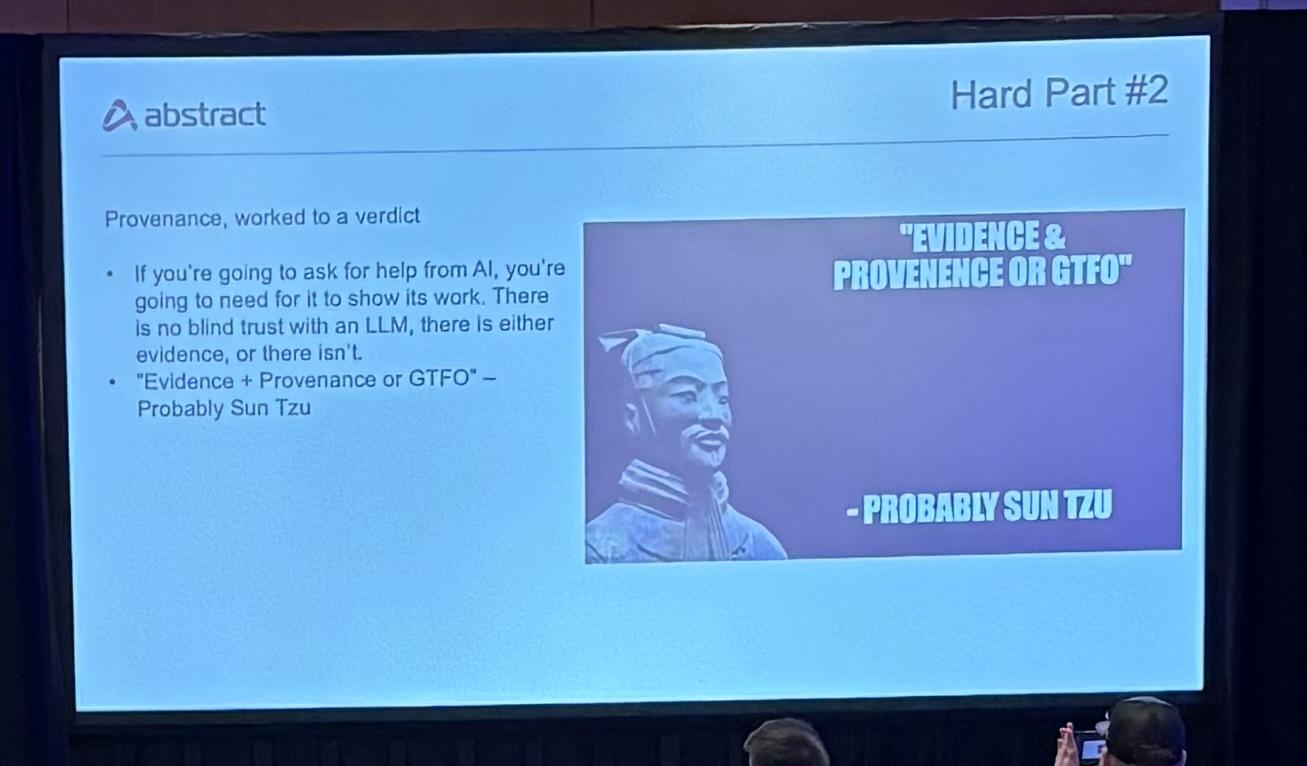
Evidence & Provenance or GTFO. AI hallucinates like it’s at burning man, you need to make it show its work. - Justin Borland at #BlueTeamCon
 @PwnieFan@infosec.exchange
GitHub is used by threat actors because it’s almost ideal for malware hosting - nearly universally allowed and easy for code to blend in - Justin Borland at #BlueTeamCon
@PwnieFan@infosec.exchangeWrite your documentation so AI can scrape documentation you trust - Johnathon Rhoades at #BlueTeamCon (I hate this is where we’re at but this is prolly true)
@PwnieFan@infosec.exchangeFast, cheap, or good: pick two - @… at #BlueTeamCon
 @PwnieFan@infosec.exchange
HCIP (human centered investigative playbooks) are both human and machine readable - Matthew Gracie at #BlueTeamCon https://github.com/InfosecGoon/StandardForPlaybooks
@PwnieFan@infosec.exchangeMobilization in CTEM is the most important step: assign ownership for fixes - Irina Dimitrov (Loktionova) at #BlueTeamCon (see also: people are the hardest problem in infosec)
@PwnieFan@infosec.exchangeFind the choke point (where multiple attack points converge) and fix that first - Irina Dimitrov (Loktionova) at #BlueTeamCon
@PwnieFan@infosec.exchangeGolden rule of threat hunting:90% of what you find is IoT devices and admins doing something weird - Matthew Gracie at #BlueTeamCon https://github.com/InfosecGoon/StandardForPlaybooks
@PwnieFan@infosec.exchangeCathartic to hear @… discussing the impact and lessons from Operation Metro Surge at #BlueTeamCon
 @PwnieFan@infosec.exchange
“This talk is by humans for humans because humans matter more than robots ever will.” @… at #BlueTeamCon
 @PwnieFan@infosec.exchange
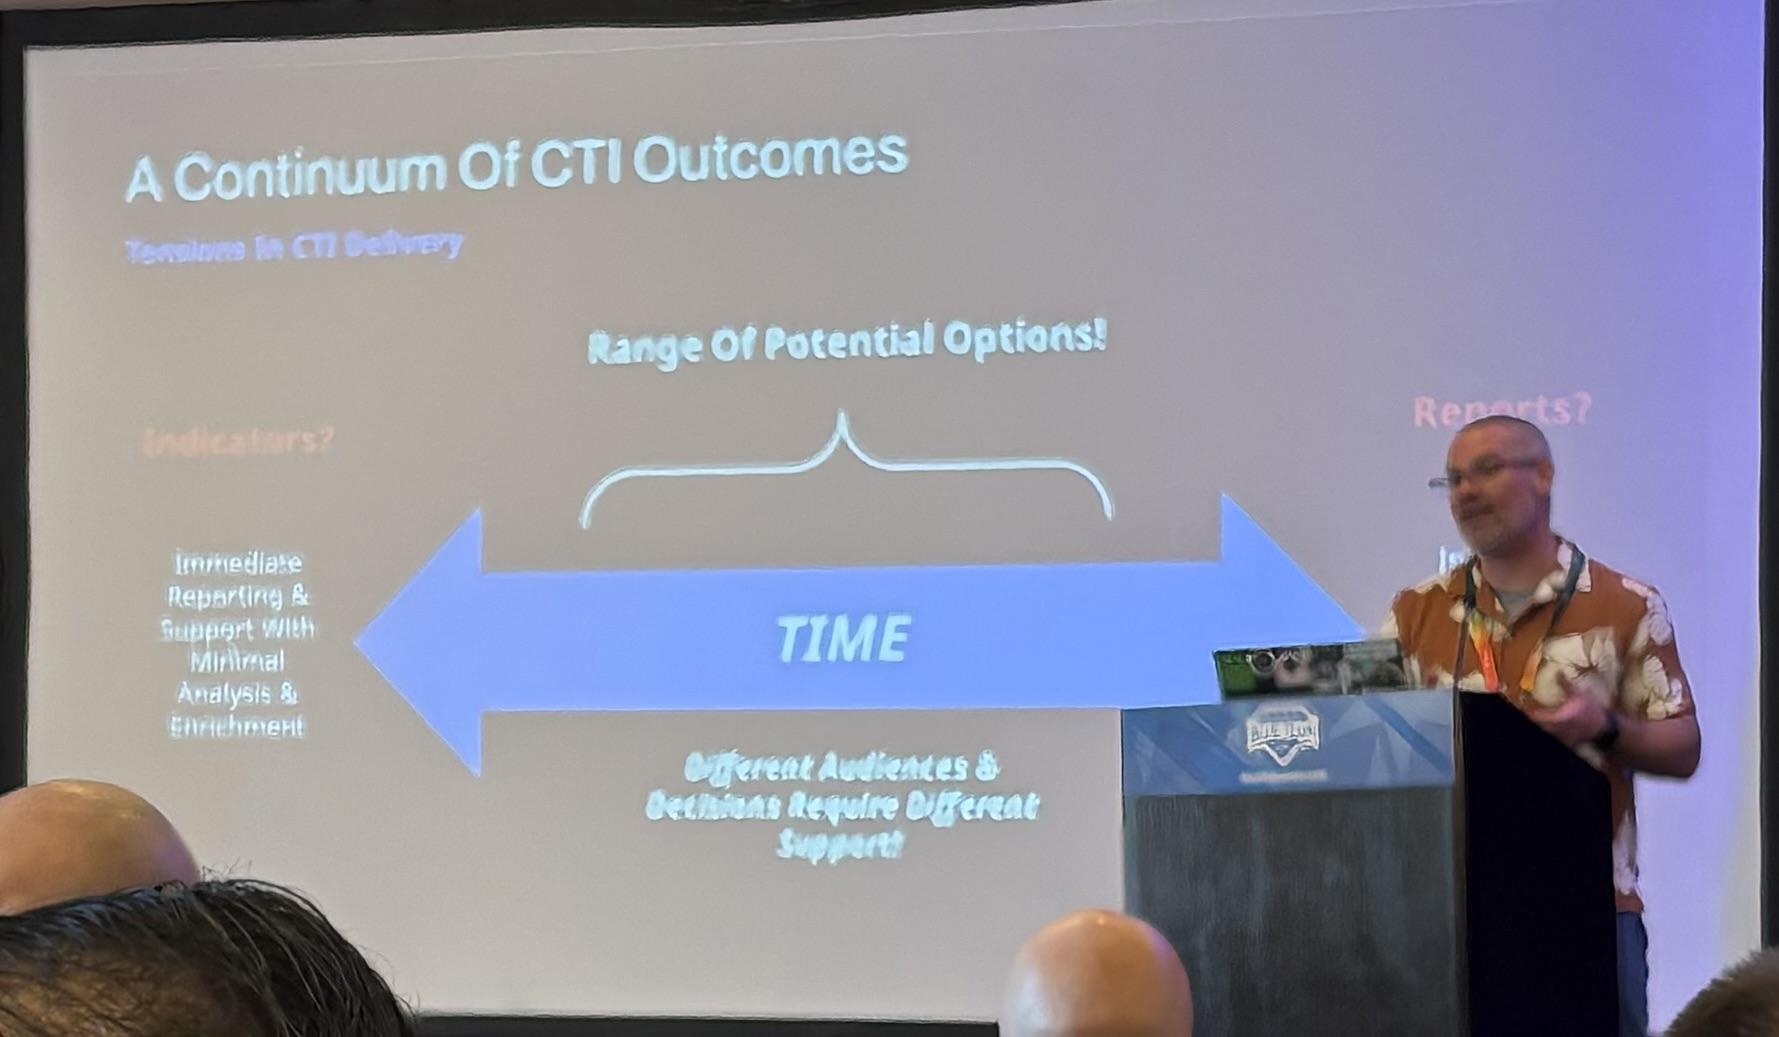
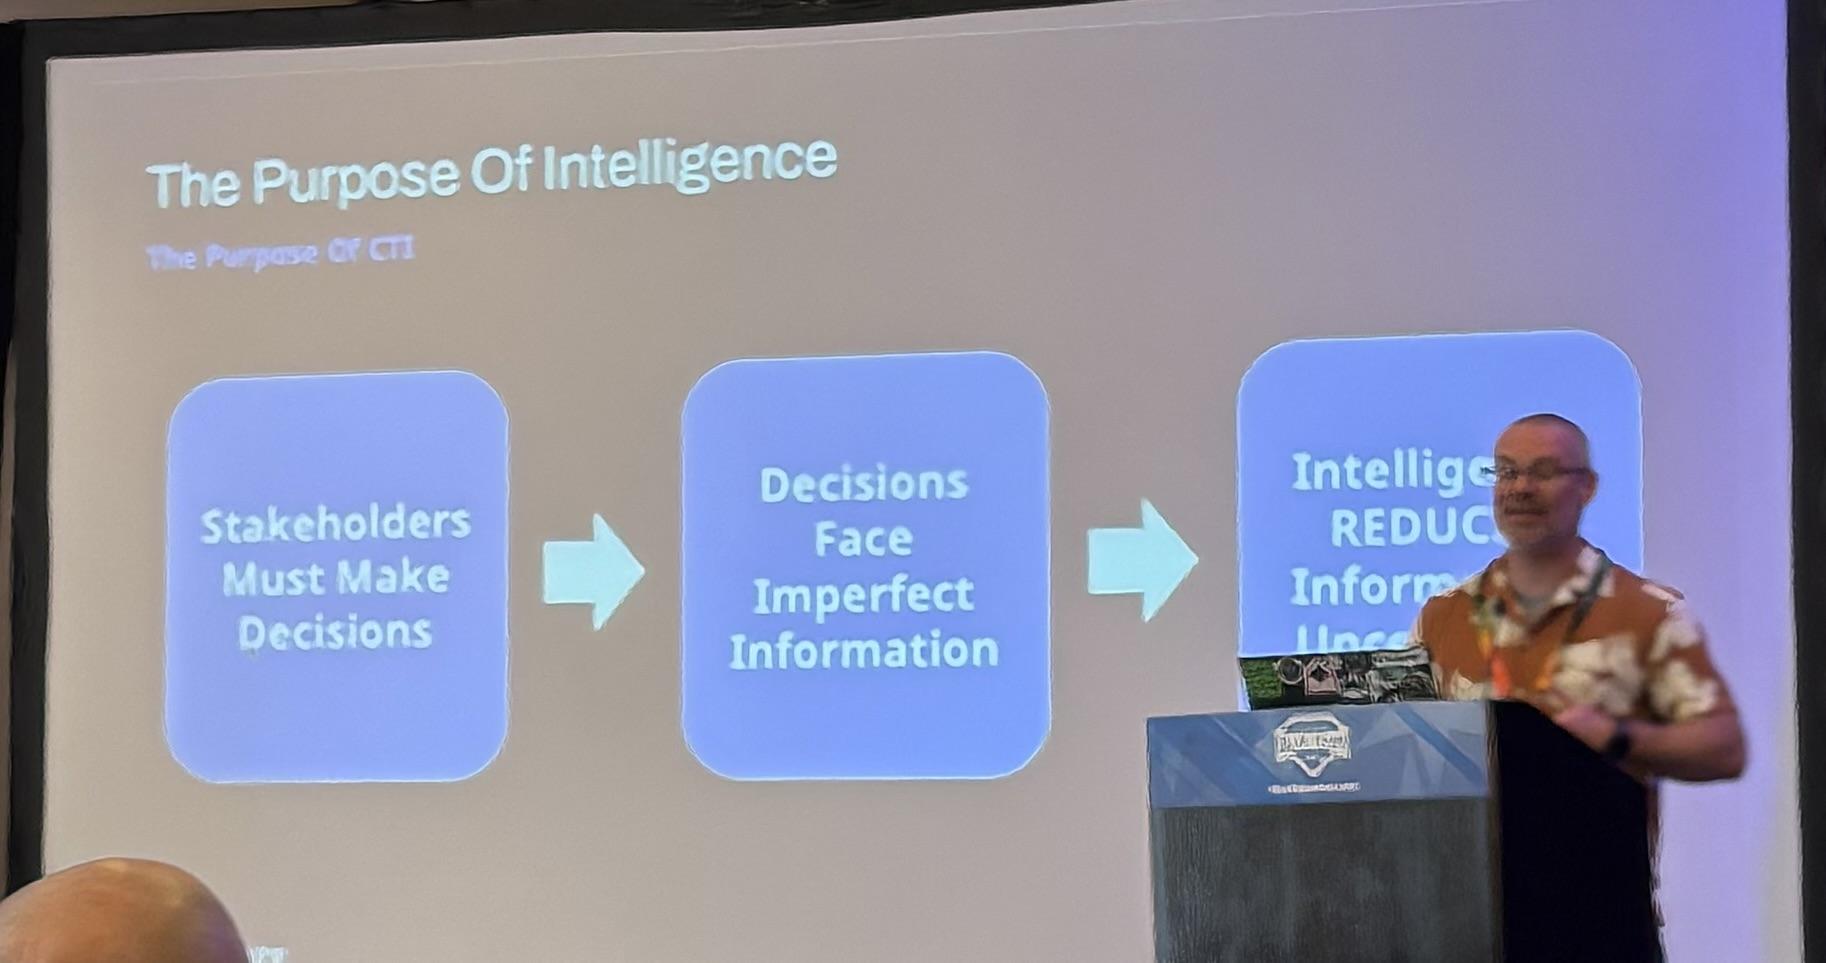
The purpose of CTI is to reduce uncertainty in decision-making. You need to know your stakeholders. - @… at #BlueTeamCon
 @PwnieFan@infosec.exchange
“So much of care work is quiet and unglamorous (and this is good because it doesn’t encourage macho showboating)” @… at #BlueTeamCon
@PwnieFan@infosec.exchange“When you are tired, scared, and cold you are capable of heroism. People in Minnesota aren’t built different. You can do what they did.” @… at #BlueTeamCon
@PwnieFan@infosec.exchangeWas off-the-grid for a bit last week so I’m sure I’m behind on some news. But I’m super excited to say … I’m speaking at OBTS and ATTCKCon this year. I’ve been researching how to find malware on VT before traditional AV or yara sigs will trigger. I’ll also be attending (not speaking) at BlueTeamCon if you like early malware detection too. #obts #attackcon #BlueTeamCon