Tootfinder

Opt-in global Mastodon full text search. Join the index!

@rettichschnidi@swiss.social
2026-09-16 12:50:18

22. September für eine #CRA-Veranstaltung ist ja etwas doof, weil die Reporting Obligations sind ja seit dem 11. September scharf und gemäss LinkedIn müssten fast alle unsere Arbeitgeber ja schon schon kaputt sein. </s>
Ernsthaft: Freue mich auf rege Teilnahme!

@adulau@infosec.exchange
2026-10-16 10:41:08

GCVE BCP-02 v1.9: Making Coordinated Vulnerability Disclosure Open, Accessible, and Practical for Everyone
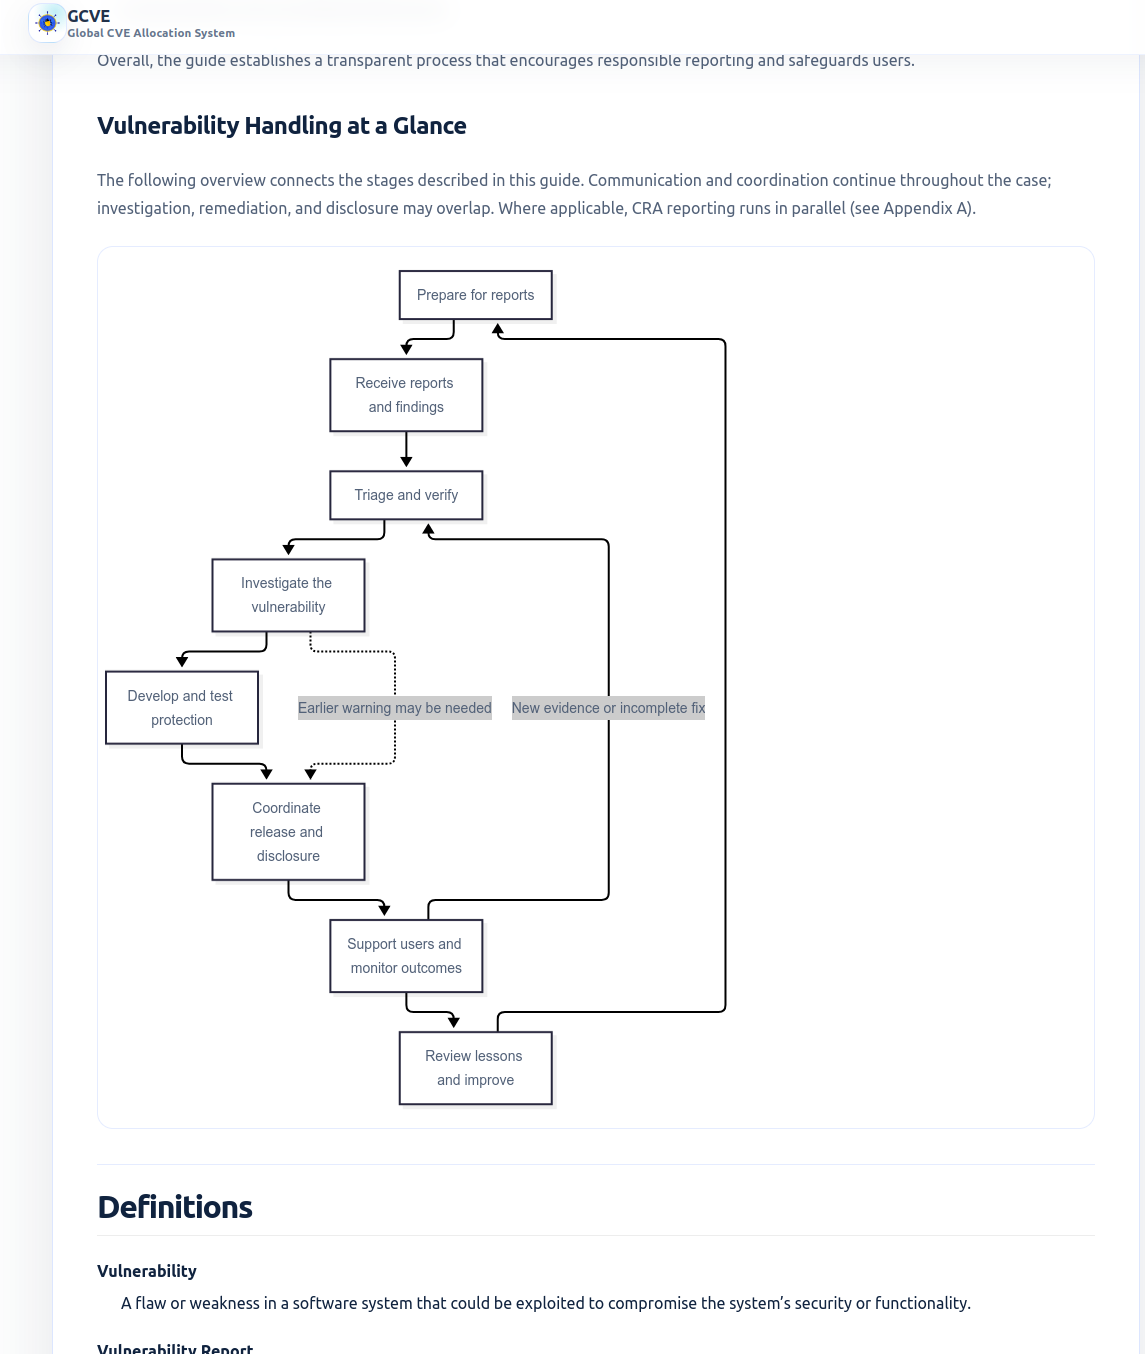
The GCVE initiative has published version 1.9 of GCVE BCP-02 . Practical Guide to Vulnerability Handling and Disclosure, introducing significant improvements to help software vendors, manufacturers, open-source maintainers, and security researchers establish effective Coordinated Vulnerability Disclosure (CVD) processes.
Coordinated Vulnerability Disclosure should not be a privilege reserved for large organizations with dedicated security teams, expensive compliance frameworks, or specialized legal departments. Every software developer and manufacturer, regardless of size or resources, should be able to receive, assess, remediate, and disclose security vulnerabilities responsibly. This is one of the fundamental principles behind GCVE BCP-02.
The updated document is freely available, openly developed, and distributed under the Creative Commons Attribution 4.0 (CC BY 4.0) license. Organizations can reuse, adapt, and integrate its recommendations into their own vulnerability-handling processes.
#cra #cve #gcve #vulnerability #cvd #vulnerabilityManagement
🔗 gcve.eu/2026/10/16/gcve-bcp-02

@adulau@infosec.exchange
2026-08-13 15:21:01

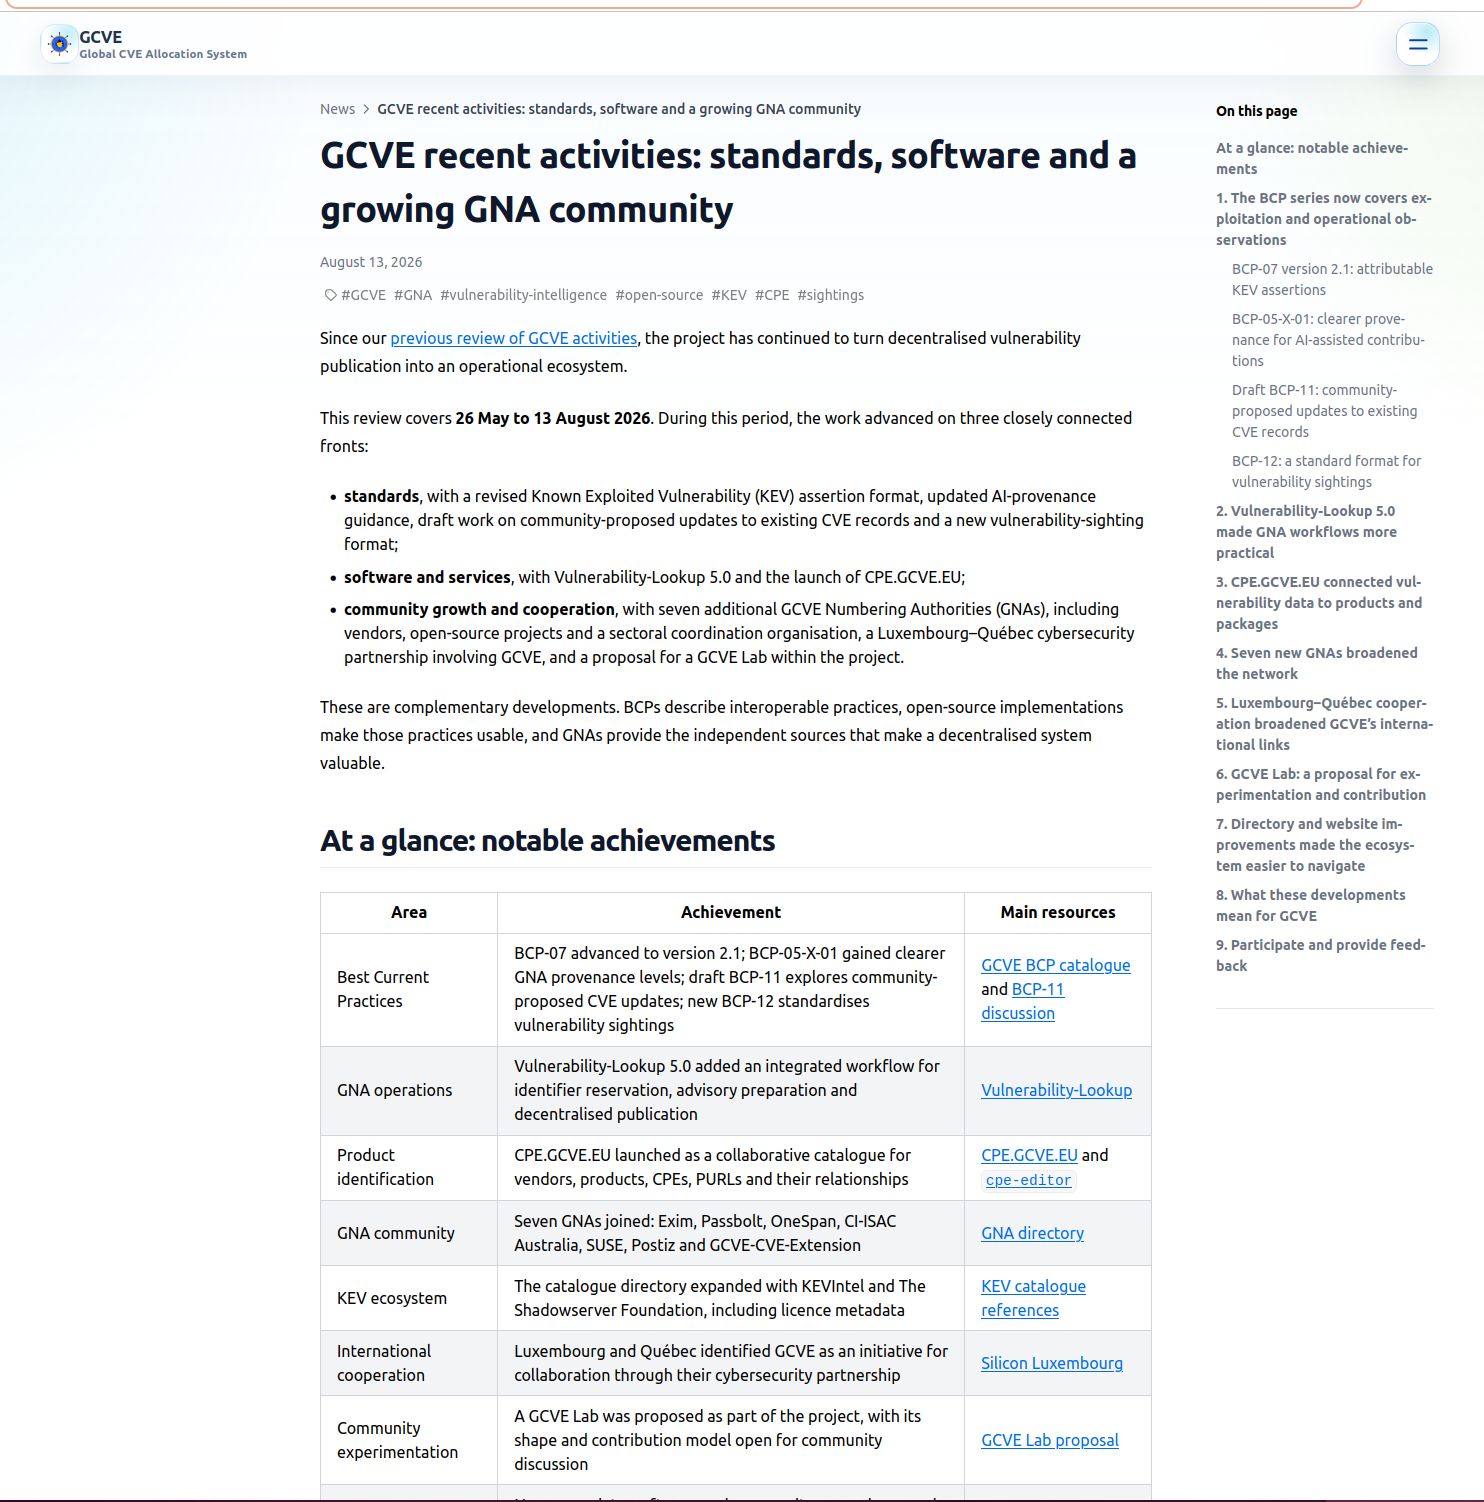
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource

@kingconsult@berlin.social
2026-08-03 10:28:21

Die Gesellschaft für #Informatik ( @… − folgen!) fordert im neuen Policy Brief die Anerkennung und Besserstellung von #OpenSource-Software-Stewards ( Das sind Verwalter quelloffener Software,#OSSStewards ) nach der EU 🇪🇺 #Cyberresilienz-Verordnung.
15.07.2026:
👉 #CyberResilienceAct #CRA #FOSS #FLOSS #Cybersicherheitsstrategie #ITSecurity #DutGemacht

@adulau@infosec.exchange
2026-10-04 08:50:55

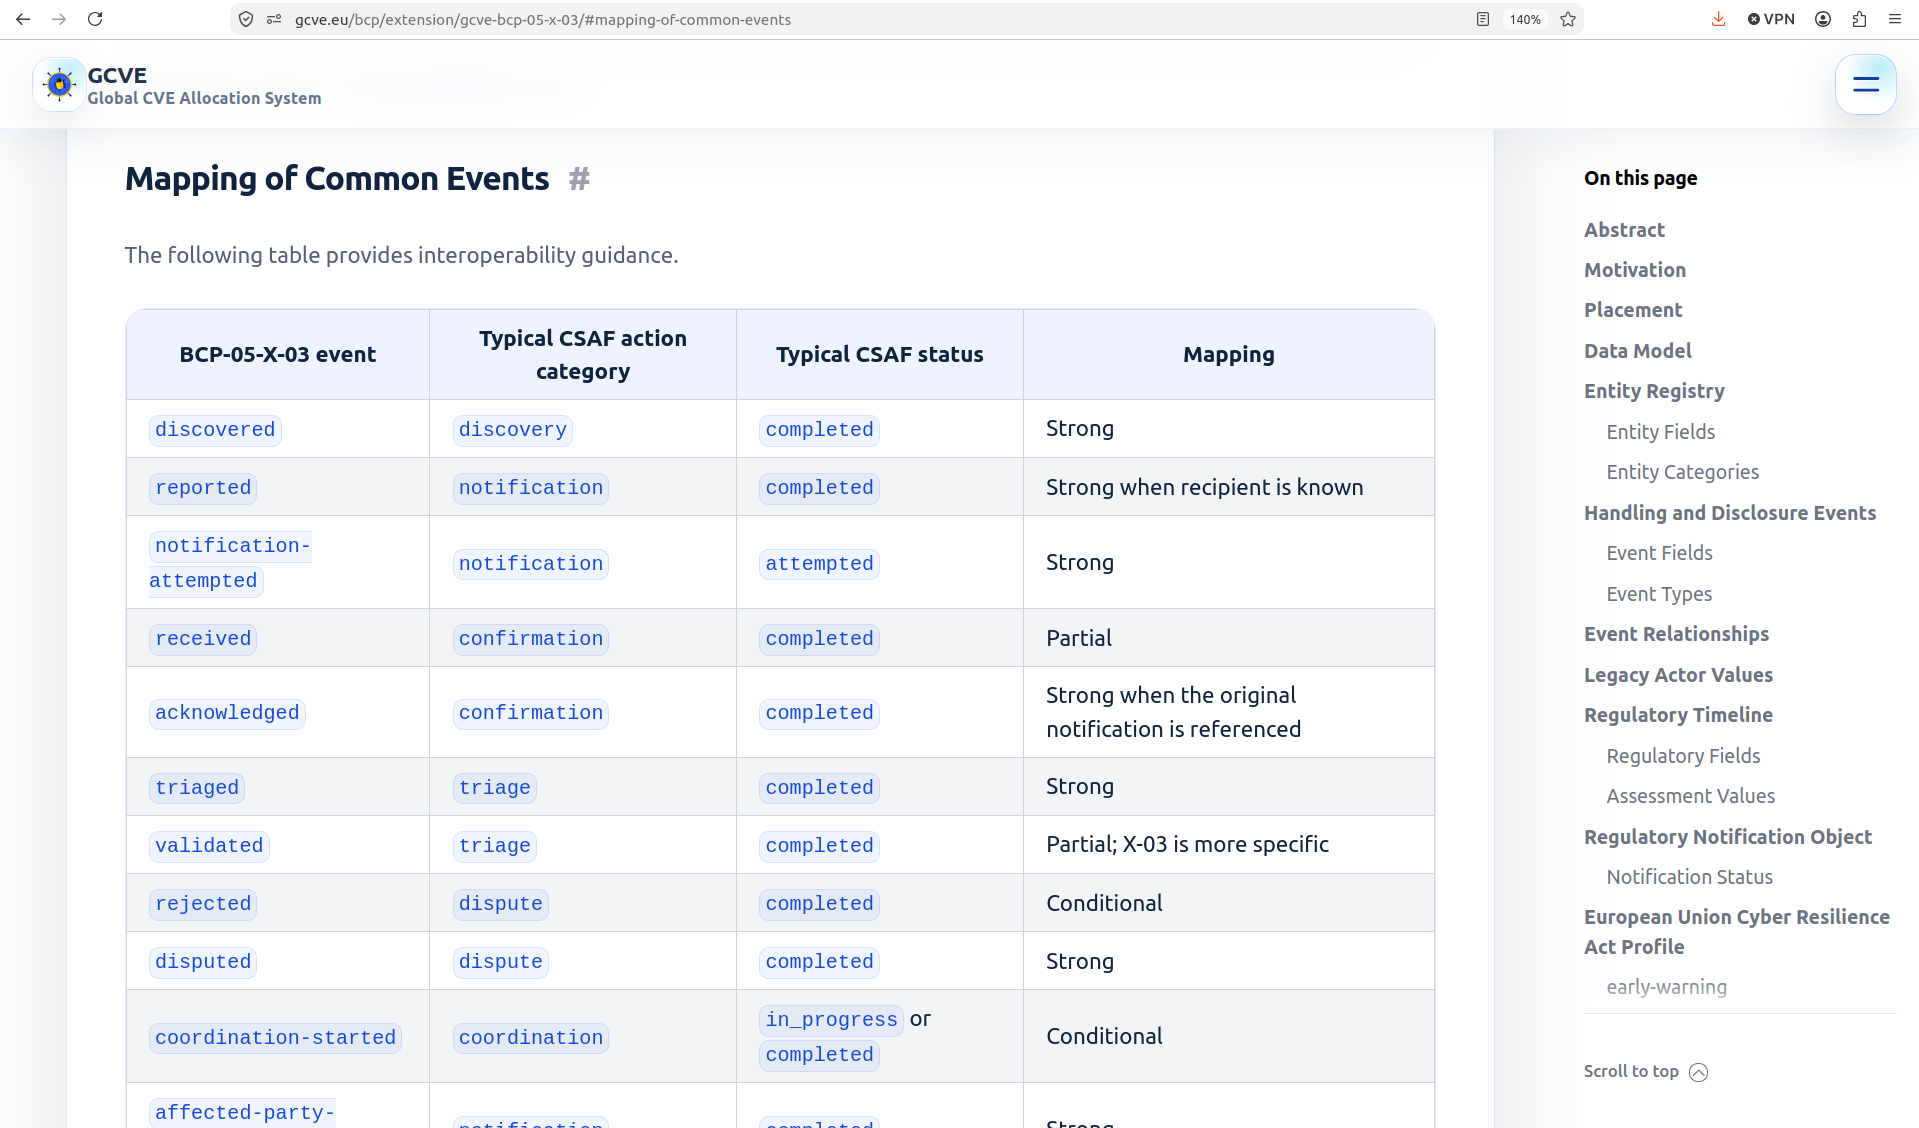
We did some improvements in GCVE extension - GCVE BCP-05-X-03 - Vulnerability Handling and Disclosure Timeline.
We also review the alignment and interoperability with CSAF 2.1.
Now there is a new object field entities to represent the entities in the handling timeline.
🔗 GCVE BCP-05-X-03 #csaf #gcve #cve #vulnerabilityManagement #vulnerability #openstandard #cra

@adulau@infosec.exchange
2026-08-01 08:20:08

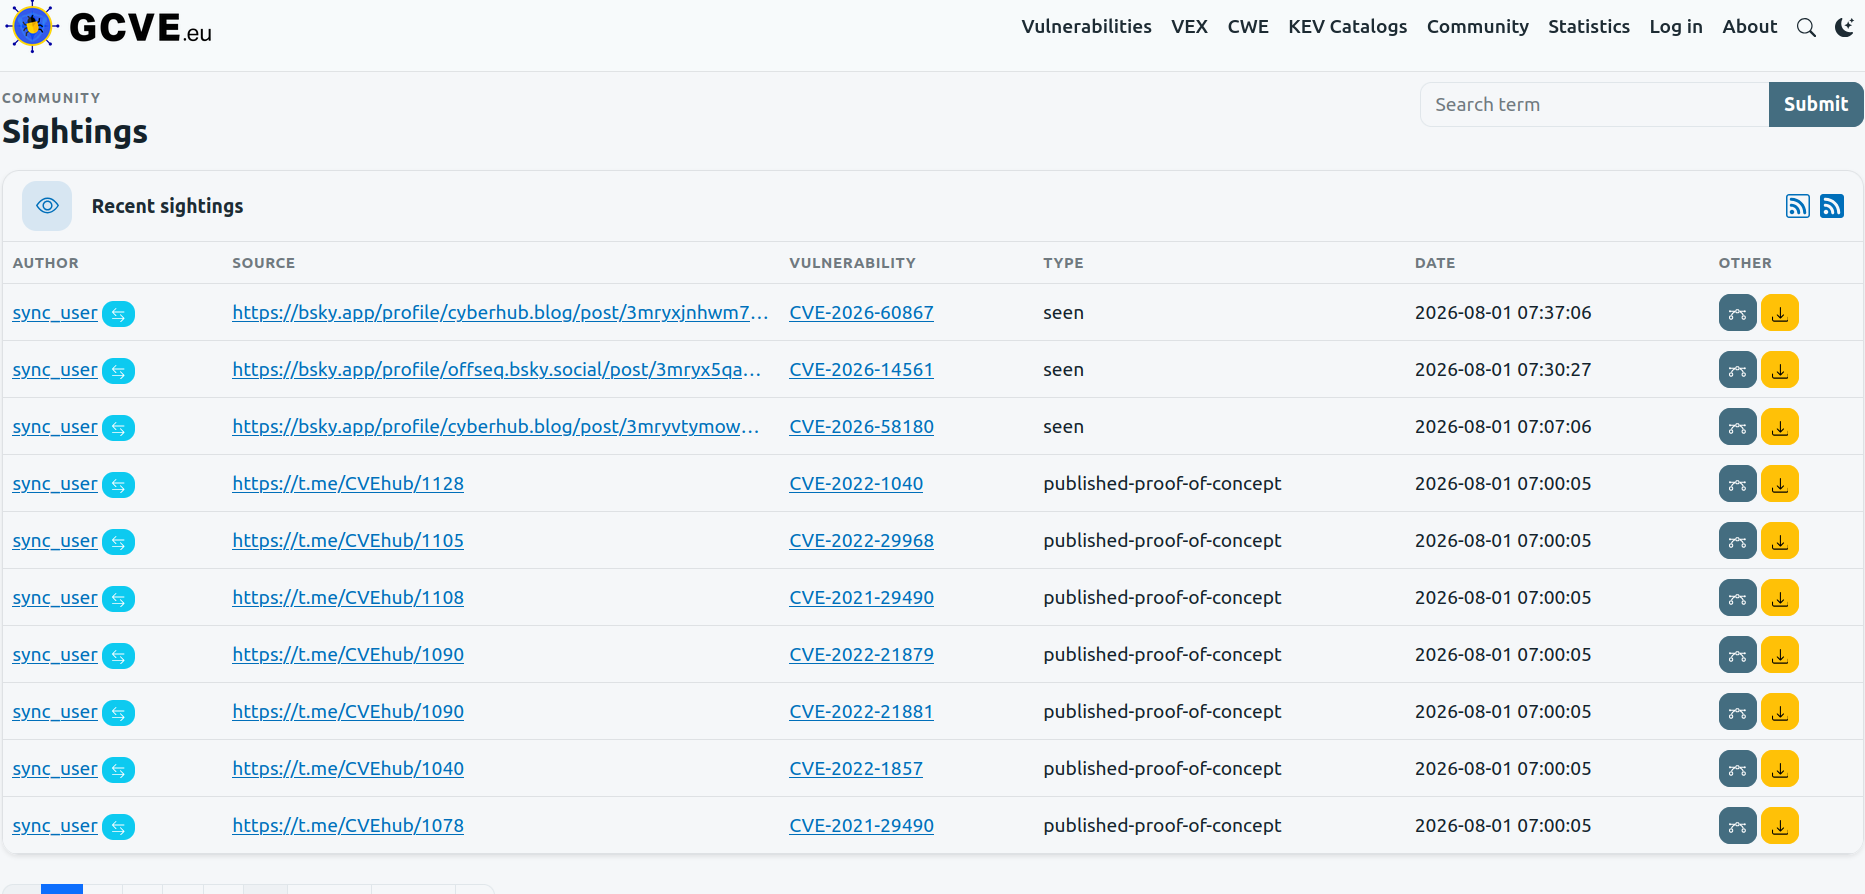
Sightings have long been a major topic of discussion in the CTI community, particularly in the field of vulnerability management. We have now published a GCVE BCP to standardise the format that has been implemented, tested and used operationally in Vulnerability-Lookup for some time.
Thanks to everyone (Cédric Bonhomme, Éireann Leverett, Andras Iklody, Sami Mokaddem and many more) who participated in discussions and worked on the implementation details of sightings over the past several years. These efforts had a strong focus on practical implementation, while BCP-12 specifically addresses sightings in the context of vulnerability management.
BCP-12 is still a draft open for review, but it already provides a strong foundation for existing implementations.
#cve #cra #gcve #vulnerabilitymanagement #cybersecurity #openstandard

@adulau@infosec.exchange
2026-10-01 12:42:44

GCVE BCP-05-X-03: Bringing Vulnerability Handling Timelines into Vulnerability Records.
Vulnerability records usually provide a good description of what a vulnerability is, which products are affected, how severe it may be, and where additional information can be found.
They are often much less effective at describing what happened, when it happened, and who was involved during the vulnerability handling and disclosure process.
Following many discussions during VulnOptiCON 2026 in Luxembourg, this limitation became particularly clear. Vulnerability analysts, coordinators, vendors and other participants repeatedly discussed how difficult it can be to reconstruct a reliable timeline during vulnerability analysis and coordinated vulnerability disclosure.
To help address this, the GCVE initiative has published a new extension:
GCVE BCP-05-X-03 - Vulnerability Handling and Disclosure Timeline.
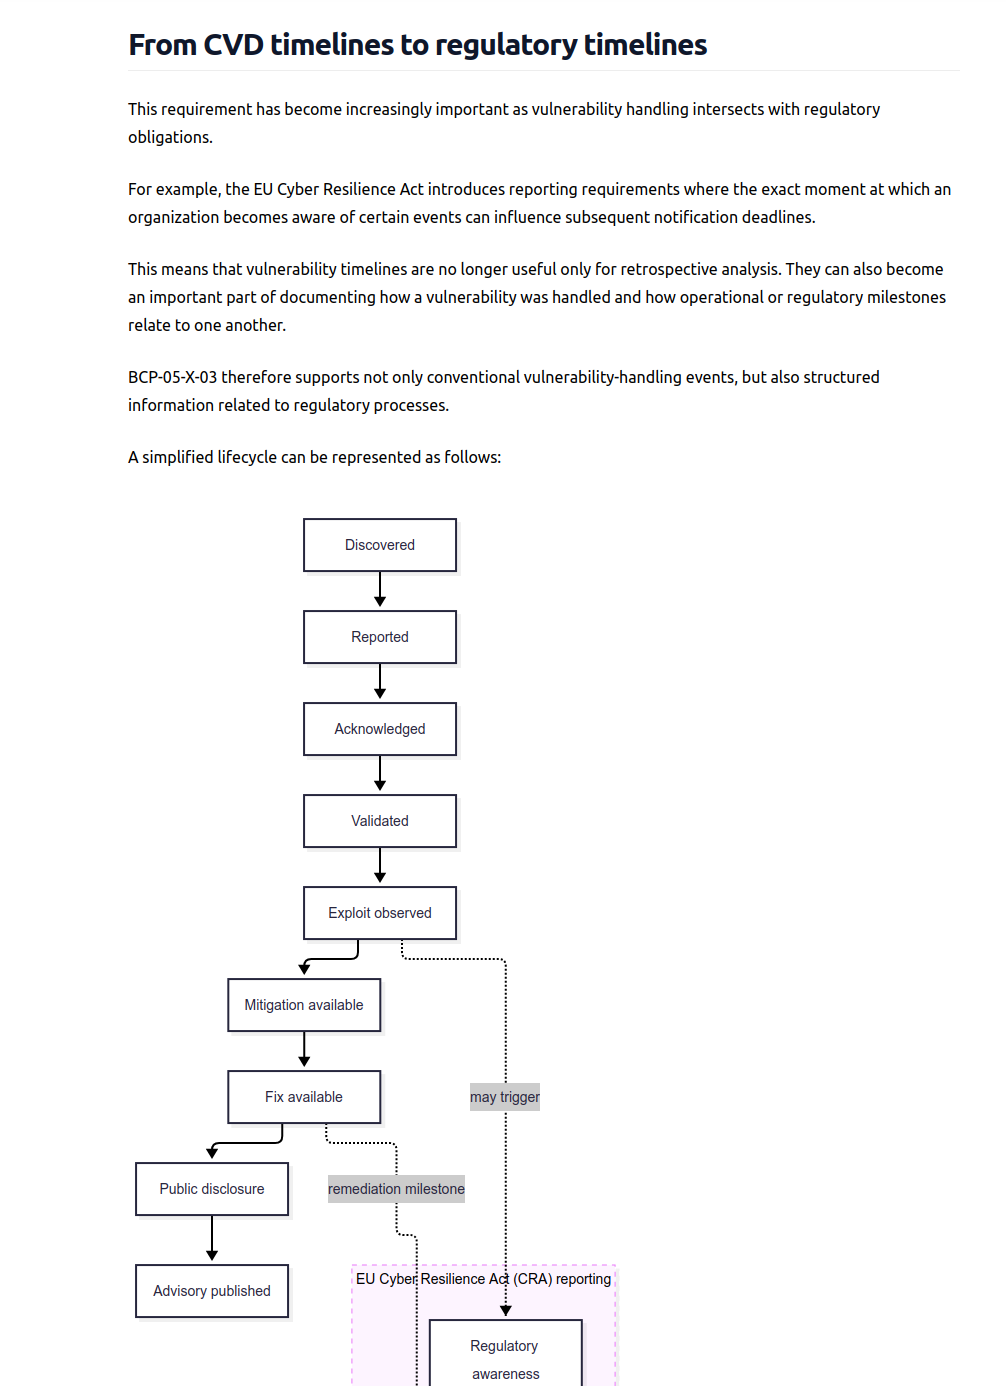
The extension provides a structured and machine-readable way to represent the lifecycle of a vulnerability from discovery and reporting through acknowledgement, validation, remediation and public disclosure. It's already live in our open-source tool-set.
🔗 Blog post #opensource #openstandard #cve #gcve #cra #cybersecurity #vulnerability