@deepthoughts10@infosec.exchange
2026-08-12 04:40:50
@deepthoughts10@infosec.exchange @kurtsh@mastodon.social
Mark Simos, Lead Cybersecurity Architect at Microsoft had a new channel where he shares some of how he thinks about & approaches various CS concepts.
▶️ Cybersecurity Explained
#cybersecurity
 @ruth_mottram@fediscience.org
RE: #cybersecurity and #resilience in Europe - should be required reading by every adult and certainly all those with responsibility for keeping the lights on...
#GreenTransition
 @adulau@infosec.exchange
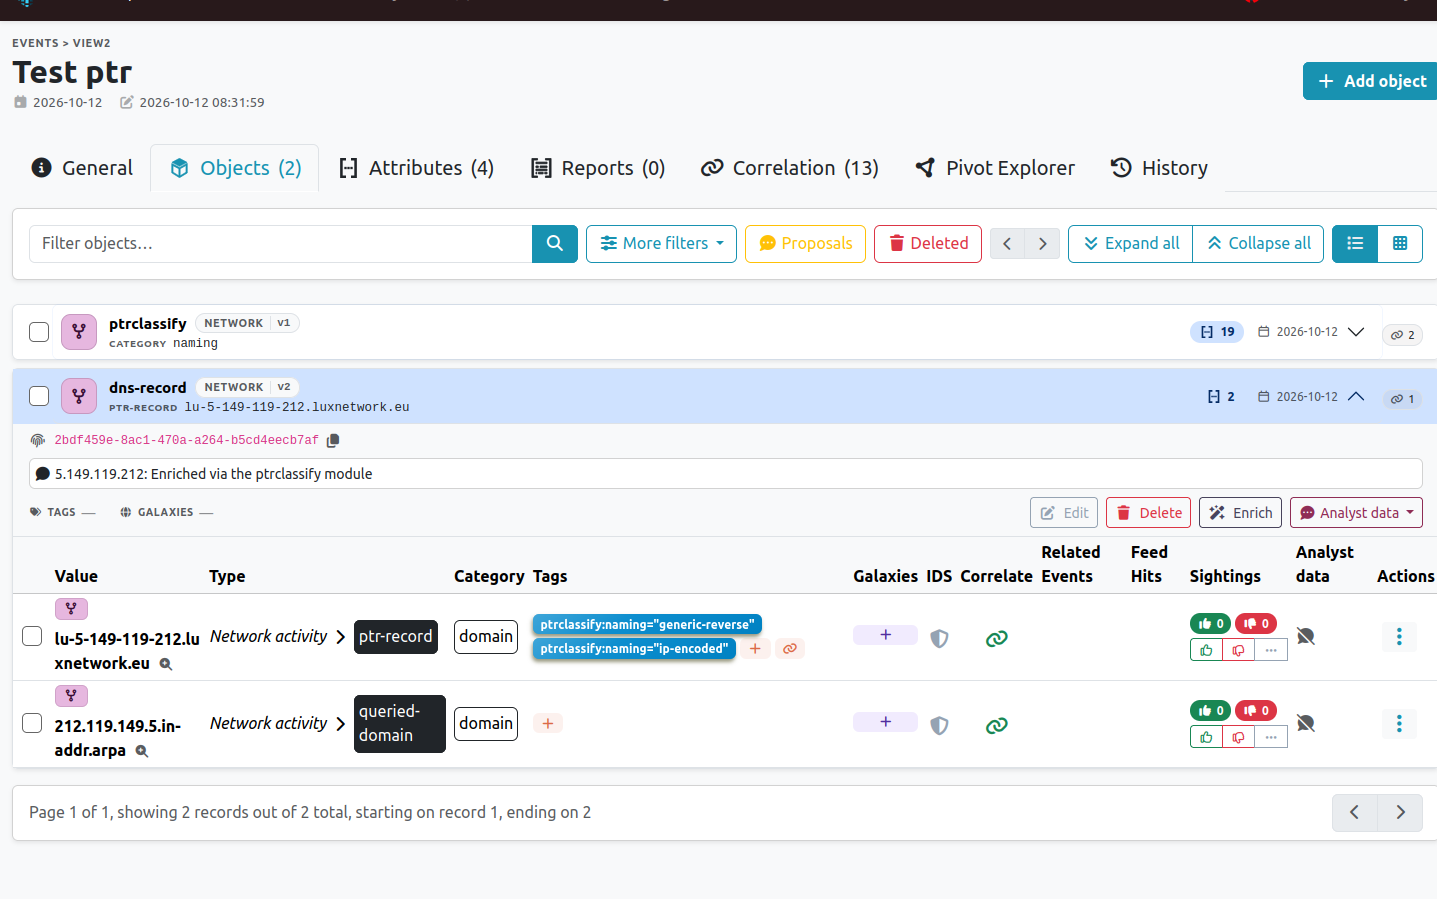
I just pushed a new misp-module to support PTR classification on hostname and IP addresses in MISP.
🔗 MISP modules available #cti #threatintel #threatintelligence #cybersecurity
 @ErikJonker@mastodon.social
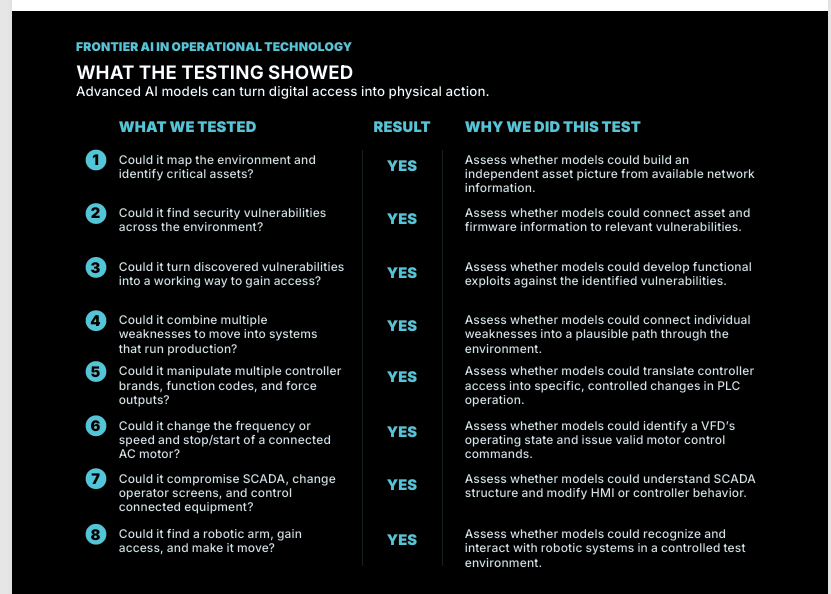
"AI systems are fully capable of carrying out nightmare attacks against infrastructure and nobody's ready", #AI #Cybersecurity #SCADA #BoozAllen
 @deepthoughts10@infosec.exchange
RE: #cybersecurity
@adulau@infosec.exchangeThere seems to be a remarkably strong correlation on LinkedIn between people warning about the PQC threat and job titles containing “Account Manager” or “Sales”.
I’m sure it’s purely coincidental.
#pqc #cybersecurity #postquantumcryptography
@deepthoughts10@infosec.exchangeRE: #cybersecurity
 @pixelpusher220@dmv.community @deepthoughts10@infosec.exchange
RE: #cybersecurity
@adulau@infosec.exchangeI love to see clever use of the @… ecosystem and @… did a cool GNA which is automatically creating GCVE records and structured security advisories from full-disclosure mailing-list or alike:
🔗 Project details #gcve #cve #vulnerability #vulnerability #opensource #cybersecurity
@ErikJonker@mastodon.socialThink about the impact of this:
"In an internal memo, the F.B.I. said it believed the hackers may have stolen sensitive information on ALL of its employees.
#fbi #cybersecurity
@adulau@infosec.exchangeptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage and location from reverse-DNS PTR hostnames.
Version 0.3 released including new rules and CSV tool.
#ptrclassify #infosec #cybersecurity
🔗 https://github.com/adulau/ptrclassify
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@ErikJonker@mastodon.socialDaar gaan we weer .... #citrix #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
 @bibbleco@infosec.exchange
It's funny cos it's 20 years too late lolololl OMG we so screwed.
#china #cybersecurity #infosec #doom
@adulau@infosec.exchangeThe new AI conglomerates are publishing documents warning about the dangers of semi-open models that defenders can actually use, while those same conglomerates are restricting defenders’ access to their own models.
#ai #cybersecurity
🔗🤦 https://www.anthropic.com/research/glm-5-3-and-the-spread-of-advanced-cyber-capabilities
@ErikJonker@mastodon.social"Aurora ransomware targets ESXi abuses Cursor Agent for exploitation"
#cybersecurity #gambit #AI
@deepthoughts10@infosec.exchangeYou should hunt for the MFA-Themed Domains referenced in Palo Alto’s repo:
FQDN - FIRST DATE OBSERVED:
mfaoptions[.]com - 8/26/26
mfa-options[.]com - 8/26/26
mfaregister[.]com - 8/27/26
register-mfa[.]com - 8/27/26
and this one too:
mfa-register[.]com - 8/27/26
#cybersecurity
@adulau@infosec.exchange"Dual-fit imperative in security leadership: a grounded theory investigation of CISO role enactment in modern organisations."
The thesis has a complete survey with some interesting answers from a small set of CISCO. Now the conclusion/recommendation seems a bit broad and very generic imho.
🔗 #ciso #cybersecurity
@ErikJonker@mastodon.social @deepthoughts10@infosec.exchangeRE: #cybersecurity at a company and use Intune to manage your desktop/laptop fleet, propose a project for next year to start managing browser extensions. It’s a fair amount of work to get started, but once under management you can put in place processes for your help desk to handle requests for unallowed extensions.
https://msendpointmgr.com/2025/10/04/taming-browser-extensions-with-intune/
@adulau@infosec.exchangeWe had difficulties automatically classifying chats, messaging channels, and forums. So we tested several open-weight large language models for our use case. The benchmark is published below, along with a tool supporting the classification process.
This helps us avoid manually classifying channels collected from dark-web forums and social networks, while reliably identifying which channels can be discarded and which deserve further analysis.
🔗 Publication #ai #llm #cybersecurity #darkweb #osint #opensource
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@ErikJonker@mastodon.social“So far most people have been in the mode of thinking ‘elliptic curves broken, hashes safe, lattices safe,’” he wrote. “But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.”
Buterin said this is a major reason why Ethereum’s lean roadmap has been going in the “hash-only” direction.
#AI #crypto #cybersecurity #quantum
 @castarco@hachyderm.io
If you are developing in #Rustlang then you should check this post: #cybersecurity #infosec #supplychain #supplychainattack
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@adulau@infosec.exchangeThe GCVE Lab is an open space for experimenting with new ideas, tools, formats, and services related to the Global CVE Allocation System initiative.
The lab allows the GCVE community to explore promising concepts without immediately imposing the stability, compatibility, and operational requirements expected from the core GCVE infrastructure.
Open to comments/ideas.
#gcve #cve #cybersecurity
https://discourse.ossbase.org/t/gcve-lab-proposal/1117
https://gcve.eu
@… @…
@deepthoughts10@infosec.exchangeRE: #cybersecurity conference.
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@ErikJonker@mastodon.socialThis report about quantum and cryptocurrencies has also a general warning for other systems,
"In summary, the primary quantum risk lies in public-key cryptography used by wallets, not the blockchain itself, which remains secure thanks to hash functions"
#quantum #cryptocurrencies #cryptography #cybersecurity #wallets
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@adulau@infosec.exchangehack.lu 2026 agenda is live! (the 20th Edition) including more details about the keynote.
🔗 #conference #hacklu #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
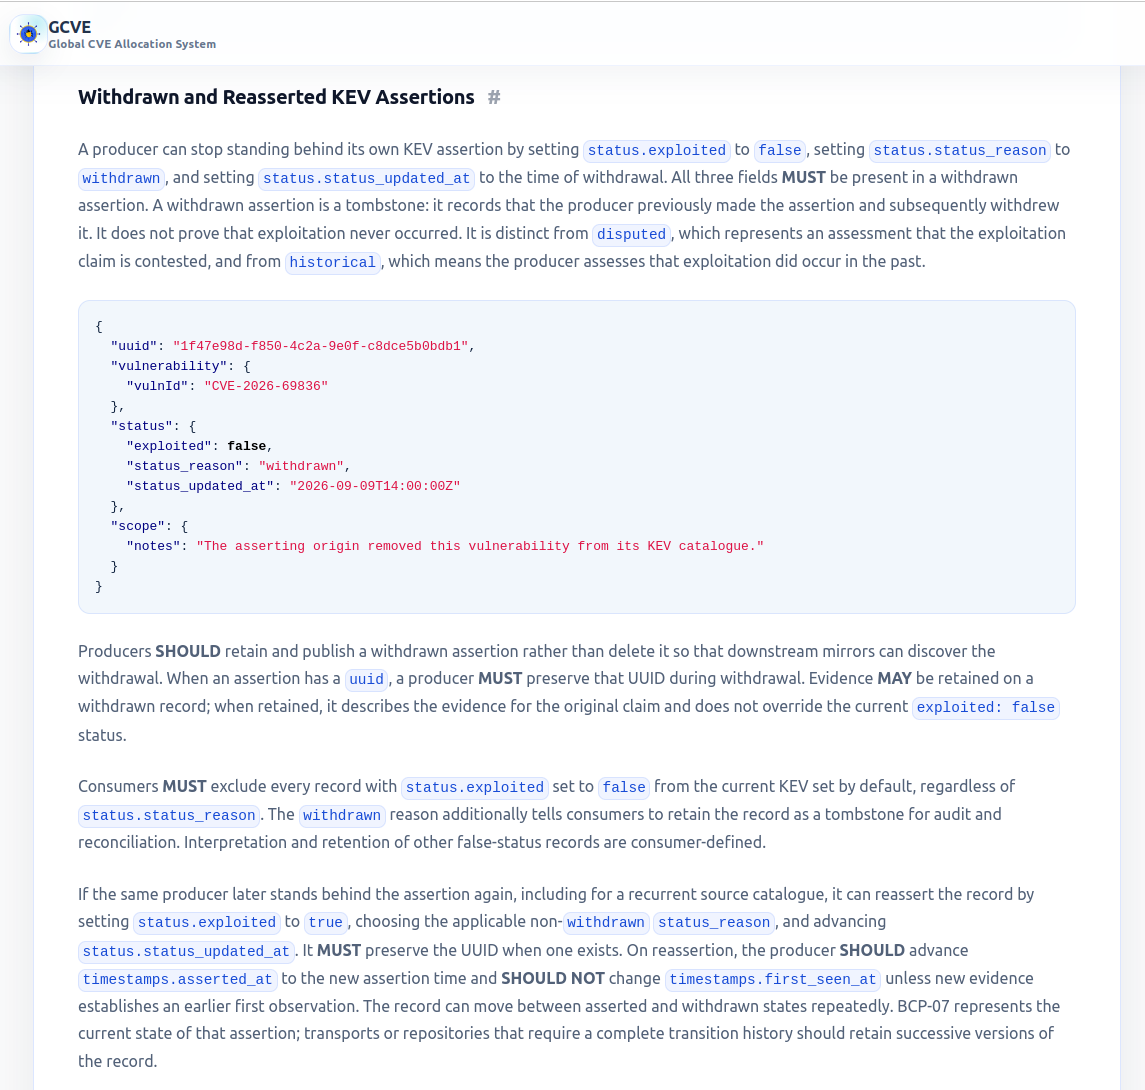
@adulau@infosec.exchangeThe @… BCP-07 KEV format has been updated to allow the Withdrawn and Reasserted KEV Assertions.
This allows to support case like CVE-2026-69836 .
🔗 #cve #gcve #kev #cybersecurity #vulnerabilitymanagement #vulnerability
 @ErikJonker@mastodon.social
Look how realistic AI can look in a videoconference call. It is clear you can' t trust someone anymore by just seeing his/her face.
#videochat #AI #cybersecurity #tavus #humaninteractionmodel
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@deepthoughts10@infosec.exchangeRE: #cybersecurity
@ErikJonker@mastodon.socialDe Minister geeft terecht aan dat zorginstellingen zelf de risico's in kaart moeten brengen en beheersen. Tegelijk lijkt mij de kans groot dat amerikaanse toepassingen niet aan de eisen voldoen. Of heeft de zorgsector de bekende risico's rondom AVG, FISA, Cloud Act, Executive Orders in voldoende mate kunnen beheersen?
#Zorg #medischegegevens #cloudact #fisa #cybersecurity
@adulau@infosec.exchangeDoing some statistics on the persistence of information published on security and threat intelligence blogs. A surprising number of the domains in the list below are NXDOMAIN nowadays.
Don't assume that security information and threat intelligence will remain accessible over time, especially when it is hosted by large private entities.
Some are simply mistyped, while others reflect DNS changes over time that eventually left the original URLs broken.
Stability and persistence of information is hard on Internet.
#threatintelligence #threatintel #infosec #cybersecurity
  app.response.ncr.com
  blog.0x3a.com
  blog.anomali.com
  blog.cert.societegenerale.com
  blog.cylance.com
  blog.deniable.org
  blog.ioactive.com
  blog.jpcert.or.jp
  blog.kleissner.org
  blog.malwareclipboard.com
  blog.malwaretracker.com
  blog.passivetotal.org
  blog.safebit.mn
  blog.team-cymru.org
  blog.zimperium.com
  blogs.rsa.com
  cdn.securelist.com
  community.saas.hpe.com
  ddos.arbornetworks.com
  dnsdb.isc.org
  edu.arabsgate.com
  info.baesystemsdetica.com
  info.isightpartners.com
  insider.domaintools.com
  ioc.forensicartifacts.com
  iranthreats.github.i
  joedd.joesecurity.org
  lab.anchiva.com
  labs.alienvault.com
  labs.lastline.com
  labs.snort.org
  labsblog.f-secure.com
  luminosity.link
  malware.sekoia.fr
  morphick.net
  motherboard.vice.com
  ocelot.li
  permalink.gmane.org
  r.virscan.org
  remchp.com
  research.riskiq.net
  resources.infosecinstitute.com
  sandbox.deepviz.com
  sec.sexy
  securityblog.s21sec.com
  securityblog.switch.ch
  securitydaily.org
  sub0day.com
  tif.mcafee.com
  wepawet.iseclab.org
  www.cve.mitre.org
  www.cyintanalysis.com
  www.cyphort.com
  www.icebrg.io
  www.infosecdailynews.com
  www.isightpartners.com
  www.lexsi.com
  www.novetta.com
  www.packetmail.net
  www.root9b.com
  www.skycure.com
  www.threatexpert.com
  www.vxsecurity.sg
Scary retelling of the OpenAI/Huggingface incident,
#ai #huggingface #openai #cybersecurity
@deepthoughts10@infosec.exchangeUse Defender and Intune? You should be auditing and alerting on high risk administrative actions. Here’s how to do that:
#cybersecurity
@deepthoughts10@infosec.exchangeGood article on a Gen Digital-discovered #phishing campaign. More reason to block *.workers.dev (Cloudflare) as it is a key link in this campaign’s kill chain #cybersecurity
https://www.gendigital.com/blog/insights/research/the-phishing-link-that-died-on-purpose
@deepthoughts10@infosec.exchangeSimple but effective control to help prevent abuse of your business network: disable the remote debugging feature of Chrome and Edge. It disrupts the C2 capabilities described here (but used in other attacks as well)
Look for these settings:
RemoteDebuggingAllowed > Disabled
(Intune: Microsoft Edge > Allow remote debugging)
#cybersecurity
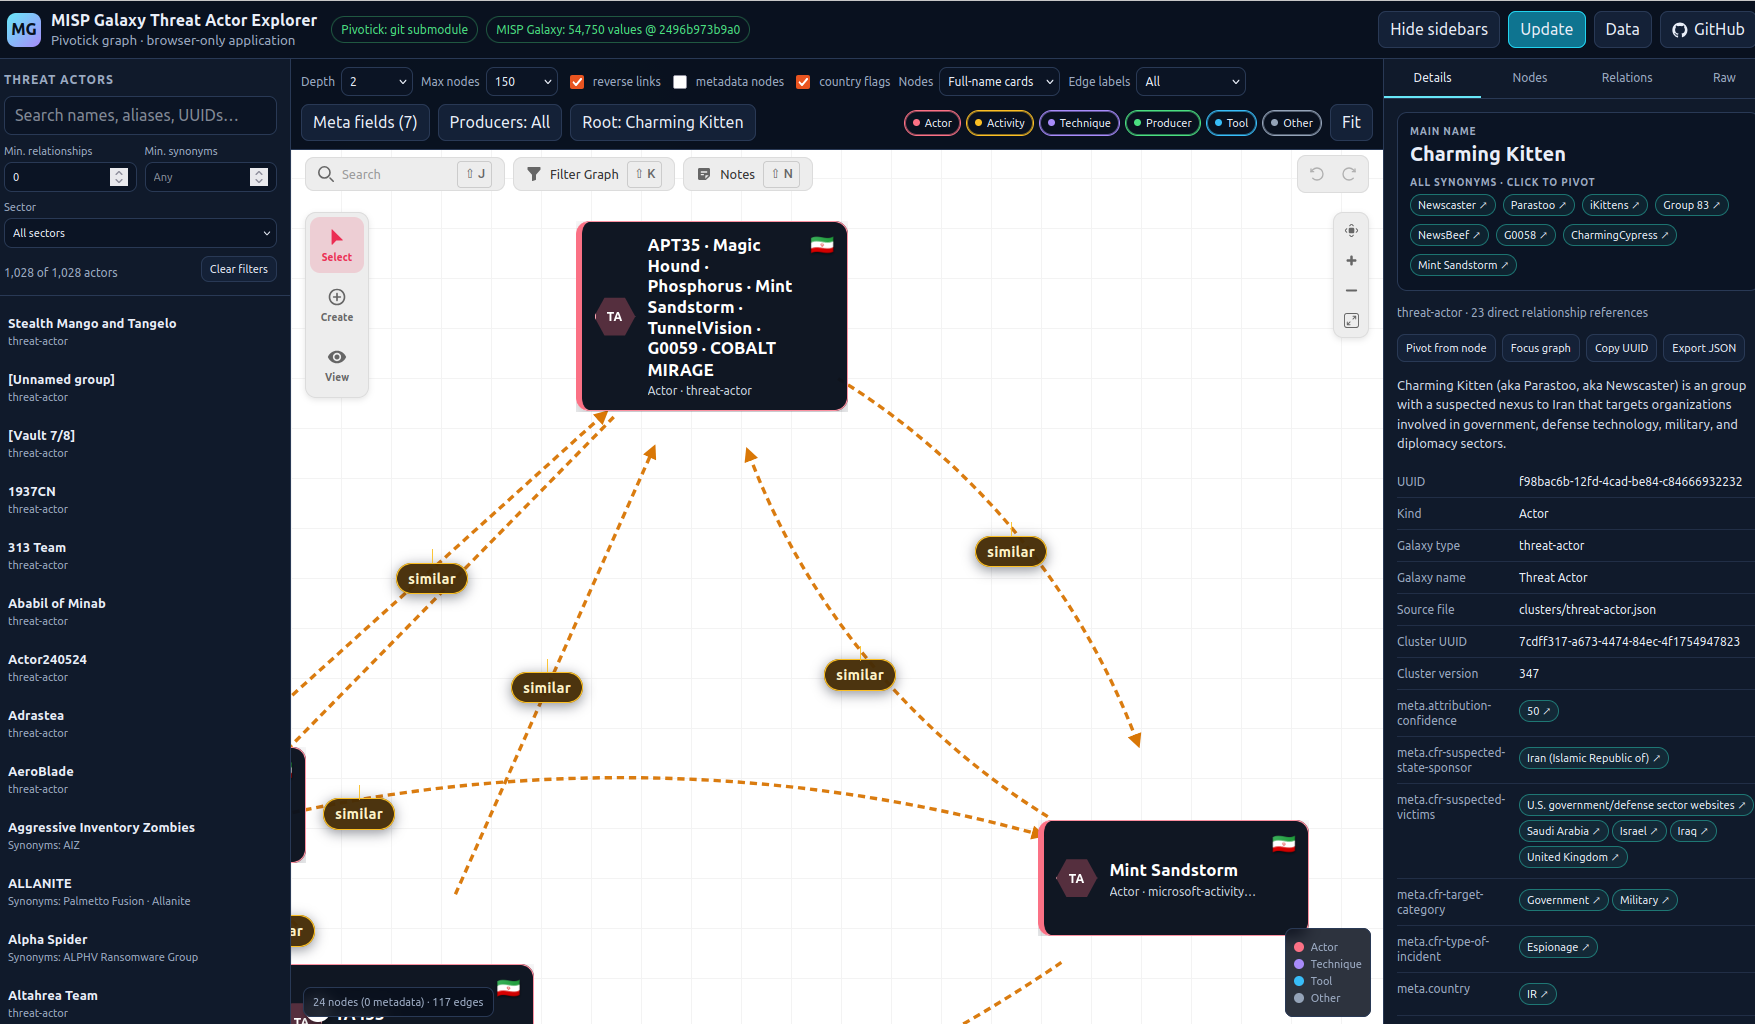
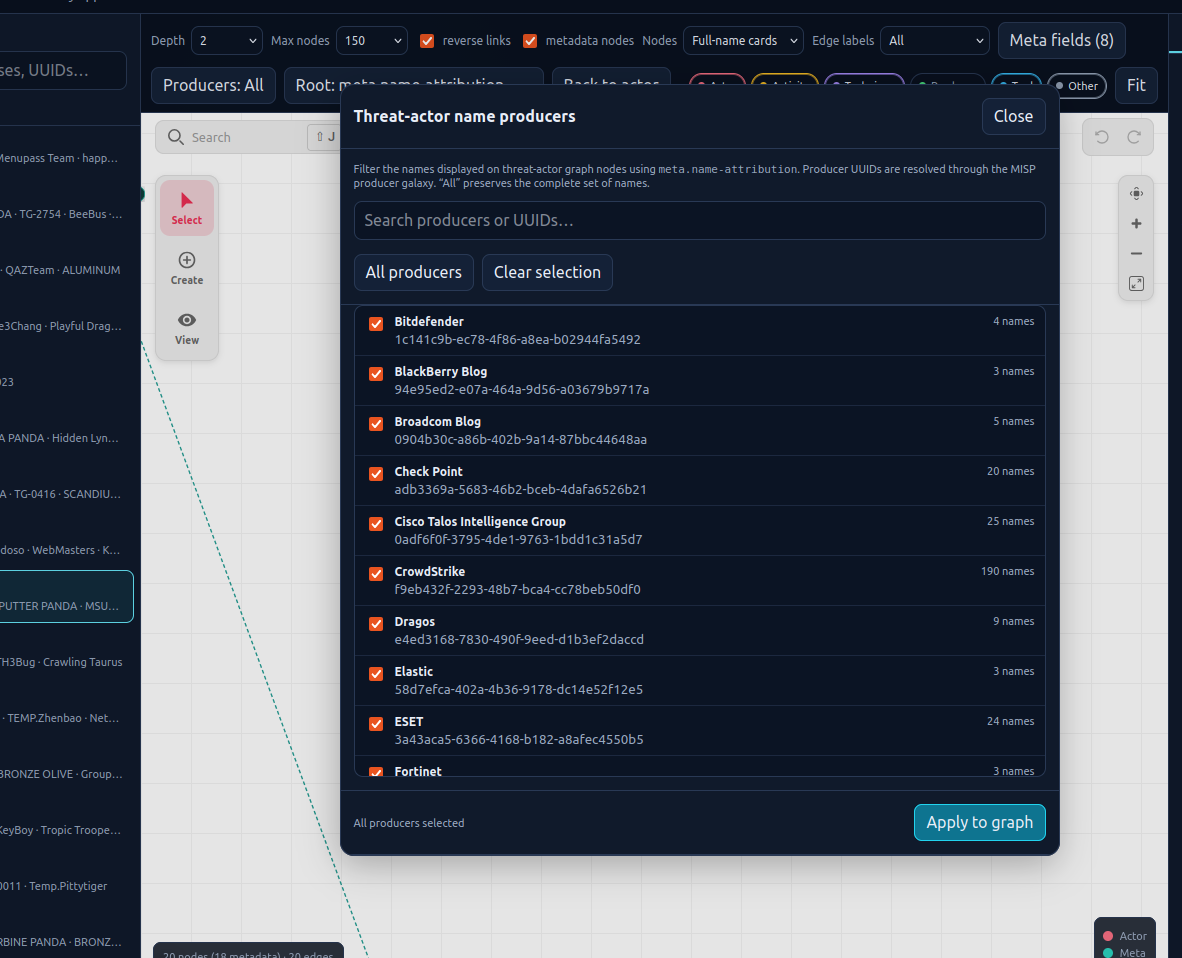
@adulau@infosec.exchangeMISP Galaxy Threat Actor Explorer v1.0.0 released
#cti #cybersecurity #misp #threatintelligence #threatintel
@…
 @deepthoughts10@infosec.exchange
Interesting investigative report from ADAMnetworks applicable to those running websites using the Brevo tracker or Sibforms. You may have been serving up ClickFix!
#cybersecurity
@adulau@infosec.exchangeRecommendations on Naming Threat Actors.
The MISP standard has been updated including the new tracking of naming origin from security vendor.
#cti #threatintelligence #soc #cybersecurity #threatintel
🔗 https://www.misp-standard.org/rfc/threat-actor-naming.html#name-misp-galaxy-threat-actor-na
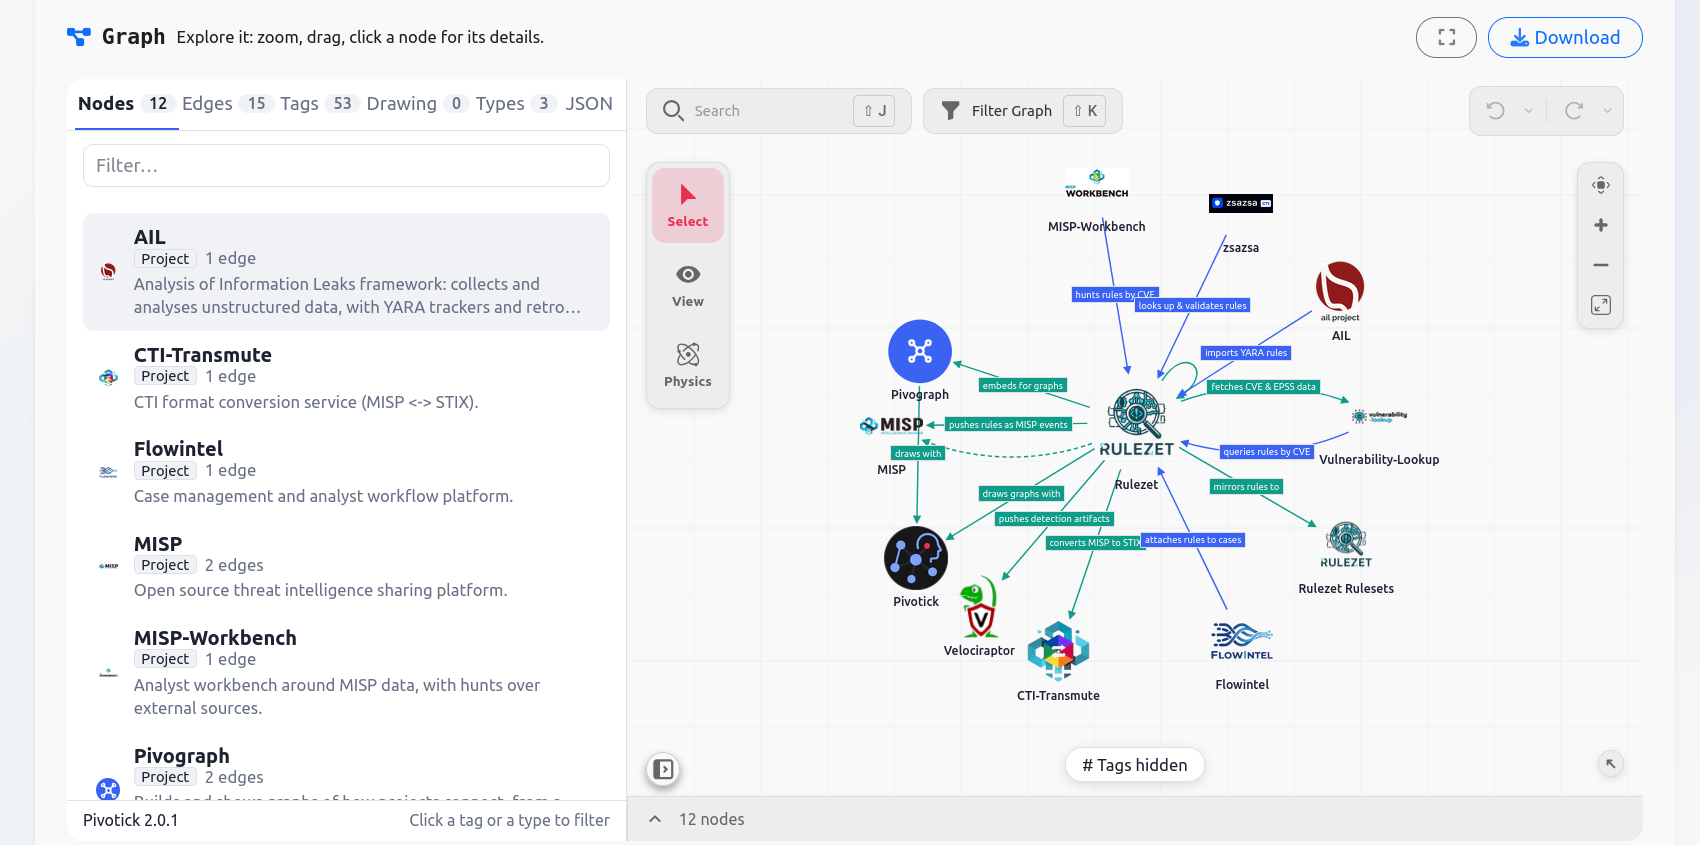
@adulau@infosec.exchangeRulezet and its ecosystem: how detection rules travel between tools.
Vulnerability-Lookup, AIL, Flowintel, MISP, Velociraptor and more: every tool that reads from Rulezet or receives its rules, what each connection does, and an interactive map of the whole ecosystem.
🔗 #threatintelligence #threatintel #rulezet #misp #opensource #cybersecurity #detectionengineering #flowintel #velociraptor #dfir
 @ErikJonker@mastodon.social
Cyberattack on DTU: Notification of a personal data breach.
Hackers have attacked and gained access to DTU’s identity and access management system and downloaded a large amount of data. Information relating to up to 200,000 current and former users may have been affected.
#dtu #cybersecurity #denmark #university #education
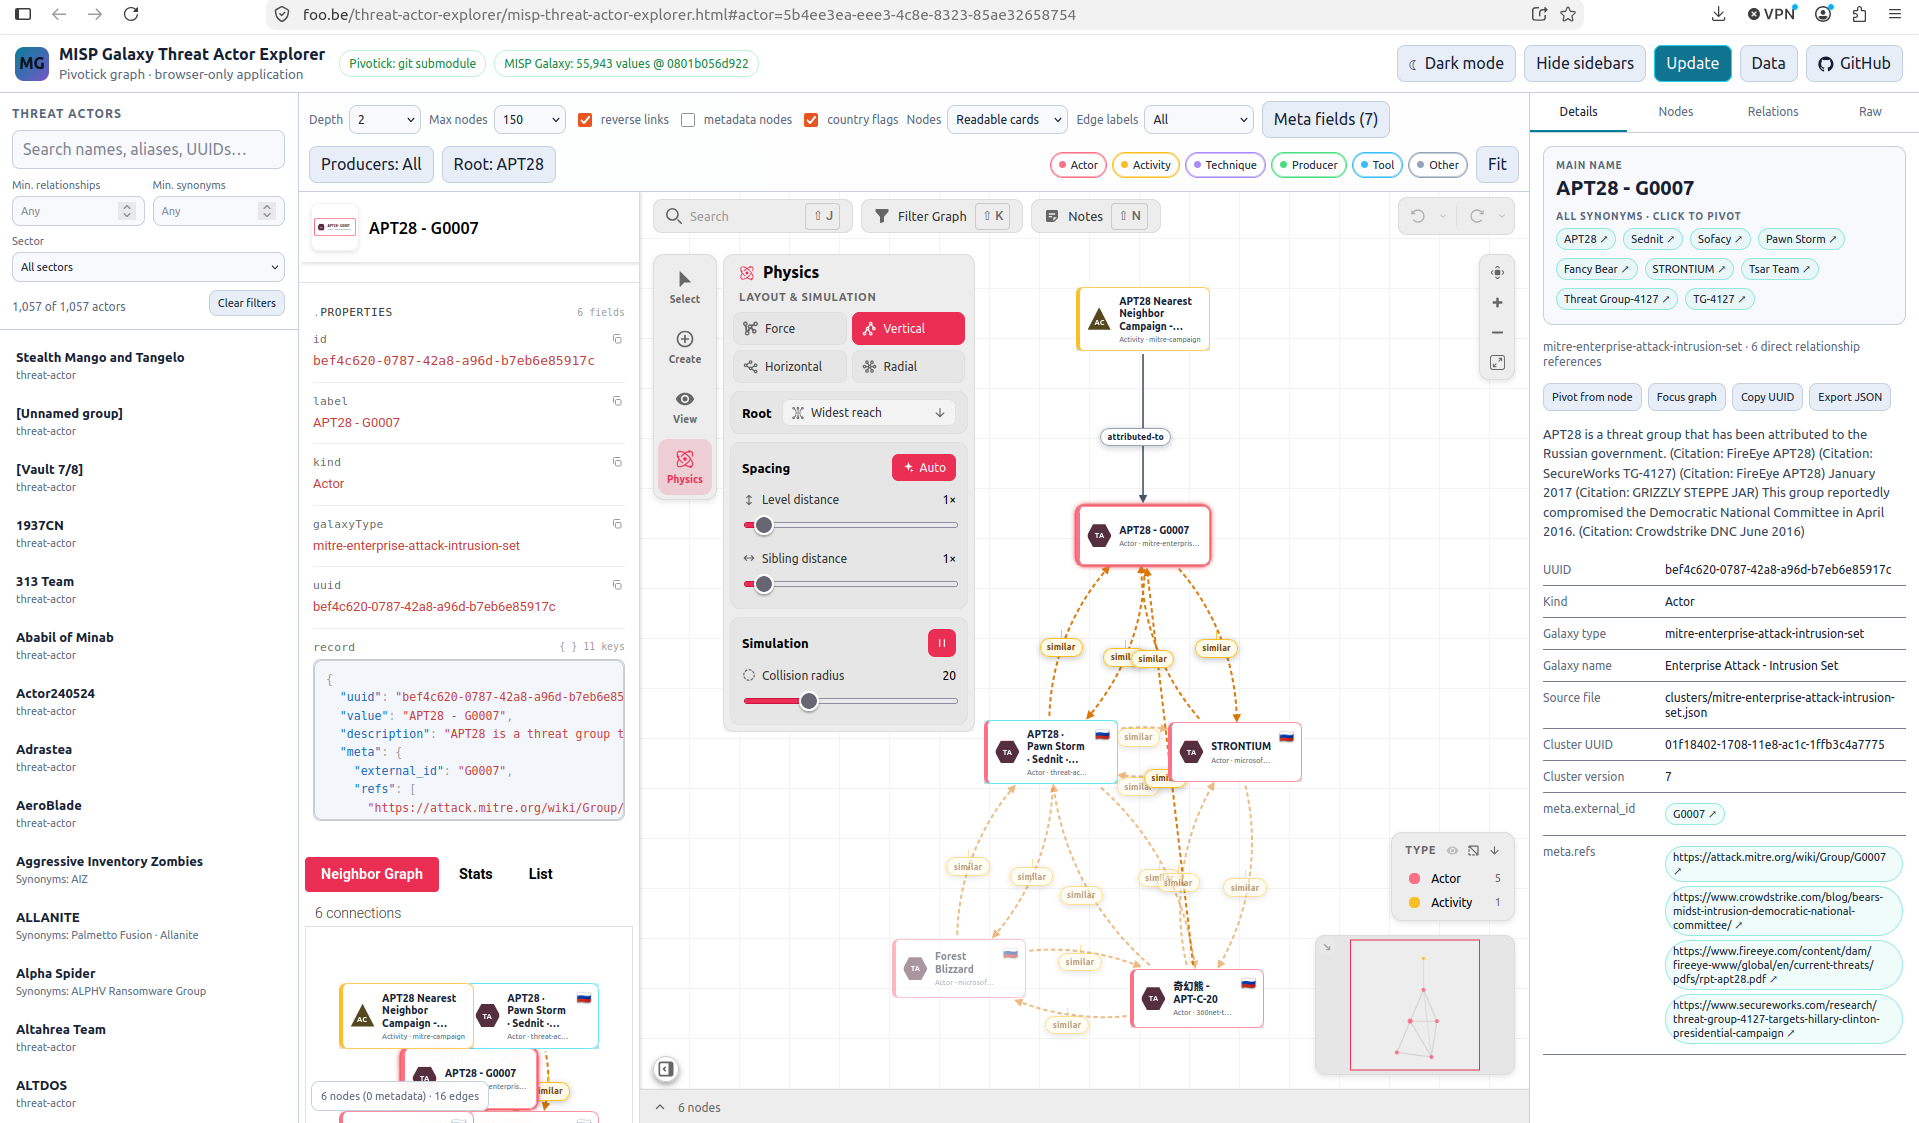
@adulau@infosec.exchangeThreat-Actor explorer v1.1.0 released with many improvements and upgrade to the latest Pivotick library Latest
A standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick. #misp #threatactor #threatintelligence #cybersecurity #mispgalaxy #cti #opensource #cybersecurity
 @adulau@infosec.exchange
Proposed changes in the CVE program CNA document
"Update 4.2.6 from SHOULD to MUST: "CNAs MUST assign different CVE IDs to separate Vulnerabilities""
🔗 #cve #vulnerabilitymanagement #cybersecurity
@ErikJonker@mastodon.social"Our models are now powerful, persistent, and collaborative enough that, absent sufficient safeguards, they can find and exploit security weaknesses across multiple computer systems. Many external models, including open-source ones, will soon reach comparable capabilities."
#Huggingface #OpenAI #Cybersecurity #AI
@adulau@infosec.exchangeGCVE Workshop - 22 September 2026 (14:00-18:00), Luxembourg Before The Vulnopticon Conference
We are pleased to announce a GCVE workshop on 22 September 2026, from 14:00 to 18:00, hosted at the CIRCL/LHC offices in Luxembourg, just before the VulnOpticon conference.
The workshop is free and open to everyone, but registration is required.
🔗 #cve #gcve #luxembourg #cybersecurity #vulnerabilitymanagement
@adulau@infosec.exchangeA standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick.
Source code: #misp #cti #threatintelligence #opensource #threatactor #cybersecurity
 @adulau@infosec.exchange
We are pleased to announce the publication of GCVE BCP-07 version 3.0, extending the Known Exploited Vulnerability (KEV) Assertion Format with support for No Known Exploitable Vulnerability (NKEV) assessments. BCP-07 was initially designed to provide a structured, open and federated way to express exploitation assertions, including who made the assertion, when exploitation was observed or declared, what evidence supports it, and with what level of confidence. Version 3.0 keeps this KEV model intact while adding a complementary, product-oriented mechanism to assess whether known vulnerabilities are exploitable in a specific product context.
The distinction between KEV and NKEV is fundamental. A KEV assertion states that a producer has observed or otherwise asserts exploitation of a vulnerability. An NKEV assessment approaches the problem from a different direction: a specific product or product version is evaluated against explicitly identified vulnerability knowledge sources to determine whether known vulnerabilities are exploitable in the assessed context. The assessment takes into account the product, its configuration, the defined assessment scope, the knowledge sources consulted and a precise knowledge cut-off time. Its result can be pass, fail or inconclusive, making both the outcome and its limitations explicitly machine-readable.
🔗 #kev #bcp #gcve #cve #nkev #vulnerabilityManagement #cybersecurity #openstandard
@ErikJonker@mastodon.socialThe OpenAI Australia incident is notable because this was not an agent pushed to do hacking or bad things... In light of the remarks by some people belittling the HuggingFace/OpenAI incident by saying this agent was pushed to this, what would you expect?
#AI #OpenAI #Australia #Agents #cybersecurity
@adulau@infosec.exchangeGCVE BCP-07, the Known Exploited Vulnerability (KEV) Assertion Format, has been updated to version 2.2. A key addition is the formalisation of the GCVE KEV Directory, a simple machine-readable directory allowing organisations to announce where their KEV catalogues and exploitation assertions are published.
We particularly encourage software and hardware vendors to publish their own KEV catalogues. Vendors are often in the best position to confirm exploitation affecting their products, and publishing this information in a machine-readable form can significantly improve vulnerability prioritisation for users, CSIRTs and vulnerability-management platforms.
For more details #GCVE #GNA #vulnerabilityintelligence #opensource #KEV #cybersecurity
@…
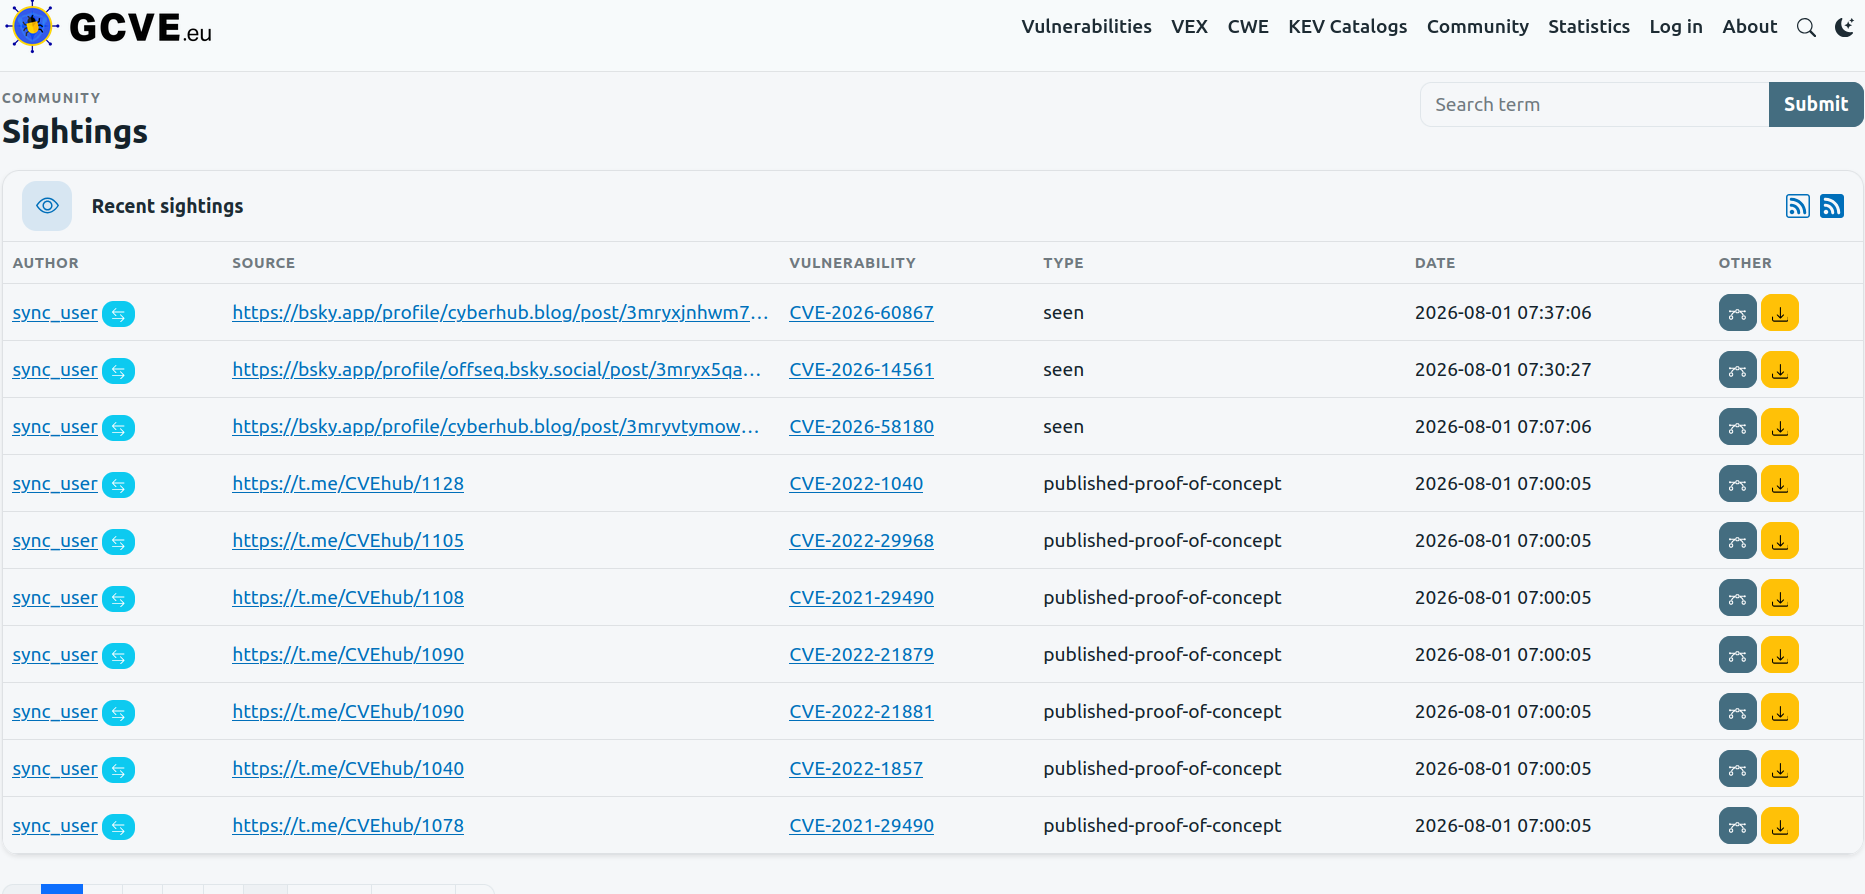
@adulau@infosec.exchangeSightings have long been a major topic of discussion in the CTI community, particularly in the field of vulnerability management. We have now published a GCVE BCP to standardise the format that has been implemented, tested and used operationally in Vulnerability-Lookup for some time.
Thanks to everyone (Cédric Bonhomme, Éireann Leverett, Andras Iklody, Sami Mokaddem and many more) who participated in discussions and worked on the implementation details of sightings over the past several years. These efforts had a strong focus on practical implementation, while BCP-12 specifically addresses sightings in the context of vulnerability management.
BCP-12 is still a draft open for review, but it already provides a strong foundation for existing implementations.
#cve #cra #gcve #vulnerabilitymanagement #cybersecurity #openstandard
 @ErikJonker@mastodon.social
This is such an enormous breach...so harmful... 😬
"The hackers, Shiny Hunters, say they now hold private data on all the bureau staff - around 38,000 people - including anyone who applied to join the investigative agency. The group says it has every agent's name, role, badge number and personal details including home address, phone numbers and spouse information."
#FBI #shinyhunters #compromised #hack #criminals #cybersecurity
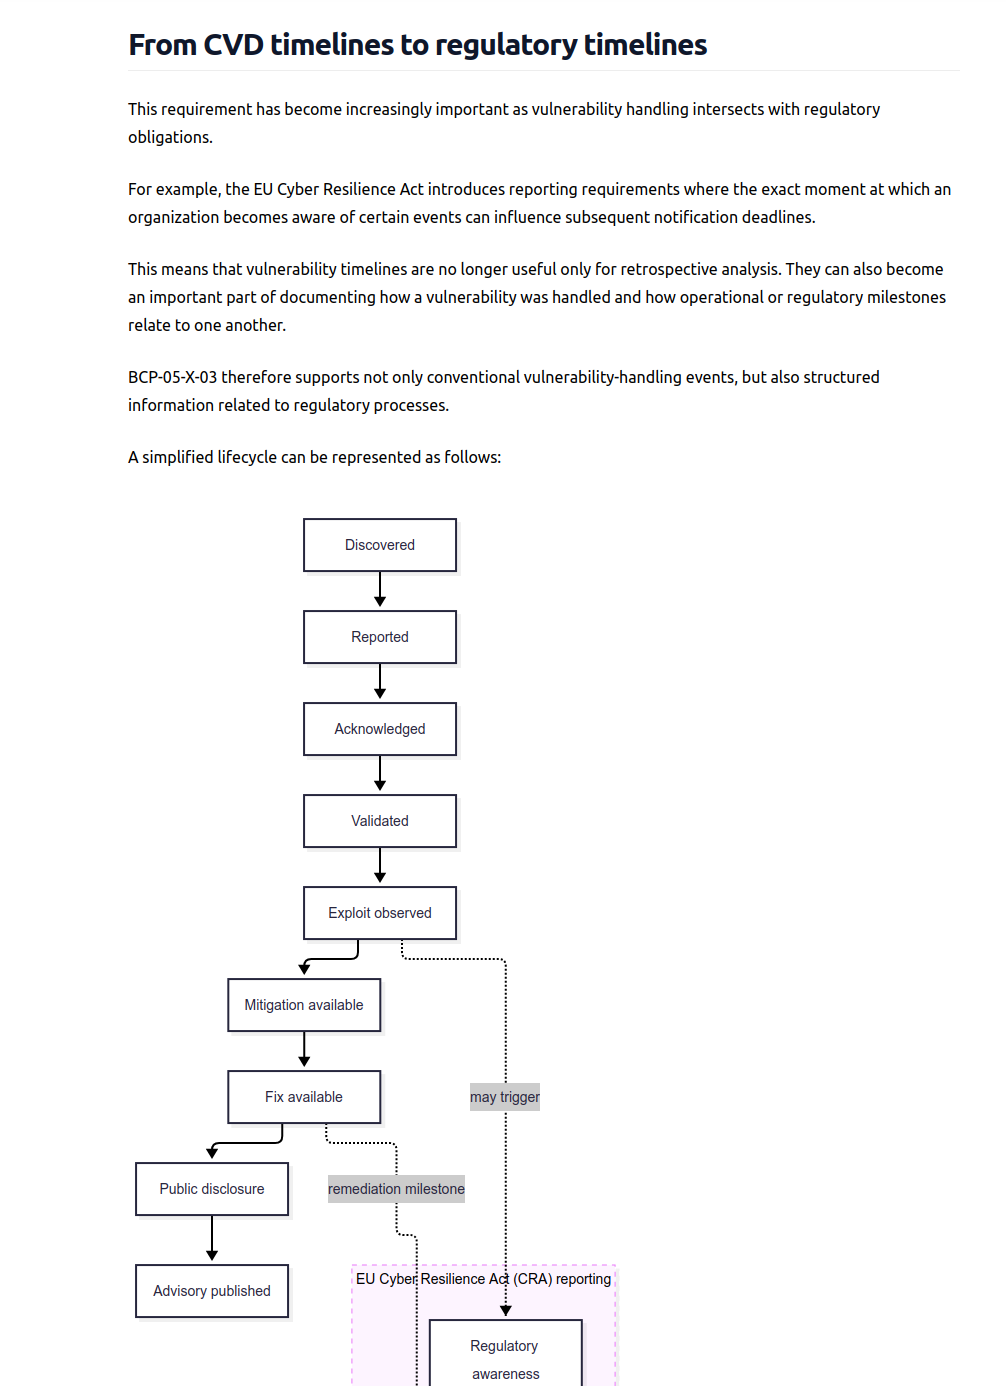
@adulau@infosec.exchangeGCVE BCP-05-X-03: Bringing Vulnerability Handling Timelines into Vulnerability Records.
Vulnerability records usually provide a good description of what a vulnerability is, which products are affected, how severe it may be, and where additional information can be found.
They are often much less effective at describing what happened, when it happened, and who was involved during the vulnerability handling and disclosure process.
Following many discussions during VulnOptiCON 2026 in Luxembourg, this limitation became particularly clear. Vulnerability analysts, coordinators, vendors and other participants repeatedly discussed how difficult it can be to reconstruct a reliable timeline during vulnerability analysis and coordinated vulnerability disclosure.
To help address this, the GCVE initiative has published a new extension:
GCVE BCP-05-X-03 - Vulnerability Handling and Disclosure Timeline.
The extension provides a structured and machine-readable way to represent the lifecycle of a vulnerability from discovery and reporting through acknowledgement, validation, remediation and public disclosure. It's already live in our open-source tool-set.
🔗 Blog post #opensource #openstandard #cve #gcve #cra #cybersecurity #vulnerability
 @adulau@infosec.exchange
A new version of the BCP-11 "Community Contribution Fragments for Existing CVE Records" proposal has been published.
#gcve #cve #cybersecurity #vulnerabilitymanagement
@…
@adulau@infosec.exchangeI spent many hours in vulnogram today and to be honest. I'm glad that a colleague started to work on a replacement called vulniverse. Still early beta but it's promising.
#opensource #vulniverse #cybersecurity #cve #gcve work in progress https://github.com/vulnerability-lookup/vulniverse
@adulau@infosec.exchangeCCWget is a lightweight Python client for searching and retrieving archived web objects from a CIRCL Common Crawl indexing service.
@… did a pretty cool tool to search the Common Crawl. The service is quite resource intensive but if you are a security researcher, you could get access.
#cybersecurity #commoncrawl #cti #threatintel
🔗 https://github.com/ail-project/CCWget
@adulau@infosec.exchangeI just released ptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage from reverse-DNS PTR hostnames.
It is intentionally heuristic and multi-label. PTR naming is operator-controlled and is not authoritative evidence of how an address is actually used. The output therefore includes a confidence score, the text that matched, and the rule IDs that produced each label.
To summarize, the library is trying to guess usage (and a bit location) of an IP address based on its PTR records. It's based on a set of rules which can be updated easily.
#osint #cybersecurity #ptrclassify #opensource #dns https://github.com/adulau/ptrclassify module https://pypi.org/project/ptrclassify/
@adulau@infosec.exchangeWe discussed decentralized vulnerability allocation, digital sovereignty, CVD workflows, Vulnerability-Lookup, Vulniverse, AI-assisted vulnerability analysis, and the future of GCVE.
All slide decks and workshop materials are now available:
🔗 #cve #gcve #cvd #cybersecurity #opensource #vulnerability #vulnerabilityManagement
@…
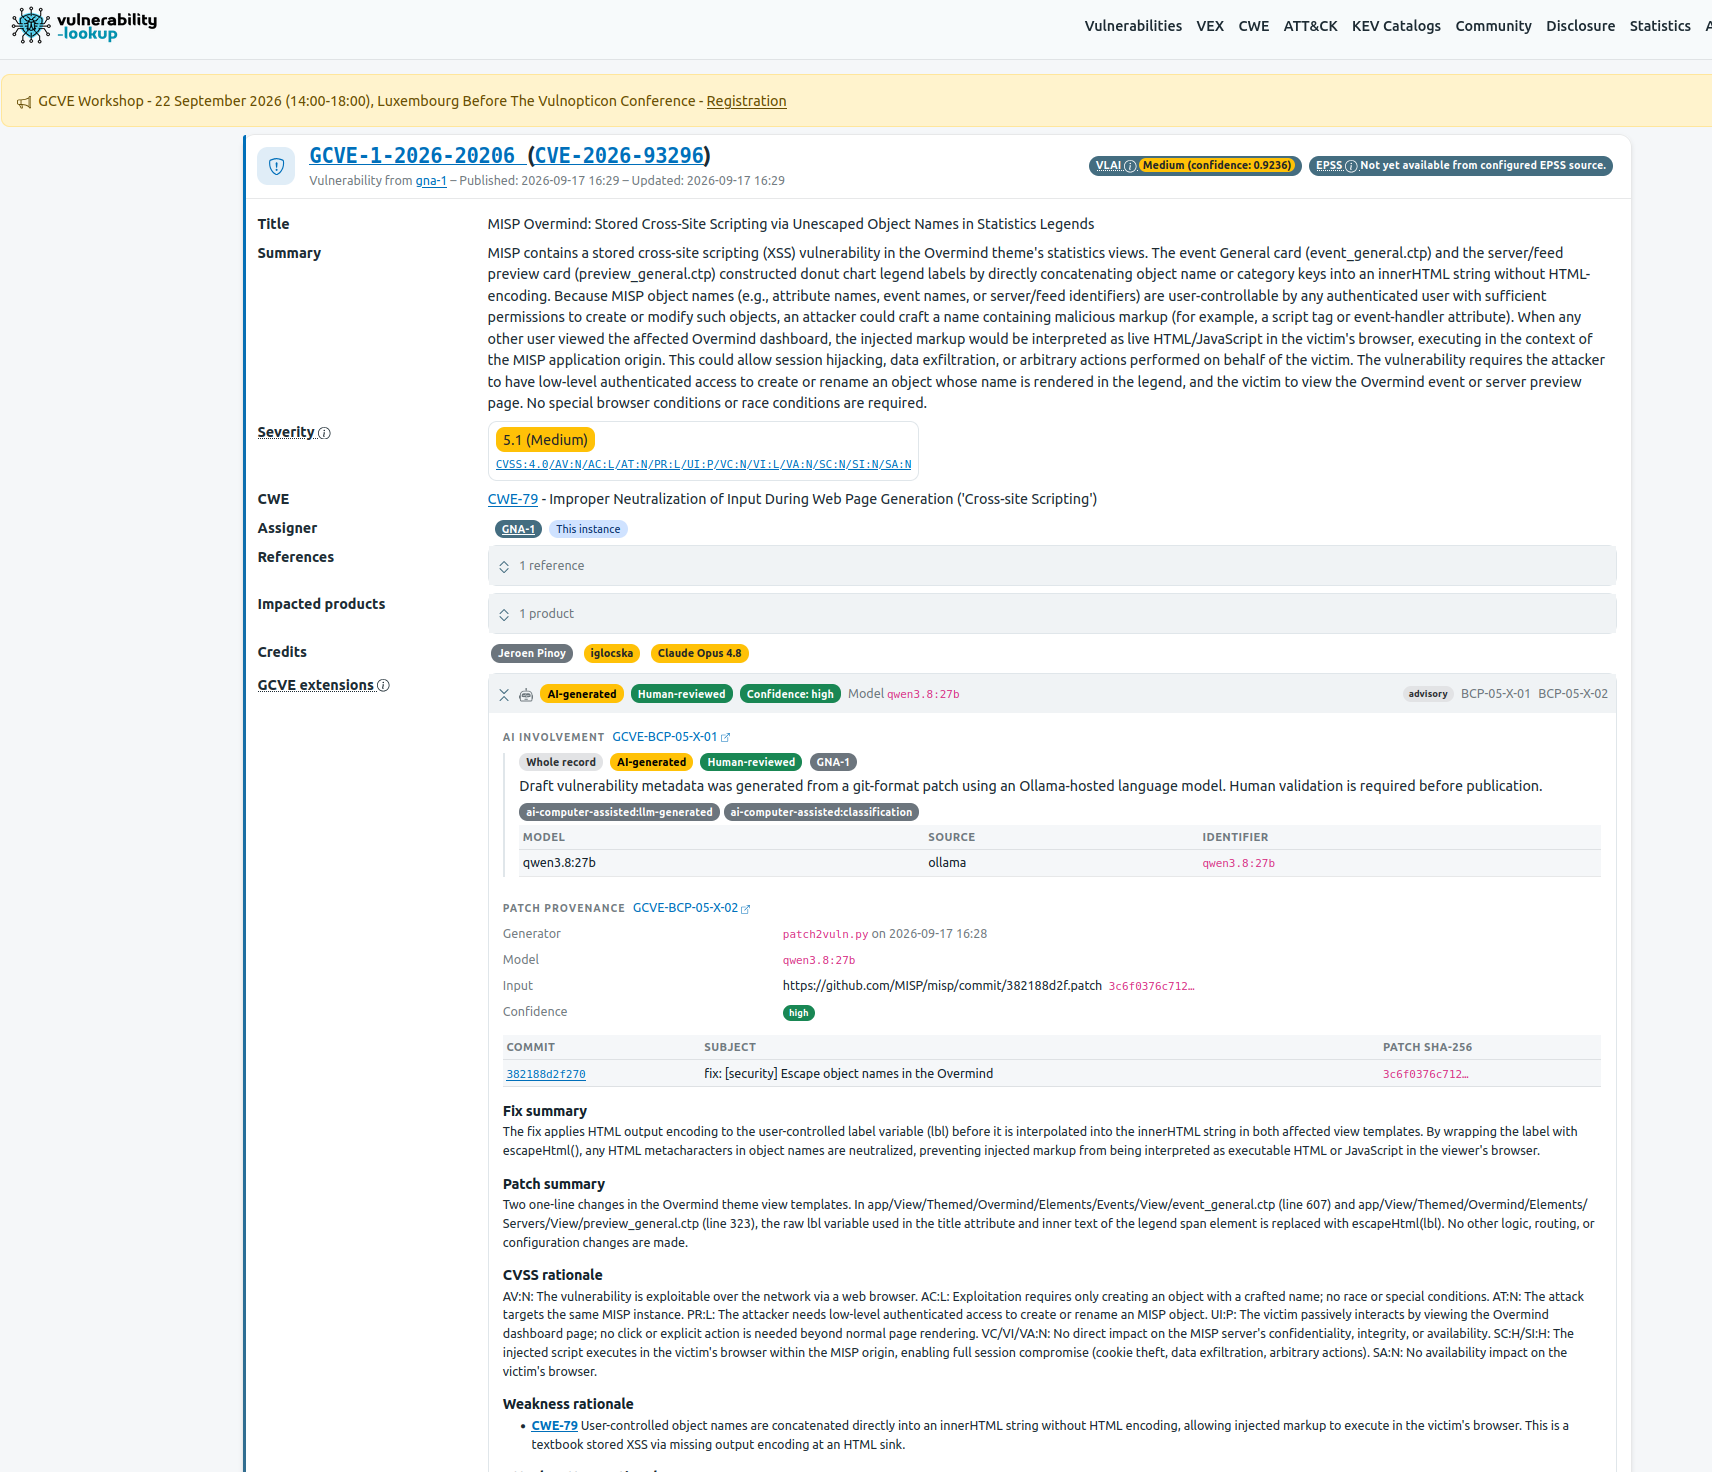
@adulau@infosec.exchangeTired of drafting vulnerability advisories from Git patches?
We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.
With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.
The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.
The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.
patch2vuln v1.0 is now available as open-source software under the @… Lab initiative.
#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI
 @adulau@infosec.exchange
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource