Tootfinder

Opt-in global Mastodon full text search. Join the index!

@deepthoughts10@infosec.exchange
2026-08-19 03:41:49

Good article on a Gen Digital-discovered #phishing campaign. More reason to block *.workers.dev (Cloudflare) as it is a key link in this campaign’s kill chain #cybersecurity
gendigital.com/blog/insights/r

@deepthoughts10@infosec.exchange
2026-08-19 13:04:59

Simple but effective control to help prevent abuse of your business network: disable the remote debugging feature of Chrome and Edge. It disrupts the C2 capabilities described here (but used in other attacks as well)
Look for these settings:
RemoteDebuggingAllowed > Disabled
(Intune: Microsoft Edge > Allow remote debugging)
#cybersecurity

@kubikpixel@chaos.social
2026-06-29 14:05:06

Vibecoding #Malware Fuels a New Wave Of Stealth Attacks
Vibe coding’s dark side, “vibe hacking,” is on the rise. #Cybersecurity companies such as McAfee and Bitdefender have observed recent spikes in vibe-coded malware, also called “

@groupnebula563@mastodon.social
2026-06-30 10:44:47

any #cybersecurity people interested in getting into a webserver in order to rescue a dying website?
boosts appreciated :P
#cybersec #infosec

@GroupNebula563@mastodon.social
2026-06-30 10:44:47

any #cybersecurity people interested in getting into a webserver in order to rescue a dying website?
boosts appreciated :P
#cybersec #infosec

@adulau@infosec.exchange
2026-08-18 20:15:06

CCWget is a lightweight Python client for searching and retrieving archived web objects from a CIRCL Common Crawl indexing service.
@… did a pretty cool tool to search the Common Crawl. The service is quite resource intensive but if you are a security researcher, you could get access.
#cybersecurity #commoncrawl #cti #threatintel
🔗 github.com/ail-project/CCWget

@deepthoughts10@infosec.exchange
2026-09-16 20:01:17

Interesting investigative report from ADAMnetworks applicable to those running websites using the Brevo tracker or Sibforms. You may have been serving up ClickFix!
#cybersecurity

@adulau@infosec.exchange
2026-09-14 16:38:04

hack.lu 2026 agenda is live! (the 20th Edition) including more details about the keynote.
🔗 #conference #hacklu #cybersecurity

@ErikJonker@mastodon.social
2026-08-27 11:40:13

"Aurora ransomware targets ESXi abuses Cursor Agent for exploitation"
#cybersecurity #gambit #AI

@pixelpusher220@dmv.community
2026-07-26 20:20:12

RE: #DataBreach #CyberSecurity

@adulau@infosec.exchange
2026-09-18 14:55:27

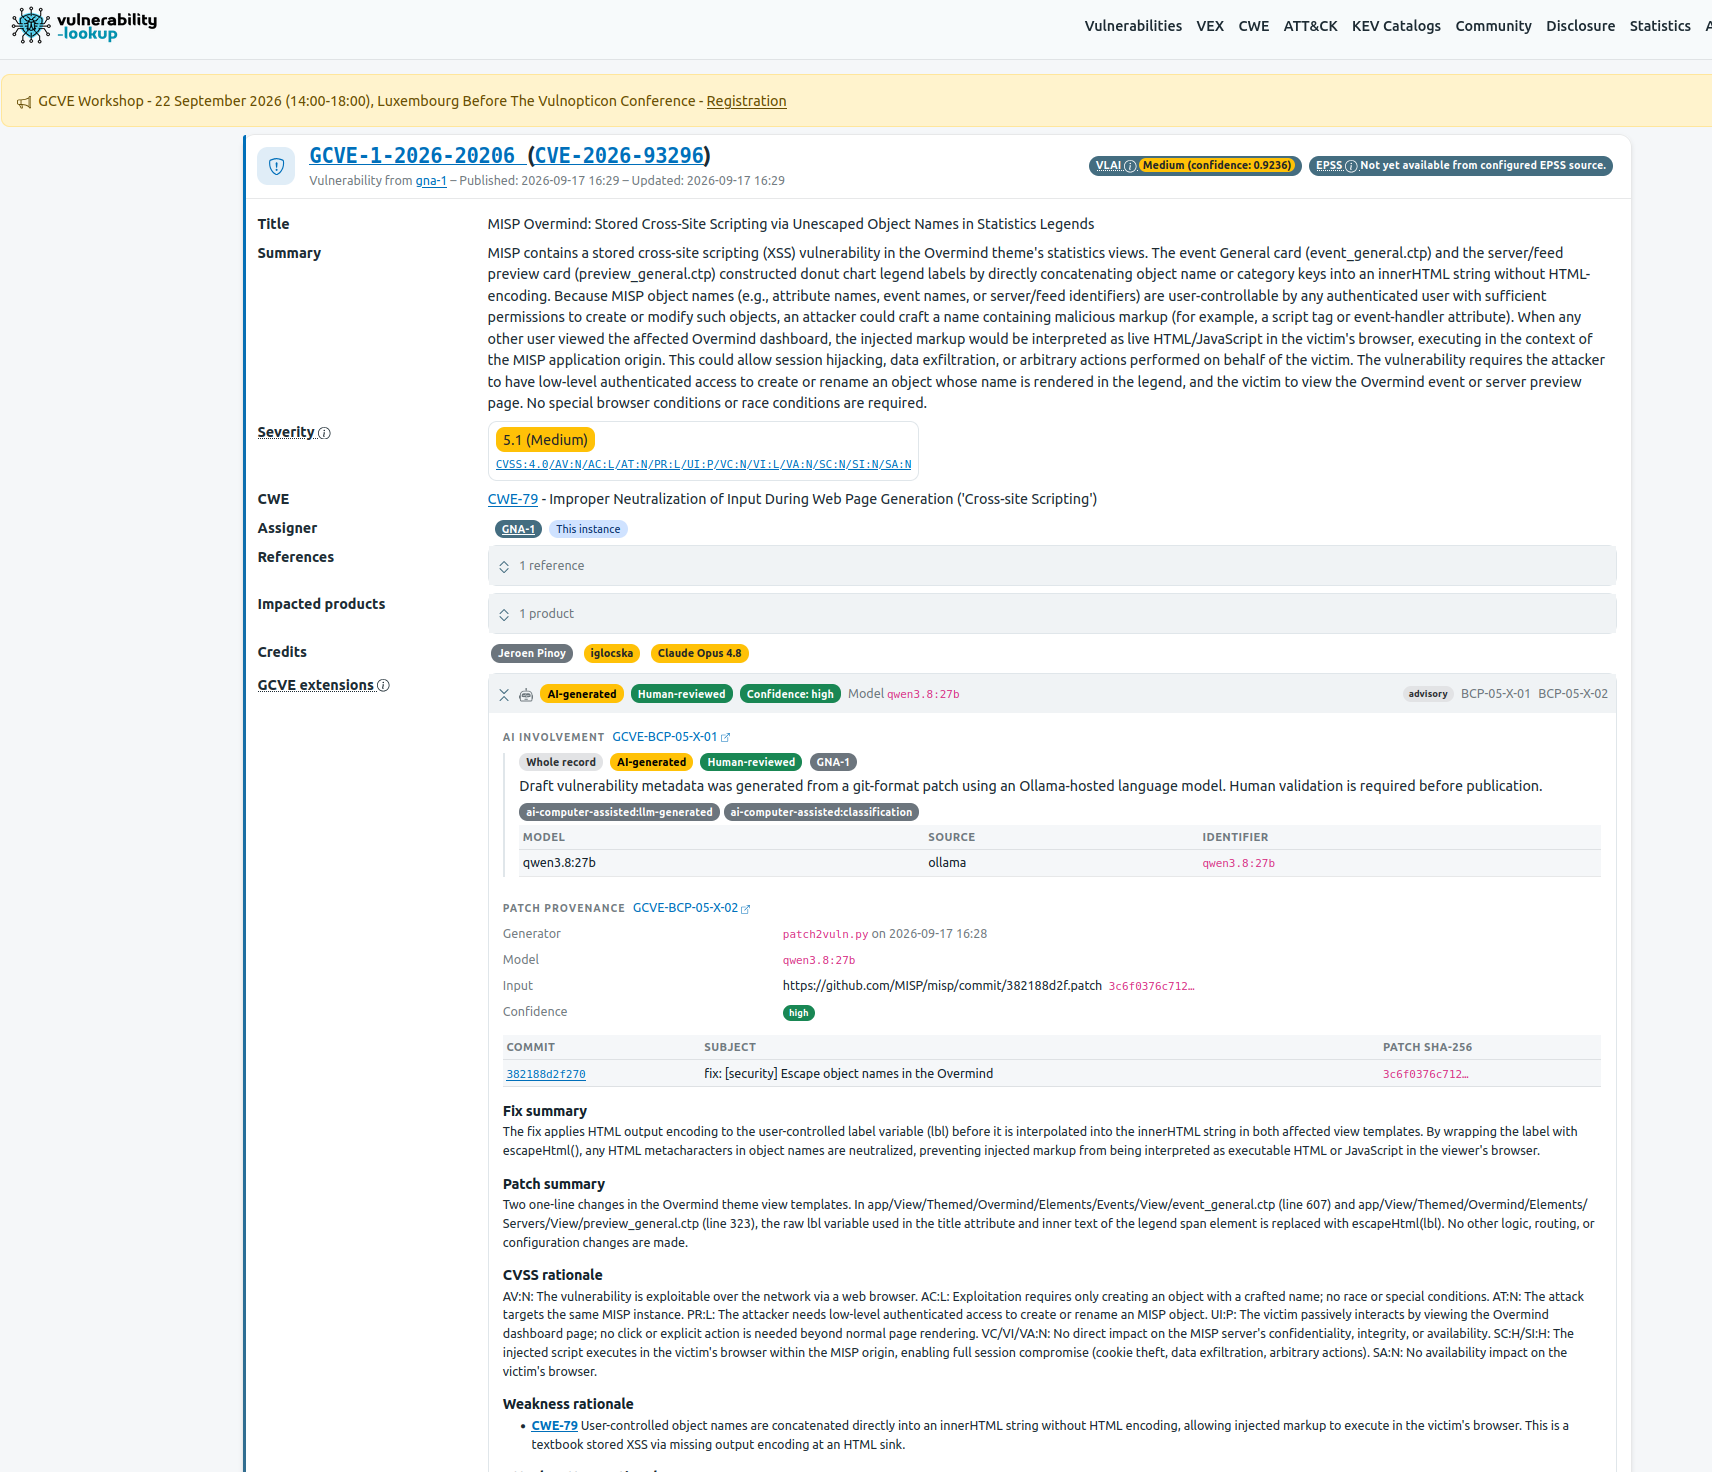
Tired of drafting vulnerability advisories from Git patches?
We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.
With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.
The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.
The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.
patch2vuln v1.0 is now available as open-source software under the @… Lab initiative.
#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI

@deepthoughts10@infosec.exchange
2026-08-12 04:40:50

RE: #cybersecurity #blueteam #ransomware

@deepthoughts10@infosec.exchange
2026-09-09 12:56:34

RE: #cybersecurity

@adulau@infosec.exchange
2026-09-04 13:45:20

ptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage and location from reverse-DNS PTR hostnames.
Version 0.3 released including new rules and CSV tool.
#ptrclassify #infosec #cybersecurity
🔗 github.com/adulau/ptrclassify

@deepthoughts10@infosec.exchange
2026-09-09 01:11:38

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-09-01 23:28:34

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-09-07 22:17:30

RE: #cybersecurity

@adulau@infosec.exchange
2026-07-26 09:40:01

The GCVE Lab is an open space for experimenting with new ideas, tools, formats, and services related to the Global CVE Allocation System initiative.
The lab allows the GCVE community to explore promising concepts without immediately imposing the stability, compatibility, and operational requirements expected from the core GCVE infrastructure.
Open to comments/ideas.
#gcve #cve #cybersecurity
discourse.ossbase.org/t/gcve-l
gcve.eu
@… @…

@deepthoughts10@infosec.exchange
2026-08-04 22:56:12

RE: #cybersecurity

@ErikJonker@mastodon.social
2026-09-04 10:27:31

Scary retelling of the OpenAI/Huggingface incident,
#ai #huggingface #openai #cybersecurity

@castarco@hachyderm.io
2026-08-20 18:40:54

If you are developing in #Rustlang then you should check this post: #cybersecurity #infosec #supplychain #supplychainattack

@deepthoughts10@infosec.exchange
2026-09-01 23:10:52

You should hunt for the MFA-Themed Domains referenced in Palo Alto’s repo:
FQDN - FIRST DATE OBSERVED:
mfaoptions[.]com - 8/26/26
mfa-options[.]com - 8/26/26
mfaregister[.]com - 8/27/26
register-mfa[.]com - 8/27/26
and this one too:
mfa-register[.]com - 8/27/26
#cybersecurity

@deepthoughts10@infosec.exchange
2026-08-31 03:10:59

RE: #cybersecurity at a company and use Intune to manage your desktop/laptop fleet, propose a project for next year to start managing browser extensions. It’s a fair amount of work to get started, but once under management you can put in place processes for your help desk to handle requests for unallowed extensions.
msendpointmgr.com/2025/10/04/t

@deepthoughts10@infosec.exchange
2026-08-31 03:05:43

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-08-31 03:22:25

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-08-31 03:03:36

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-07-28 22:42:52

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-07-28 22:18:07

RE: #cybersecurity

@adulau@infosec.exchange
2026-08-13 15:21:01

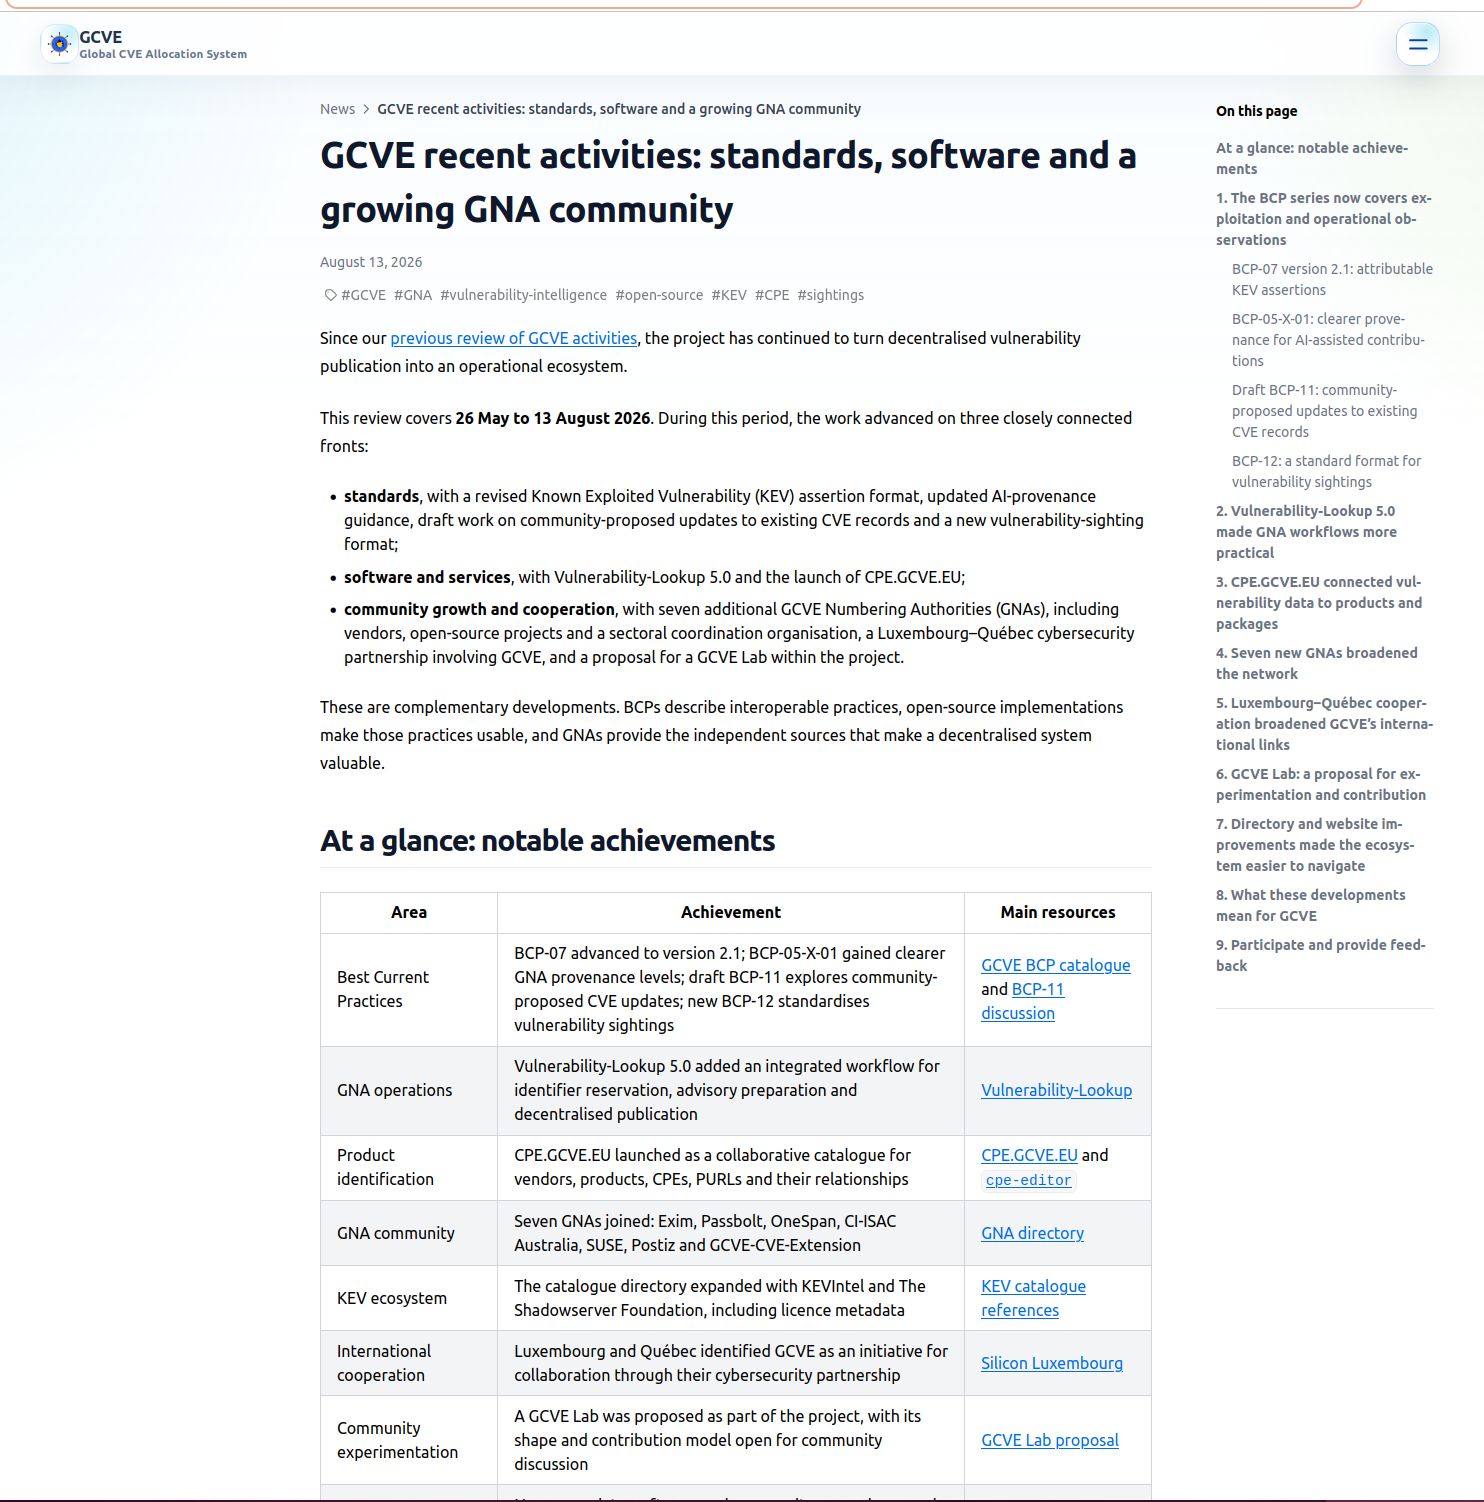
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource

@deepthoughts10@infosec.exchange
2026-07-28 12:42:37

RE: #cybersecurity conference.

@ErikJonker@mastodon.social
2026-08-27 13:01:44

"Our models are now powerful, persistent, and collaborative enough that, absent sufficient safeguards, they can find and exploit security weaknesses across multiple computer systems. Many external models, including open-source ones, will soon reach comparable capabilities."
#Huggingface #OpenAI #Cybersecurity #AI

@deepthoughts10@infosec.exchange
2026-07-28 12:46:06

RE: #cybersecurity

@adulau@infosec.exchange
2026-09-11 20:00:00

I love to see clever use of the @… ecosystem and @… did a cool GNA which is automatically creating GCVE records and structured security advisories from full-disclosure mailing-list or alike:
🔗 Project details #gcve #cve #vulnerability #vulnerability #opensource #cybersecurity

@deepthoughts10@infosec.exchange
2026-07-26 16:12:05

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-07-28 12:53:55

RE: #cybersecurity

@deepthoughts10@infosec.exchange
2026-07-28 13:00:09

RE: #cybersecurity

@adulau@infosec.exchange
2026-09-11 06:10:26

We had difficulties automatically classifying chats, messaging channels, and forums. So we tested several open-weight large language models for our use case. The benchmark is published below, along with a tool supporting the classification process.
This helps us avoid manually classifying channels collected from dark-web forums and social networks, while reliably identifying which channels can be discarded and which deserve further analysis.
🔗 Publication #ai #llm #cybersecurity #darkweb #osint #opensource

@deepthoughts10@infosec.exchange
2026-08-24 12:54:24

RE: #cybersecurity

@adulau@infosec.exchange
2026-09-06 10:17:02

Doing some statistics on the persistence of information published on security and threat intelligence blogs. A surprising number of the domains in the list below are NXDOMAIN nowadays.
Don't assume that security information and threat intelligence will remain accessible over time, especially when it is hosted by large private entities.
Some are simply mistyped, while others reflect DNS changes over time that eventually left the original URLs broken.
Stability and persistence of information is hard on Internet.
#threatintelligence #threatintel #infosec #cybersecurity

  app.response.ncr.com
blog.0x3a.com
blog.anomali.com
blog.cert.societegenerale.com
blog.cylance.com
blog.deniable.org
blog.ioactive.com
blog.jpcert.or.jp
blog.kleissner.org
blog.malwareclipboard.com
blog.malwaretracker.com
blog.passivetotal.org
blog.safebit.mn
blog.team-cymru.org
blog.zimperium.com
blogs.rsa.com
cdn.securelist.com
community.saas.hpe.com
ddos.arbornetworks.com
dnsdb.isc.org
edu.arabsgate.com
info.baesystemsdetica.com
info.isightpartners.com
insider.domaintools.com
ioc.forensicartifacts.com
iranthreats.github.i
joedd.joesecurity.org
lab.anchiva.com
labs.alienvault.com
labs.lastline.com
labs.snort.org
labsblog.f-secure.com
luminosity.link
malware.sekoia.fr
morphick.net
motherboard.vice.com
ocelot.li
permalink.gmane.org
r.virscan.org
remchp.com
research.riskiq.net
resources.infosecinstitute.com
sandbox.deepviz.com
sec.sexy
securityblog.s21sec.com
securityblog.switch.ch
securitydaily.org
sub0day.com
tif.mcafee.com
wepawet.iseclab.org
www.cve.mitre.org
www.cyintanalysis.com
www.cyphort.com
www.icebrg.io
www.infosecdailynews.com
www.isightpartners.com
www.lexsi.com
www.novetta.com
www.packetmail.net
www.root9b.com
www.skycure.com
www.threatexpert.com
www.vxsecurity.sg
@deepthoughts10@infosec.exchange
2026-08-21 04:04:30

Use Defender and Intune? You should be auditing and alerting on high risk administrative actions. Here’s how to do that:
#cybersecurity

@adulau@infosec.exchange
2026-08-04 20:30:25

MISP Galaxy Threat Actor Explorer v1.0.0 released
#cti #cybersecurity #misp #threatintelligence #threatintel
@…

@adulau@infosec.exchange
2026-09-09 14:43:49

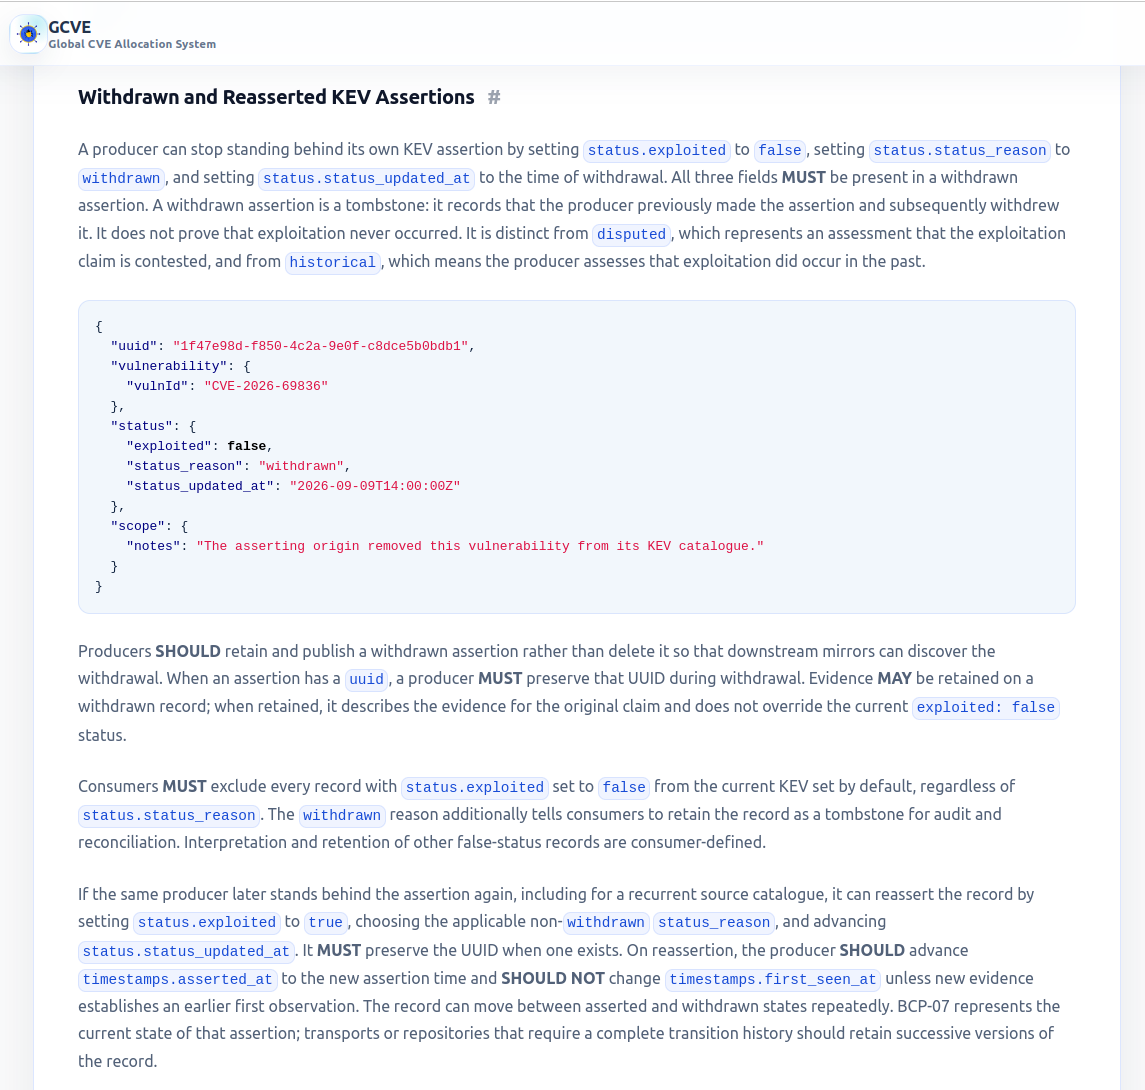
The @… BCP-07 KEV format has been updated to allow the Withdrawn and Reasserted KEV Assertions.
This allows to support case like CVE-2026-69836 .
🔗 #cve #gcve #kev #cybersecurity #vulnerabilitymanagement #vulnerability

@adulau@infosec.exchange
2026-08-06 20:46:11

Recommendations on Naming Threat Actors.
The MISP standard has been updated including the new tracking of naming origin from security vendor.
#cti #threatintelligence #soc #cybersecurity #threatintel
🔗 misp-standard.org/rfc/threat-a

@adulau@infosec.exchange
2026-09-03 04:37:23

Proposed changes in the CVE program CNA document
"Update 4.2.6 from SHOULD to MUST: "CNAs MUST assign different CVE IDs to separate Vulnerabilities""
🔗 #cve #vulnerabilitymanagement #cybersecurity

@adulau@infosec.exchange
2026-09-02 11:46:31

GCVE Workshop - 22 September 2026 (14:00-18:00), Luxembourg Before The Vulnopticon Conference
We are pleased to announce a GCVE workshop on 22 September 2026, from 14:00 to 18:00, hosted at the CIRCL/LHC offices in Luxembourg, just before the VulnOpticon conference.
The workshop is free and open to everyone, but registration is required.
🔗 #cve #gcve #luxembourg #cybersecurity #vulnerabilitymanagement

@adulau@infosec.exchange
2026-08-03 17:34:45

A standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick.
Source code: #misp #cti #threatintelligence #opensource #threatactor #cybersecurity

@adulau@infosec.exchange
2026-09-01 15:33:22

GCVE BCP-07, the Known Exploited Vulnerability (KEV) Assertion Format, has been updated to version 2.2. A key addition is the formalisation of the GCVE KEV Directory, a simple machine-readable directory allowing organisations to announce where their KEV catalogues and exploitation assertions are published.
We particularly encourage software and hardware vendors to publish their own KEV catalogues. Vendors are often in the best position to confirm exploitation affecting their products, and publishing this information in a machine-readable form can significantly improve vulnerability prioritisation for users, CSIRTs and vulnerability-management platforms.
For more details #GCVE #GNA #vulnerabilityintelligence #opensource #KEV #cybersecurity
@…

@adulau@infosec.exchange
2026-08-01 08:20:08

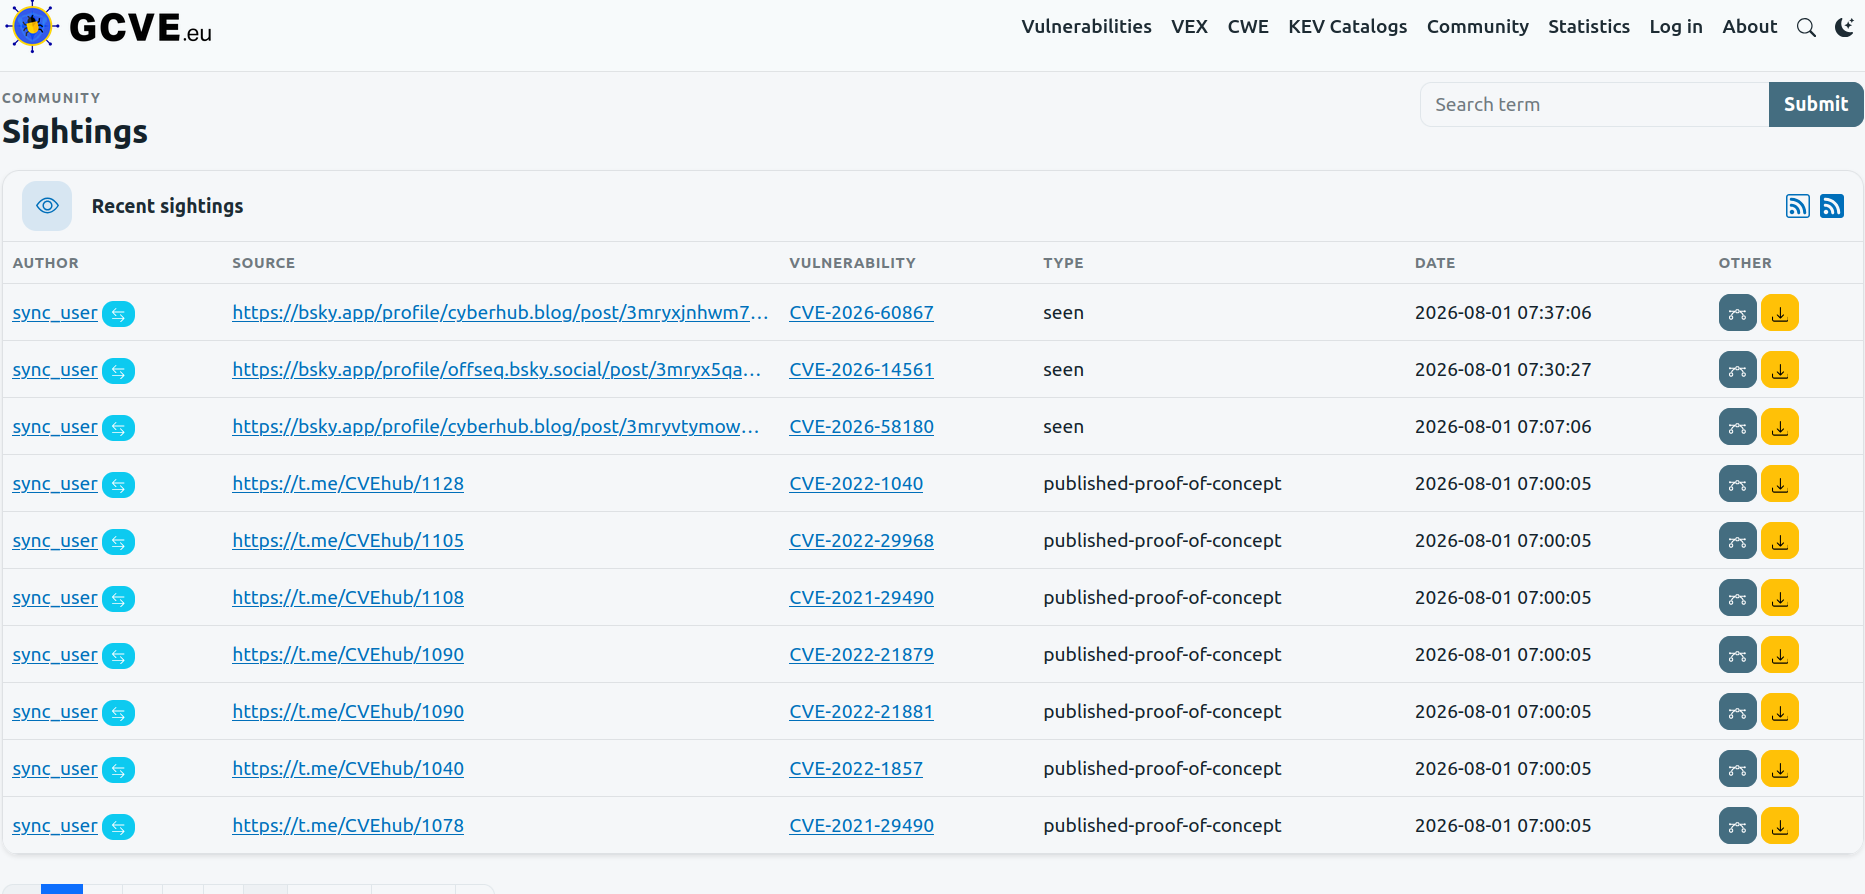
Sightings have long been a major topic of discussion in the CTI community, particularly in the field of vulnerability management. We have now published a GCVE BCP to standardise the format that has been implemented, tested and used operationally in Vulnerability-Lookup for some time.
Thanks to everyone (Cédric Bonhomme, Éireann Leverett, Andras Iklody, Sami Mokaddem and many more) who participated in discussions and worked on the implementation details of sightings over the past several years. These efforts had a strong focus on practical implementation, while BCP-12 specifically addresses sightings in the context of vulnerability management.
BCP-12 is still a draft open for review, but it already provides a strong foundation for existing implementations.
#cve #cra #gcve #vulnerabilitymanagement #cybersecurity #openstandard

@adulau@infosec.exchange
2026-08-24 20:00:49

I spent many hours in vulnogram today and to be honest. I'm glad that a colleague started to work on a replacement called vulniverse. Still early beta but it's promising.
#opensource #vulniverse #cybersecurity #cve #gcve
:github: work in progress github.com/vulnerability-looku

@adulau@infosec.exchange
2026-07-30 06:14:45

A new version of the BCP-11 "Community Contribution Fragments for Existing CVE Records" proposal has been published.
#gcve #cve #cybersecurity #vulnerabilitymanagement
@…

@adulau@infosec.exchange
2026-08-23 09:56:48

I just released ptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage from reverse-DNS PTR hostnames.
It is intentionally heuristic and multi-label. PTR naming is operator-controlled and is not authoritative evidence of how an address is actually used. The output therefore includes a confidence score, the text that matched, and the rule IDs that produced each label.
To summarize, the library is trying to guess usage (and a bit location) of an IP address based on its PTR records. It's based on a set of rules which can be updated easily.
#osint #cybersecurity #ptrclassify #opensource #dns
:github: github.com/adulau/ptrclassify
:python: module pypi.org/project/ptrclassify/