 @frankel@mastodon.top
2026-07-19 16:55:05
@frankel@mastodon.top @TobiasFrech@ijug.social
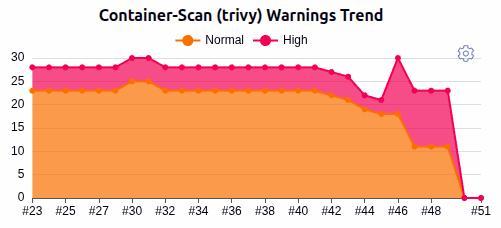
From this perspective, today is a good day! Thanks to a team effort we succeeded in getting the #trivy warnings down to zero before the QS cycle starts.
#security #DevSecOps
 @dankeck@a11y.social
 @crell@phpc.social
 @mgorny@social.treehouse.systems
 @larsfosdal@mastodon.social
 @pixelpusher220@dmv.community
reason 343521562 to never use Comcast
Comcast enabling WIFI motion tracking ability on all Xfinity routers.
Free, but *supposedly* Opt-In.
#Privacy #Security #WifiMotionTracking
@frankel@mastodon.topGuest author Peter Firmstone continues his brilliant series of #Security baked into the #JVM, with his third post: two Subjects, one call
This part covers the two kinds of identity a call carries, how SPIFFE manages process credentials without keystores, and how three identity layers coexist on a singl…
 @patrick_townsend@infosec.exchange
Signal – Don’t forget to configure for privacy
In a business or non-profit environment, there is a good chance that your management team is using Signal. And why not? It brings security and privacy to messaging, file sharing, video and phone calls. Not only can you do one-to-one communications, you can create and manage groups. Sensitive business conversations can remain secret. What’s not to like about that?
Out-of-the-Box Signal needs attention to the configuration settings to get the best privacy. If you are a CISO or IT specialist, you can help your management team configure Signal for the best privacy.
After installing Signal on a mobil phone or desktop, review the configuration settings and adjust them as needed. Here is a free guide that will get you started:
#Security #Privacy #Signal
 @michabbb@social.vivaldi.net
🔐 Hermes Vault: a local-first credential broker and encrypted vault for AI agents. It scans for plaintext secrets, brokers policy-gated access and proves audit integrity.
#opensource #security #MCP
 @cyrevolt@mastodon.social
I can't stop saying the NVRAM vars are a tough #UEFI attack surface, and if processed wrong, may undermine all #security:
https://kb.cert.org/vuls…
 @jake4480@c.im
 @khalidabuhakmeh@mastodon.social
 @curiouscat@fosstodon.org
"The TSA has an important job to do. Their actions at airports have been very poor. This creates lots of loss to travelers – waste. And their actions show a disrespect for people and the risks that exist. The #security theater is not what we need. We need evidence based security measure while maintaining a focus on the value stream of people flying."
 @kubikpixel@chaos.social
If you ask me, it's advertising #propaganda and not a real call for respectful #security. Above all, AI is only so "smart" to what amount it is fed with #data in which context.
«Time is runn…
 @publicvoit@graz.social
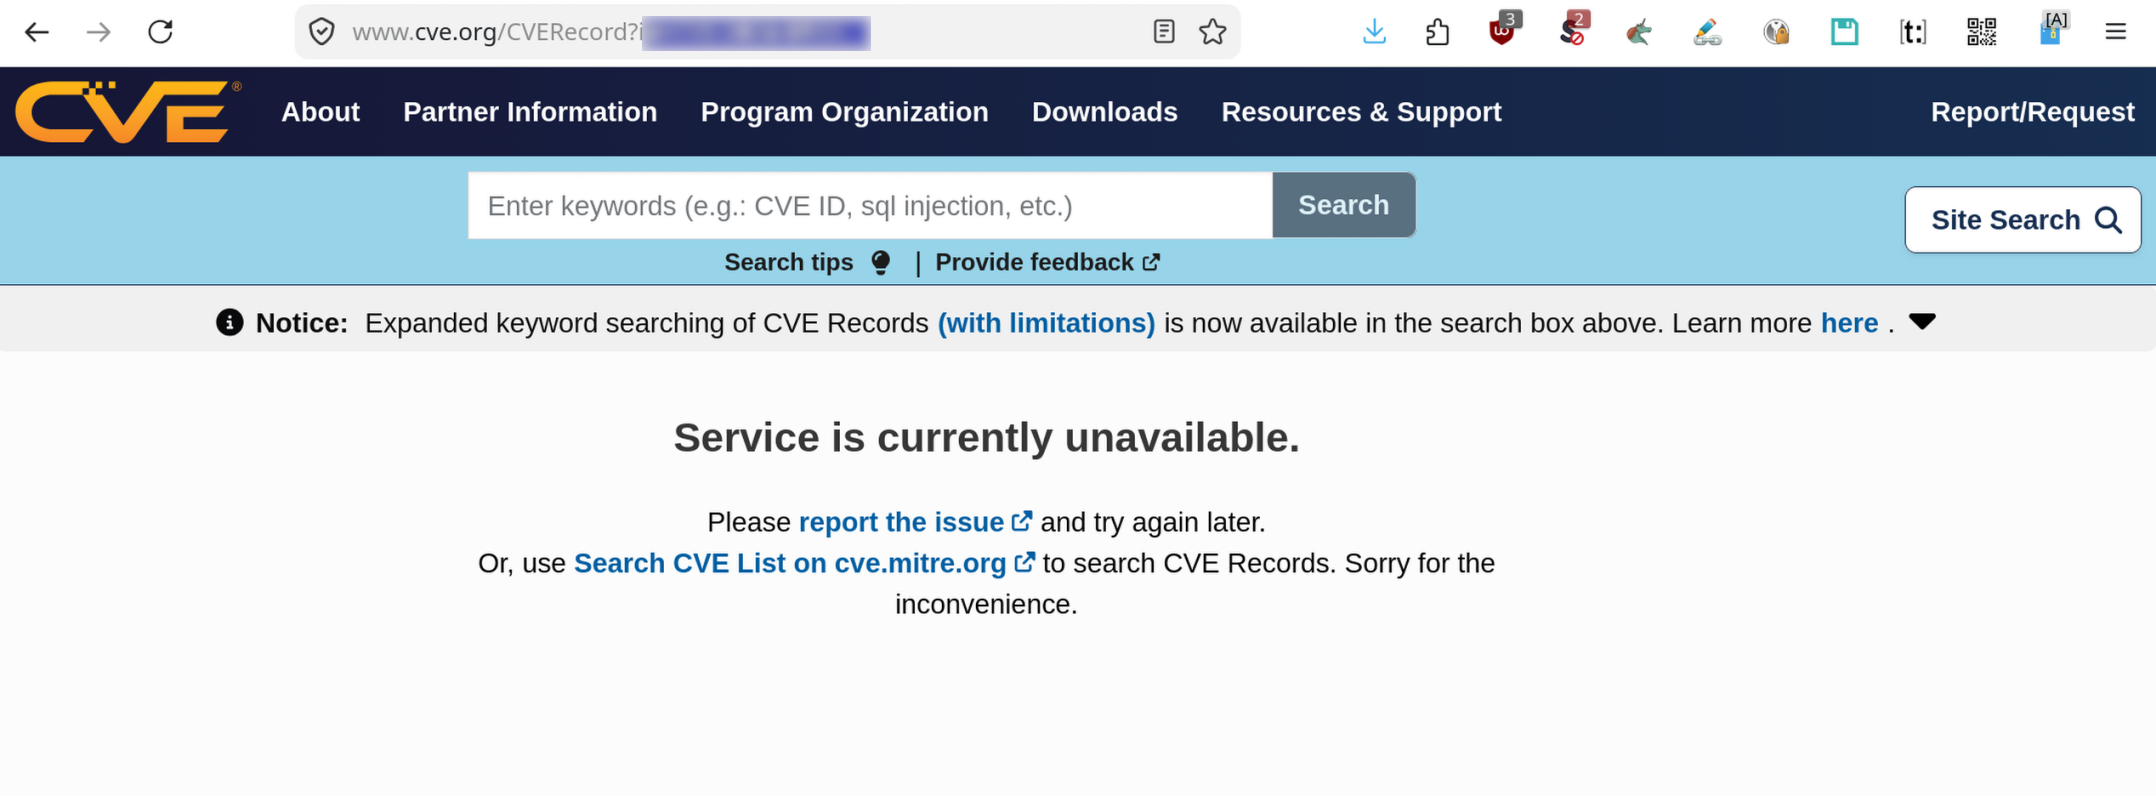
This is what cve.org is showing when I don't allow JavaScript execution for a third party domain (mitre.org) in my LibreWolf browser: "Service is currently unavailable." 🤦♂️
I guess the #security community should do better than that.
And yes, when JavaScript is disabled for cve.org, I do get a helpful message that informs me that the web site can't work without JavaS…
 @frankel@mastodon.top @mgorny@social.treehouse.systems
Dependency cooldowns are a nice idea, but I dare say they're a short-term solution.
They resemble the idea of avoiding poison by waiting for someone else to start eating first. That works, provided that someone actually eats first, and that the poison works fast. But eventually it leads to that awkward silence at the table when nobody wants to risk the first bite.
Adapting dependency cooldowns means basically waiting for "someone else" to notice the problem. At some point when large enough number of projects adapts them, we're going back to square one — except with an artificial few-day delay.
#security #FreeSoftware
@cyrevolt@mastodon.social @frankel@mastodon.top @khalidabuhakmeh@mastodon.social @stephane_klein@social.coop
« J'ai découvert cc-safety-net : des hooks pour sécuriser les agents IA »
#security
 @geant@mstdn.social
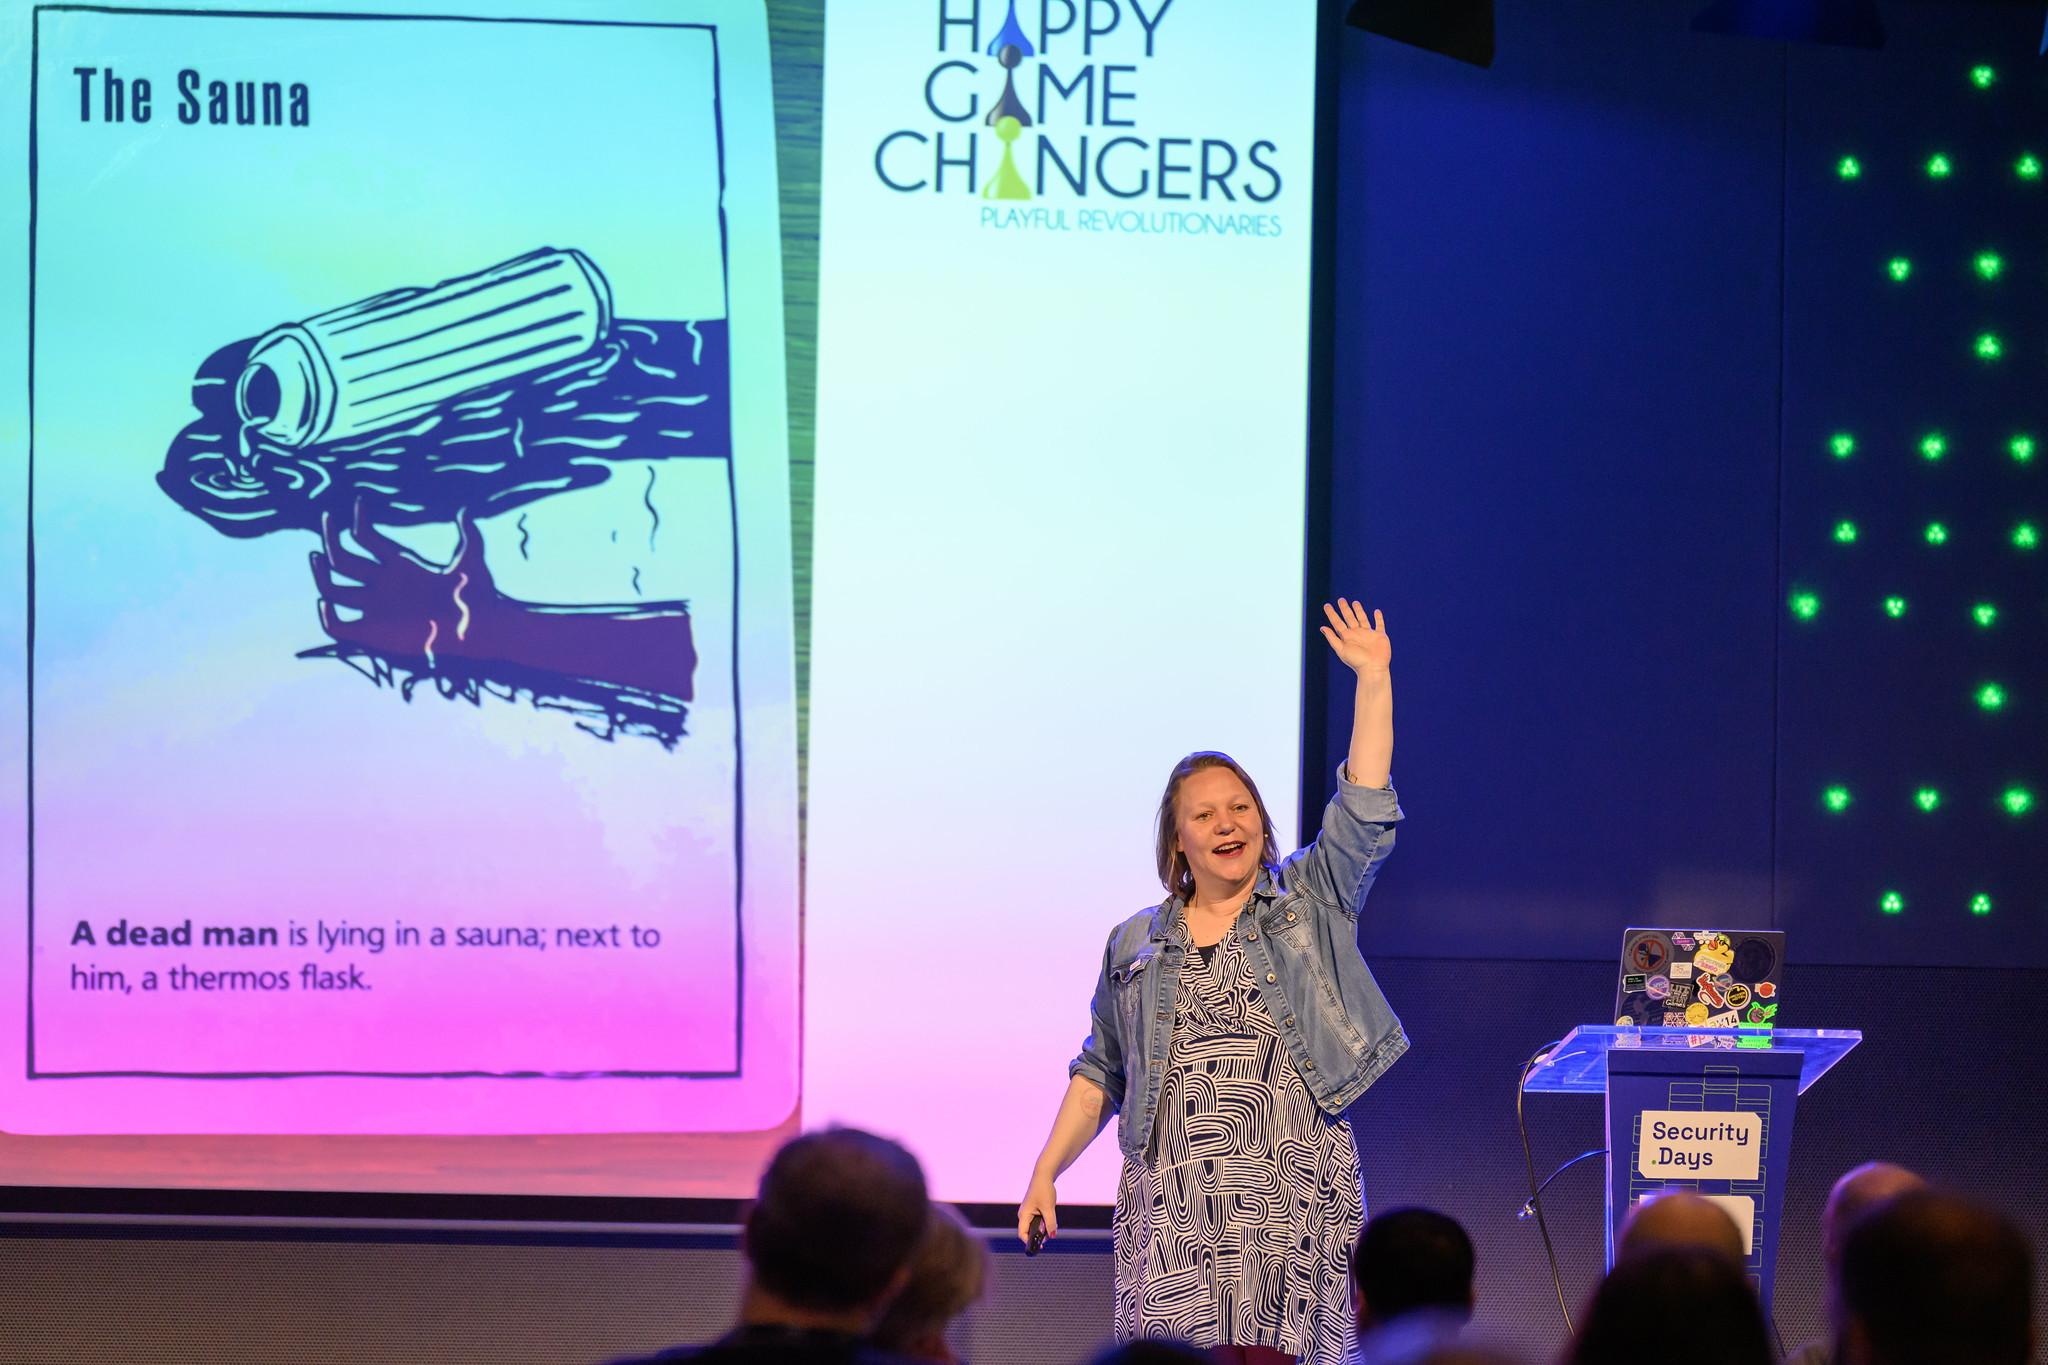
Nancy Beers' keynote at #SecurityDays 2026 had the whole room on its feet, playing games and laughing together.
We spoke with her recently to learn more about what "Play More Today. Secure Tomorrow" means for security culture, from how a simple box of LEGO bricks can make abstact discussions come alive, to why she believes cybersecurity can't exist in silos.
🔗 Re…
 @ruth_mottram@fediscience.org
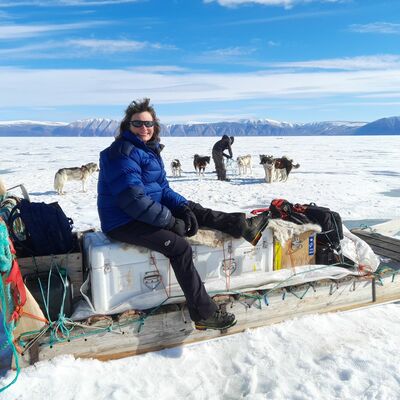
More than mildly alarmed listening to this episode on the #Arctic #Europe and #Russia #Ukraine and #HybridWar, #Security and lots of other very very interesting items. *Essential* listening for anyone concerned with European security.
Mildly Alarmed: Russian nukes and spies in the Arctic, with The Barents Observer
https://podcasters.spotify.com/pod/show/mildly-alarmed/episodes/Russian-nukes-and-spies-in-the-Arctic--with-The-Barents-Observer-e3l00hr
Media file: https://anchor.fm/s/111aff124/podcast/play/121683963/https://d3ctxlq1ktw2nl.cloudfront.net/staging/2026-5-18/426419250-44100-2-05b100b5043df.mp3
@pixelpusher220@dmv.community#Security #PasswordManager
Random question for those who use a browser plugin for a dedicated manager like BitWardon or LastPass or whatever.
How does this handle security vs the built in browser manager?
I know the in browser ones are not recommended and curious how having a plug-in to the BitWarden/LastPass 3rd party is different?
@mgorny@social.treehouse.systemsHonestly, what kind of scam #Akamai / #LInode is? They give you a form to report malicious activity from their network, you file it, you get "Error message to be decided", and it turns out they've banned you in the meantime; all their websites give you "Access denied".
And they host an exploit since 2021 at least: #security #abuse
 @ErikJonker@mastodon.social
Reading this, people could actually think Anthropic helps them keeping their data safe. However you still have to trust Anthropic itself that has access to all your data when using their AI or am i misreading it?
#AI #Anthropic #EFS #privacy #security
@pixelpusher220@dmv.community#BigTech #Billionaires #EatTheRich #Security #Win10 #TechSupport
So some press covered Zuckerberg's mega yacht not responding to a distress call and rightfully saying the Law Of the Sea requires aid to be rendered if possible.
Now, there's apparently a Win10 zero-day vulnerability in the wild. A vulnerability that Microsoft HAS A FIX FOR.
And yet they won't allow you to run it if you haven't paid up for support.
They should be REQUIRED TO RELEASE the fix to all.
 @randombaywatch@mastodon.social
#BikiniBeauty
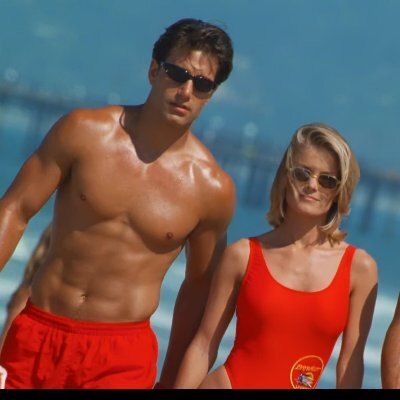
Season 3 Episode 14 "Strangers Among Us"
#Security #RandomBaywatch #lvdlpx #Baywatch #BaywatchKittens #Gorgeous #BaywatchBabes #hot #sexy #swimsuit #BaywatchBoobs #Headlights #Bikini #Beauty #StrangersAmongUs