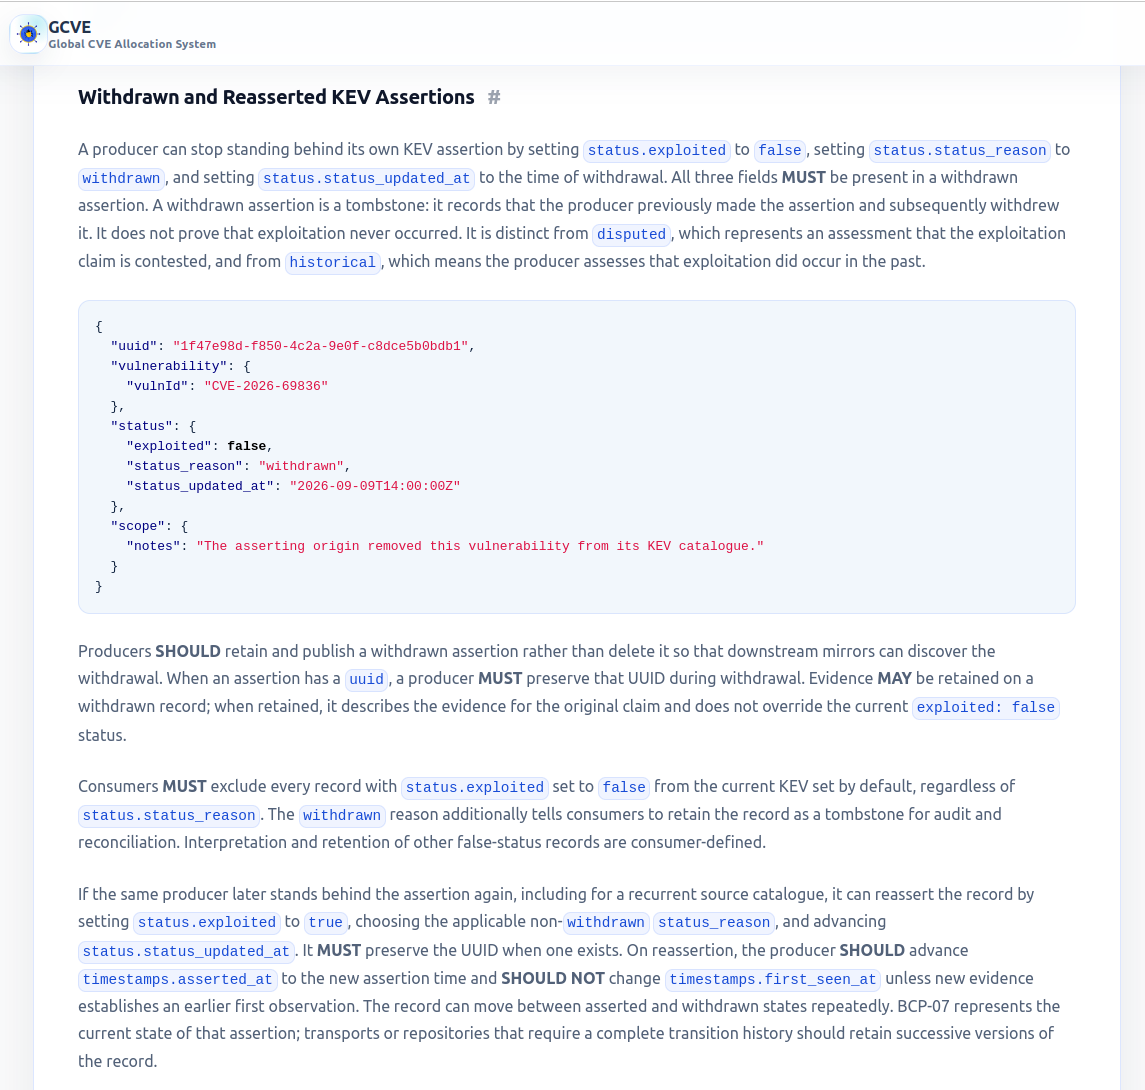
We are pleased to announce the publication of GCVE BCP-07 version 3.0, extending the Known Exploited Vulnerability (KEV) Assertion Format with support for No Known Exploitable Vulnerability (NKEV) assessments. BCP-07 was initially designed to provide a structured, open and federated way to express exploitation assertions, including who made the assertion, when exploitation was observed or declared, what evidence supports it, and with what level of confidence. Version 3.0 keeps this KEV model intact while adding a complementary, product-oriented mechanism to assess whether known vulnerabilities are exploitable in a specific product context.
The distinction between KEV and NKEV is fundamental. A KEV assertion states that a producer has observed or otherwise asserts exploitation of a vulnerability. An NKEV assessment approaches the problem from a different direction: a specific product or product version is evaluated against explicitly identified vulnerability knowledge sources to determine whether known vulnerabilities are exploitable in the assessed context. The assessment takes into account the product, its configuration, the defined assessment scope, the knowledge sources consulted and a precise knowledge cut-off time. Its result can be pass, fail or inconclusive, making both the outcome and its limitations explicitly machine-readable.
🔗 #kev #bcp #gcve #cve #nkev #vulnerabilityManagement #cybersecurity #openstandard
 @adulau@infosec.exchange