 @frankel@mastodon.top
2026-08-22 17:17:10
@frankel@mastodon.top @a@paperbay.org
Is there somewhere a good open source software in Python to act as bridge between RSS and ActivityPub act as actor? Before I write something new.
#activitypub #opensource #rss
 @michabbb@social.vivaldi.net
🐝 #SwarmForge is an #opensource agent coordination system that turns swarms of #AI agents into a disciplined engineering team, built on
@michabbb@social.vivaldi.net📋 #Autoprompt is an #opensource coding-agent skill that cut failures by 45% on agentic coding tasks #aiagents
@michabbb@social.vivaldi.net📋 #FreeToken is an edge-native #MoE serving engine for running frontier-scale open-weight models on personal, consumer hardware #opensource
@frankel@mastodon.top @rasos@fairmove.net
Soll ich wieder einen Vortrag zum #Linuxday einreichen? #OpenSource #ERP Systeme wäre vielleicht für Unternehmen interessant und mit

 @adulau@infosec.exchange
I don’t like playing the futurologist, but after seeing AI companies warn EU institutions about the supposed risks of open-weight models, I suspect some are lobbying to regain control over genuine open source and open-weight AI.
Don’t fall into the trap: the greater danger lies in opaque, proprietary models, not open-source ones.
#opensource
 @digitalnaiv@mastodon.social
Kiel macht ernst: Über 200 Beschäftigte der Staatskanzlei arbeiten laut Stefan Krempl bei @… mit Linux. Rund 20 Rechner bleiben vorerst bei Windows – Fachverfahren ohne Alternative. Genau da liegt die eigentliche Baustelle der digitalen Souveränität. Nächste Schritte: Nextcloud, Univention Nubus, Oskar. #Linux #OpenSource #DigitaleSouveränität https://www.heise.de/news/Nachfolger-von-Windows-Staatskanzlei-Kiel-stellt-auf-Linux-um-11460729.html
 @tinoeberl@mastodon.online
Löblich:
Die Schweizer Armee setzt künftig verstärkt auf #OpenSource und will Microsoft-Produkte schrittweise ersetzen.
Als Gründe werden digitale Souveränität, Sicherheitsbedenken und geringere Abhängigkeit von einzelnen Softwareanbietern genannt.
Bis Oktober 2026 sollen die Arbeitsplätze mit #Opendesk
 @opencommit@fosstodon.org
We had an intermittent storage issue. This problem has now been resolved.
#opencommit #git #opensource
 @publicvoit@graz.social
#Google hammers another, extremely petty nail in the #Android #OpenSource Project’s coffin
 @grist@fosstodon.org
All data stays local when self-hosting, including anything processed through the REST API or MCP. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
 @simon_brooke@mastodon.scot
Well, I have just written my first software, and created my first pull request, since April. It's not rocket science but perhaps my brain is recovering from fog.
#OpenSource
#AmWriting
@a@paperbay.orgHow mature is this repository? My long quest for open-source software metrics
When I discover an open-source software project for the first time, how can I estimate whether it is mature, healthy and usable?
I just released OSSTRL - Open Source Software Technology Readiness Level to help me calculating the maturity of open-source projects.
#opensource
 @dde@social.tchncs.de
Pebble Time 2 – #opensource
@michabbb@social.vivaldi.net📋 #croc is a CLI tool that transfers files and folders between any two computers, with end-to-end encryption #opensource #golang

 @rettichschnidi@swiss.social
Letzte Chance - wir haben noch 11 Plätze!
#OpenSource
@frankel@mastodon.top @michabbb@social.vivaldi.net🧹 shadcn/lint by #shadcn is an agent-first linter for #TailwindCSS design systems: write design system rules that #AI coding agents can verify
 @thijs_lucas@norden.social
Was ich noch sehr vermisse: eine Alternative zum Speichern, Kategorisieren, Bewerten und Beschreiben von Orten wie mit #GoogleMaps. Etwas #MadeInEurope und #OpenSource.
@grist@fosstodon.orgStop saying “open source sustainability” #business
@michabbb@social.vivaldi.net☁️ #Floci is a free, #opensource local #AWS emulator built with #Quarkus Native — AWS-compatibl…
 @ubuntourist@mastodon.social
Starting in 2027, a silent update, nonconsensually pushed by Google, will block every Android app whose developer hasn't registered with Google, signed their contract, paid up, and handed over government ID.
https://keepandroidopen.org/
@adulau@infosec.exchangeAn idea for next year workshop @… - open source license for developers? It could be a nice opportunity because it seems to be a never ending learning process.
#opensource
@michabbb@social.vivaldi.net🧱 #AWS Blocks is a new #opensource framework from AWS (#Apache2 license) built specifically for the era of #Ai #coding
 @dde@social.tchncs.de
Distributionsfremde Software – #opensource
@frankel@mastodon.topBuilding an #OpenSource #RobotVacuum — Meet OOMWOO
https://makerspet.com/blog/building-an
@grist@fosstodon.orgAnd for questions along the way, the Grist Discord has a dedicated self-hosting channel. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@michabbb@social.vivaldi.net @a@paperbay.org"General Resolution: LLM usage in Debian"
When people don’t understand a system, they try to regulate it.
#ai #debian #opensource
@michabbb@social.vivaldi.net🔌 #Toolport is a local-first #MCP gateway. Every AI client points at one port and shares the same servers, so you set up and authenticate each server once instead of in every app.
#opensource

 @enriquericos@mastoart.social
Reading a lot of Linux projects talking about LLMs now, focusing on if they work well enough or not. No talk about ethics, ideals or politics.
If it continues down this path, FLOSS will end up like the Ed Sheeran of software.
#software #foss #floss #libresoftware #linux #lxqt #desktopEnvironment #openSource #ethics #llm #techbros #tech
@michabbb@social.vivaldi.net🌈 zsh-patina is an #opensource #Zsh plugin that highlights your command line while you type — written in #Rust, MIT licensed 🧵👇

 @JBrickelt963@framapiaf.org
#VLC4 a enfin une date de sortie officielle pour décembre 2026. Je viens de voir ^^ #VLC #OpenSource #FOSS
J'…
 @digitalnaiv@mastodon.social
Die Schweiz nennt ihr Anti-Microsoft-Programm BOSS – und trifft damit unfreiwillig den Nagel auf den Kopf: Wer entscheidet, wo die eigenen Daten liegen, ist eben der Chef im Ring. 3000 Beschäftigte, openDesk, Rollout bis Ende 2027. Der US-CLOUD-Act als bester Verkäufer von Open Source, den man sich vorstellen kann. #DigitaleSouveränität #OpenSource #Schweiz https://www.heise.de/news/Schweiz-startet-Open-Source-Arbeitsplatz-fuer-3000-Beschaeftigte-11444842.html?wt_mc=rss.red.unbekannt.unbekannt.atom.beitrag.beitrag
 @frankel@mastodon.top @michabbb@social.vivaldi.net
🐢 #Atuin is an #opensource shell history tool written in #Rust that replaces your existing shell history with a #SQLite
 @adulau@infosec.exchange
I just released ptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage from reverse-DNS PTR hostnames.
It is intentionally heuristic and multi-label. PTR naming is operator-controlled and is not authoritative evidence of how an address is actually used. The output therefore includes a confidence score, the text that matched, and the rule IDs that produced each label.
To summarize, the library is trying to guess usage (and a bit location) of an IP address based on its PTR records. It's based on a set of rules which can be updated easily.
#osint #cybersecurity #ptrclassify #opensource #dns  https://github.com/adulau/ptrclassify
 module https://pypi.org/project/ptrclassify/
@grist@fosstodon.orgUpdating Grist means pulling a new Docker image and restarting the container. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
 @freeminded@tooting.ch
Heute bin ich am #SGES in #Winterthur als Redner im Innovationsforum IF.19 zum Thema Digitalisierung und Resilienz: Wie schaffen wir zukunftsfähige Infrastrukturen?
Natürlich dreht sich mein Beitrag um die Rolle von #OpenSource
https://sges.ch/if2026/if19-2026/
Würde mich freuen hier auf andere Fedinaut*innen zu treffen.
@michabbb@social.vivaldi.net🐚 #direnv is a shell extension that loads and unloads environment variables depending on the current directory. A .envrc file in a project folder gives you per-project environments without cluttering your ~/.profile #opensource
 @michabbb@social.vivaldi.net
📊 #OpenPanel is an #opensource web and product analytics platform — an alternative to #Mixpanel,

 @veit@mastodon.social
WTF: An anonymous security researcher has published working exploit code for a total of 15 previously unknown vulnerabilities without first notifying the affected manufacturers and open-source projects: #OpenSource #Vulnerability
@grist@fosstodon.orgHow do I self-host Grist? Recap of our setup wizard webinar #OpenSource
@michabbb@social.vivaldi.net🔐 Hermes Vault: a local-first credential broker and encrypted vault for AI agents. It scans for plaintext secrets, brokers policy-gated access and proves audit integrity.
#opensource #security #MCP
@michabbb@social.vivaldi.net🧰 #ECC is an #opensource agent harness optimization system that adds skills, instincts, memory, security and research-first development to #ClaudeCode,
@adulau@infosec.exchangeWe discussed decentralized vulnerability allocation, digital sovereignty, CVD workflows, Vulnerability-Lookup, Vulniverse, AI-assisted vulnerability analysis, and the future of GCVE.
All slide decks and workshop materials are now available:
🔗 #cve #gcve #cvd #cybersecurity #opensource #vulnerability #vulnerabilityManagement
@…
 @ErikJonker@mastodon.social
Looking at and playIng around with Hermes Agent, impressive and relatively easy to install and use.
Also opensource. Hermes Agent — Open-Source AI Agent That Grows With You | Nous Research #AI #HermesAgent #opensource #foss #agents
@michabbb@social.vivaldi.net📋 The PHP Foundation looks at how European public administrations run their #digitalsovereignty strategies on #PHP applications #opensource
 @mgorny@social.treehouse.systems
Too many days working on #FLOSS feel like: "I'm not paid for this shit. I'm paid to do other shit and I have to focus on that shit, but I can't when I have to spend so much time fixing shit that apparently others are being paid to break all the time."
#Gentoo #LLVM #FreeSoftware #OpenSource
 @gla@mastodon.social
That's a nice little utility, also available as a #launchbar action
#markdown #html #opensource
@michabbb@social.vivaldi.net🎛️ #CTRLNODE is an #opensource remote orchestration platform for #AIcodingagents. Install the Bridge binary on any machine — laptop, VPS, CI box — and dispatch tasks, schedule routin…
 @michabbb@social.vivaldi.net
🤖 #BrowserAct is an open-source browser automation CLI built for #AIagents — real browsers, anti-bot bypass and human handoff when the agent gets stuck #opensource
@michabbb@social.vivaldi.net🔍 #ctx is an #opensource CLI for fast local search across your past coding agent sessions, built in #Rust. Coding agents start from zero — they see the current repo but lose earlier decisions, fail…
 @michabbb@social.vivaldi.net
📋 #queuesql is an #opensource #Laravel package that turns any write query — delete, update, insert, upsert — into parallel batched queue jobs
 @michabbb@social.vivaldi.net
📦 v2 is a ground-up rewrite in Rust of the original Go tool, MIT licensed. Windows support is planned
🌐 #opensource
@michabbb@social.vivaldi.net🧠 #VoiceMem is an #opensource memory system for real-time #voiceagents, built on a streaming dual-brain architecture
 @michabbb@social.vivaldi.net @michabbb@social.vivaldi.net
🔁 #CompoundEngineering is an #opensource plugin of 33 skills for AI coding agents that turns each task into stored knowledge, so the next unit of work gets easier instead of harder #ClaudeCode
 @michabbb@social.vivaldi.net
🎨 Inspo — real production websites your coding agent can study before it writes UI #opensource #MCP #webdev #AI
 @kingconsult@berlin.social
> @… announces 60 projects strenghtening the #DigitalCommons ¹
➡️ There are two #Fediverse-related tools:
#ActivityBot — A full #ActivityPub server in a single #PHP file
👉 #Fedipub — #Ruby Library for adding #ActivityPub Federation
👉 #NLnet #OpenSource #SocialMedia #OpenSocialWeb #FOSS #FLOSS
@michabbb@social.vivaldi.net📋 #Luvus is an #opensource mission control for your #AI coding agents — one terminal to run, watch, resume and orchestrate
 @michabbb@social.vivaldi.net
🎨 #Impeccable is a design language for #AI coding agents: 1 skill, 23 commands, live browser iteration and 46 deterministic detector rules for AI-generated frontend design #opensource
 @adulau@infosec.exchange
So finally Kimi-k3 is not really open-source
#kimi #ai #opensource
@michabbb@social.vivaldi.net🫧 #bubbles by #Hyperplexed brings Android-style app bubbles to the web — floating, draggable overlays that snap to screen edges, stack into a group, expand into content panels, and fling away to dismiss. #opensource
@michabbb@social.vivaldi.net⚙️ #Kestra is an open-source, event-driven orchestration platform for data, #AI and infrastructure workflows, unifying scheduled and event-driven automation behind a declarative, language-agnostic interface #opensource

 @castarco@hachyderm.io
A short video showcasing the current state of the #SoulCrafted Slicer I'm working on.
#3dPrinting #Resin3dPrinting #SoulCraftedSlicer #FLOSS #OpenSource #Rust #Rustlang
 @michabbb@social.vivaldi.net
🧩 #Laravel LSP announced at #LaraconUS 2026: a first-party language server that teaches your editor about your app #PHP
 @adulau@infosec.exchange
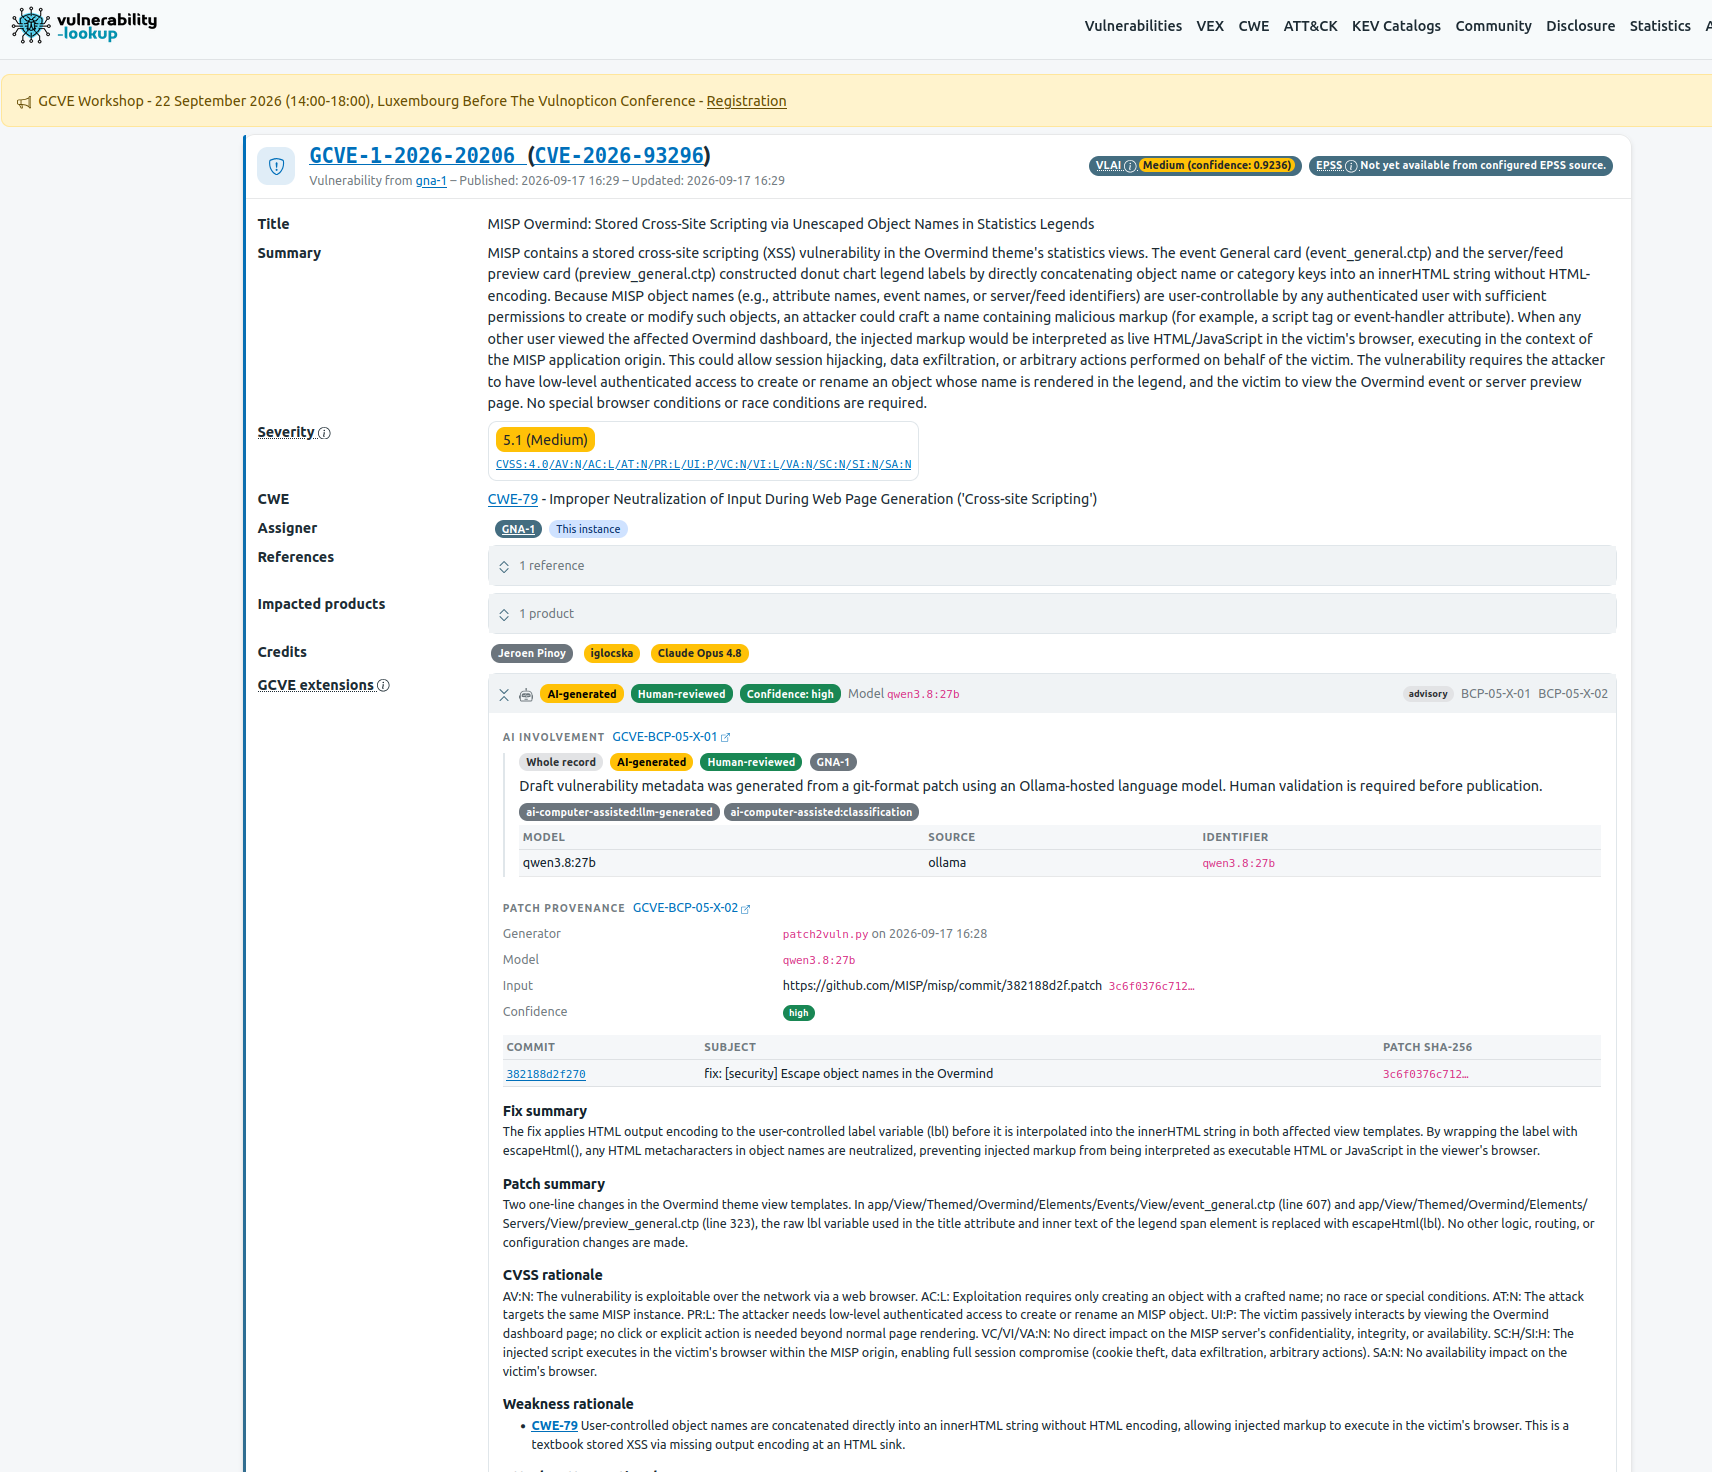
Tired of drafting vulnerability advisories from Git patches?
We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.
With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.
The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.
The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.
patch2vuln v1.0 is now available as open-source software under the @… Lab initiative.
#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI
 @michabbb@social.vivaldi.net
📋 #HuntProxy is an #opensource web security workbench built for #AI agents — connect it over #MCP
@kingconsult@berlin.social @ErikJonker@mastodon.socialInteresting 🤔
#AI #opensource #openweights #china #usa #geopolitics #foss
@michabbb@social.vivaldi.net📊 Local-first dashboard for #Codex CLI and #ClaudeCode usage limits #opensource #nodejs
 @castarco@hachyderm.io
It's been a looooong time since I wrote a technical article for my #blog
This one is about my work on Logtau, a collection of logging libraries for #NodeJS : #JavaScript #TypeScript #logging #FLOSS #OpenSource
@michabbb@social.vivaldi.net🔍 #Hunk is a review-first terminal diff viewer for agent-authored changesets #opensource #git #cli
 @adulau@infosec.exchange
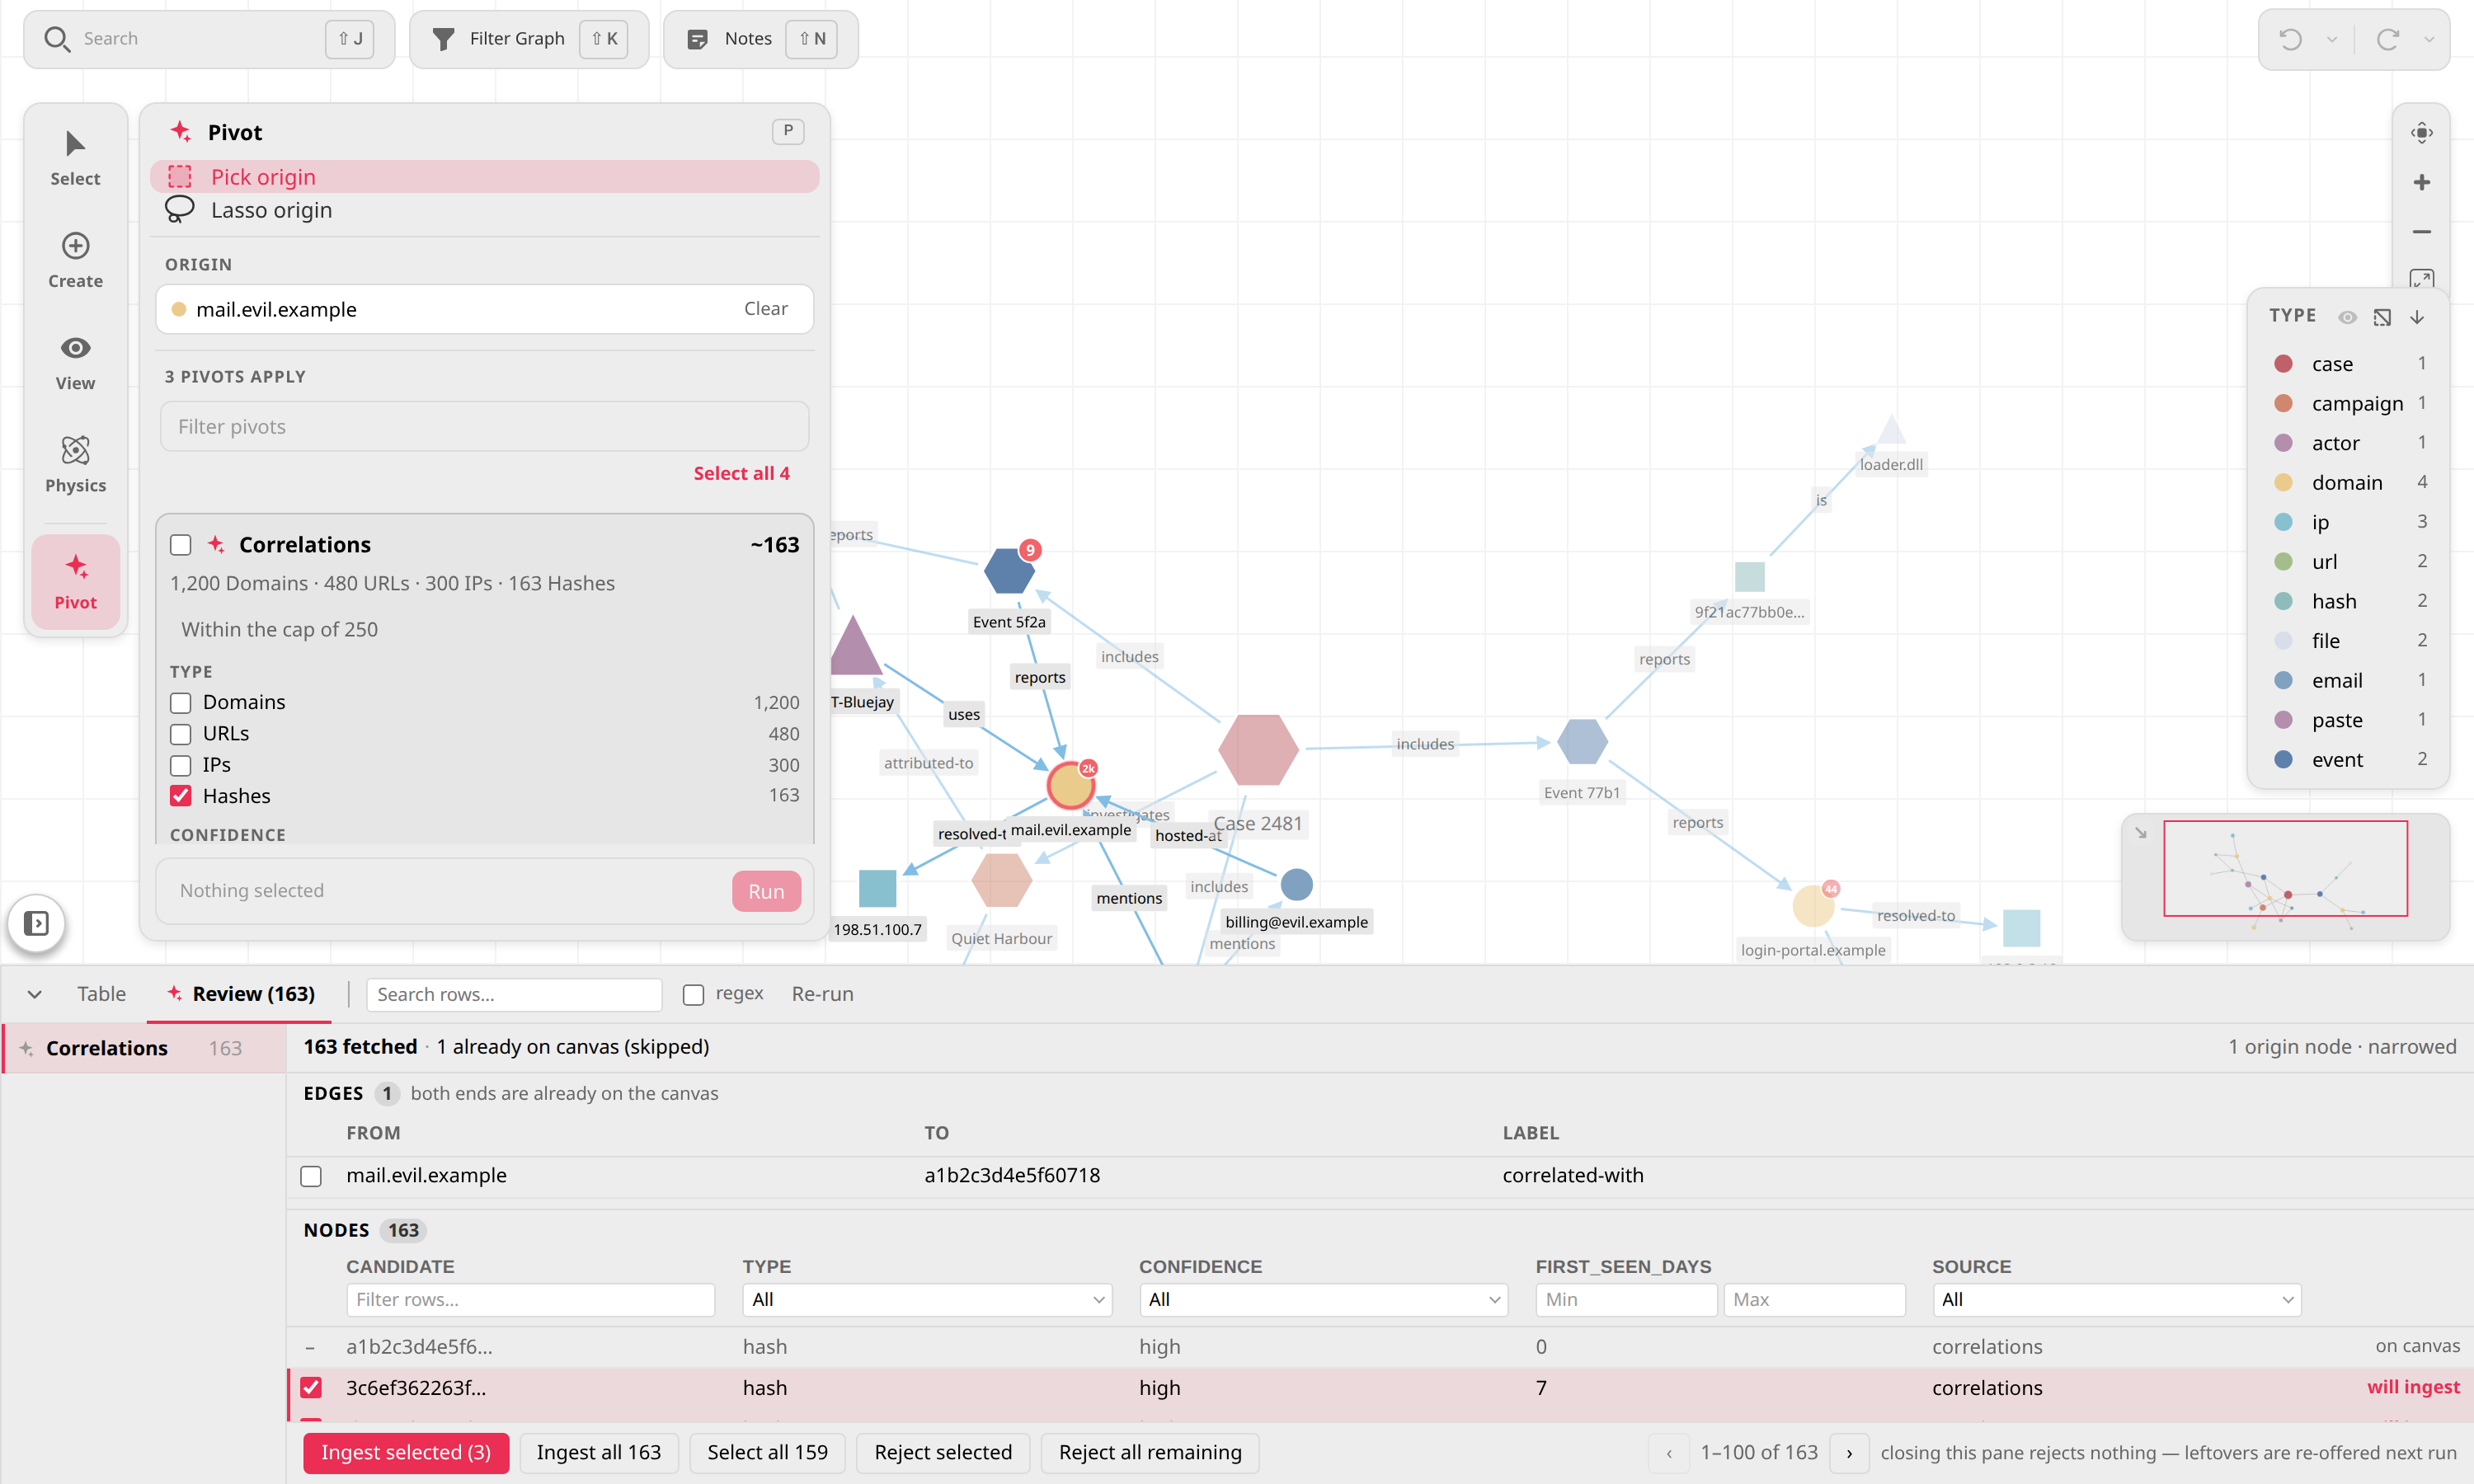
Pivotick v2.0.0 has been released.
Pull more graph out of wherever your data lives, and you choose what lands. History is the way back out of anything that does.
Actually you can update, pivot graph and review. This release also includes many new other features.
#graph #library #infosec #opensource #graphing #pivotick #cti #threatintelligence
 @michabbb@social.vivaldi.net
📋 #Archify is an #opensource #AI #agent
 @kingconsult@berlin.social
Die Gesellschaft für #Informatik ( @… − folgen!) fordert im neuen Policy Brief die Anerkennung und Besserstellung von #OpenSource-Software-Stewards ( Das sind Verwalter quelloffener Software,#OSSStewards ) nach der EU 🇪🇺 #Cyberresilienz-Verordnung.
15.07.2026:
👉 #CyberResilienceAct #CRA #FOSS #FLOSS #Cybersicherheitsstrategie #ITSecurity #DutGemacht
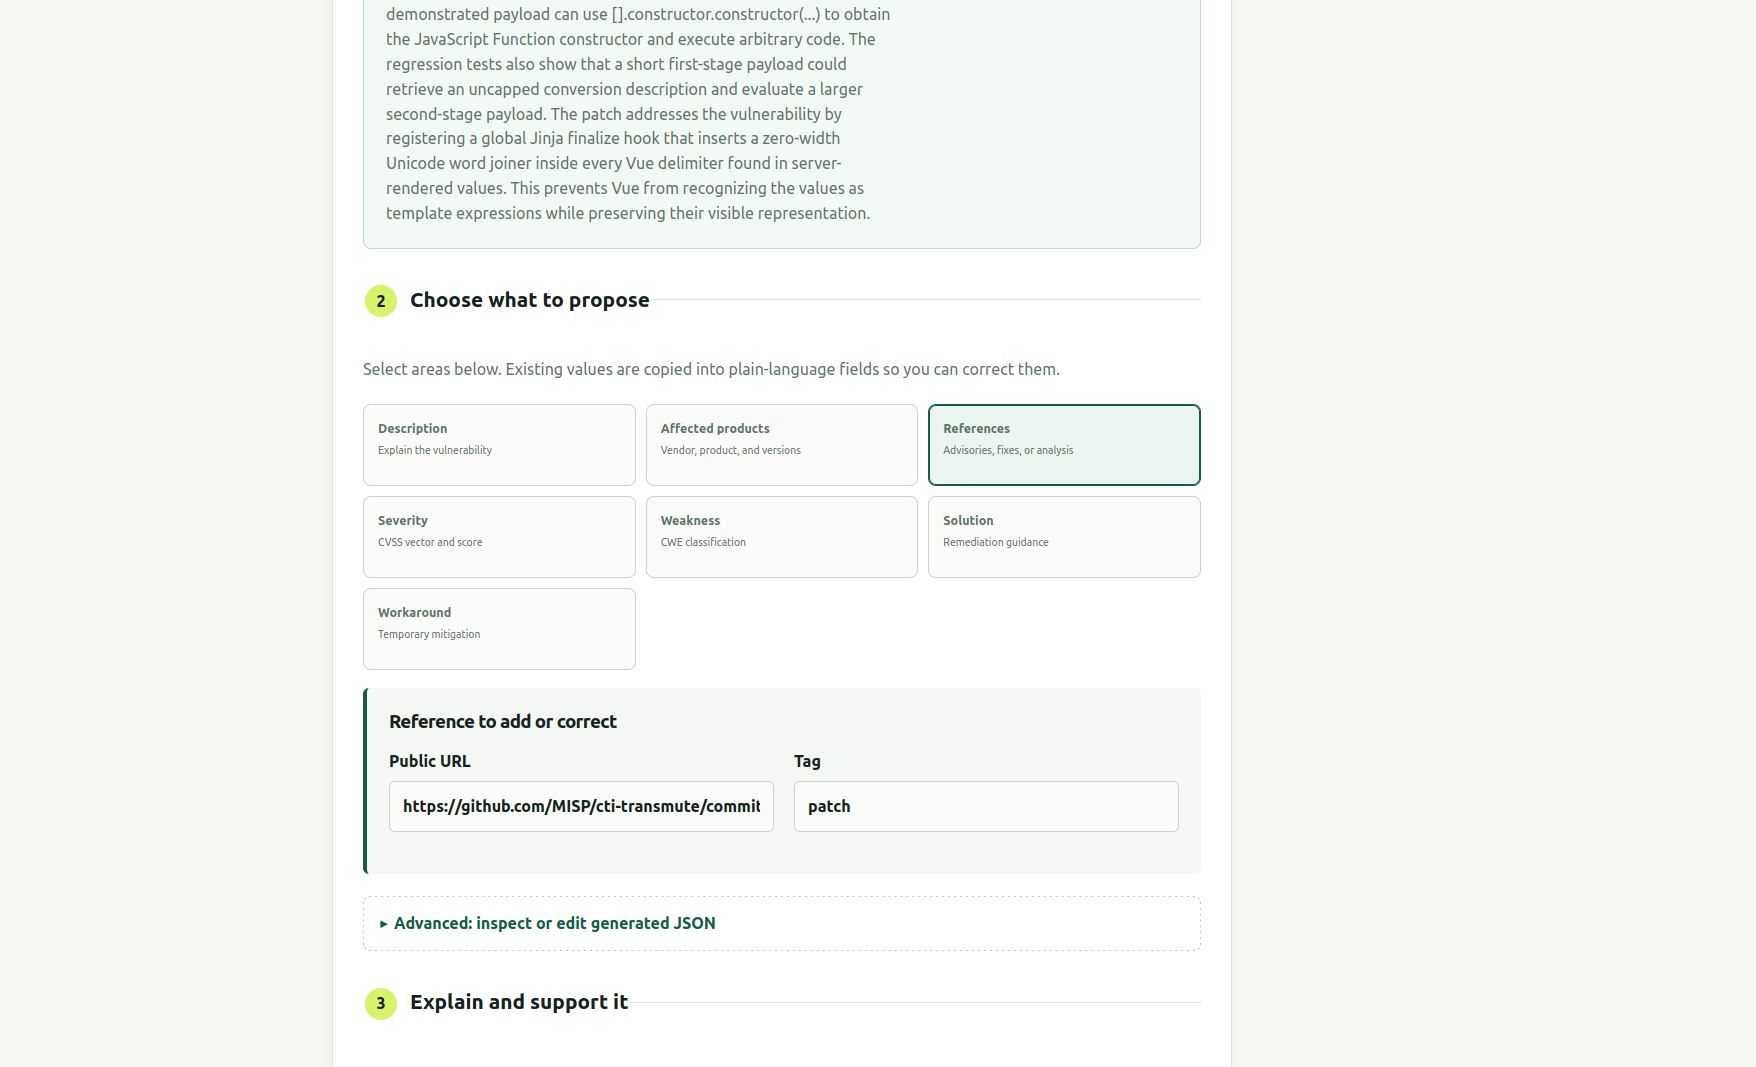
@adulau@infosec.exchangeWorking on a first super beta implementation of @… BCP-11 "Community-Proposed Updates to Existing CVE Records"
To validate if the BCP-11 can be published.
#cve #gcve #vulnerability #opensource #opendata
Discussions https://discourse.ossbase.org/t/gcve-bcp-11-community-proposed-updates-to-existing-cve-records/1110
 @michabbb@social.vivaldi.net
🔐 #AgentVault is an #opensource HTTP credential proxy and vault from #Infisical that sits between #AIagents
 @michabbb@social.vivaldi.net
📋 #CrabTrap by #Brex is an #opensource HTTP/HTTPS proxy that sits between #AI agents and externa…
 @adulau@infosec.exchange
I love to see clever use of the @… ecosystem and @… did a cool GNA which is automatically creating GCVE records and structured security advisories from full-disclosure mailing-list or alike:
🔗 Project details #gcve #cve #vulnerability #vulnerability #opensource #cybersecurity
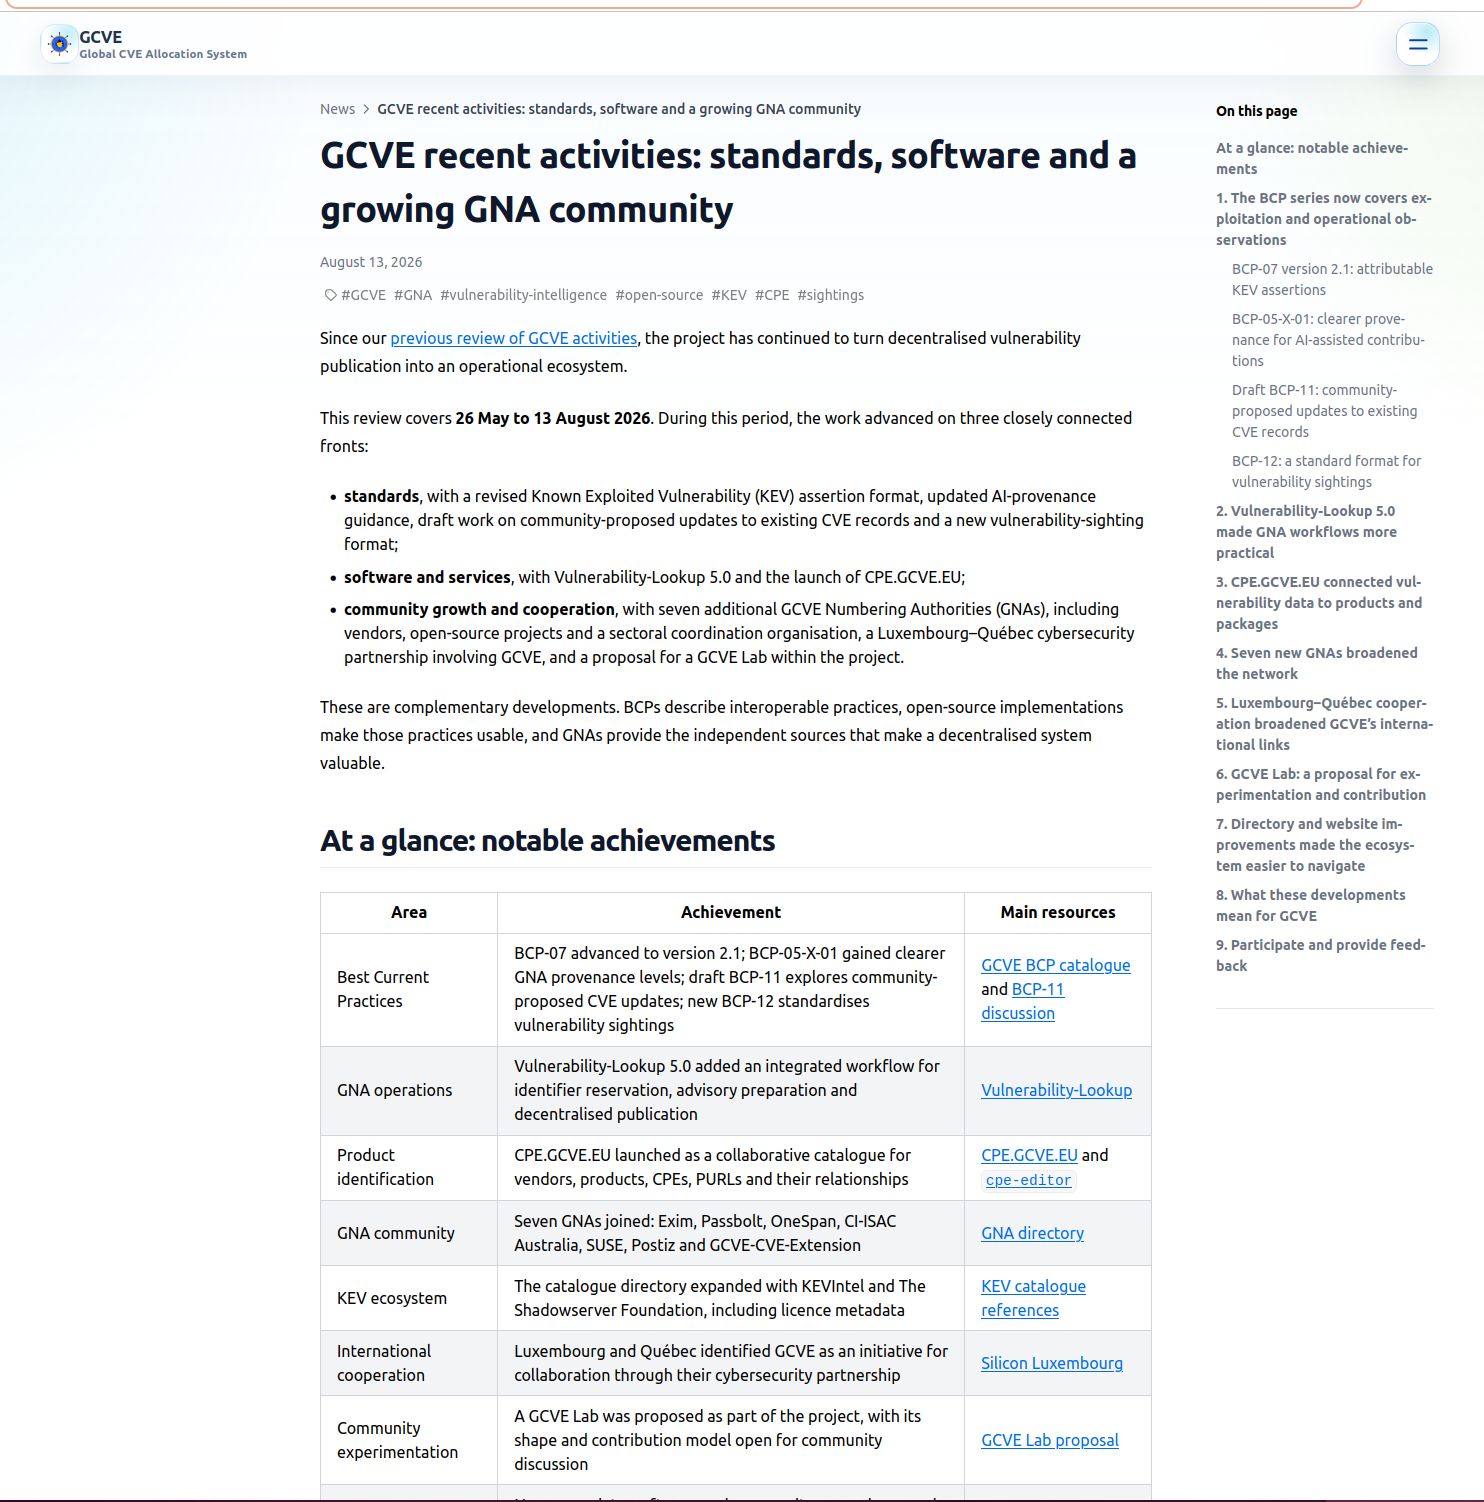
@adulau@infosec.exchangeIf you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource
 @adulau@infosec.exchange
We had difficulties automatically classifying chats, messaging channels, and forums. So we tested several open-weight large language models for our use case. The benchmark is published below, along with a tool supporting the classification process.
This helps us avoid manually classifying channels collected from dark-web forums and social networks, while reliably identifying which channels can be discarded and which deserve further analysis.
🔗 Publication #ai #llm #cybersecurity #darkweb #osint #opensource
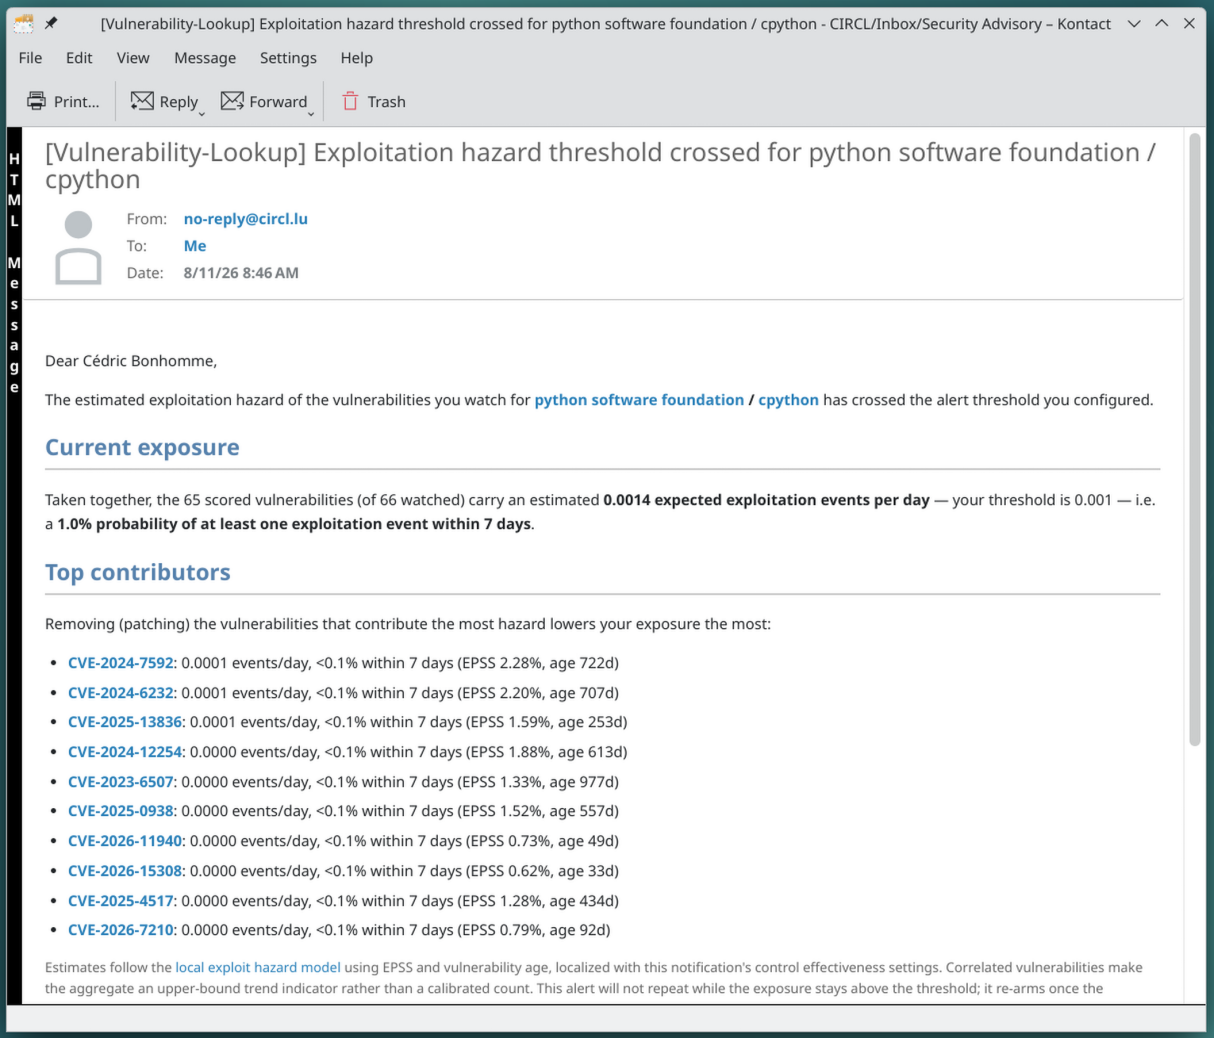
@adulau@infosec.exchangeFrom a research paper to running open-source code in just a few days.
We (with @…) have been experimenting in Vulnerability-Lookup with the concept of Local Exploit Hazard, based on the recent research paper “Modeling Local Exploit Hazard — A Bayesian Framework for Quantifying Exploit Risk and Operational Efficiency” by Stephen Shaffer and Laura Cristiana Voicu.
The idea addresses an important question in vulnerability management:
Not simply “How dangerous is this vulnerability globally?” but “How much exploitation risk does this vulnerability represent in my environment?”
Instead of introducing yet another static vulnerability score, the model starts from exploit likelihood such as EPSS and combines it with local security controls, CVSS attack vectors, vulnerability age and KEV policy to estimate an exploitation hazard.
We implemented an experimental version in Vulnerability-Lookup and connected it directly to operational workflows.
For the full details: #cve #gcve #vulnerabilitymanagement #vulnerability #opensource #opendata
@…
 @adulau@infosec.exchange
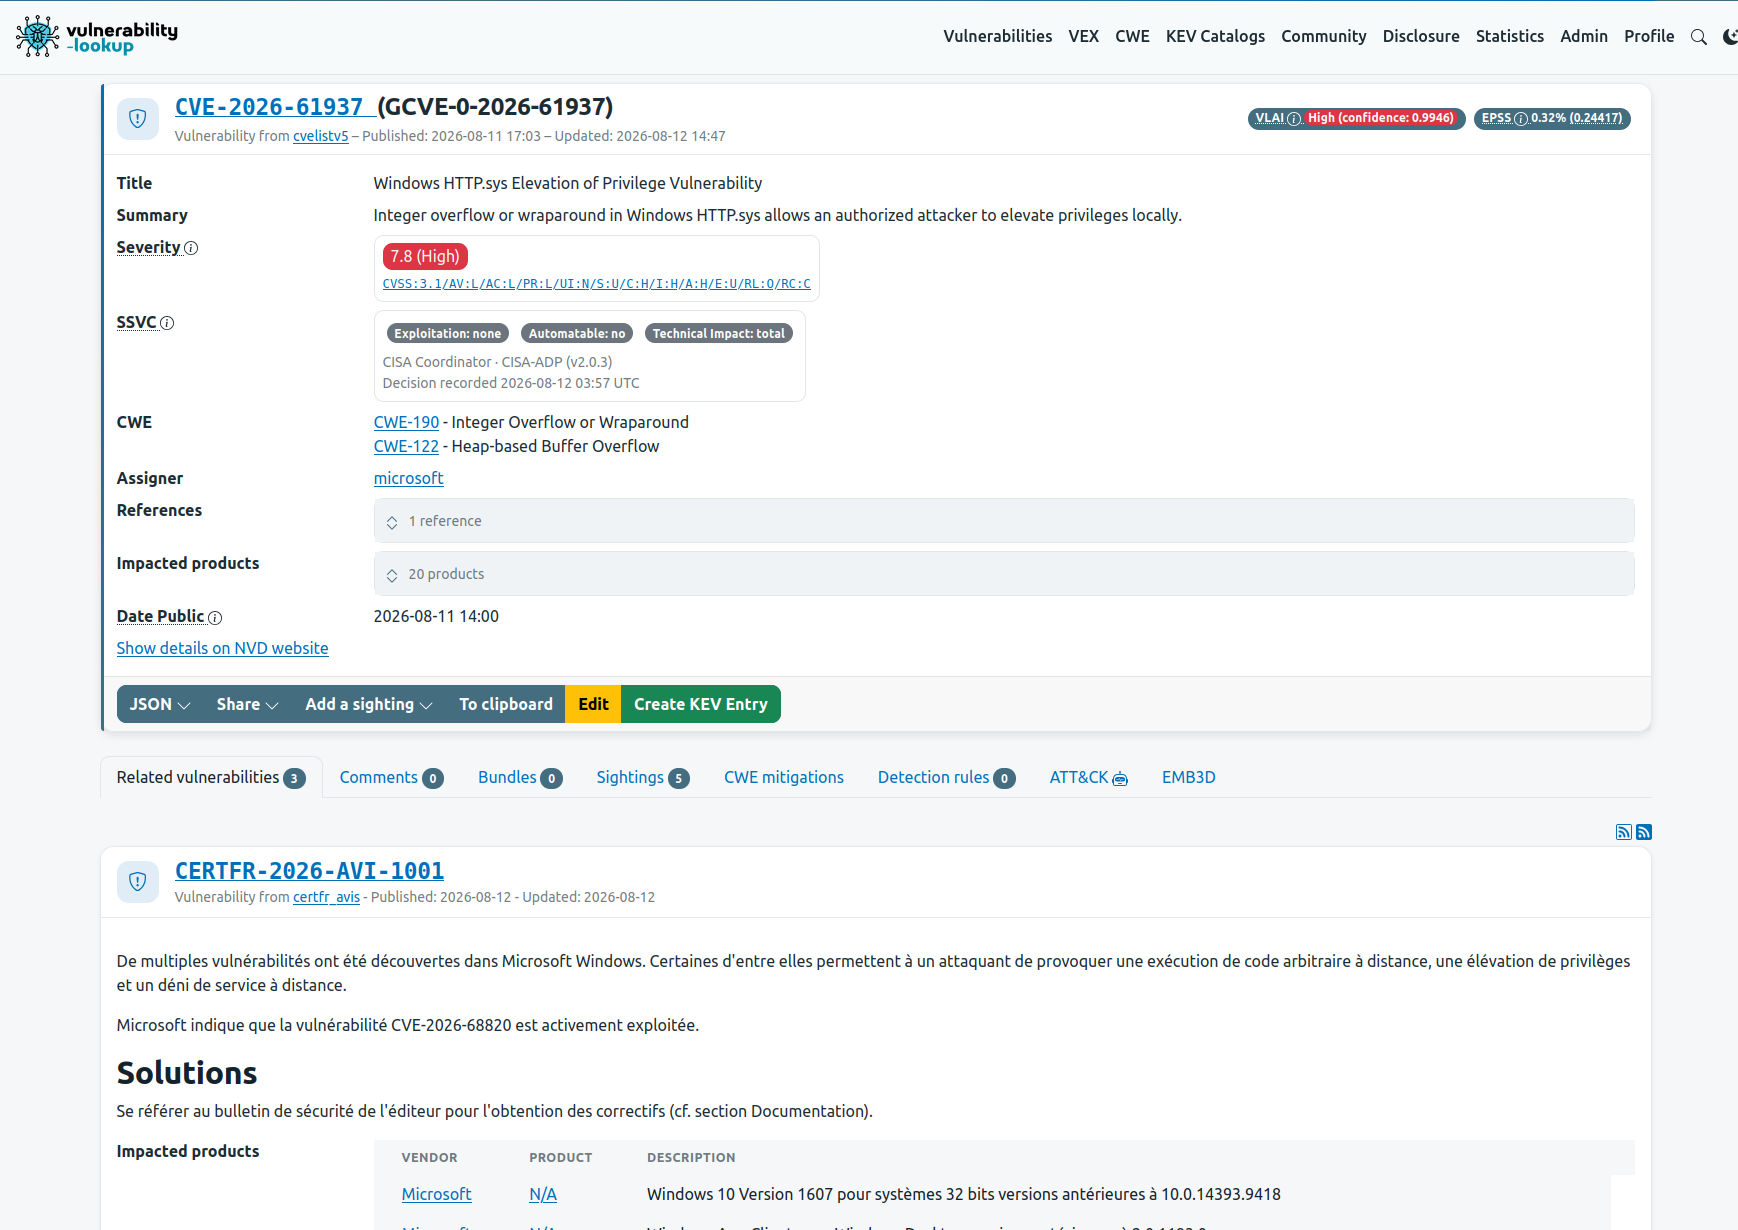
vulnerability-lookup 6.0 will be released this week with many (really, many!) new features.
One of the smaller, but important, additions is support for multiple SSVC views alongside CVSS. When SSVC information is available from an ADP (such as CISA) , or from additional sources such as GCVE, it is now displayed by default.
This allows users to more easily compare the different severity and prioritization assessments associated with a vulnerability.
The CIRCL vulnerability-lookup instance is running the pre-release of 6.0 -
#cve #gcve #opensource #vulnerabilitylookup #opendata #vulnerabilitymanagement #cyberecurity #ssvc
@…
@…
 @kingconsult@berlin.social
Mehr digitale Autonomie gefordert:
Die niederländischen 🇳🇱 Behörden für Verbraucher und Märkte, #Finanzmärkte, #Datenschutz, digitale #Infrastruktur und die »De Nederlandsche Bank« fordern #Unternehmen und #Regierungen auf, den Übergang zu mehr digitaler Autonomie zu beschleunigen.
10. Juli 2026: Bericht
»Der Weg zur digitalen Autonomie« (PDF NL)
👉 #2MR #DigitalSovereignty #DigitaleSouveranitat #DutGemacht #DiDIT #Digitalisierung #OpenSource #OSWA
@adulau@infosec.exchangeThe Radio Image Framing Protocol (RIFP) 1.0 is an experimental, extensible standard for sending images over low-rate radio links.
The default rifp-cpfsk-4800 profile uses binary continuous-phase FSK and can be deployed around 433.92 MHz where local regulation permits it. RIFP itself is not tied to 433 MHz or to FSK and can be used in any frequency bands.
I'm still exploring various low-cost options for a device that can receive and display images on an e-ink screen in emergency areas or similar environments. Python implementation #radio #fax #433mhz #opensource
 @adulau@infosec.exchange
A standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick.
Source code: #misp #cti #threatintelligence #opensource #threatactor #cybersecurity
 @adulau@infosec.exchange
I spent many hours in vulnogram today and to be honest. I'm glad that a colleague started to work on a replacement called vulniverse. Still early beta but it's promising.
#opensource #vulniverse #cybersecurity #cve #gcve work in progress https://github.com/vulnerability-lookup/vulniverse
@adulau@infosec.exchangeGCVE BCP-07, the Known Exploited Vulnerability (KEV) Assertion Format, has been updated to version 2.2. A key addition is the formalisation of the GCVE KEV Directory, a simple machine-readable directory allowing organisations to announce where their KEV catalogues and exploitation assertions are published.
We particularly encourage software and hardware vendors to publish their own KEV catalogues. Vendors are often in the best position to confirm exploitation affecting their products, and publishing this information in a machine-readable form can significantly improve vulnerability prioritisation for users, CSIRTs and vulnerability-management platforms.
For more details #GCVE #GNA #vulnerabilityintelligence #opensource #KEV #cybersecurity
@…
@adulau@infosec.exchangePivotick is an open-source network graph library to facilitate pivoting.
Version 1.4.0 has been released and also includes a security fix.
Release notes #opensource #infovis #graph #networkgraph #visual