 @michabbb@social.vivaldi.net
2026-09-08 23:17:19
📋 The PHP Foundation looks at how European public administrations run their #digitalsovereignty strategies on #PHP applications #opensource
@michabbb@social.vivaldi.net📋 The PHP Foundation looks at how European public administrations run their #digitalsovereignty strategies on #PHP applications #opensource
 @dde@social.tchncs.de
Pebble Time 2 – #opensource
 @frankel@mastodon.top
#OpenSource as We Know It Is Dead
https://jross.me/open-source-as-we-know-it-is-dead/
@michabbb@social.vivaldi.net🫧 #bubbles by #Hyperplexed brings Android-style app bubbles to the web — floating, draggable overlays that snap to screen edges, stack into a group, expand into content panels, and fling away to dismiss. #opensource
 @ubuntourist@mastodon.social
Starting in 2027, a silent update, nonconsensually pushed by Google, will block every Android app whose developer hasn't registered with Google, signed their contract, paid up, and handed over government ID.
https://keepandroidopen.org/
 @a@paperbay.org
"General Resolution: LLM usage in Debian"
When people don’t understand a system, they try to regulate it.
#ai #debian #opensource
 @thijs_lucas@norden.social
Was ich noch sehr vermisse: eine Alternative zum Speichern, Kategorisieren, Bewerten und Beschreiben von Orten wie mit #GoogleMaps. Etwas #MadeInEurope und #OpenSource.
@michabbb@social.vivaldi.net🤖 #BrowserAct is an open-source browser automation CLI built for #AIagents — real browsers, anti-bot bypass and human handoff when the agent gets stuck #opensource
@dde@social.tchncs.deDistributionsfremde Software – #opensource
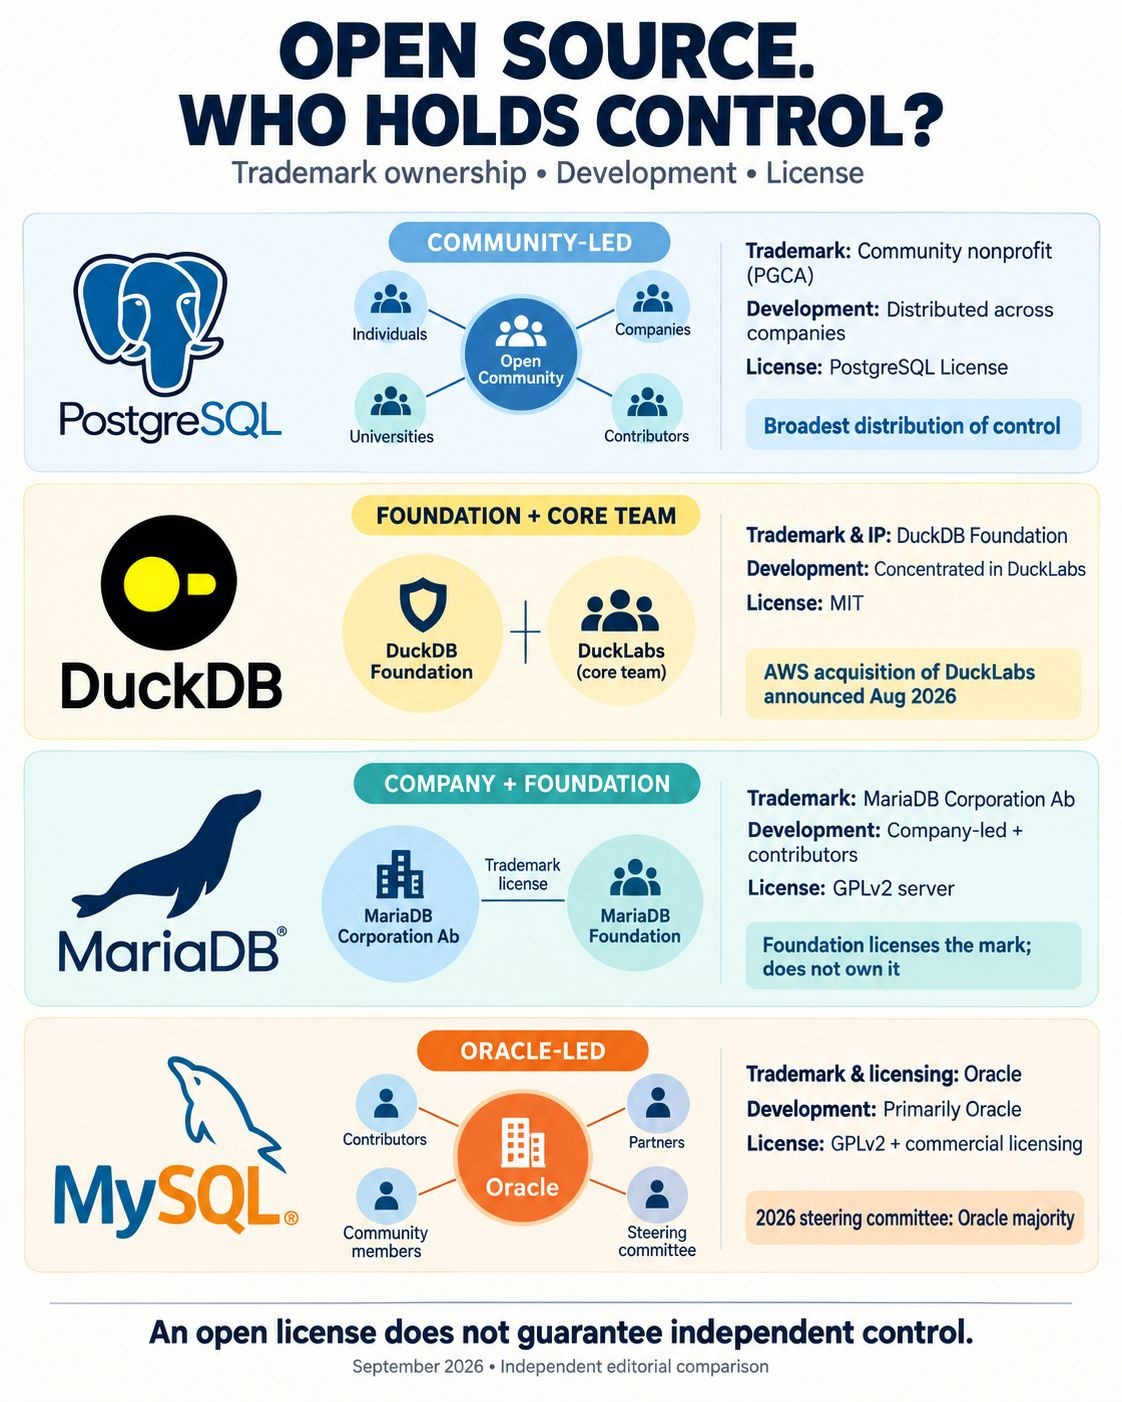
@frankel@mastodon.top#OpenSource - Who holds control?
via Peter Zaitsev on LinkedIn https://www.linkedin.com/posts/peterzaitsev_i-was-asked-how-do-…
 @ErikJonker@mastodon.social
Mooi om te zien hoeveel keuze en variatie er is als het gaat om een meer autonome digitale werkplek.
#opensource #foss #mijnbureau
 @adulau@infosec.exchange
I don’t like playing the futurologist, but after seeing AI companies warn EU institutions about the supposed risks of open-weight models, I suspect some are lobbying to regain control over genuine open source and open-weight AI.
Don’t fall into the trap: the greater danger lies in opaque, proprietary models, not open-source ones.
#opensource
 @tinoeberl@mastodon.online
Löblich:
Die Schweizer Armee setzt künftig verstärkt auf #OpenSource und will Microsoft-Produkte schrittweise ersetzen.
Als Gründe werden digitale Souveränität, Sicherheitsbedenken und geringere Abhängigkeit von einzelnen Softwareanbietern genannt.
Bis Oktober 2026 sollen die Arbeitsplätze mit #Opendesk
 @publicvoit@graz.social
#Google hammers another, extremely petty nail in the #Android #OpenSource Project’s coffin
 @rasos@fairmove.net
Soll ich wieder einen Vortrag zum #Linuxday einreichen? #OpenSource #ERP Systeme wäre vielleicht für Unternehmen interessant und mit
 @a@paperbay.org
Is there somewhere a good open source software in Python to act as bridge between RSS and ActivityPub act as actor? Before I write something new.
#activitypub #opensource #rss
 @JBrickelt963@framapiaf.org
#VLC4 a enfin une date de sortie officielle pour décembre 2026. Je viens de voir ^^ #VLC #OpenSource #FOSS
J'…
 @michabbb@social.vivaldi.net
📋 #queuesql is an #opensource #Laravel package that turns any write query — delete, update, insert, upsert — into parallel batched queue jobs
 @frankel@mastodon.top
Guest poster Stefano Fago on a Java Geek today:
"I started with a simple task: I needed an #AI agent to help me compile decision records, structured documents that capture why a team chose option A over B, using the #opensource
 @opencommit@fosstodon.org
We had an intermittent storage issue. This problem has now been resolved.
#opencommit #git #opensource
@michabbb@social.vivaldi.net📦 v2 is a ground-up rewrite in Rust of the original Go tool, MIT licensed. Windows support is planned
🌐 #opensource
 @freeminded@tooting.ch
Heute bin ich am #SGES in #Winterthur als Redner im Innovationsforum IF.19 zum Thema Digitalisierung und Resilienz: Wie schaffen wir zukunftsfähige Infrastrukturen?
Natürlich dreht sich mein Beitrag um die Rolle von #OpenSource
https://sges.ch/if2026/if19-2026/
Würde mich freuen hier auf andere Fedinaut*innen zu treffen.
@frankel@mastodon.top @rberger@hachyderm.io
Find and Help your Open Source Friends
- Leonid Bugaev
"So let the large projects close the queue [to LLM contributions]. There is a lot more open source out there.
That was the reason I built Help Wanted in the first place, few years ago. At the time of writing, it has 650,456 issues from 96,576 projects in its index, from the projects who actually WANT help. Most developers will never hear the names of nearly all these projects.”
#OpenSource
 @grist@fosstodon.org
All data stays local when self-hosting, including anything processed through the REST API or MCP. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@michabbb@social.vivaldi.net🧠 #VoiceMem is an #opensource memory system for real-time #voiceagents, built on a streaming dual-brain architecture
 @frankel@mastodon.top @a@paperbay.org
How mature is this repository? My long quest for open-source software metrics
When I discover an open-source software project for the first time, how can I estimate whether it is mature, healthy and usable?
I just released OSSTRL - Open Source Software Technology Readiness Level to help me calculating the maturity of open-source projects.
#opensource
@michabbb@social.vivaldi.net🔁 #CompoundEngineering is an #opensource plugin of 33 skills for AI coding agents that turns each task into stored knowledge, so the next unit of work gets easier instead of harder #ClaudeCode
 @adulau@infosec.exchange
Working on a first super beta implementation of @… BCP-11 "Community-Proposed Updates to Existing CVE Records"
To validate if the BCP-11 can be published.
#cve #gcve #vulnerability #opensource #opendata
Discussions https://discourse.ossbase.org/t/gcve-bcp-11-community-proposed-updates-to-existing-cve-records/1110
 @johnleonard@mastodon.social
The SaaSpocalypse might be back on. A developer has used AI to create an alternative to the Adobe Suite and in doing so has put the entire cloud model, with it's hard-to-exit ecosystems, back under scrutiny.
#saaspocalypse #adobe #opensource #technews #ArtCraft
@michabbb@social.vivaldi.net📊 Local-first dashboard for #Codex CLI and #ClaudeCode usage limits #opensource #nodejs
 @michabbb@social.vivaldi.net
📋 #Luvus is an #opensource mission control for your #AI coding agents — one terminal to run, watch, resume and orchestrate

 @digitalnaiv@mastodon.social
Kiel macht ernst: Über 200 Beschäftigte der Staatskanzlei arbeiten laut Stefan Krempl bei @… mit Linux. Rund 20 Rechner bleiben vorerst bei Windows – Fachverfahren ohne Alternative. Genau da liegt die eigentliche Baustelle der digitalen Souveränität. Nächste Schritte: Nextcloud, Univention Nubus, Oskar. #Linux #OpenSource #DigitaleSouveränität https://www.heise.de/news/Nachfolger-von-Windows-Staatskanzlei-Kiel-stellt-auf-Linux-um-11460729.html
@grist@fosstodon.orgStop saying “open source sustainability” #business
@frankel@mastodon.top @ErikJonker@mastodon.socialKey Takeaways: OSOR Webinar on EU Open Source Strategy.
#opensource #foss #EU
@michabbb@social.vivaldi.net🎨 #Impeccable is a design language for #AI coding agents: 1 skill, 23 commands, live browser iteration and 46 deterministic detector rules for AI-generated frontend design #opensource
 @grist@fosstodon.org
And for questions along the way, the Grist Discord has a dedicated self-hosting channel. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@michabbb@social.vivaldi.net🐝 #SwarmForge is an #opensource agent coordination system that turns swarms of #AI agents into a disciplined engineering team, built on
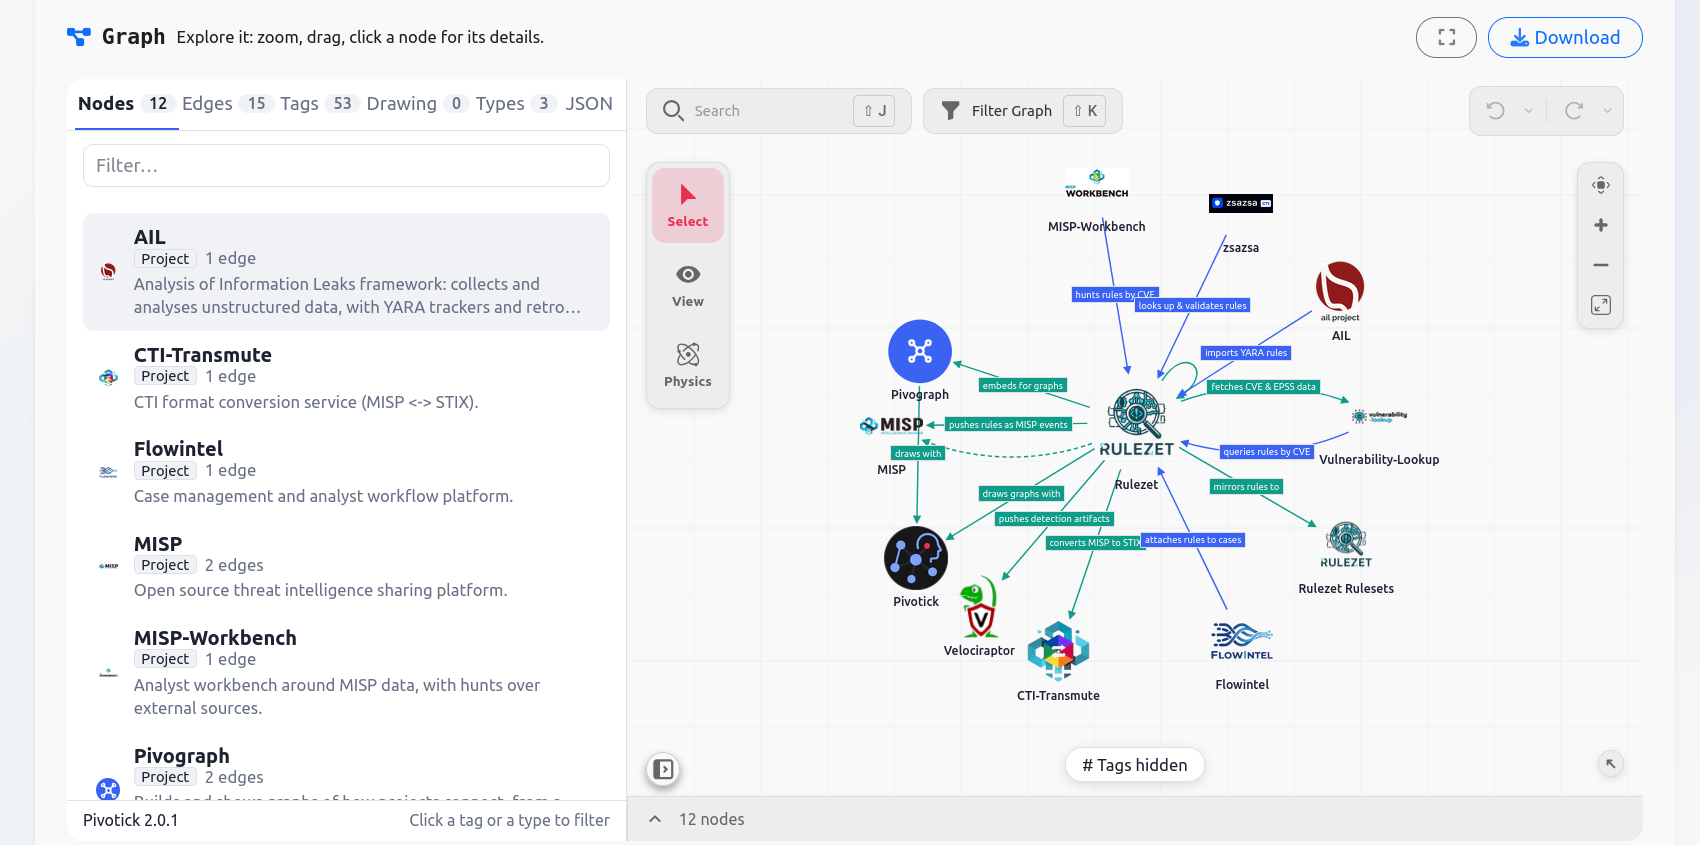
@frankel@mastodon.top @adulau@infosec.exchangeRulezet and its ecosystem: how detection rules travel between tools.
Vulnerability-Lookup, AIL, Flowintel, MISP, Velociraptor and more: every tool that reads from Rulezet or receives its rules, what each connection does, and an interactive map of the whole ecosystem.
🔗 #threatintelligence #threatintel #rulezet #misp #opensource #cybersecurity #detectionengineering #flowintel #velociraptor #dfir
 @michabbb@social.vivaldi.net
📋 #Autoprompt is an #opensource coding-agent skill that cut failures by 45% on agentic coding tasks #aiagents
@michabbb@social.vivaldi.net📋 #FreeToken is an edge-native #MoE serving engine for running frontier-scale open-weight models on personal, consumer hardware #opensource
@grist@fosstodon.orgHow do I self-host Grist? Recap of our setup wizard webinar #OpenSource
@ErikJonker@mastodon.socialThe Tax Administration of the Netherlands has decided to move from M365 to opensource and on premis solutions for it's office environment. An important step.
Letter to dutch parliament and news article, in dutch.
#taxadministration #opensource #foss #Microsoft #M365
@michabbb@social.vivaldi.net📋 #croc is a CLI tool that transfers files and folders between any two computers, with end-to-end encryption #opensource #golang
 @digitalnaiv@mastodon.social
Die Schweiz nennt ihr Anti-Microsoft-Programm BOSS – und trifft damit unfreiwillig den Nagel auf den Kopf: Wer entscheidet, wo die eigenen Daten liegen, ist eben der Chef im Ring. 3000 Beschäftigte, openDesk, Rollout bis Ende 2027. Der US-CLOUD-Act als bester Verkäufer von Open Source, den man sich vorstellen kann. #DigitaleSouveränität #OpenSource #Schweiz https://www.heise.de/news/Schweiz-startet-Open-Source-Arbeitsplatz-fuer-3000-Beschaeftigte-11444842.html?wt_mc=rss.red.unbekannt.unbekannt.atom.beitrag.beitrag
 @michabbb@social.vivaldi.net @adulau@infosec.exchange
So finally Kimi-k3 is not really open-source
#kimi #ai #opensource
@grist@fosstodon.orgUpdating Grist means pulling a new Docker image and restarting the container. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
 @kingconsult@berlin.social
Dossier in #DasParlament: #DigitaleSouveränität: Wie raus aus der Abhängigkeit? ¹
mit Beiträgen von/über: Thomas #Jarzombek, Friedhelm Greis, @… @…, Leonhard Kugler @…, @…, @… uvm:
🔹 Drei Länder, drei Wege: #Frankreich #Südkorea #Finnland
🔹 #SchleswigHolstein stellt auf #OpenSource um
🔹 Vom #DigitalIndependenceDay bis zum Großkonzern …
¹ #DasParlament, herausgegeben von @…:
👉 #Digitalisierung #DiDit #2MR
@michabbb@social.vivaldi.net🧩 #Laravel LSP announced at #LaraconUS 2026: a first-party language server that teaches your editor about your app #PHP
 @michabbb@social.vivaldi.net
🌈 zsh-patina is an #opensource #Zsh plugin that highlights your command line while you type — written in #Rust, MIT licensed 🧵👇
 @michabbb@social.vivaldi.net
🔌 #Toolport is a local-first #MCP gateway. Every AI client points at one port and shares the same servers, so you set up and authenticate each server once instead of in every app.
#opensource
 @ErikJonker@mastodon.social
Goed nieuws in deze brief van Stas Eerenberg aan de Tweede Kamer. Hulde aan de @…
#opensource #belastingdienst #onpremis #foss
@michabbb@social.vivaldi.net🔐 Hermes Vault: a local-first credential broker and encrypted vault for AI agents. It scans for plaintext secrets, brokers policy-gated access and proves audit integrity.
#opensource #security #MCP
@michabbb@social.vivaldi.net🐢 #Atuin is an #opensource shell history tool written in #Rust that replaces your existing shell history with a #SQLite
 @michabbb@social.vivaldi.net
📊 #OpenPanel is an #opensource web and product analytics platform — an alternative to #Mixpanel,

 @castarco@hachyderm.io
A short video showcasing the current state of the #SoulCrafted Slicer I'm working on.
#3dPrinting #Resin3dPrinting #SoulCraftedSlicer #FLOSS #OpenSource #Rust #Rustlang
 @michabbb@social.vivaldi.net
🧰 #ECC is an #opensource agent harness optimization system that adds skills, instincts, memory, security and research-first development to #ClaudeCode,
@michabbb@social.vivaldi.net🐚 #direnv is a shell extension that loads and unloads environment variables depending on the current directory. A .envrc file in a project folder gives you per-project environments without cluttering your ~/.profile #opensource

 @gla@mastodon.social
That's a nice little utility, also available as a #launchbar action
#markdown #html #opensource
@michabbb@social.vivaldi.net📺 youtube-subscriptions-ingest pulls video metadata from your real #YouTube subscriptions and turns it into a cross-linked knowledge graph in your #Obsidian second brain, not just a flat list of videos #opensource
 @mgorny@social.treehouse.systems
Too many days working on #FLOSS feel like: "I'm not paid for this shit. I'm paid to do other shit and I have to focus on that shit, but I can't when I have to spend so much time fixing shit that apparently others are being paid to break all the time."
#Gentoo #LLVM #FreeSoftware #OpenSource
@kingconsult@berlin.socialDie Gesellschaft für #Informatik ( @… − folgen!) fordert im neuen Policy Brief die Anerkennung und Besserstellung von #OpenSource-Software-Stewards ( Das sind Verwalter quelloffener Software,#OSSStewards ) nach der EU 🇪🇺 #Cyberresilienz-Verordnung.
15.07.2026:
👉 #CyberResilienceAct #CRA #FOSS #FLOSS #Cybersicherheitsstrategie #ITSecurity #DutGemacht
@michabbb@social.vivaldi.net🔍 #Hunk is a review-first terminal diff viewer for agent-authored changesets #opensource #git #cli
 @michabbb@social.vivaldi.net
🧹 shadcn/lint by #shadcn is an agent-first linter for #TailwindCSS design systems: write design system rules that #AI coding agents can verify
 @enriquericos@mastoart.social
Reading a lot of Linux projects talking about LLMs now, focusing on if they work well enough or not. No talk about ethics, ideals or politics.
If it continues down this path, FLOSS will end up like the Ed Sheeran of software.
#software #foss #floss #libresoftware #linux #lxqt #desktopEnvironment #openSource #ethics #llm #techbros #tech
@ErikJonker@mastodon.socialInteresting 🤔
#AI #opensource #openweights #china #usa #geopolitics #foss
@michabbb@social.vivaldi.net📋 #Archify is an #opensource #AI #agent
 @kingconsult@berlin.social
#FollowFriday
👉 @…
»The first conference dedicated to #OpenSource software in #Luxembourg for the greater region and beyond.«
👉 @…
»Digitale Kompetenzen für Berlins #Kulturbereich.« Konferenz „On/Off“ 15. Okt.: #Berlin.Check out talks from previous editions: https://fair.tube/c/fediday/videos « …
@adulau@infosec.exchangeA standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick.
Source code: #misp #cti #threatintelligence #opensource #threatactor #cybersecurity
 @michabbb@social.vivaldi.net
🔐 #AgentVault is an #opensource HTTP credential proxy and vault from #Infisical that sits between #AIagents
 @michabbb@social.vivaldi.net @michabbb@social.vivaldi.net
📋 #CrabTrap by #Brex is an #opensource HTTP/HTTPS proxy that sits between #AI agents and externa…
 @adulau@infosec.exchange
GCVE BCP-07, the Known Exploited Vulnerability (KEV) Assertion Format, has been updated to version 2.2. A key addition is the formalisation of the GCVE KEV Directory, a simple machine-readable directory allowing organisations to announce where their KEV catalogues and exploitation assertions are published.
We particularly encourage software and hardware vendors to publish their own KEV catalogues. Vendors are often in the best position to confirm exploitation affecting their products, and publishing this information in a machine-readable form can significantly improve vulnerability prioritisation for users, CSIRTs and vulnerability-management platforms.
For more details #GCVE #GNA #vulnerabilityintelligence #opensource #KEV #cybersecurity
@…
@michabbb@social.vivaldi.net☁️ #Floci is a free, #opensource local #AWS emulator built with #Quarkus Native — AWS-compatibl…
@adulau@infosec.exchangeThe Radio Image Framing Protocol (RIFP) 1.0 is an experimental, extensible standard for sending images over low-rate radio links.
The default rifp-cpfsk-4800 profile uses binary continuous-phase FSK and can be deployed around 433.92 MHz where local regulation permits it. RIFP itself is not tied to 433 MHz or to FSK and can be used in any frequency bands.
I'm still exploring various low-cost options for a device that can receive and display images on an e-ink screen in emergency areas or similar environments. Python implementation #radio #fax #433mhz #opensource
 @michabbb@social.vivaldi.net
🎨 Inspo — real production websites your coding agent can study before it writes UI #opensource #MCP #webdev #AI
@kingconsult@berlin.socialMehr digitale Autonomie gefordert:
Die niederländischen 🇳🇱 Behörden für Verbraucher und Märkte, #Finanzmärkte, #Datenschutz, digitale #Infrastruktur und die »De Nederlandsche Bank« fordern #Unternehmen und #Regierungen auf, den Übergang zu mehr digitaler Autonomie zu beschleunigen.
10. Juli 2026: Bericht
»Der Weg zur digitalen Autonomie« (PDF NL)
👉 #2MR #DigitalSovereignty #DigitaleSouveranitat #DutGemacht #DiDIT #Digitalisierung #OpenSource #OSWA
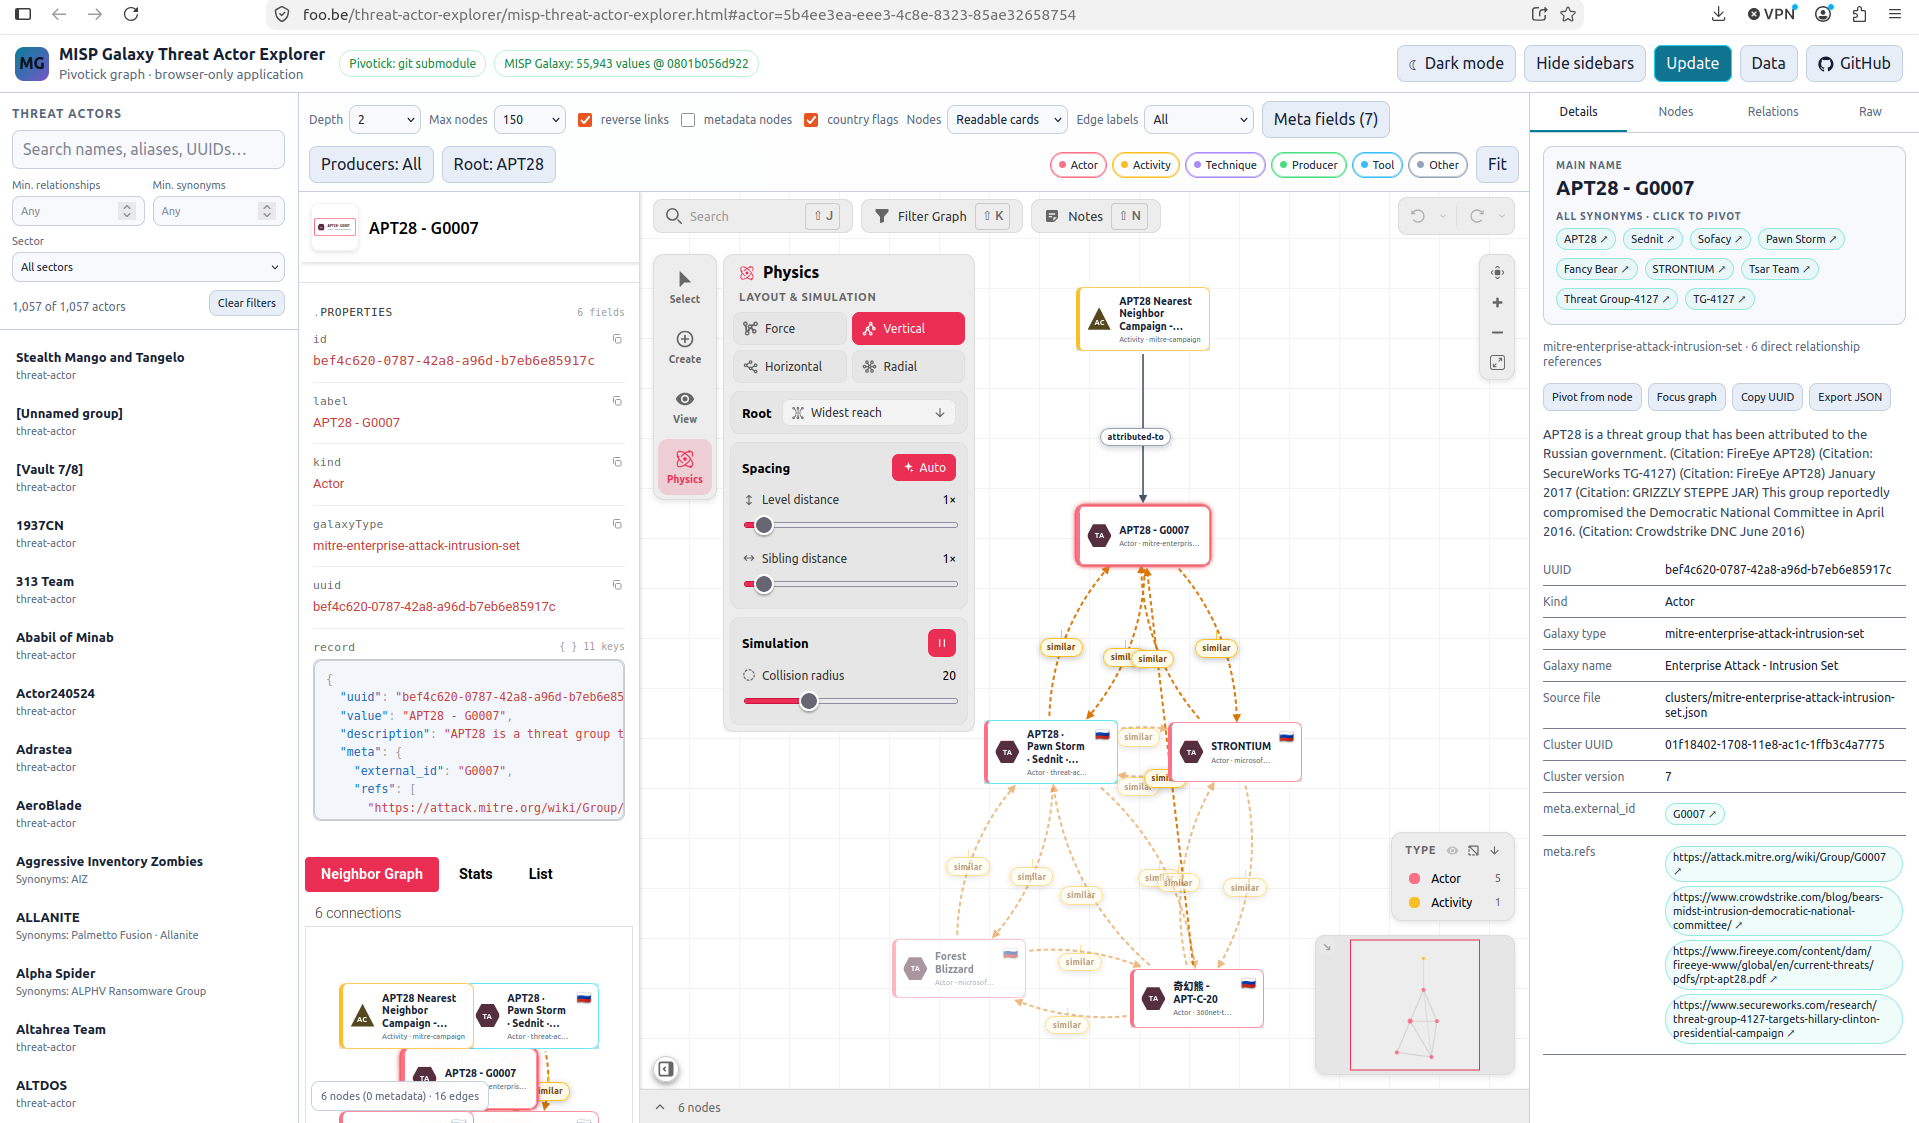
@adulau@infosec.exchangeThreat-Actor explorer v1.1.0 released with many improvements and upgrade to the latest Pivotick library Latest
A standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick. #misp #threatactor #threatintelligence #cybersecurity #mispgalaxy #cti #opensource #cybersecurity
 @ErikJonker@mastodon.social
Looking at and playIng around with Hermes Agent, impressive and relatively easy to install and use.
Also opensource. Hermes Agent — Open-Source AI Agent That Grows With You | Nous Research #AI #HermesAgent #opensource #foss #agents
@adulau@infosec.exchangeWe were very happy to participate in Vulnopticon 2026 and to meet so many people interested in vulnerability identification, publication, coordination, and management.
The discussions during the conference and just as importantly, the conversations around and outside the formal sessions brought a lot of useful feedback, new ideas, questions, and potential directions for GCVE. These exchanges are especially valuable for a project such as GCVE, where openness, federation, interoperability, and experimentation are at the core of the initiative.
🔗 #cve #gcve #vulnerabilityManagement #vulnerability #opensource
@michabbb@social.vivaldi.net📋 #HuntProxy is an #opensource web security workbench built for #AI agents — connect it over #MCP
@adulau@infosec.exchangeGCVE BCP-05-X-03: Bringing Vulnerability Handling Timelines into Vulnerability Records.
Vulnerability records usually provide a good description of what a vulnerability is, which products are affected, how severe it may be, and where additional information can be found.
They are often much less effective at describing what happened, when it happened, and who was involved during the vulnerability handling and disclosure process.
Following many discussions during VulnOptiCON 2026 in Luxembourg, this limitation became particularly clear. Vulnerability analysts, coordinators, vendors and other participants repeatedly discussed how difficult it can be to reconstruct a reliable timeline during vulnerability analysis and coordinated vulnerability disclosure.
To help address this, the GCVE initiative has published a new extension:
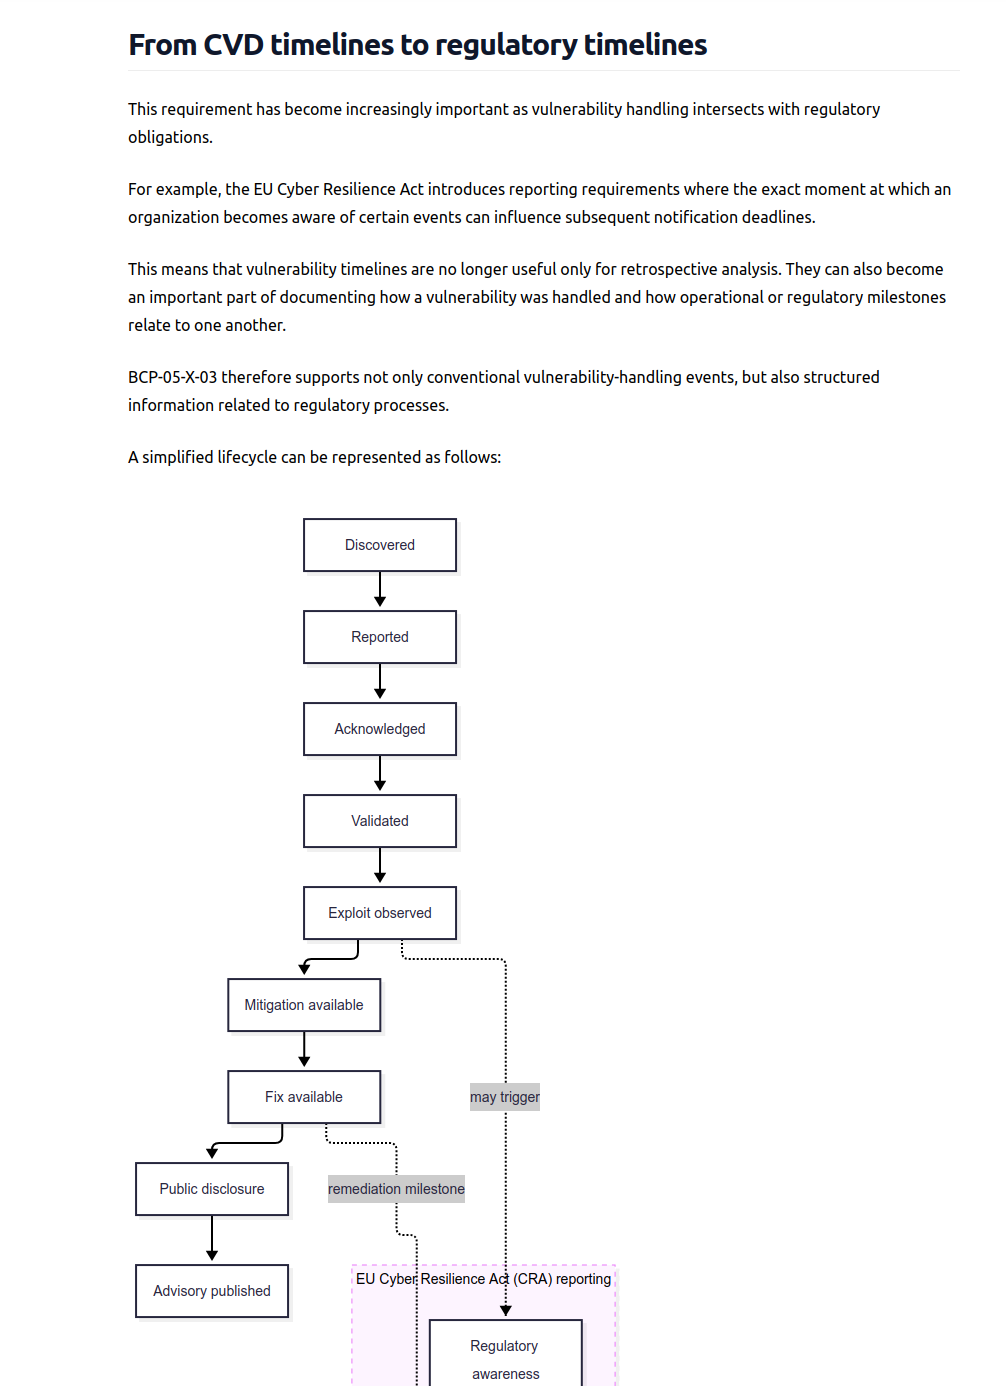
GCVE BCP-05-X-03 - Vulnerability Handling and Disclosure Timeline.
The extension provides a structured and machine-readable way to represent the lifecycle of a vulnerability from discovery and reporting through acknowledgement, validation, remediation and public disclosure. It's already live in our open-source tool-set.
🔗 Blog post #opensource #openstandard #cve #gcve #cra #cybersecurity #vulnerability
 @ErikJonker@mastodon.social
Working together on digital autonomy
The DAWO community is an open community in which government, industry and society jointly build a digitally autonomous workplace for the Dutch government.
#opensource #foss #workplace #government #Netherlands #dawo #community
@adulau@infosec.exchangePivotick is an open-source network graph library to facilitate pivoting.
Version 1.4.0 has been released and also includes a security fix.
Release notes #opensource #infovis #graph #networkgraph #visual
 @adulau@infosec.exchange
I spent many hours in vulnogram today and to be honest. I'm glad that a colleague started to work on a replacement called vulniverse. Still early beta but it's promising.
#opensource #vulniverse #cybersecurity #cve #gcve work in progress https://github.com/vulnerability-lookup/vulniverse
@adulau@infosec.exchangeI just released ptrclassify is a small, dependency-free Python library and CLI that infers likely IP usage from reverse-DNS PTR hostnames.
It is intentionally heuristic and multi-label. PTR naming is operator-controlled and is not authoritative evidence of how an address is actually used. The output therefore includes a confidence score, the text that matched, and the rule IDs that produced each label.
To summarize, the library is trying to guess usage (and a bit location) of an IP address based on its PTR records. It's based on a set of rules which can be updated easily.
#osint #cybersecurity #ptrclassify #opensource #dns https://github.com/adulau/ptrclassify module https://pypi.org/project/ptrclassify/
@adulau@infosec.exchangeWe discussed decentralized vulnerability allocation, digital sovereignty, CVD workflows, Vulnerability-Lookup, Vulniverse, AI-assisted vulnerability analysis, and the future of GCVE.
All slide decks and workshop materials are now available:
🔗 #cve #gcve #cvd #cybersecurity #opensource #vulnerability #vulnerabilityManagement
@…
@kingconsult@berlin.social> @… announces 60 projects strenghtening the #DigitalCommons ¹
➡️ There are two #Fediverse-related tools:
#ActivityBot — A full #ActivityPub server in a single #PHP file
👉 #Fedipub — #Ruby Library for adding #ActivityPub Federation
👉 #NLnet #OpenSource #SocialMedia #OpenSocialWeb #FOSS #FLOSS
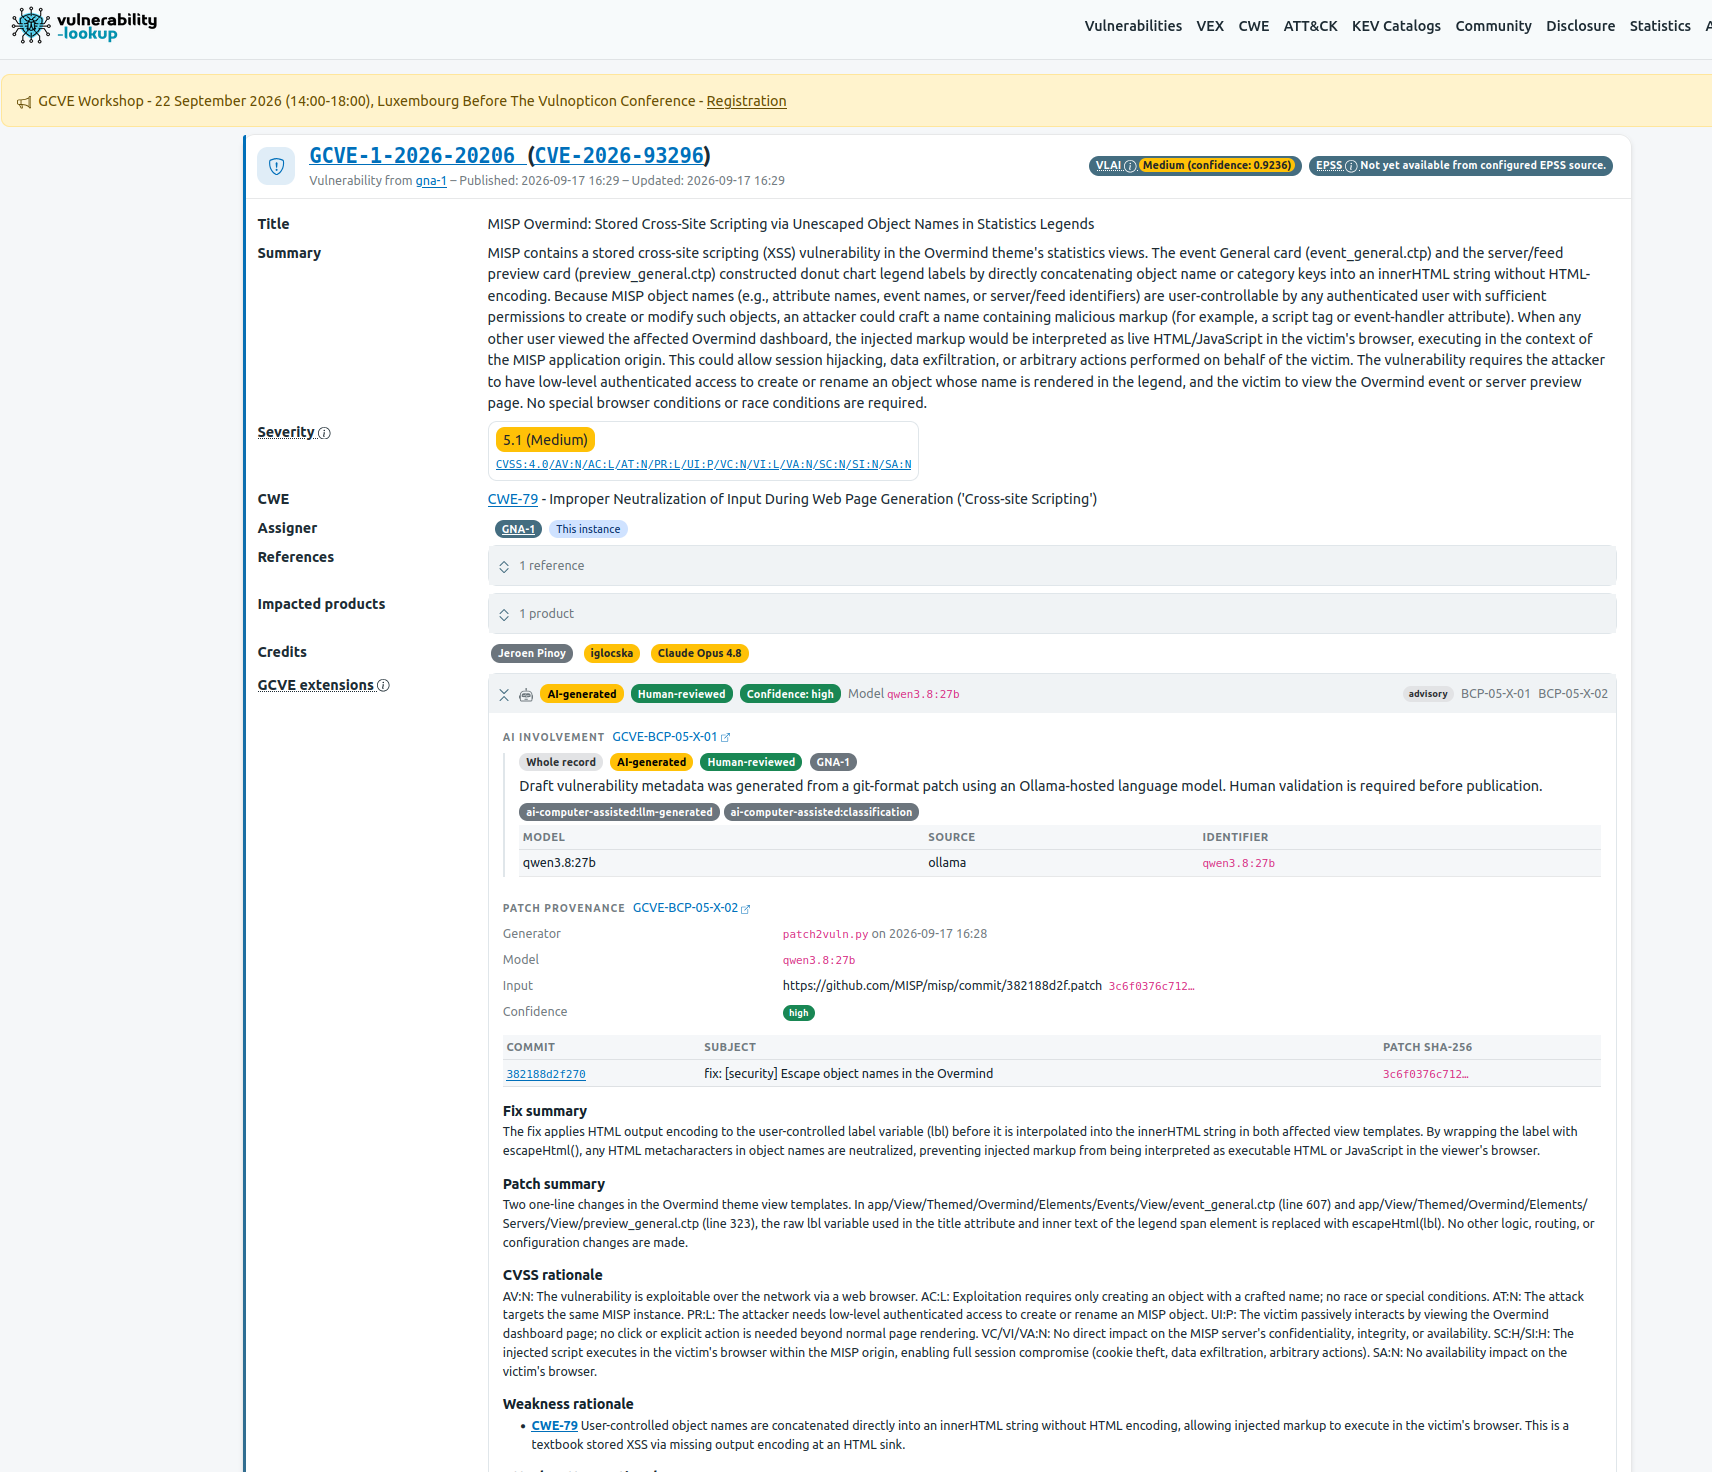
@adulau@infosec.exchangeTired of drafting vulnerability advisories from Git patches?
We developed patch2vuln to facilitate the creation of security advisories directly from Git patches.
With a single command, patch2vuln can assist an analyst throughout the advisory creation process: analyzing the patch, drafting the vulnerability title and description, identifying CWE and CAPEC mappings, proposing a CVSS v4.0 vector, extracting affected versions, remediation information and credits, and generating a structured CVE/GCVE record.
The analysis can run entirely locally using an LLM via Ollama, while deterministic processing is used for elements such as CVSS scoring and structured output validation.
The goal is not to replace the security analyst, but to remove much of the repetitive work and provide a solid structured draft for human review and publication.
patch2vuln v1.0 is now available as open-source software under the @… Lab initiative.
#VulnerabilityManagement #CVD #CVE #GCVE #OpenSource #CyberSecurity #AI
 @adulau@infosec.exchange
I love to see clever use of the @… ecosystem and @… did a cool GNA which is automatically creating GCVE records and structured security advisories from full-disclosure mailing-list or alike:
🔗 Project details #gcve #cve #vulnerability #vulnerability #opensource #cybersecurity
@adulau@infosec.exchangeWe had difficulties automatically classifying chats, messaging channels, and forums. So we tested several open-weight large language models for our use case. The benchmark is published below, along with a tool supporting the classification process.
This helps us avoid manually classifying channels collected from dark-web forums and social networks, while reliably identifying which channels can be discarded and which deserve further analysis.
🔗 Publication #ai #llm #cybersecurity #darkweb #osint #opensource
@adulau@infosec.exchangeFrom a research paper to running open-source code in just a few days.
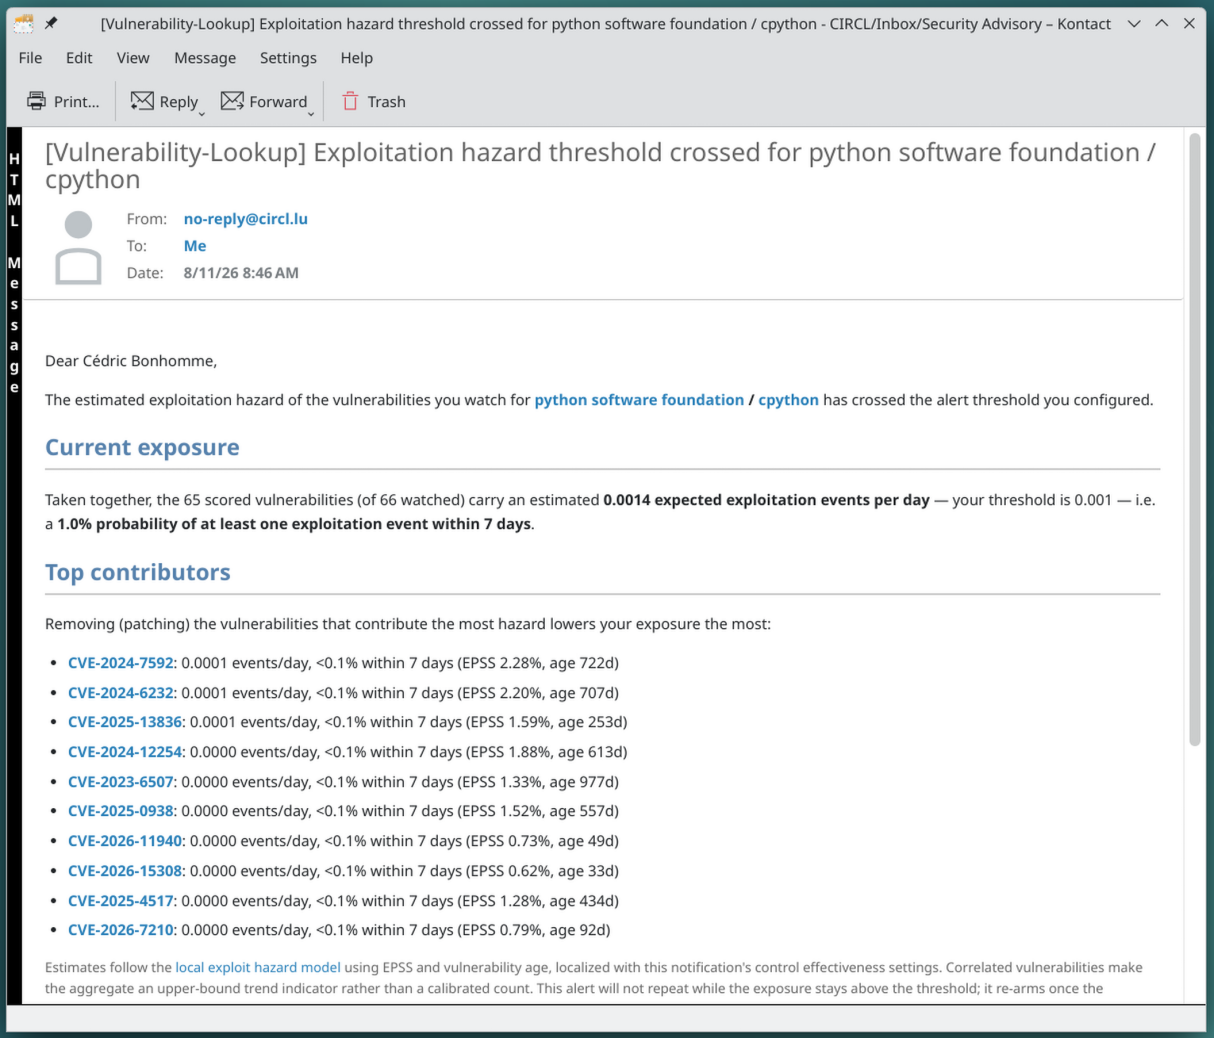
We (with @…) have been experimenting in Vulnerability-Lookup with the concept of Local Exploit Hazard, based on the recent research paper “Modeling Local Exploit Hazard — A Bayesian Framework for Quantifying Exploit Risk and Operational Efficiency” by Stephen Shaffer and Laura Cristiana Voicu.
The idea addresses an important question in vulnerability management:
Not simply “How dangerous is this vulnerability globally?” but “How much exploitation risk does this vulnerability represent in my environment?”
Instead of introducing yet another static vulnerability score, the model starts from exploit likelihood such as EPSS and combines it with local security controls, CVSS attack vectors, vulnerability age and KEV policy to estimate an exploitation hazard.
We implemented an experimental version in Vulnerability-Lookup and connected it directly to operational workflows.
For the full details: #cve #gcve #vulnerabilitymanagement #vulnerability #opensource #opendata
@…
 @adulau@infosec.exchange
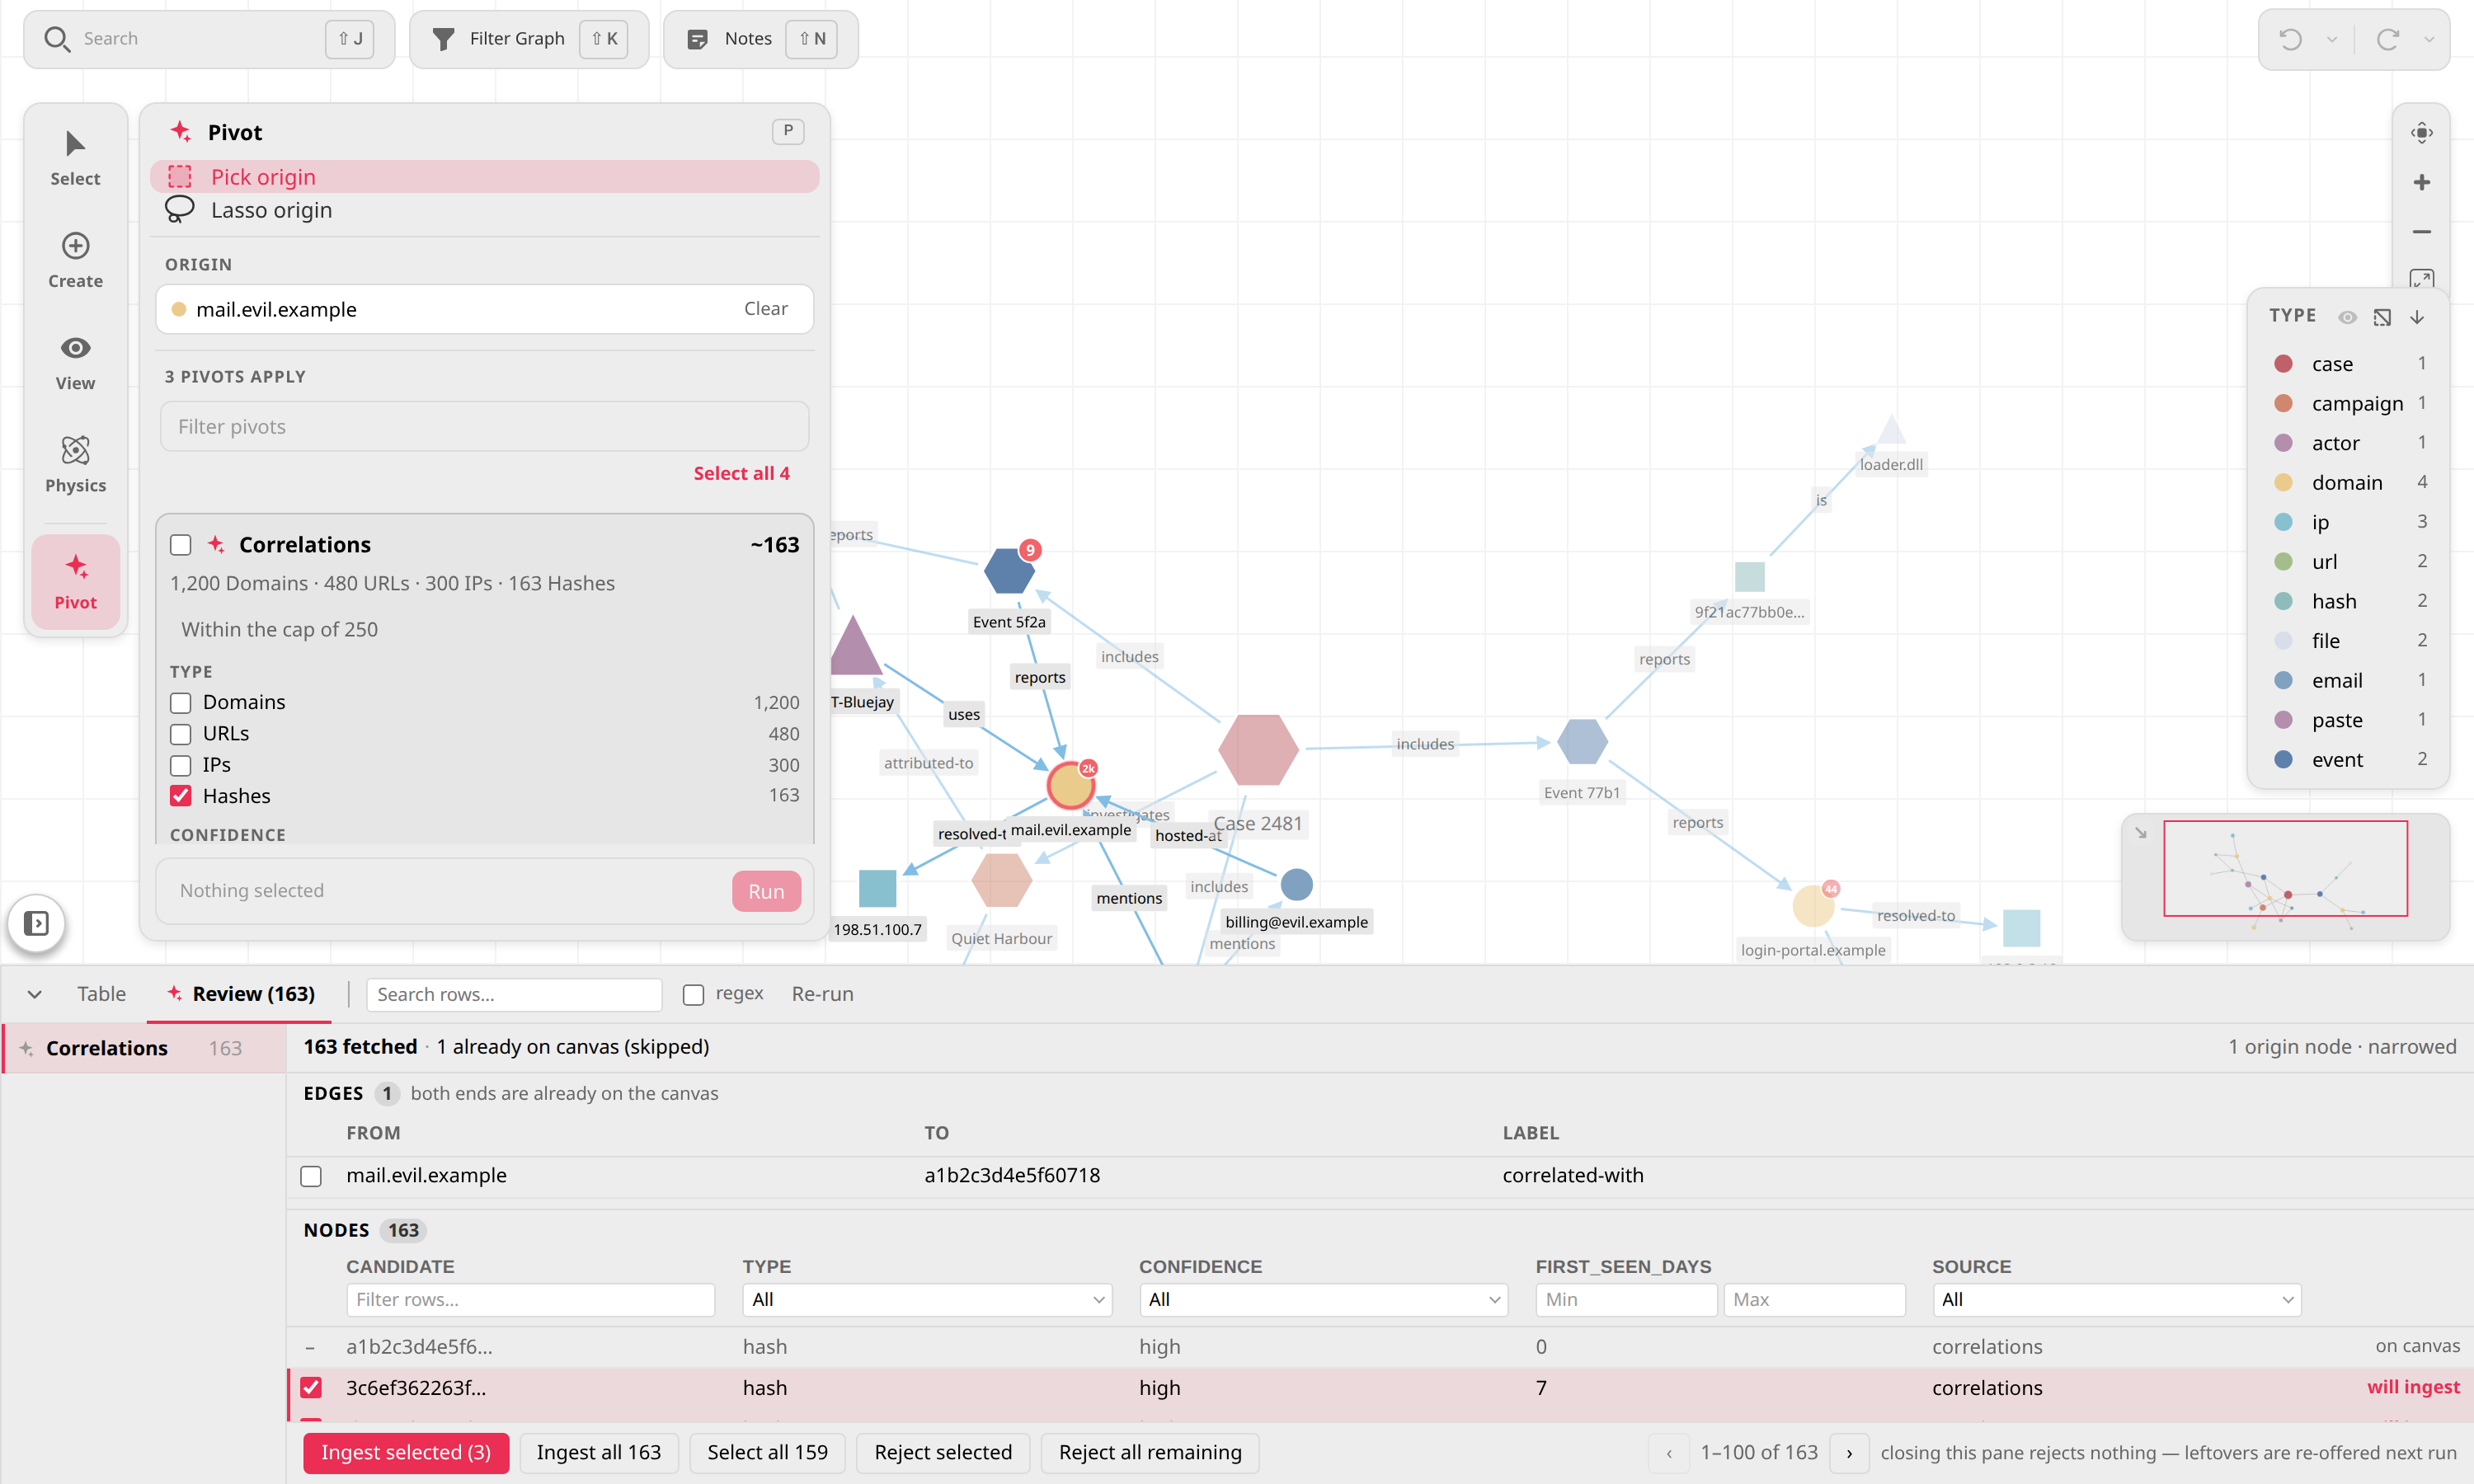
Pivotick v2.0.0 has been released.
Pull more graph out of wherever your data lives, and you choose what lands. History is the way back out of anything that does.
Actually you can update, pivot graph and review. This release also includes many new other features.
#graph #library #infosec #opensource #graphing #pivotick #cti #threatintelligence
 @adulau@infosec.exchange
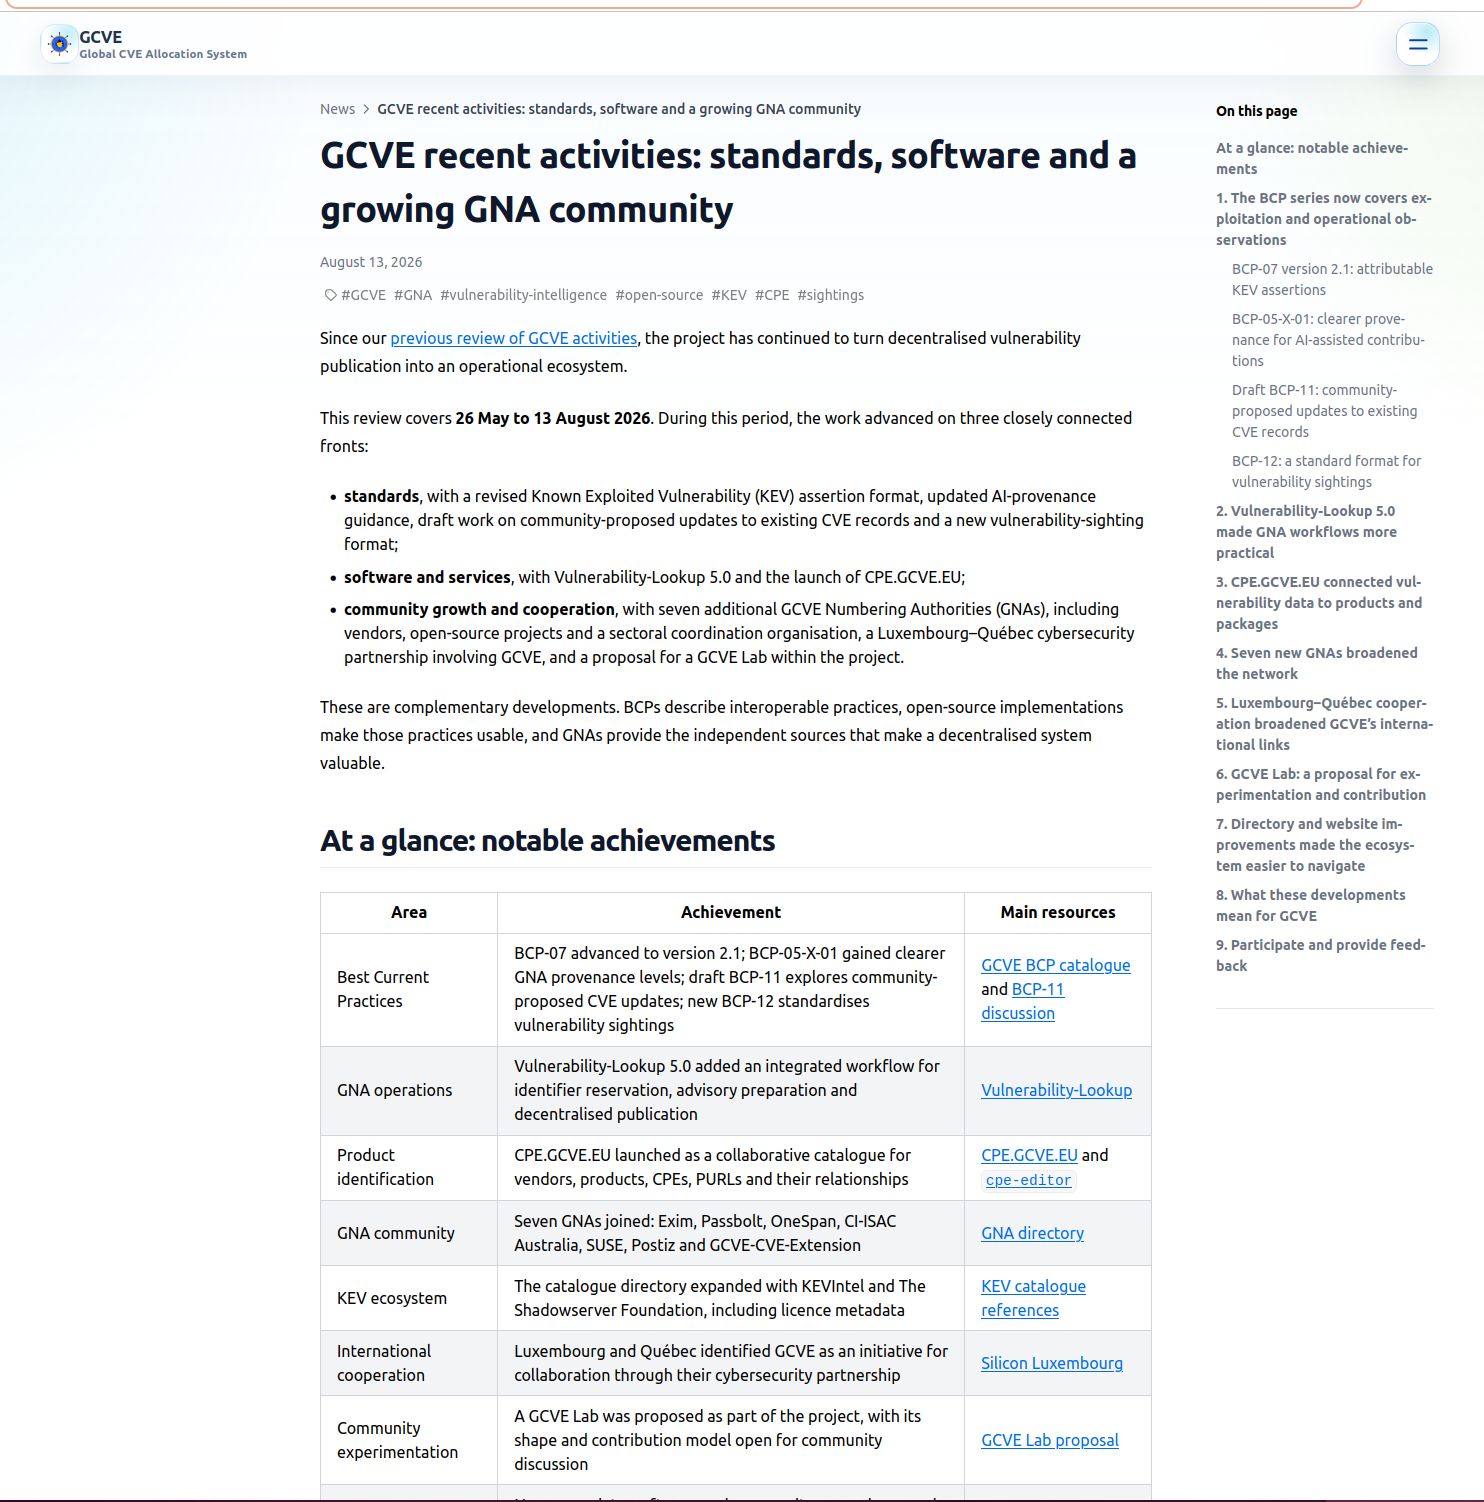
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource
 @adulau@infosec.exchange
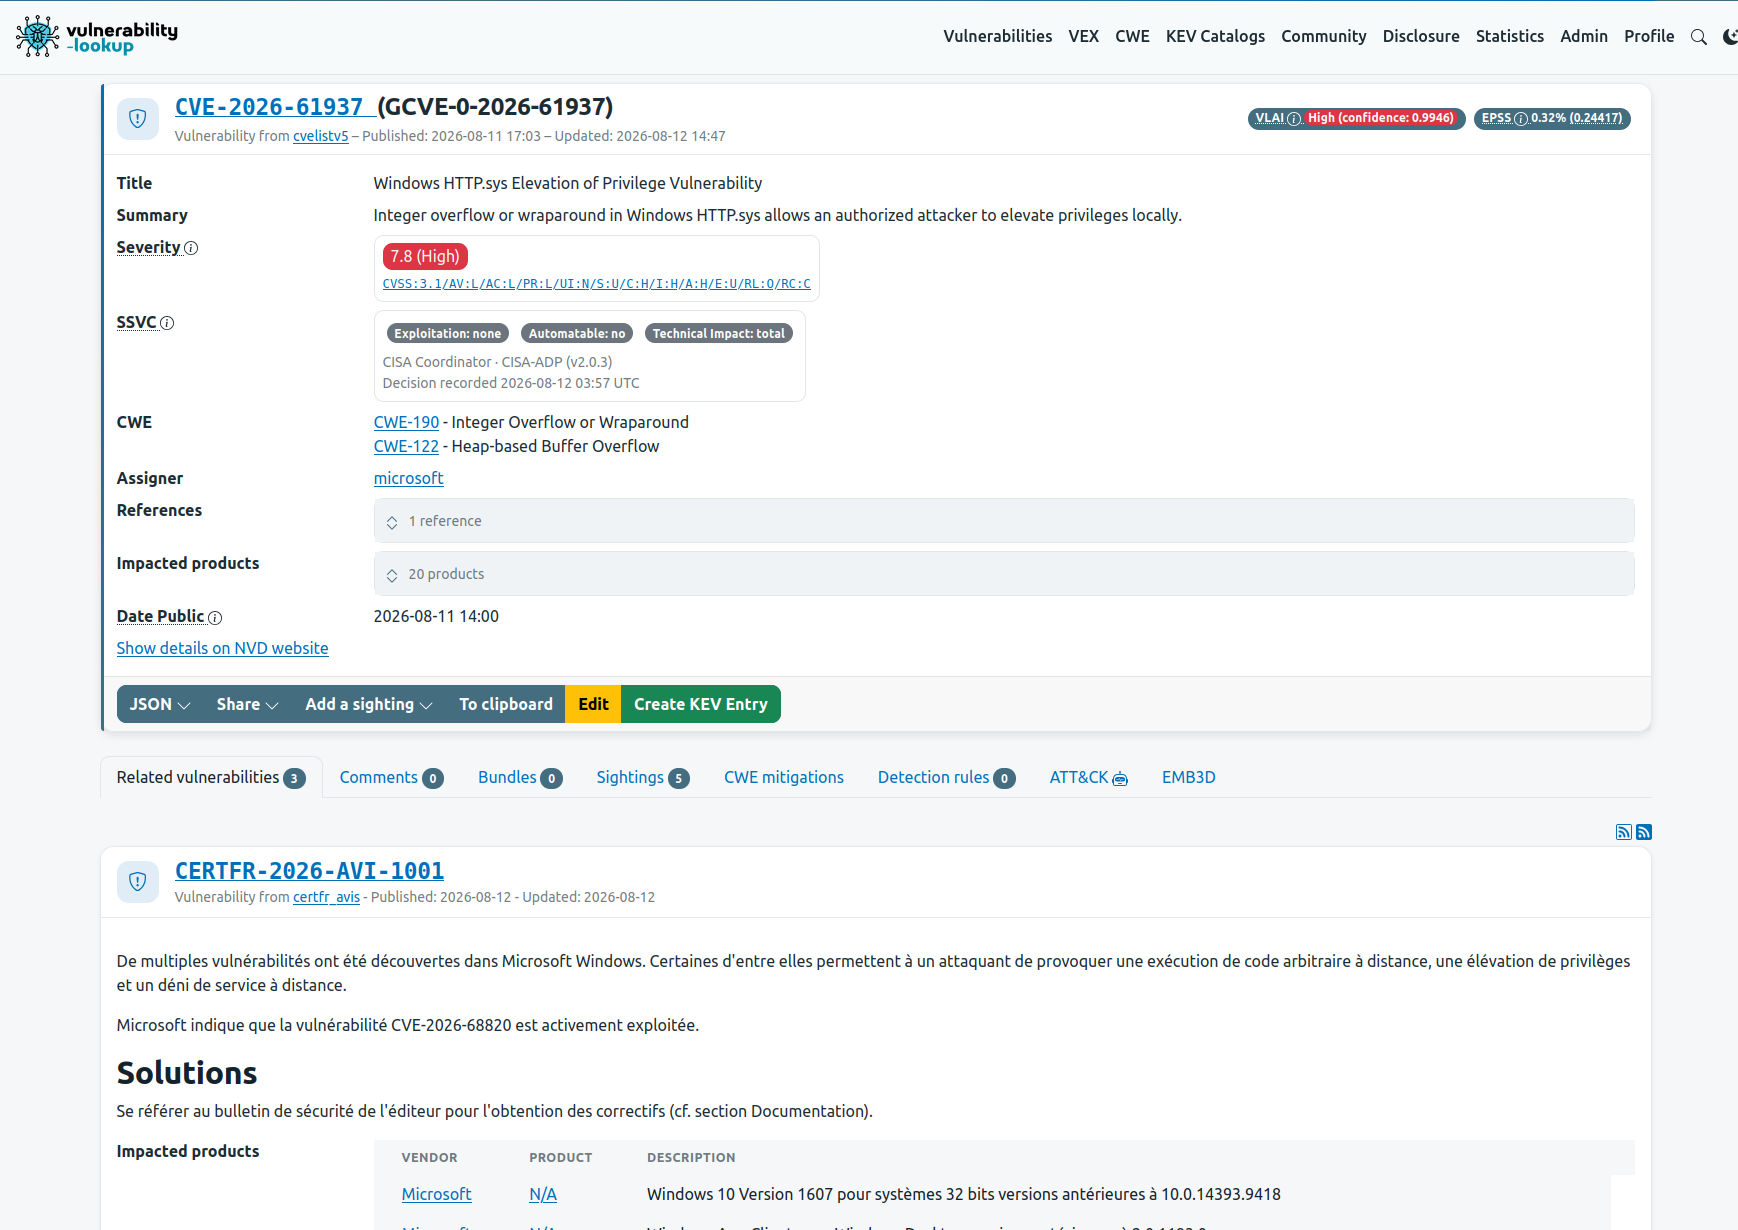
vulnerability-lookup 6.0 will be released this week with many (really, many!) new features.
One of the smaller, but important, additions is support for multiple SSVC views alongside CVSS. When SSVC information is available from an ADP (such as CISA) , or from additional sources such as GCVE, it is now displayed by default.
This allows users to more easily compare the different severity and prioritization assessments associated with a vulnerability.
The CIRCL vulnerability-lookup instance is running the pre-release of 6.0 -
#cve #gcve #opensource #vulnerabilitylookup #opendata #vulnerabilitymanagement #cyberecurity #ssvc
@…
@…