 @adulau@infosec.exchange
2026-08-13 15:21:01
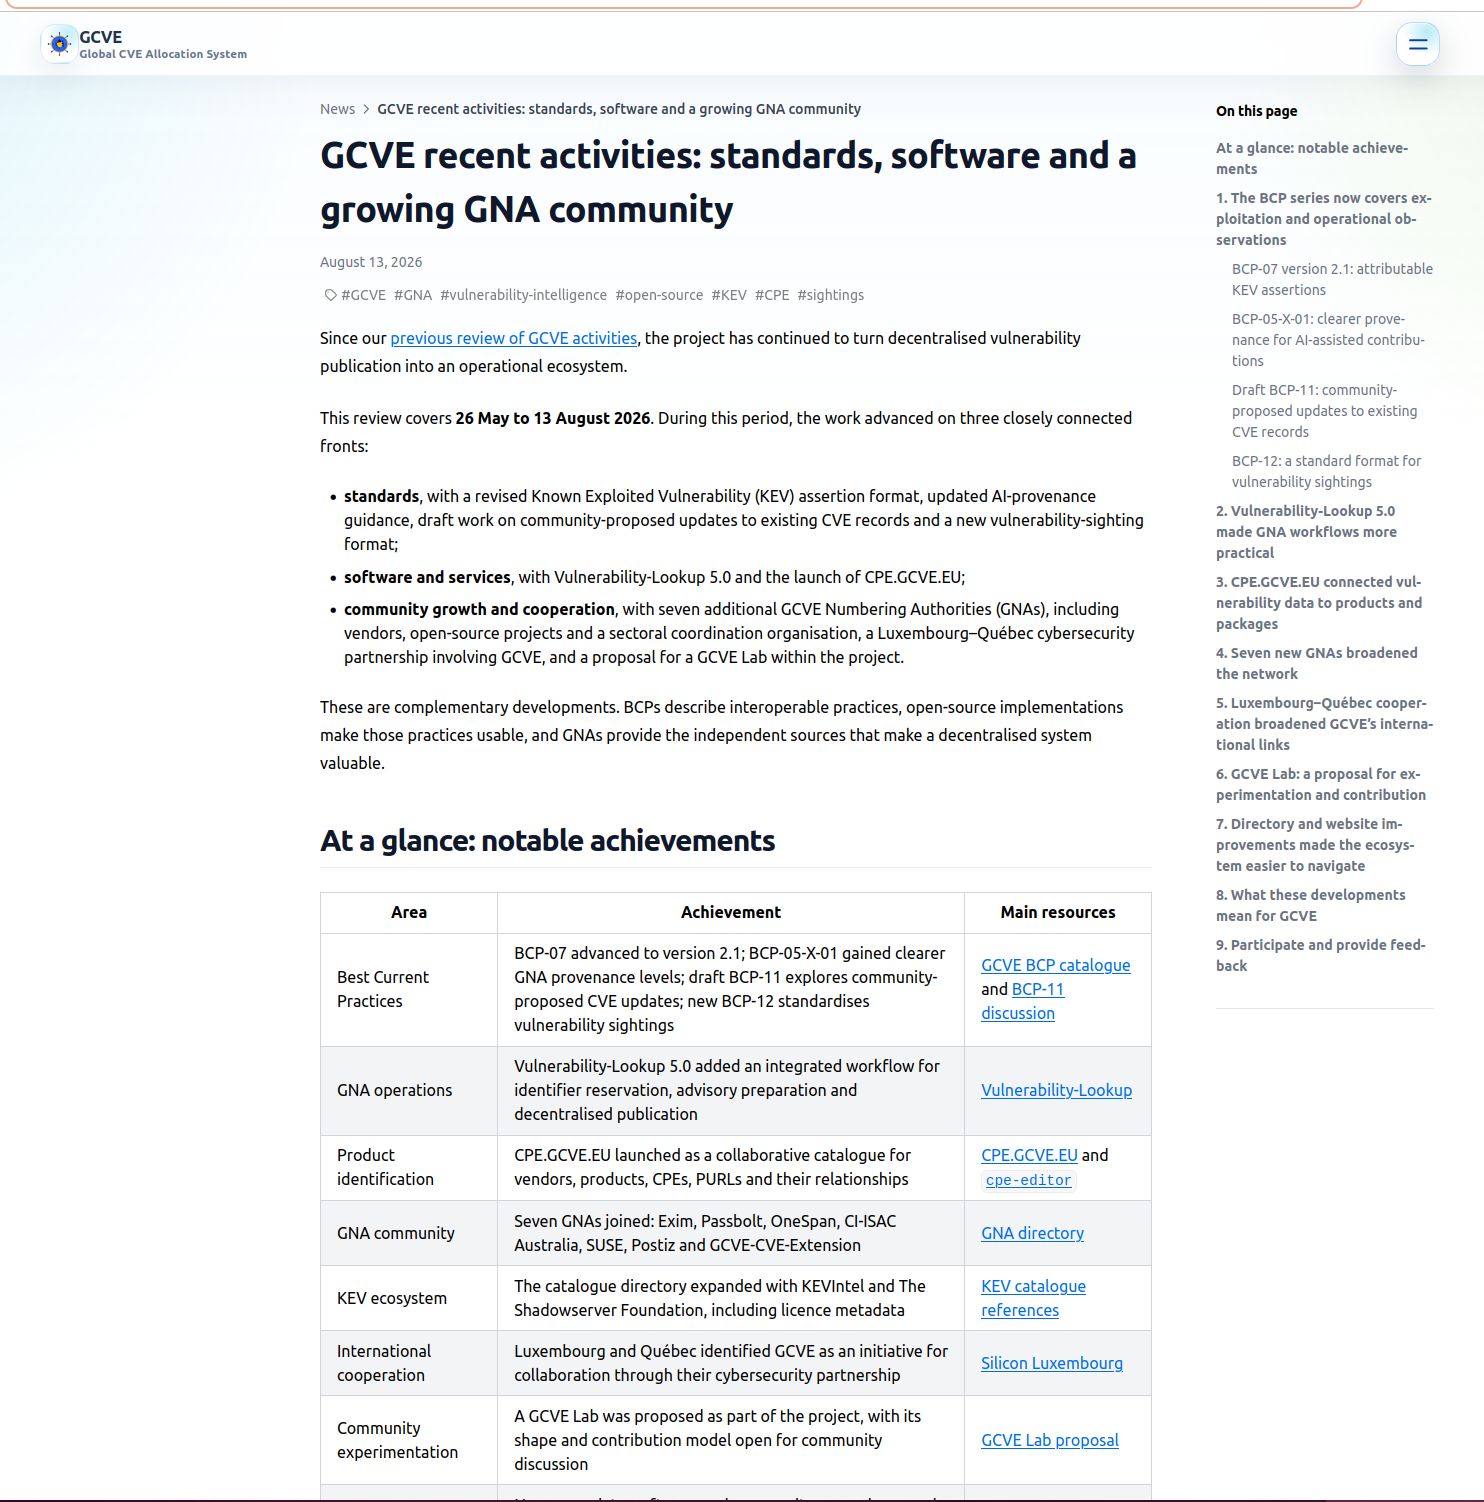
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource
 @adulau@infosec.exchange
If you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource
@adulau@infosec.exchangevulnerability-lookup 6.0 will be released this week with many (really, many!) new features.
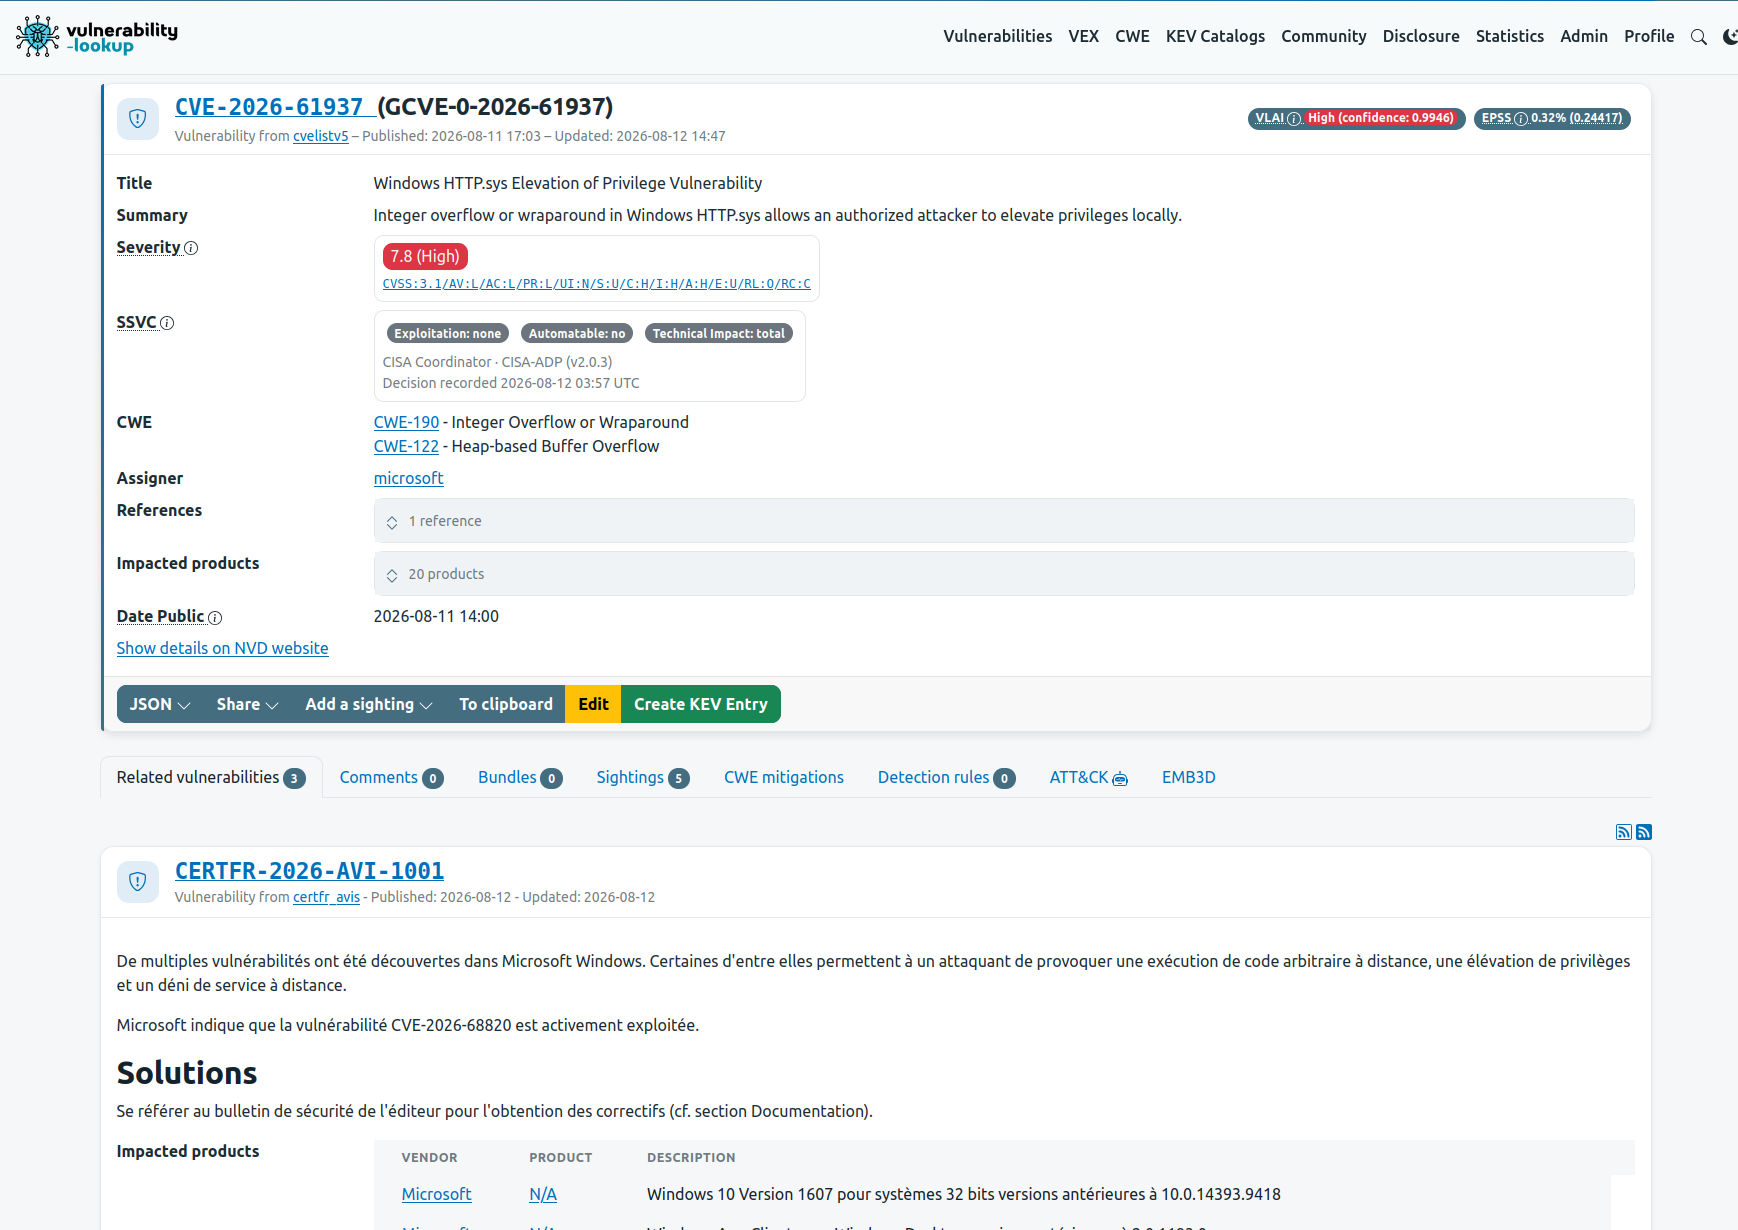
One of the smaller, but important, additions is support for multiple SSVC views alongside CVSS. When SSVC information is available from an ADP (such as CISA) , or from additional sources such as GCVE, it is now displayed by default.
This allows users to more easily compare the different severity and prioritization assessments associated with a vulnerability.
The CIRCL vulnerability-lookup instance is running the pre-release of 6.0 -
#cve #gcve #opensource #vulnerabilitylookup #opendata #vulnerabilitymanagement #cyberecurity #ssvc
@…
@…
 @adulau@infosec.exchange
From a research paper to running open-source code in just a few days.
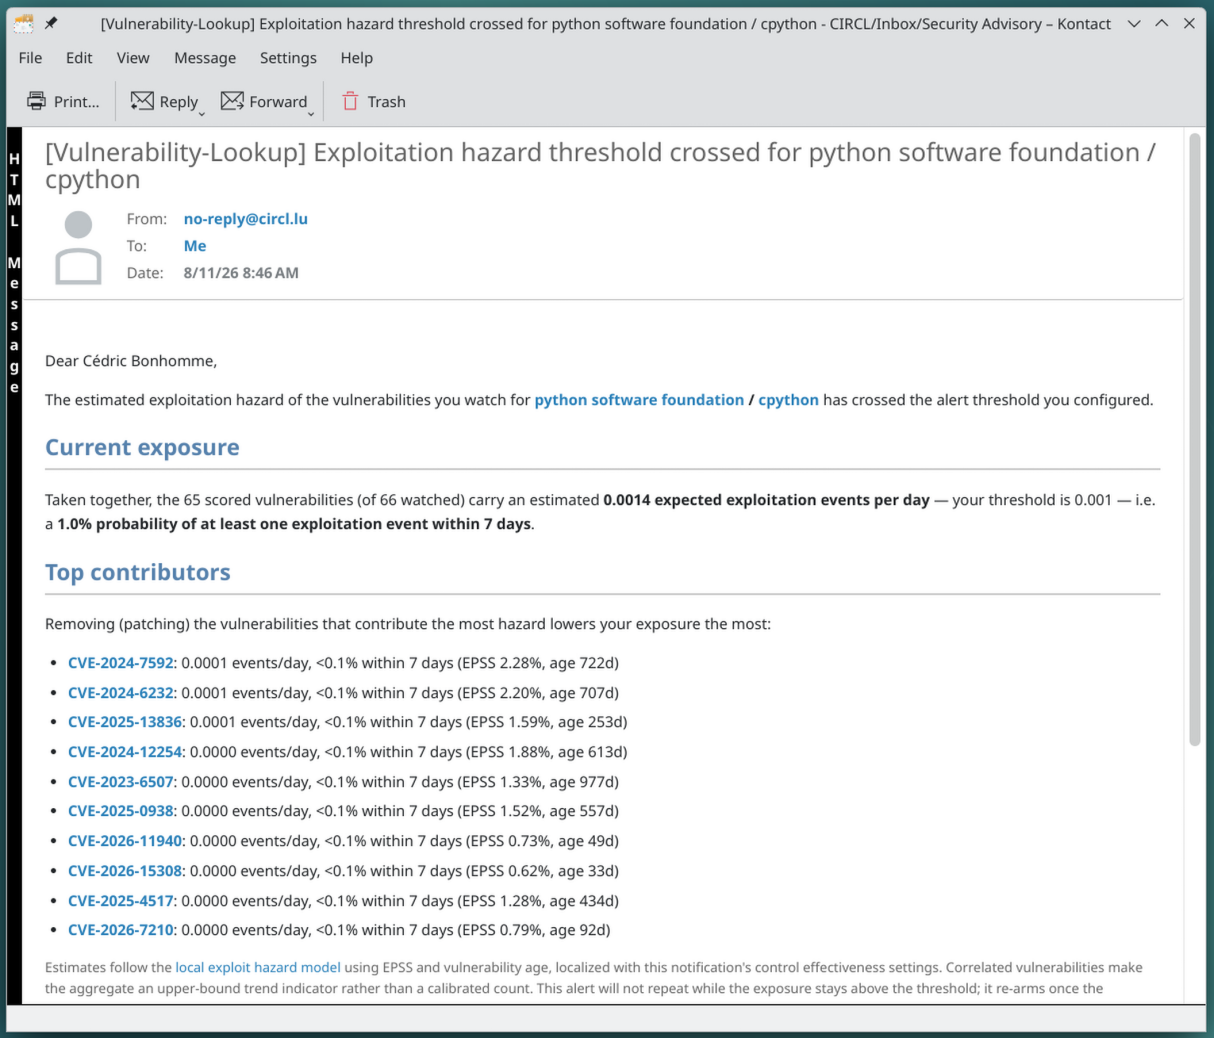
We (with @…) have been experimenting in Vulnerability-Lookup with the concept of Local Exploit Hazard, based on the recent research paper “Modeling Local Exploit Hazard — A Bayesian Framework for Quantifying Exploit Risk and Operational Efficiency” by Stephen Shaffer and Laura Cristiana Voicu.
The idea addresses an important question in vulnerability management:
Not simply “How dangerous is this vulnerability globally?” but “How much exploitation risk does this vulnerability represent in my environment?”
Instead of introducing yet another static vulnerability score, the model starts from exploit likelihood such as EPSS and combines it with local security controls, CVSS attack vectors, vulnerability age and KEV policy to estimate an exploitation hazard.
We implemented an experimental version in Vulnerability-Lookup and connected it directly to operational workflows.
For the full details: #cve #gcve #vulnerabilitymanagement #vulnerability #opensource #opendata
@…
 @adulau@infosec.exchange
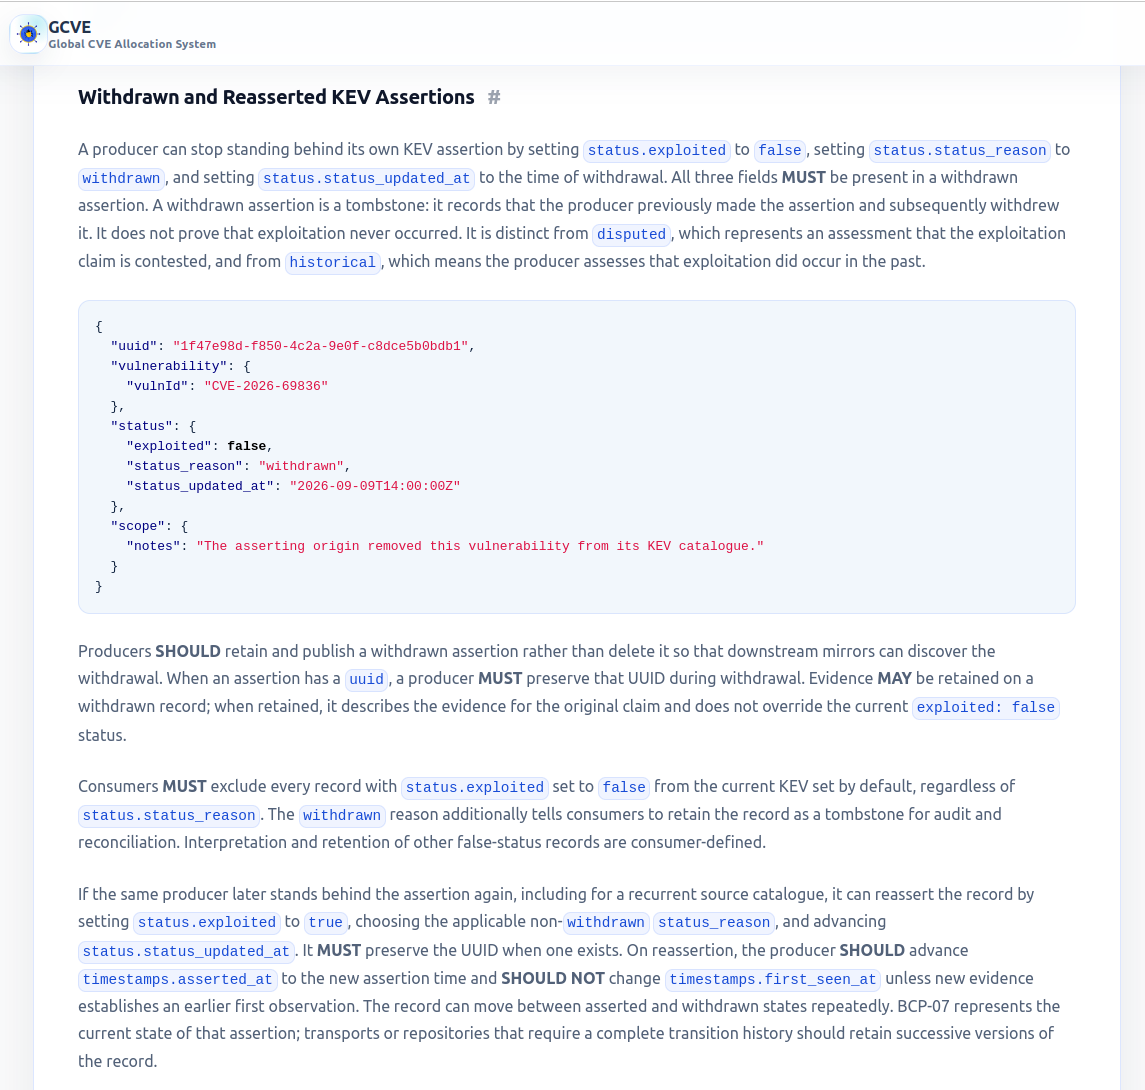
The @… BCP-07 KEV format has been updated to allow the Withdrawn and Reasserted KEV Assertions.
This allows to support case like CVE-2026-69836 .
🔗 #cve #gcve #kev #cybersecurity #vulnerabilitymanagement #vulnerability
 @adulau@infosec.exchange
Proposed changes in the CVE program CNA document
"Update 4.2.6 from SHOULD to MUST: "CNAs MUST assign different CVE IDs to separate Vulnerabilities""
🔗 #cve #vulnerabilitymanagement #cybersecurity
@adulau@infosec.exchangeGCVE Workshop - 22 September 2026 (14:00-18:00), Luxembourg Before The Vulnopticon Conference
We are pleased to announce a GCVE workshop on 22 September 2026, from 14:00 to 18:00, hosted at the CIRCL/LHC offices in Luxembourg, just before the VulnOpticon conference.
The workshop is free and open to everyone, but registration is required.
🔗 #cve #gcve #luxembourg #cybersecurity #vulnerabilitymanagement
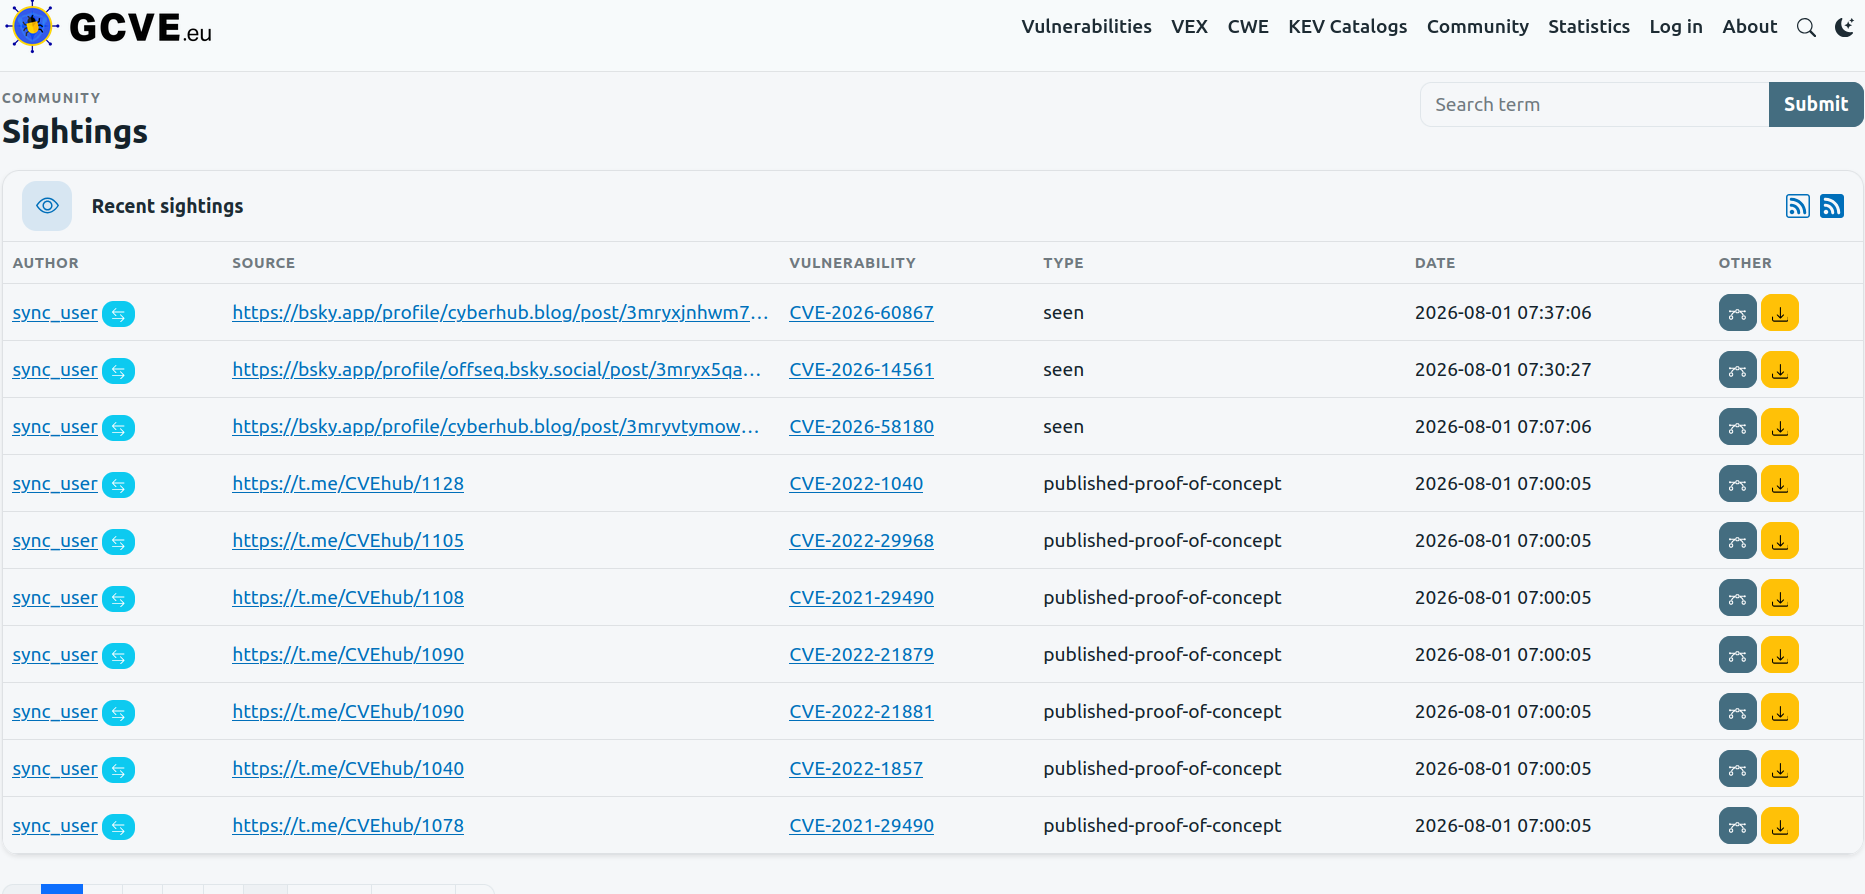
@adulau@infosec.exchangeSightings have long been a major topic of discussion in the CTI community, particularly in the field of vulnerability management. We have now published a GCVE BCP to standardise the format that has been implemented, tested and used operationally in Vulnerability-Lookup for some time.
Thanks to everyone (Cédric Bonhomme, Éireann Leverett, Andras Iklody, Sami Mokaddem and many more) who participated in discussions and worked on the implementation details of sightings over the past several years. These efforts had a strong focus on practical implementation, while BCP-12 specifically addresses sightings in the context of vulnerability management.
BCP-12 is still a draft open for review, but it already provides a strong foundation for existing implementations.
#cve #cra #gcve #vulnerabilitymanagement #cybersecurity #openstandard
 @adulau@infosec.exchange
A new version of the BCP-11 "Community Contribution Fragments for Existing CVE Records" proposal has been published.
#gcve #cve #cybersecurity #vulnerabilitymanagement
@…