 @chiraag@mastodon.online
2026-09-25 19:30:55
Something good may come of PE bankrupting JoAnn's after all:
https://www.theguardian.com/business/2026/sep/24/joann-fabrics-fans-crafts-co-op
 @laxsill@social.spejset.org
2026-06-26 07:30:23
Vad säger ni #drinkklubben

 @bici@mastodon.social
2026-08-24 03:17:20
"The White House wanted to tell us who we could trade with. To take French off your Cheerios box. To bring your milk in from Wisconsin. And to tax us the same ldevel as the grovellers in the UK or Vietnam. Trump does not care about Canada or Canadians, Ukraine, Taiwan, Cubans or sending life-saving vaccines to brown people.
This is a corrupt, inept administration that has disrupted the global economic order, alienated allies and soiled its own flag.... "
@garthturner
 @arXiv_csCR_bot@mastoxiv.page
2026-07-24 07:51:53
Buzz to Boom: Detecting Message Progression Vulnerabilities in Electron Applications via Segmented Directed Fuzzing
Jianjia Yu, Zhengyu Liu, Ziyang Li, Yu Sun, Yinzhi Cao
https://arxiv.org/abs/2607.20698 https://arxiv.org/pdf/2607.20698 https://arxiv.org/html/2607.20698
arXiv:2607.20698v1 Announce Type: new
Abstract: Electron is a popular framework for building cross-platform desktop applications using web technologies. Such applications consist of multiple processes with different privilege levels that communicate via message passing. When inter-process messages carry attacker-controlled inputs, they can propagate across processes and reach privileged APIs, e.g., command execution. Such a message propagation behavior is characterized as Message Progression Vulnerabilities (MPVs). The exploitation of MPVs is challenging because it often requires multiple steps, e.g., first arbitrary code execution in one process via message passing, and then command injection in another process using another message crafted in the first process. To our knowledge, existing works on Electron security only study unsafe configurations and malicious Document Object Model (DOM) content, i.e., they cannot detect or exploit these vulnerabilities that need to be triggered by complex cross-process exploits via message passing. We present Proton, a segmented directed fuzzing framework for detecting MPVs. Our key insight is to decompose end-to-end fuzzing into per-process segments along message-passing boundaries, where the goals of fuzzing each segment are either: (i) reaching a sink in the current process or (ii) propagating the payload to the next process, to enable the exploration of another process. In the second case, the messages seed the corpus of the next segment. Finally, Proton synthesizes crash inputs from each process to validate end-to-end exploits. We evaluate Proton against 589 real-world Electron applications, resulting in 23 zero-day MPVs. Among them, 22 lead to OS command execution, including projects with over 50k GitHub stars. We responsibly disclosed all findings. To date, we have received 13 acknowledgments, 11 fixes, and 11 CVEs, including a bug bounty from Vercel.
toXiv_bot_toot
 @callunavulgaris@mastodon.scot
2026-08-15 15:33:48
The hallway started the day this meh grey-lilac colour, which had become very grubby and marked, and has ended it a nice invisible shade of mangolia. Next step is the stairwell and upstairs landing, maybe tomorrow otherwise next weekend. We'll be changing the pictures to show a few that have been in storage for years. All this because we needed to make good after having the new radiators fitted as part of the #HeatPump


 @cdarwin@c.im
2026-09-19 18:11:13
“The clan of predators currently in charge of the U.S. federal government”
are striving to make the world safe for grift, corruption, and theft,
with their mob boss president leading the way.
https://kottke.org/26/09/0049624-striving-to-make-the-worl
 @toxi@mastodon.thi.ng
2026-09-14 12:48:33
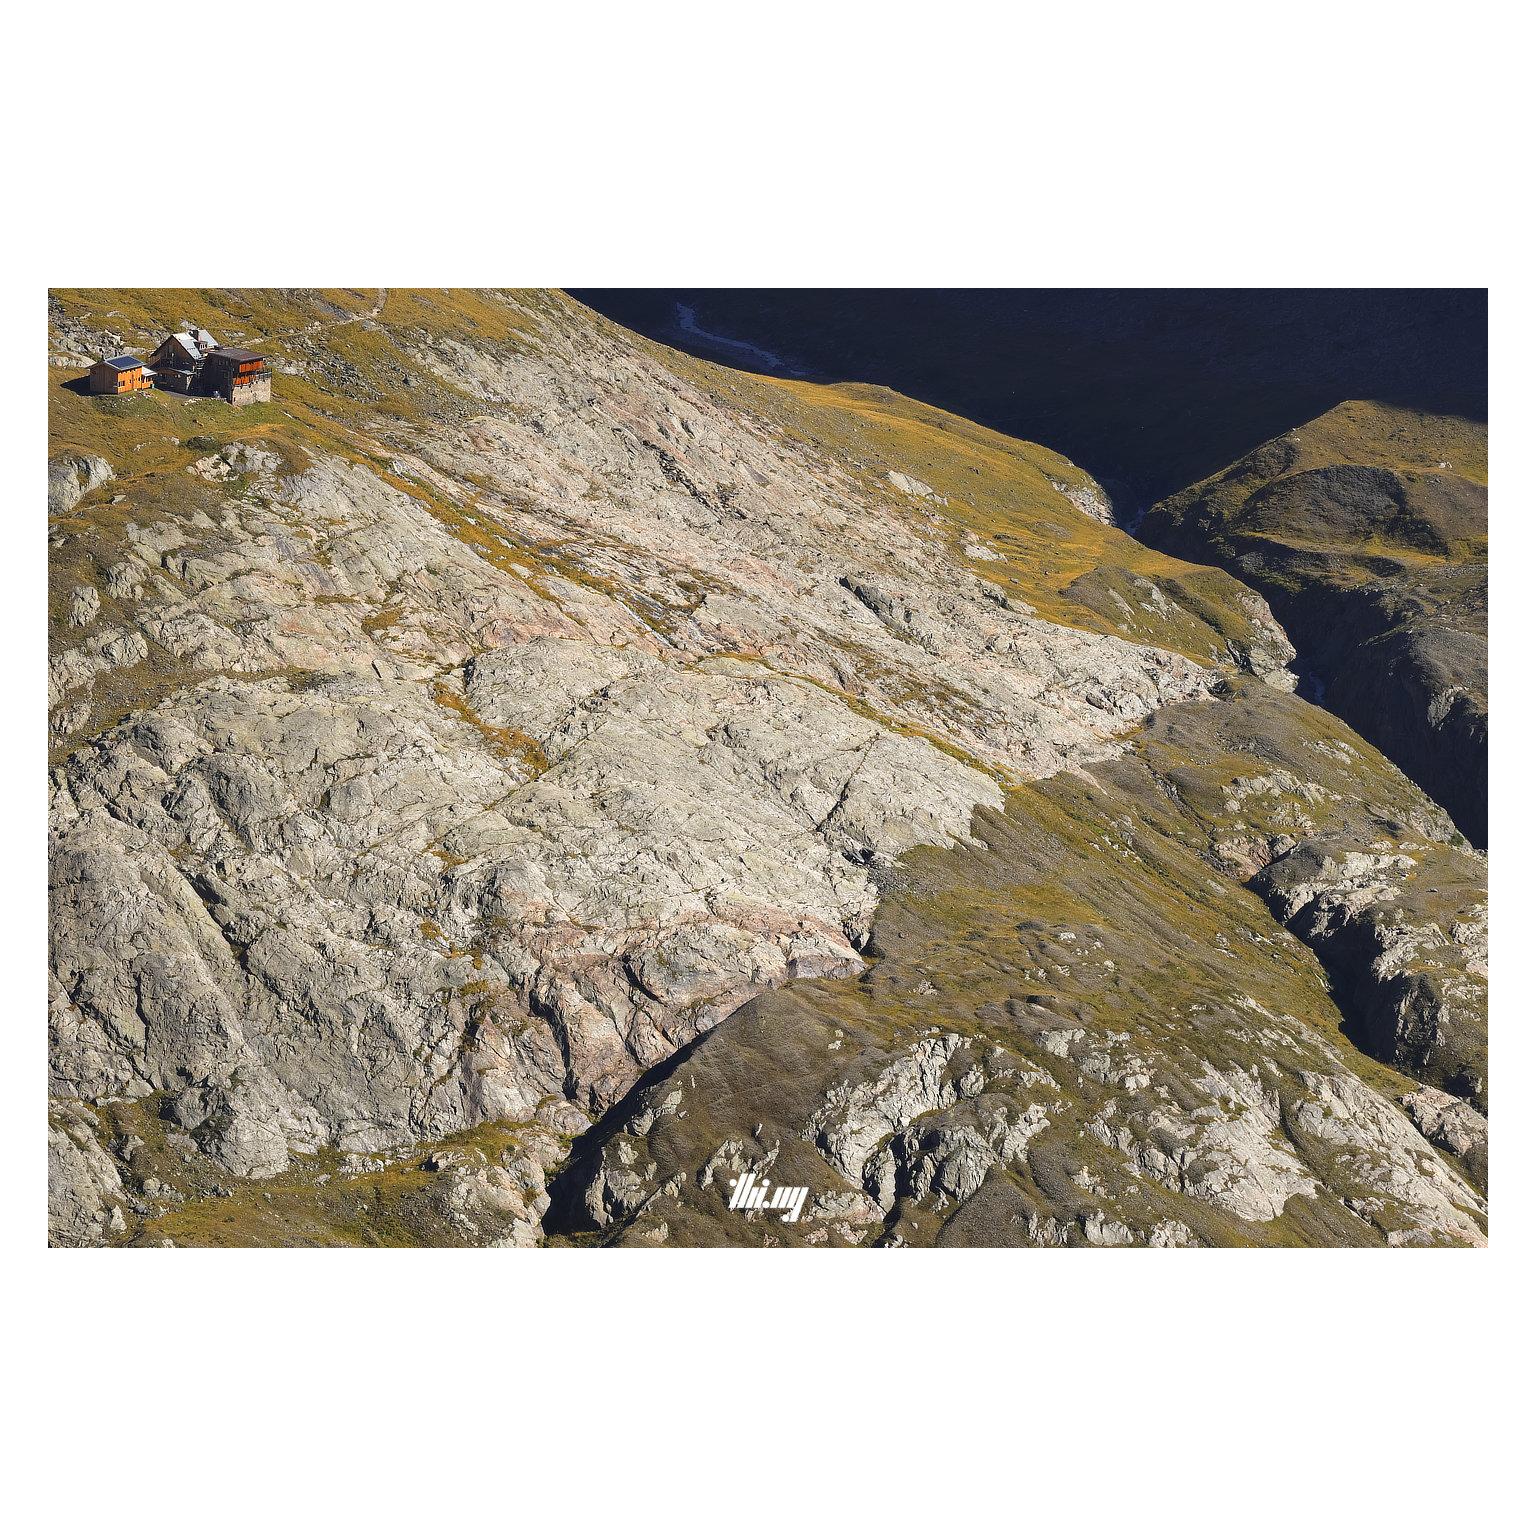
Room With Another View (2026)
(Same as [1], only here showing parts of the large drop into the glacial canyon(s) below...)
[1] #MountainMonday
 @chiraag@mastodon.online
2026-07-23 15:21:07
 @cdarwin@c.im
2026-08-15 06:59:48
Ever since Donald Trump returned to the White House, his administration has taken a sledgehammer to anti-corruption efforts,
destroying policy after policy dedicated to preventing bribery and money laundering in the country.
But this week brought the biggest blow yet:
The Treasury has obliterated a recent rule to deter devious shell companies,
handily reopening the American economy to anyone looking to hide their illicit wealth.
On Tuesday, the Department of th…

