Here's why this bothers me so much. There's already a lot of automation for patches getting backported to the numerous stable kernels. In theory those updates are focused on important or minor fixes, so distributions just pull in the latest stable release and it shows up in security updates on your machines. We _already_ have problems with problematic fixes slipping into the stable kernel series, and llm reviews are going to make it worse.
#PhanpySocial changelog ✨
🗂️ Collections (Mastodon v4.6)
🤖 Filter notifications from bots (Mastodon v4.6)
🐛 Bug fixes
🔗 https://phanpy.social/
💬
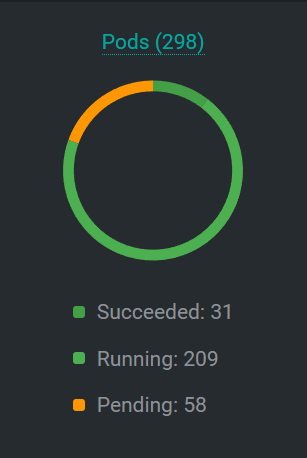
The fun side of self-hosting my GitHub Actions runners for private projects (and thus on private repos) is that I now have nearly 60 pending pods after doing some Renovate fixes and upgrades
#home-lab #Renovate
I just discovered `letterboxColor=transparent` which fixes the black background on responsive @… Stream embeds, especially for videos styled with a border radius.
I just added it to my WordPress Video Manager plugin as the default setting, which automatically sets it in the embed code when adding Stream videos to posts.
1.5 weeks into a 3 week holiday* and I can feel now just how much I needed it.
And how little I want to go back to work in August.
Let's hope the second half of the holiday fixes that.
#AcademicChatter
*yes I know, I am incredibly fortunate to get to take 3 weeks of summer holiday off, but the feeling of utter burnout is also real.
I've been coding for 20 years. I've always enjoyed it but the problem the code fixes has always been the reason I did the coding. I just want to fix problems.
Bringing up the final batch of two scope / probe demo boards.
On s/n 002, all of the power rails come up and are within range, and the supervisor flashed fine, but the FPGA doesn't show up on JTAG.
Gonna run another reflow cycle and hope that fixes it. No visually evident defects, chip isn't getting hot, and JTAG pins all have plausible resistances to ground.
The Long Game
Every episode explores the little moments that quietly change who we become, reminding us that growth isn't about quick fixes or overnight success—it's about playing the long game...
Great Australian Pods Podcast Directory: https://www.greataustralianpods.com/the-lo
And another senior citizen rant.
When you post what the update does do NOT use "bug fixes and performance improvements". How about a short update on what you really did like "fixed overflow that may cause a security issue" or "fixed spelling errors".
When I update my code it always has a short description of the change. If there is a RFC to it I include that so you can find the details, the proposed fix, test cases and test results.
We just released cve-search v6.0.1 - it is a security and maintenance release. All users are strongly encouraged to upgrade.
Thanks to @… for the remediation fix and release support. Thanks to George Chen for the report about the security vulnerability.
#cve
Competitive and Complementary Tools
David C. Krakauer
https://arxiv.org/abs/2607.18460 https://arxiv.org/pdf/2607.18460 https://arxiv.org/html/2607.18460
arXiv:2607.18460v1 Announce Type: new
Abstract: Humans have always externalized thought onto tools, from the tally and the abacus to the map and, now, large language models. I model the agent, the tool, and the task as one dynamical system in which competence (what the user retains) and reliance (what the user outsources) co-evolve, and find that the outcome is bistable. Above a critical tool availability the competent state is destroyed and competence collapses toward a low dependent floor as the user outsources completely. Lowering availability does not reverse the collapse until a far lower threshold, so history of practice rather than the current tool fixes the state. Two users with the same present access can therefore occupy opposite and lasting states, one competent and one dependent, decided only by which they built first. The collapse threshold depends jointly on the competence a user brings to a task and on the tool's transparency, the fraction of its working a user can reconstruct. In the case where an agent faces an uncertain goal, a tool can cause agency itself to transfer to the tool and the human-agent becomes an agentic-instrument, irreversibly, because the tool's model is too large to internalize. The model is tested against several independent data sets, including GPS and map use, arithmetic expertise, and language models. These results reframe how tools should be built, how artificial intelligence is deployed, and what a tool-resistant education might require.
toXiv_bot_toot
Zahlreiche Sicherheitslücken gefixt: Schnell auf iOS 26.6 und Co. aktualisieren
Apple hat nun seine Sicherheitshinweise zu den neuen Betriebssystemen publiziert. Es gibt erneut enorm viele Fixes – vermutlich auch dank KI.
🥳 Just released: Auto Encrypt¹ version 6.2.0
If at first you don’t succeed…
• Transient ACME server failures are now retried up to four times and obey the Retry-After header, falling back to exponential back-off if one isn’t provided.
• Vastly improved error handling.
• Some bug fixes.
Basically, Auto Encrypt now does its very best to provision you that certificate even when things go wrong.
Full change log:
🧩 Proposed procurement fixes: 20% of tender points for verified open-source contributions under the MEAT framework, a maintenance line item of 2-5% of contract value, and a 30-day rule for contributing non-sensitive public-contract code upstream
🌐 https://thephp.foundation/blog/2026/09
@… All Chromium versions "that are not up to date". By the time you posted this Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
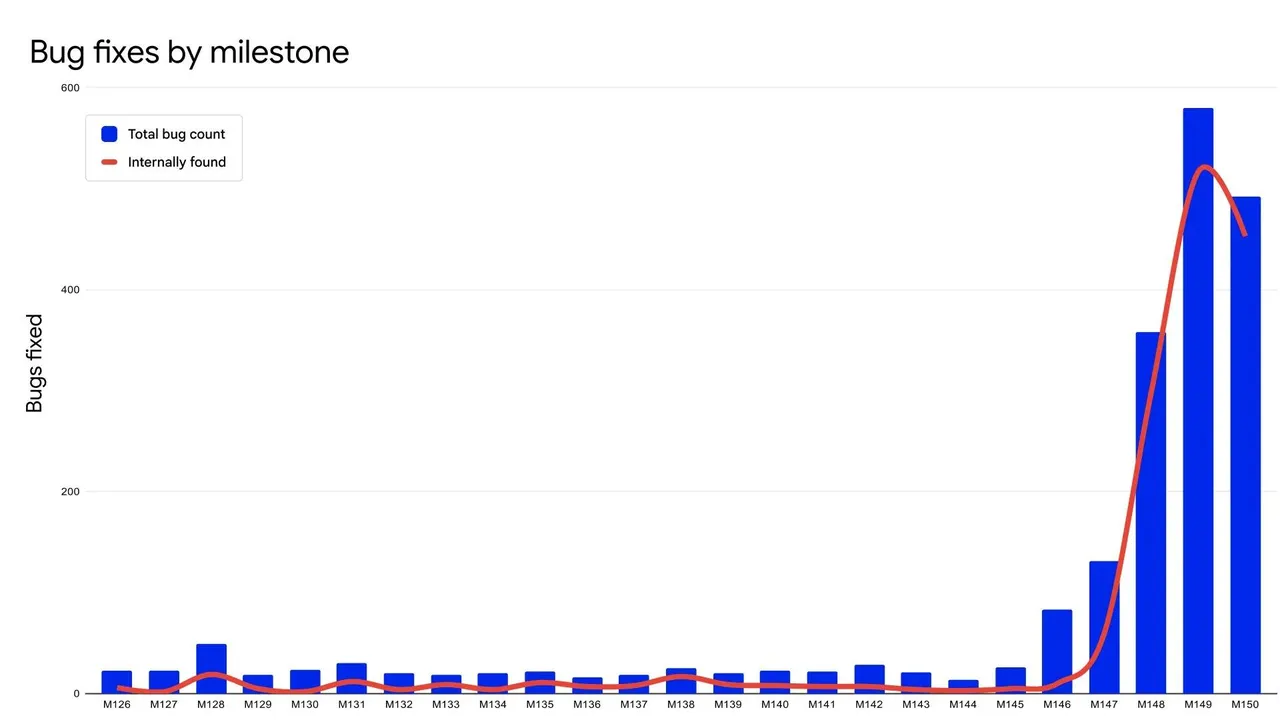
Ofcourse this story is also Google promoting it's own AI. At the same time if the numbers with regard to bug fixes by milestone are correct, something dramatic is happening with regard to AI and cybersecurity.
https://www.zdnet.com/article/google-used-
#NikonZR getting a much-needed firmware update! Already the best news of the day 👀
(Thanks to @… for making me aware!)
This week on #ProFed: security review.
I found a minor issue and took it as an opportunity to systematically check for more security issues. A few small things have been addressed already, more to follow.
The fixes also clean up the architecture in a few places – so the end result is both more secure and cleaner.
Because this fixes problems
Microsoft rolls out emergency fix for critical issues caused by its September Patch Tuesday update, which addressed ~1,000 vulnerabilities but introduced bugs (Tom Warren/The Verge)
https://www.theverge.com/news/995302/microsoft-out-of-band-windows-11-…
Security-minded #devops folks who are adding package cooldowns to your deployment rules…
…how are you possibly dealing with zero day fixes? (Short of auditing everything, which… you're lying to yourself if you truly believe that is happening, thoroughly.)
(defs:
Cooldowns: "don't update this package until the version you'd update to has been available for at least 48h”
Next time answer is no we will not treat this like a regular release when it is an emergency release. Program fixes should be treated as an emergency fix, not a full-blown production release. There is a documented process for this, but I guess it is for 'political reasons' not to go that route.
Also, I will refuse to have an emergency release done on the same day as a production/UA release. Stress levels are climbing.
My shiny new Ducati! Turns out they started off with electric components before motor vehicles.
Now, lets hope it fixes my dryer.
#Apple brings 8 new #emojis plus some security fixes. Takes 10.17 GB. Will download several hours. This leads nowhere. #Enshittification
And nobody is surprised.
Our collective sense of entitlement is getting in the way of doing the work to get things improved.
"But they should _____"
Sure but they is we.
"But nobody should go hungry"
Okay and? HOW DO WE DO THAT? Let's build it! It's not just going to happen! Government isn't a magical provider! It's us! Sometimes complaining fixes things but mostly small things.
"They should run the busses all night."
Okay so let's work the system to get it right.
Things cost money. Systems take care to build and maintain. They don't just happen. Sometimes trade-offs have to be made.
I just published a new release of Crell/Serde for PHP, v1.6.0.
Nothing drastic in this release. Mostly cleanup and bug fixing around nulls. But it does now support using an Enum as a type map, which is neat. Get it from your usual Packagist sources.
Thanks to our newest contributors for those fixes! It's great to see more people getting involved.
h…
@… Nope. All Chromium versions "that are not up to date". By the time you posted this Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
RE: https://infosec.exchange/@JessTheUnstill/117162567712283729
Once upon a time, software changes were driven by errata fixes and user desires.
Now they are driven by project manager and developer performance & bonus metrics. As enhance…
Update on the Steam Machine knock-off: like I was saying earlier, there are some sharp edges on going down your own path building your own. The latest sharp bit is resuming from sleep which I'd argue is pretty critical for any "set top box". Can you wake it up from sleep via the controller and jump back into gaming?
Right now for my build, the answer is *yes. Unfortunately, that yes has the caveat of "and when it comes back from sleep you will be presented with th…
If anyone can explain to me how Chromium/Blink decides when to use AA, I'd very much appreciate it. These are identical elements, and for some reason even changing the flex direction of the parent container "fixes" this. (enables AA for both)
(Helium 0.13.4.1 / Chromium 149.0.7827.155, macOS 15 on a low DPI screen)
Microsoft's September 2026 Patch Tuesday fixes a record ~972 vulnerabilities, bringing its total flaws patched in 2026 to 2,760, more than double from 2025 (Dan Goodin/Ars Technica)
https://arstechnica.com/security/2026/09/mic…
@… @… In fact by the time this toot was posted Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
🤖 /lfg runs the whole pipeline hands-off: plans, works, simplifies, runs code review and applies fixes, executes browser tests, commits, pushes, opens a PR and watches CI with a bounded repair loop
🧩 33 skills grouped into core loop, on-demand helpers (/ce-debug, /ce-ideate, /ce-explain, /ce-optimize), #git workflow, testing/design and collaboration
@… It is bad yes but the title "all Chromium versions" is stretching it a little. You posted this after the fix was out for all major Chromium versions. Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue when you posted.
Have all users update…
Mobilization in CTEM is the most important step: assign ownership for fixes - Irina Dimitrov (Loktionova) at #BlueTeamCon (see also: people are the hardest problem in infosec)
Radu Gheorghe and Rafał Kuć were at Berlin Buzzwords 2026 to talk about preparations for the golden set and untangling the dependencies with the title "Circular Dependency Fixes when Bootstrapping a Golden Set".
Check out the recording: #bbuzz
RE: https://techhub.social/@rayckeith/116994540671631900
This is the arc of modern tech.
The system breaks.
A human fixes it despite the system.
The system removes the human.
Repeat."
@… Probably too late. It was fixed days before this became a news item and before this toot. You probably can find users on old versions but most will be updated by now.
In fact by the time this toot was posted Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this …
Yesterday, I was one of four panelists at the annual Emmy Noether Treffen organised by the @… , talking about how we use (generative) #ai in #research.
Here's the thing: I don't.
The mood was surprisingly skeptical with none of my peers being particularly optimistic, highlighting issues with applying #llm to indigenous studies (Walther Maradiegue), dealing with fabricated bibliographies (Daria Elagina), or possibilities of quick fixes to the underlying tech (Michael Roth).
1/3
Buzz to Boom: Detecting Message Progression Vulnerabilities in Electron Applications via Segmented Directed Fuzzing
Jianjia Yu, Zhengyu Liu, Ziyang Li, Yu Sun, Yinzhi Cao
https://arxiv.org/abs/2607.20698 https://arxiv.org/pdf/2607.20698 https://arxiv.org/html/2607.20698
arXiv:2607.20698v1 Announce Type: new
Abstract: Electron is a popular framework for building cross-platform desktop applications using web technologies. Such applications consist of multiple processes with different privilege levels that communicate via message passing. When inter-process messages carry attacker-controlled inputs, they can propagate across processes and reach privileged APIs, e.g., command execution. Such a message propagation behavior is characterized as Message Progression Vulnerabilities (MPVs). The exploitation of MPVs is challenging because it often requires multiple steps, e.g., first arbitrary code execution in one process via message passing, and then command injection in another process using another message crafted in the first process. To our knowledge, existing works on Electron security only study unsafe configurations and malicious Document Object Model (DOM) content, i.e., they cannot detect or exploit these vulnerabilities that need to be triggered by complex cross-process exploits via message passing. We present Proton, a segmented directed fuzzing framework for detecting MPVs. Our key insight is to decompose end-to-end fuzzing into per-process segments along message-passing boundaries, where the goals of fuzzing each segment are either: (i) reaching a sink in the current process or (ii) propagating the payload to the next process, to enable the exploration of another process. In the second case, the messages seed the corpus of the next segment. Finally, Proton synthesizes crash inputs from each process to validate end-to-end exploits. We evaluate Proton against 589 real-world Electron applications, resulting in 23 zero-day MPVs. Among them, 22 lead to OS command execution, including projects with over 50k GitHub stars. We responsibly disclosed all findings. To date, we have received 13 acknowledgments, 11 fixes, and 11 CVEs, including a bug bounty from Vercel.
toXiv_bot_toot
🧩 For tree 4 builds a plan file fixes interfaces, file ownership and naming before fan-out, every leaf and branch gets its own gates file, and each leaf runs as a fresh subagent
📊 A controlled test measured 1.6-3.9x more effort and 4-10 self-found defects fixed before delivery; depth 6 cost only 1.0-1.5x depth 3, so the old 2^(N-1) math was dropped
RE: https://hachyderm.io/@thomasfuchs/117232685623827779
If you have no deep experience in making software (all the way from product research, to UX design to programming and solid knowledge of human-computer interaction, etc.) and in leading programmers your vibe-coded app will simply be a useless pile of garbage that will slowly rot in a repository that no one ever uses (including you) and just stink up the Internet.
If you do have that deep experience and knowledge LLM-assisted software development is just one of many tools that can be useful (it may or may not be depending on specific circumstances).
The successful uses I’ve seen first-hand are mainly for prototyping and for bug fixes/security issues; both of which require years of experience and expertise.
Me after laboriously backporting #Python 3.15 fixes to #Django 6.0.x in #Gentoo: "oh, nice, the patchset applies cleanly to 5.2.x as well."
And today, I have to laboriously backport another patch to 6.0.x, and it turns out the backport doesn't apply cleanly to 5.2.x, so I have to laboriously backport it there as well.
I honestly *hate* Django Python version support policy. Shifting all the burden downstream.
How the data center boom is exposing weaknesses in US power grids and what fixes the electricity infrastructure may need to become fit for the future (Chris Gillett/Works in Progress Magazine)
https://worksinprogress.co/issue/why-american-data-centers-cant-plug-in/…
Small update on this #mobile #nixos pixel 9 pro effort. Most of the hardware still don’t work, but I do have a full uboot->systemd boot chain which makes my life a lot simpler for iteration, no more manual fastboot flashing to try new kernel fixes. Also I put the flake on my forgejo in case anyone want to play along at home. https://code.bas.es/marcus/nixos-pixel-9pro
Split Radiance Cascades: Real-Time Global Illumination via Sparse Radiance Probes
Rouli Freeman, Alexander Sannikov
https://arxiv.org/abs/2607.20384 https://arxiv.org/pdf/2607.20384 https://arxiv.org/html/2607.20384
arXiv:2607.20384v1 Announce Type: new
Abstract: Radiance probe methods are a popular and well-tested approach for approximating diffuse global illumination for real-time graphics, but they commonly suffer from a lack of detail due to the large spacing between probes. Radiance Cascade (RC) fixes this by increasing spatial resolution and reducing angular resolution for light and occlusion from closer objects, which allows it to provide details at all scales without noise or aliasing. However, leading implementations of RC either run in 2D or screenspace, due to the prohibitive costs of storing high-detail volumetric radiance information.
In this work, we adapt Radiance Cascades for accurate real-time 3D diffuse global illumination using a sparse hashmap to store world-space probes. We introduce ray splitting, a method for calculating radiance intervals used in RC by tracing rays from visible surfaces and calculating their contribution to cascades based on their hit distance. We evaluate our algorithm, Split Radiance Cascades, on a variety of scenes, and demonstrate that it can provide high-quality indirect illumination in both single-frame and temporally accumulated contexts.
toXiv_bot_toot
PSA: If you have fruity devices, update now.
macOS/iOS 26.6 fixes hundreds of security issues.
 @Techmeme@techhub.social