Tootfinder

Opt-in global Mastodon full text search. Join the index!

@marcel@waldvogel.family
2026-08-12 16:50:32

Cool idea:
"Researchers from Tracebit on Monday said they found that placing prompt injections alongside passwords, cryptographic keys, and other secrets stored on Amazon Web Services was often all that was needed to shut down attacks from AI hacking agents. The prompts direct the attacking LLM to perform an action forbidden by its guardrails, the safety barriers AI developers erect to prevent it from taking harmful actions. The LLM responds by shutting down."

@profcarroll@federate.social
2026-09-19 14:12:04

This Flock security teardown would be comedy gold if it wasn’t so tragic. medium.com/@neonmaxima/flock-h

@fazalmajid@vivaldi.net
2026-09-10 22:10:42

@… @… it does not include passwords shared with you in the export, however. Still, that's a massive improvement over Keychain Access.

@seav@en.osm.town
2026-10-09 01:57:42

@… has disclosed a few now-fixed security issues related to the backend of @….
“TL;DR: #MapRoulette had several security vulne…

@shriramk@mastodon.social
2026-07-29 13:48:46

I would really like passkey advocates to lay out in full how one helps elderly parents once they switch to passkeys. (Can be done; not trivial. This article rambles about YubiKeys—like typical customers need one—while entirely missing this disadvantage.)
nytimes.com/wirecutter/reviews

@Techmeme@techhub.social
2026-07-16 13:20:43

1Password launches a new Claude integration for Mac that lets Anthropic's AI agent sign in to websites without seeing the user's password or 2FA code (Zac Hall/9to5Mac)
9to5mac.com/2026/07/16/1passwo

@fazalmajid@vivaldi.net
2026-09-10 22:22:30

@… @… I'm guessing its a policy decision that you don't own shared passwords by definition (unless you are the one sharing them). Certainly in Enterprise situations where password managers are used to share team secrets and c…

@frankel@mastodon.top
2026-10-04 09:18:42

Where Sensitive Data Hides in #OpenTelemetry Pipelines, and How to Find It
ollygarden.com/resources/blog/

@datascience@genomic.social
2026-09-20 10:00:01

BFG Repo-Cleaner is a simpler, faster alternative to git-filter-branch for removing large files, passwords and other private data from Git history: #git

@Erikmitk@mastodon.gamedev.place
2026-10-04 18:41:10

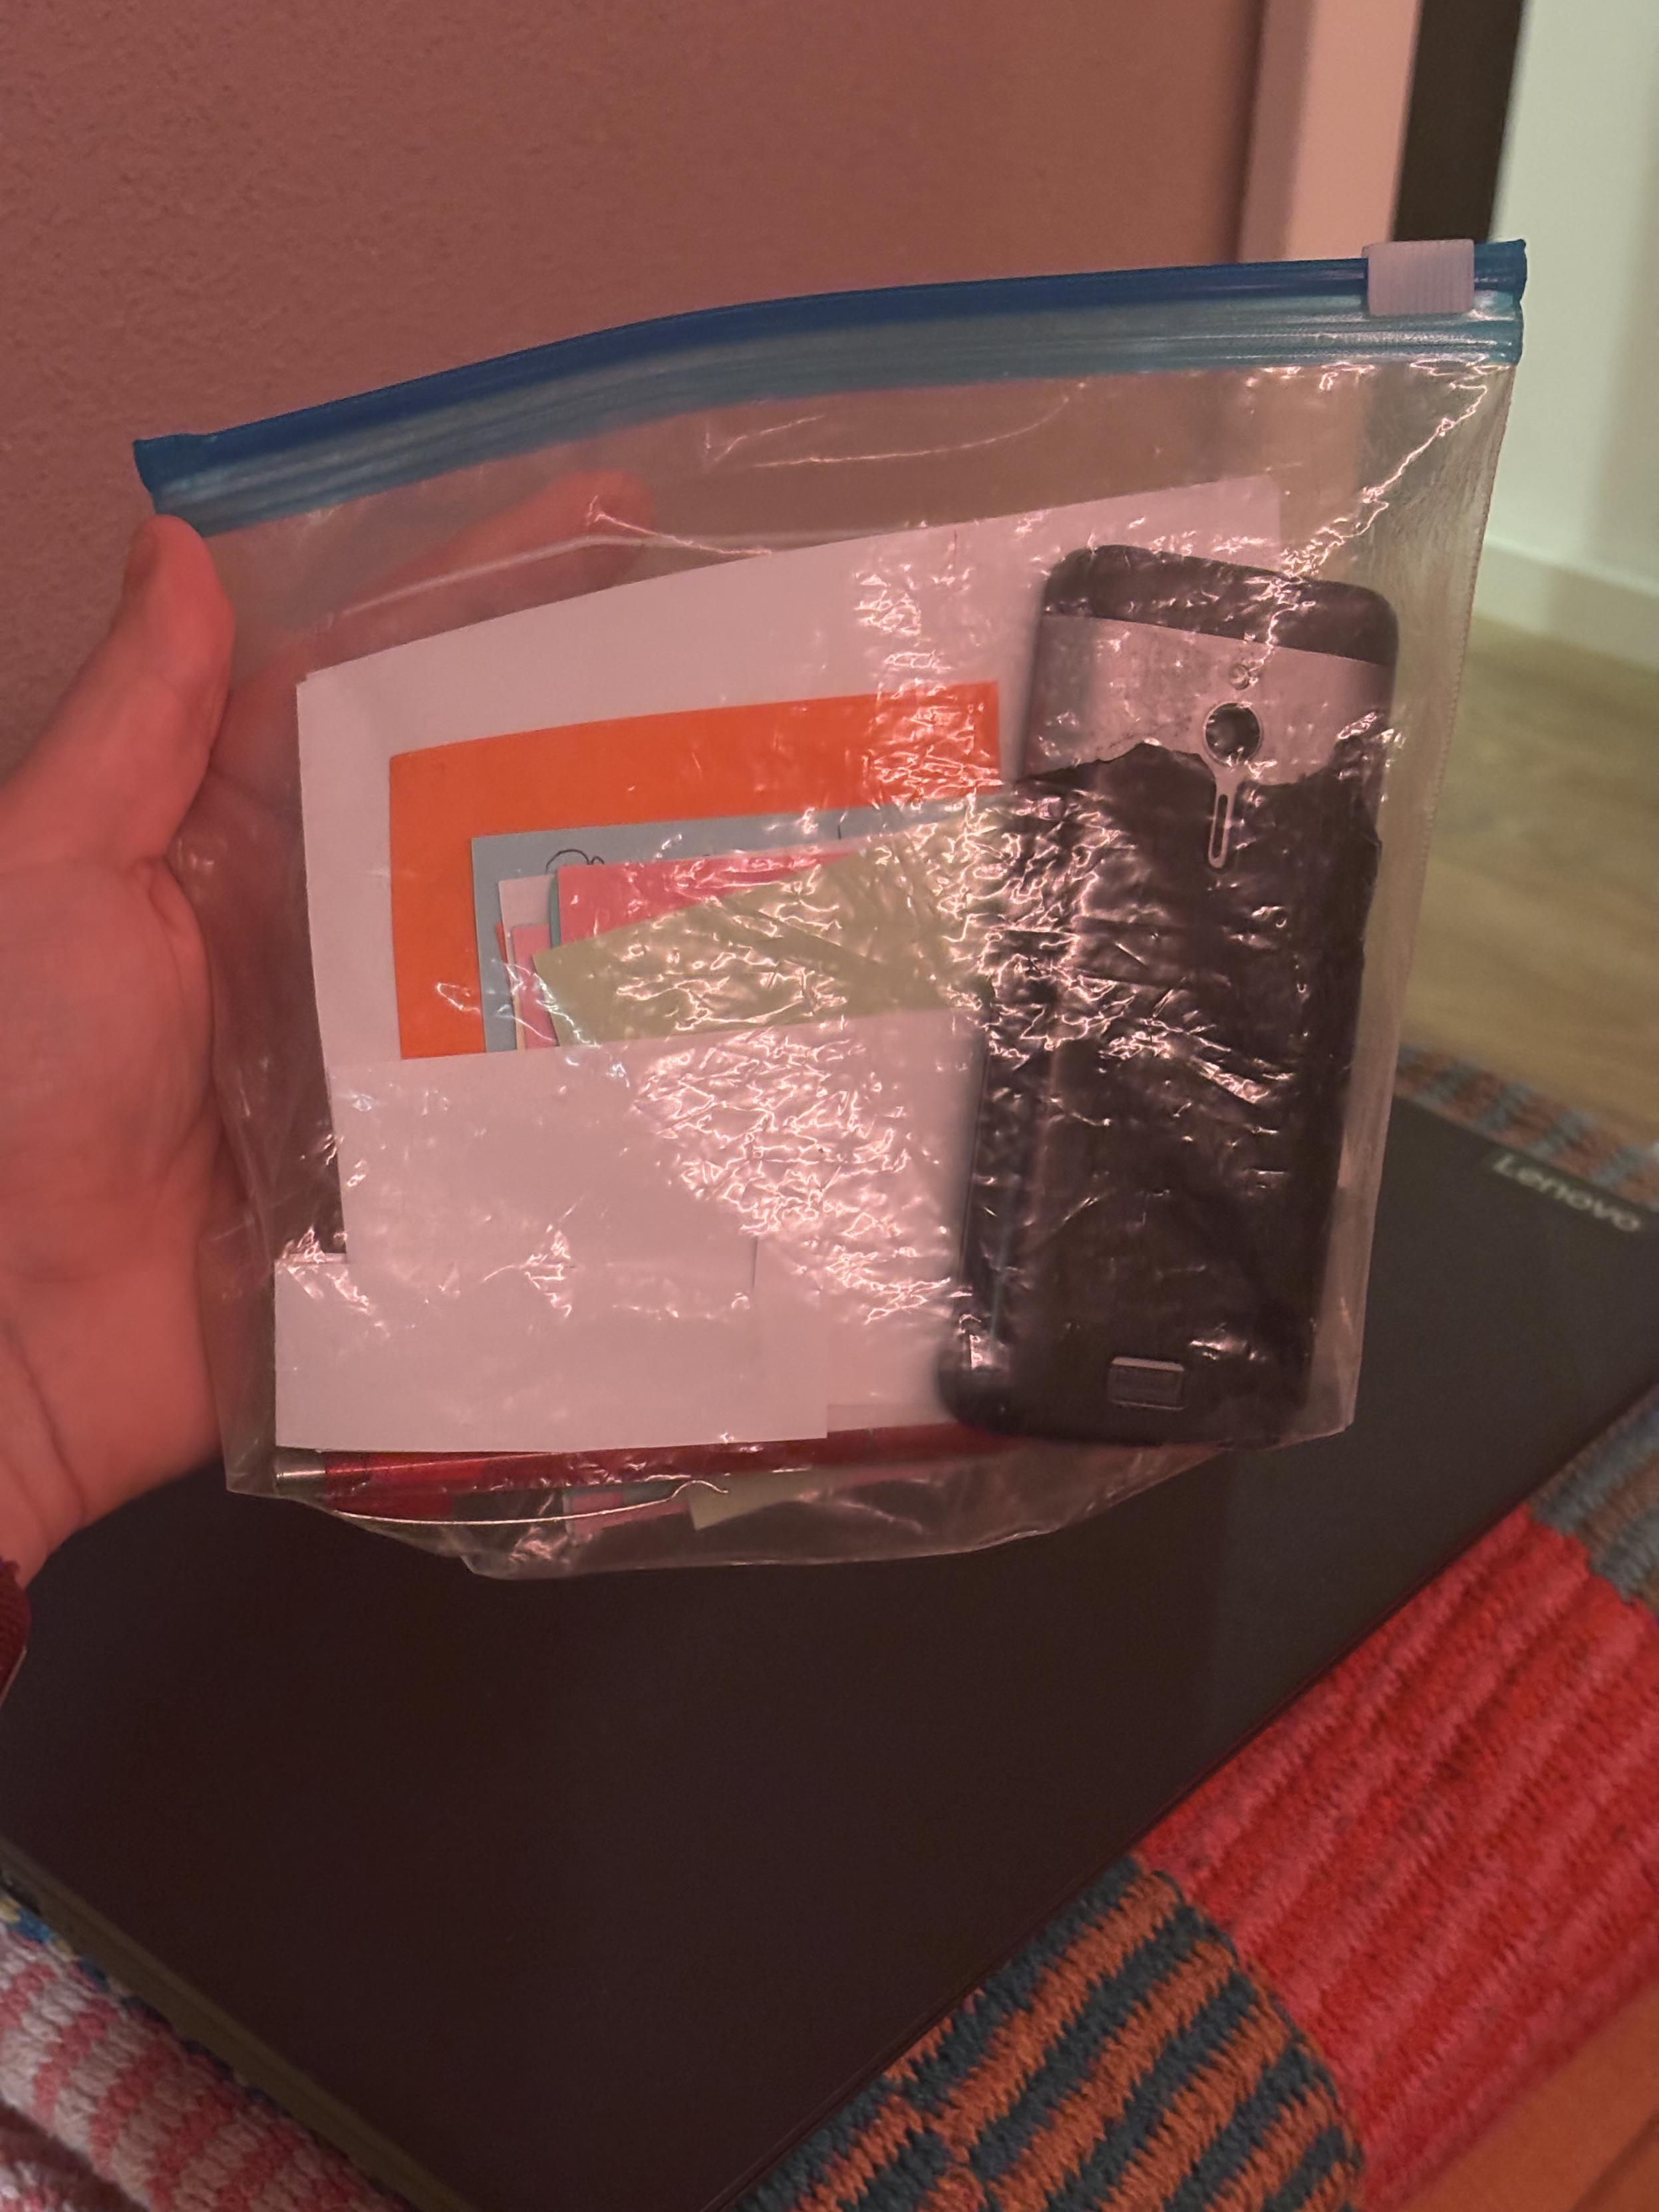
I’m doing tech support for my mother-in-law because Google thinks she’s a bot and keeps closing up her gmail account.
She handed me her ziplock bag of passwords and her old phone for 2FA.

a ziplock bag full of paper and an old
mobile phone
Fix This Jimmy Fallon GIF by The Tonight Show Starring Jimmy Fallon
@iam_jfnklstrm@social.linux.pizza
2026-09-21 14:25:51

What does unintentionally mean here "Google's Gemini AI model unintentionally hacked three companies by guessing passwords during a security test with Israeli startup Irregular."
Can I as a human unintentionally guess passwords? I thought it was called brute force attacks and therefore intentional #ai

@andres4ny@social.ridetrans.it
2026-07-27 19:11:23

It's so wild to me that people have professionals install their WiFi and just never get the passwords for their routers. Like, I get the whole "I just want to pay for an appliance and never think about it" thing, but by definition it's locked down and so you can't have someone ELSE fix it.

Numerous health systems across the country have issued alerts,
warning patients to ignore scam messages that are attempting to phish passwords from patients,
allowing hackers to gain access to Epic Systems’ MyChart patient portal.
The effort appears to be coordinated by a single cybercriminal or a group,
as more than a dozen facilities have issued similar warnings after receiving reports of emails that offer patients a chance to claim
a “reward,” in the form of …

@simon_brooke@mastodon.scot
2026-08-22 14:09:46

I've been dusting off my #ScottishIndependence canvassing app, to see how hard it would be to get it working if a new #IndyRef did actually happen.
It's suffered much less bit rot than I thought. It's mostly ready to go, there are still some issues to fix.

The YouYesYet app welcome page. A blue screen with a big 'Project Hope' logo in the centre, 'You yes yet?' at the top, and 'Yes' and 'No' buttons on the right.
The login screen. A blue screen with 'Please log in' at the top, and buttons for oauth providers at the right.

Below is a login form with conventional username and password boxes, but that's intended to be temporary. The idea is not to store people's passwords for security reasons, but to use well known oauth verification services; but for testing there is a login system.
The map screen. A blue screen showing a map with flags where the homes of electors we want to canvas are.
The database entity relationship diagram
@qbi@freie-re.de
2026-07-16 10:09:24

Website: Please register for an account
qbi: OK, Username: foo and Passwort: "EEbkVt3nAqdUsgtuUgbX5wjW".
Webseite: "Passwords must have at least one non letter or digit character."
qbi: 🤔

@kubikpixel@chaos.social
2026-09-15 06:40:02

«Mass Scanning Targets Exposed Vite Servers to Steal AWS Keys and Azure Tokens:
[…] Honeynet telemetry recorded 807 session-grouped attacks and approximately 32,000 raw events during the monthly analysis period. […]»
It is becoming more and more that passwords / passkeys are not stolen or hacked, are their generated tokens. Many of them, in my opinion, say too much about the users and their use.
🧑‍💻

@pre@boing.world
2026-09-09 17:40:31

So the wave of spam-registrations I figured wouldn't really affect us here on the tiny server with registrations closed and clear instructions that only users who know us personally are welcome and we will check.
Turns out no. Our server has run out of email credits from sending lots of email-validation messages.
Hope everyone remembers their passwords, coz password-reset emails and notification emails and whatnot won't be going out for a little while.
All .jp addresses and about half of them bounced as not real email anyway.
Started 10am yesterday, not an hour gone by without some since.
Nothing even clicking those activation links I don't think, certainly nothing filling in the "So who do you know then?" form to create an account.
With email notifications not working, replies to moderation actions could be slower. Not that there's ever much really.
I've turned registration off entirely. Probably should be that way anyhow really here. If you want an account, ask someone who has one personally.
#spam #mastodon

@ddrake@mathstodon.xyz
2026-07-21 13:52:34

Man, the ACM website -- the Association for Computing Machinery's site -- is so confusing with all the usernames and accounts.
I am trying to subscribe to one of their mailing lists and it's asking me for an email address and a password. As an ACM member, I have an @acm.org email; my account also knows about my Macalester email, and my newer St. Olaf email. I have tried all of those, and all the various passwords in my password manager. None work.
If only, somehow, someo…

@Life_is@no-pony.farm
2026-08-18 12:42:17

@…
Out of curiosity i asked a password app, if "123456" has been breached, and its answer was 210.410.000 times.
I understand, that there are 210.410.000 sites, that have been breached and that allow passwords, that only consist of numbers and that are only 6 bytes long.
However most sites only allow passwords that are s…

@life_is@no-pony.farm
2026-08-18 12:42:17

@…
Out of curiosity i asked a password app, if "123456" has been breached, and its answer was 210.410.000 times.
I understand, that there are 210.410.000 sites, that have been breached and that allow passwords, that only consist of numbers and that are only 6 bytes long.
However most sites only allow passwords that are s…

@probablyjohnfunk@social.linux.pizza
2026-07-16 16:17:31

Multiple high profile website breaches over the years mean cybercriminals already have your personal data, including things as sensitive as passwords and Social Security numbers. It's too late to hide from them, but you can be prepared for them.
cybersecuritysimplified.subst…

@teledyn@mstdn.ca
2026-10-05 21:05:46

I'm downgrading quantum computing as a threat due to instantly cracking passwords. Quantum computing will hypercharge the graph data operations that support the LLMs to spew slop at breathtaking speeds.

@Hans5958@mastodon.social
2026-08-15 17:01:43

Hello from August. Let's get going: passwords.
I'm not sure why they have to remove passwords, or maybe that's just me hating magic links.
There's the weird change when someday... passwords are not a thing in Trakt. I don't know why or what they are thinking, but it's just gone, replaced with a "check your e-mail for the OTP" prompt.
#Trakt

@thomasfuchs@hachyderm.io
2026-09-02 14:55:42

Wrt to the 1Password fiasco: if you’re using Apple stuff, Apple’s password manager works great across many apps. Unless you have very specific needs (like managing passwords for employees) you probably don’t need a paid-for password manager.
(It also works on Windows if you have e.g. a gaming PC!)
⚠️ How to use this post:
1. This isn’t an invite to rant about Apple
2. Yes, I know it doesn’t work on Linux
3. Do not recommend other ethically indefensible software

@hanno@mastodon.social
2026-09-01 12:15:48

Not sure what to make of this, but:
I've been getting "Your temporary ChatGPT login code" mails from ChatGPT that I haven't triggered. They also say: "If you were not trying to log in to ChatGPT, please reset your password." Which makes me believe: triggering these mails should only be possible with my password. I use random passwords unique for each service. I'm reasonably confident my password is not compromised.

@bici@mastodon.social
2026-09-25 03:03:36

Artificial intelligence researchers are warning the public to use strong passwords and promptly install software updates on their devices to combat "AI-driven computer worms," a new breed of cyber-threat they say can launch custom attacks on devices, sapping processing power and information as they hunt for new victims.

@metacurity@infosec.exchange
2026-08-26 13:42:25

You won't want to miss today's Metacurity for the most critical infosec developments you should know, including
--OpenAI disrupted an elaborate Russian influence operation,
--Cyberattack disrupts Boston Scientific worldwide,
--Man accused of impersonating NSA hacking chief,
--Hackers steal confidential Nutex data,
--LACMA breach exposed sensitive personal data,
--Akira-linked attack hits benefits provider Paylogix,
--CISA red team exposes tale of two defenses,
--CISA pushes agencies to strengthen security logging,
--Hackers turn npm mirrors into phishing hosts,
--New loader delivers Amatera through fake CAPTCHAs,
--AI malware remains mostly stuck in the lab,
--Army moves cloud management under Cyber Command,
--WhatsApp strengthens 2FA and passkey security,
--ChatGPT Work can now handle authenticated tasks,
--Parking service breach exposes 73,000 payment cards,
--Hackers hijack Kylie Jenner’s X account for crypto scam,
--AI security startup Alice raises $140 million,
--Meta settles child-addiction claims for up to $17.1 billion,
--No, hackers didn’t steal a gazillion passwords,
--ICE seeks access to nationwide voter data
metacurity.com/openai-disrupte

@hacksilon@infosec.exchange
2026-08-19 17:02:26

PSA: Critical unauthenticated account takeover vulnerability in #Keycloak - allows resetting arbitrary users‘ passwords. Update to 26.7.2 immediately or disable password reset. Tracked as CVE-2026-18963. #infosec

@metacurity@infosec.exchange
2026-09-18 13:33:21

Humanity has continued to survive, so before you leave for the weekend, check out today's Metacurity for the most critical infosec developments you should know, including
--Three guys used Claude and Codex to hack into OpenAI,
--White House weighs government-backed cyber foundry,
--Israeli firm trained Angola in online influence operations,
--University rescinds job offer over wiped phone case,
--North Korean recruiter scams infected 30k devices,
--Cyberattack targeted Armenia’s election system,
--Hijacked torrent repository spreads movie malware,
--Fake LastPass downloads steal passwords and crypto,
--Critical Check Point flaw enables root access,
--CrowdSec discloses private source code leak,
--CISA launches upgraded vulnerability disclosure platform,
--AI monitoring startup Raindrop raises $35m,
--TigerByte emerges with $3m and $7m in contracts,
--France probes pervy smart glasses,
--Flock’s fake police department searched real drivers,
--Free Chinese AI models supercharge hacking
metacurity.com/three-guys-used

@Hans5958@mastodon.social
2026-08-15 17:01:44

The thing is that I kind of hate checking my e-mail to log in. It took quite some time to load on my browser, and I don't really like auto-sync on my phone to save battery (maybe people take this for granted...). E-mails are supposed to be an emergency option (e.g., resetting passwords, recovering accounts), but I guess this is the new normal?
#Trakt