Francisco Partners plans to take patient engagement software company Weave Communications private for ~$650M; Weave went public at a ~$1.5B valuation in 2021 (Brock E.W. Turner/Axios)
https://www.axios.com/pro/health-tech-deals/2026/08/18/f…
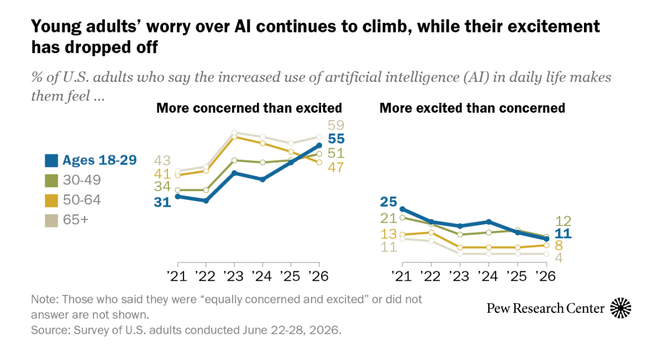
Survey: 52% of Americans say they are more concerned than excited about increased AI use in daily life, up from 37% in 2021, including 55% of those under 30 (Pew Research Center)
https://www.pewresearch.org/short-reads/20
Five years after the Taliban took power, an increasing number of countries are renewing ties or scaling up diplomatic contacts with the hardline Islamists, who seized power in Kabul in 2021 after 20 years of brutal insurgent warfare.
Campaigners fear that the individual contacts by different countries risk undermining “coherent, consistent” demands for an improvement in human rights in return for any diplomatic concessions.
The United Nations described a recent “cascade of [Talib…
from my link log —
GhostCell: separating permissions from data in Rust.
http://plv.mpi-sws.org/rustbelt/ghostcell/
saved 2021-05-23 https://
Mariensprung (2021)
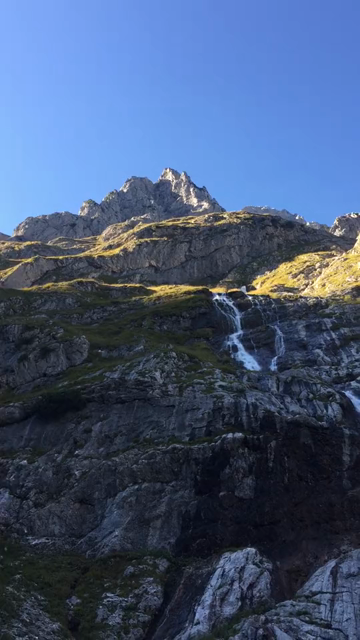
A 160 meter tall waterfall emerging straight out of the rock below the Waxenstein, and a tributary to the Hammersbach in the Höllental (Hell's Valley).
#WaterfallWednesday #Video #POV
from my link log —
An incomplete list of mistakes in the design of CSS.
https://wiki.csswg.org/ideas/mistakes
saved 2021-01-24 https://dotat.at/:/…
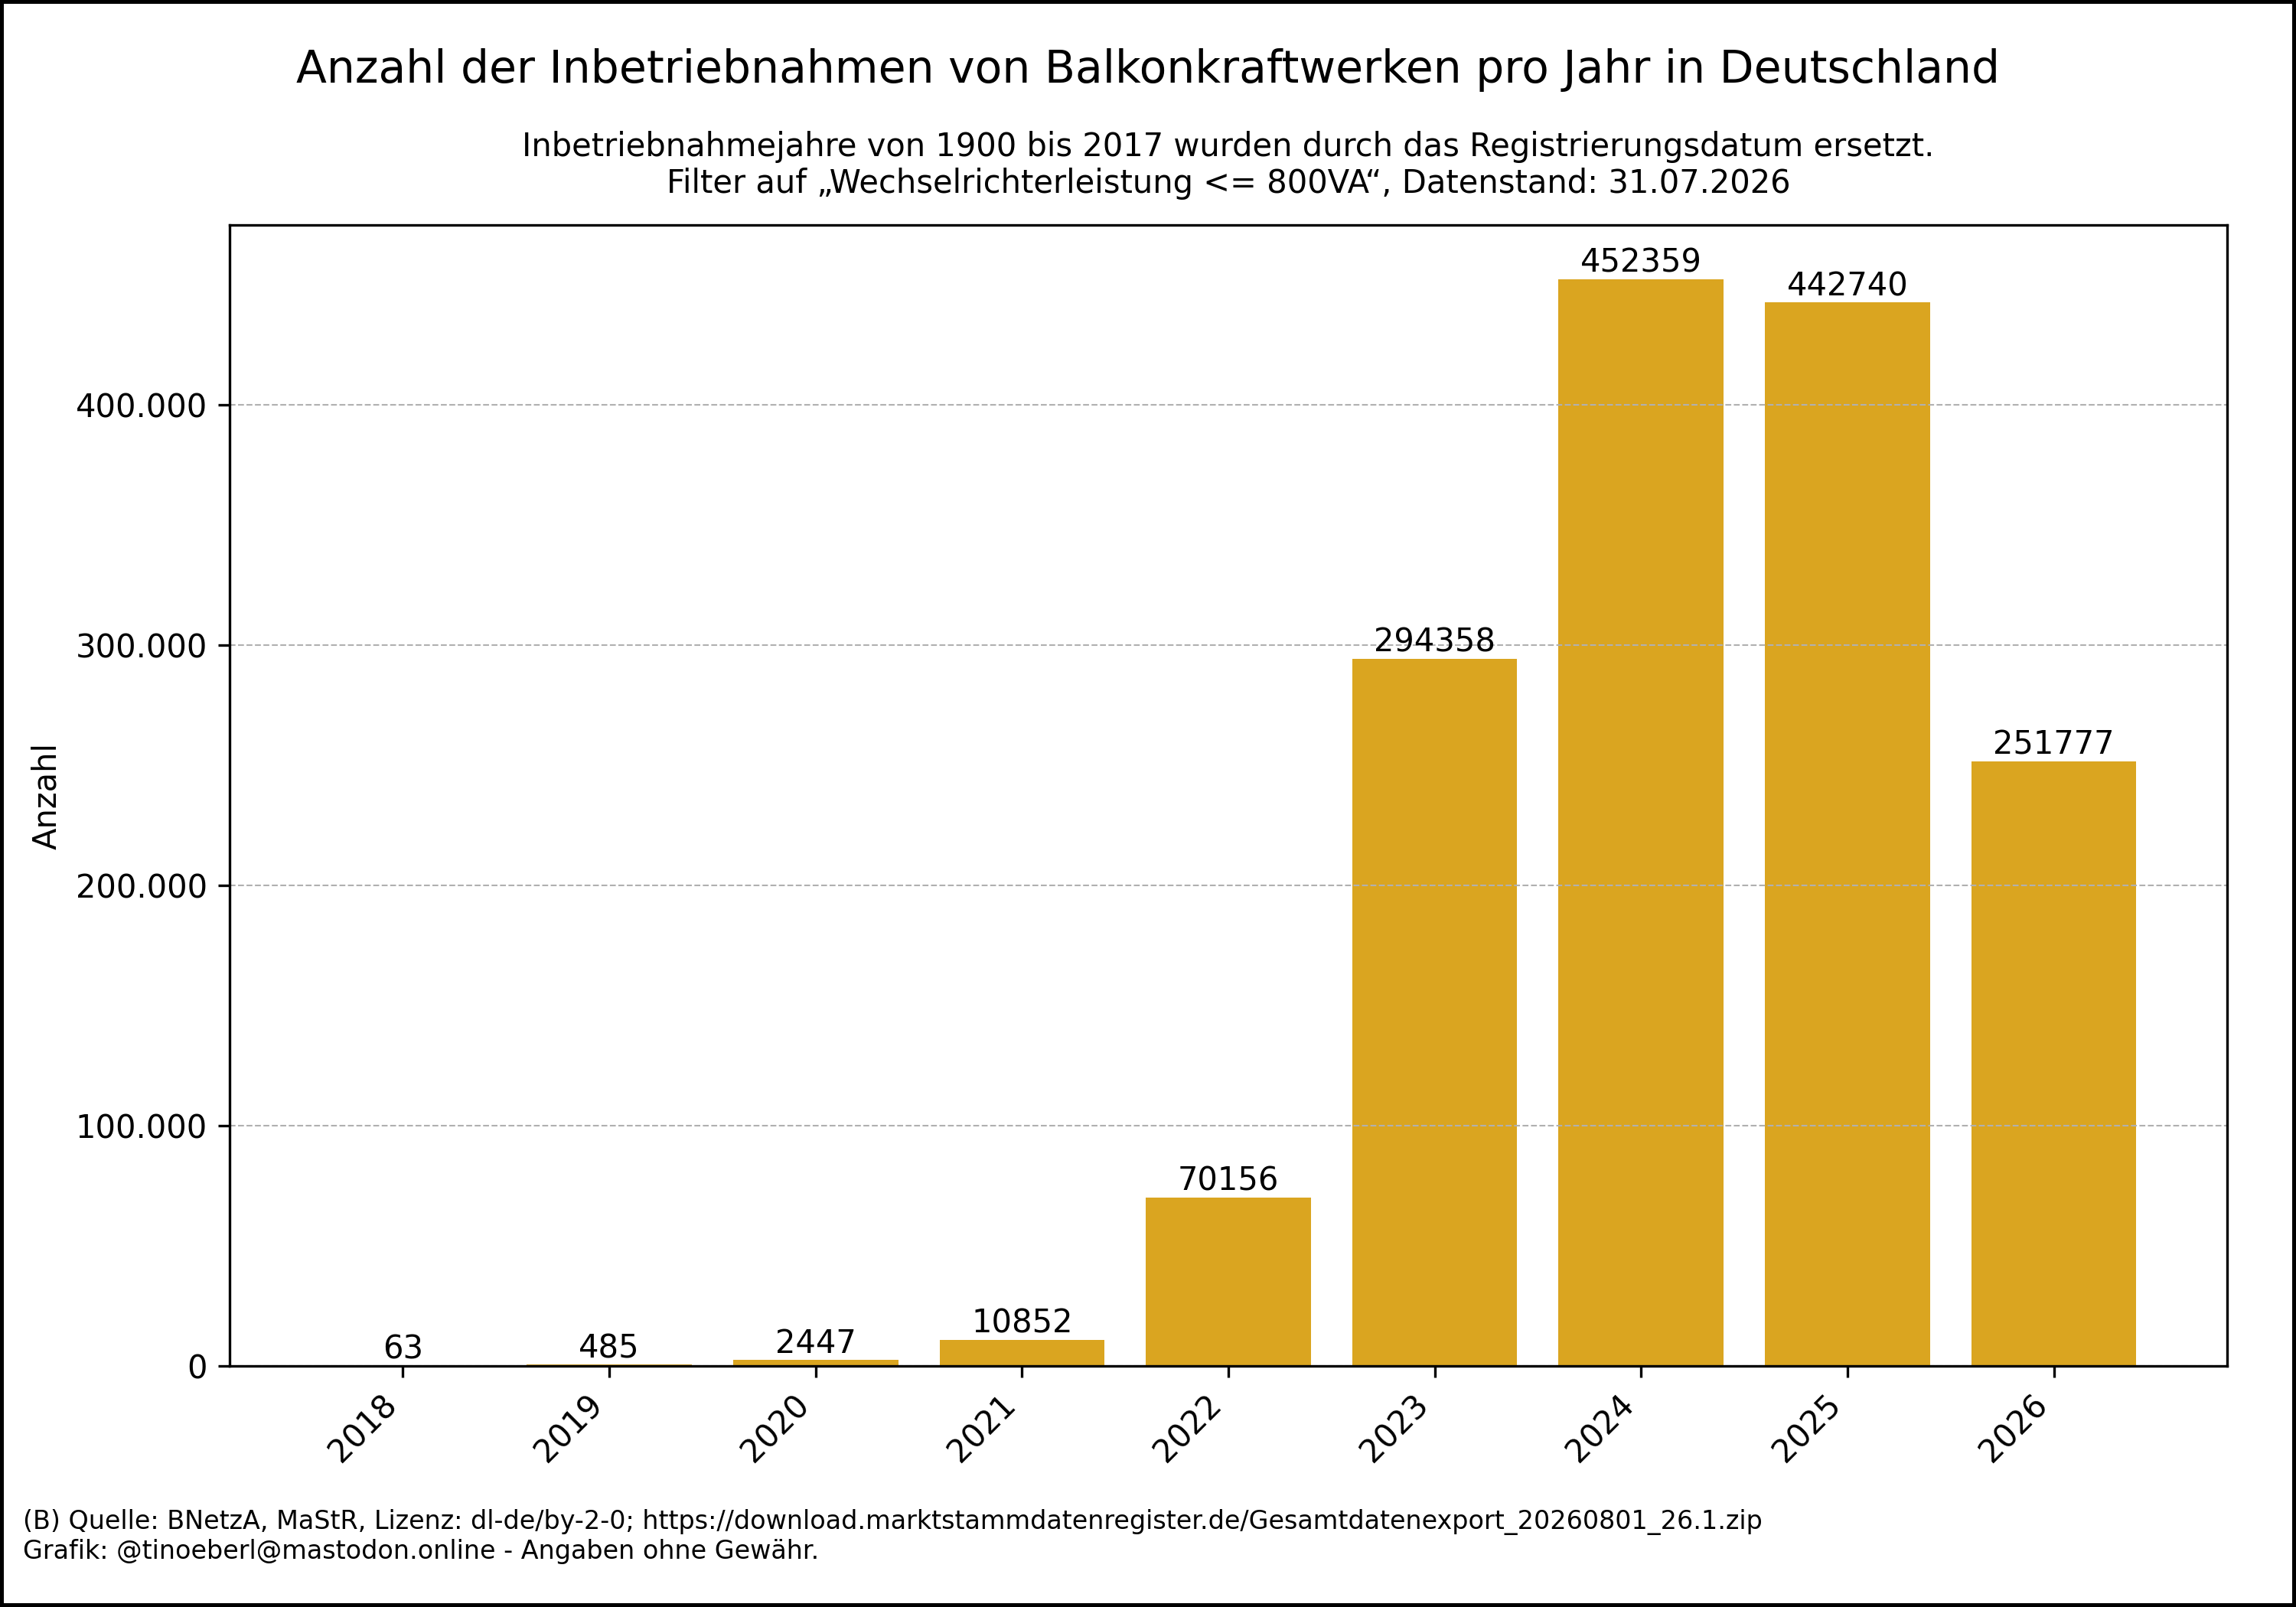
Anzahl der Inbetriebnahmen von Balkonkraftwerken pro Jahr in #Deutschland mit Stand vom 31.07.2026.
Unplausible Inbetriebnahmedaten von 1900 bis 2017 wurden durch das Registrierungsdatum der #Steckersolaranlage ersetzt.
👉 Zusatzlesestoff:
Netflix is closing game studios Night School Studio, which it acquired in 2021, and Moonloot, and is also cutting jobs from its internal games team (Stephen Totilo/Game File)
https://www.gamefile.news/p/netflix-closes-night-school-moonloot
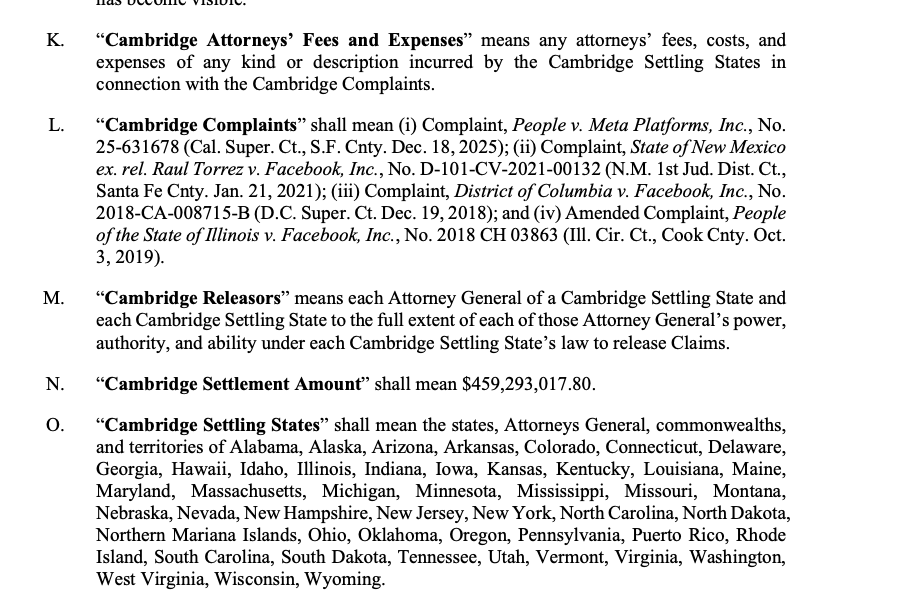
The Mega Meta settlement bundles the outstanding Cambridge Analytica lawsuits as well.
Bank accounts held by President Donald Trump were closed by Capital One in 2021
-- after it flagged financial activity that had characteristics of money laundering, the bank disclosed in a court filing over the weekend.
The court filing is tied to a lawsuit filed against Capital One by one of Trump’s financial holding companies shortly after he was sworn into office a second time.
Trump alleges that Capital One illegally closed his accounts for political reasons, following …
cofe: Collaboration in Financial Economics (2021)
Network of authors and commenters of papers in finantial economics, obtained from the acknowledgement sections of over 5,000 published research papers.
This network has 13967 nodes and 102039 edges.
Tags: Social, Directed, Weighted, Online, Collaboration
https://networks.ske…
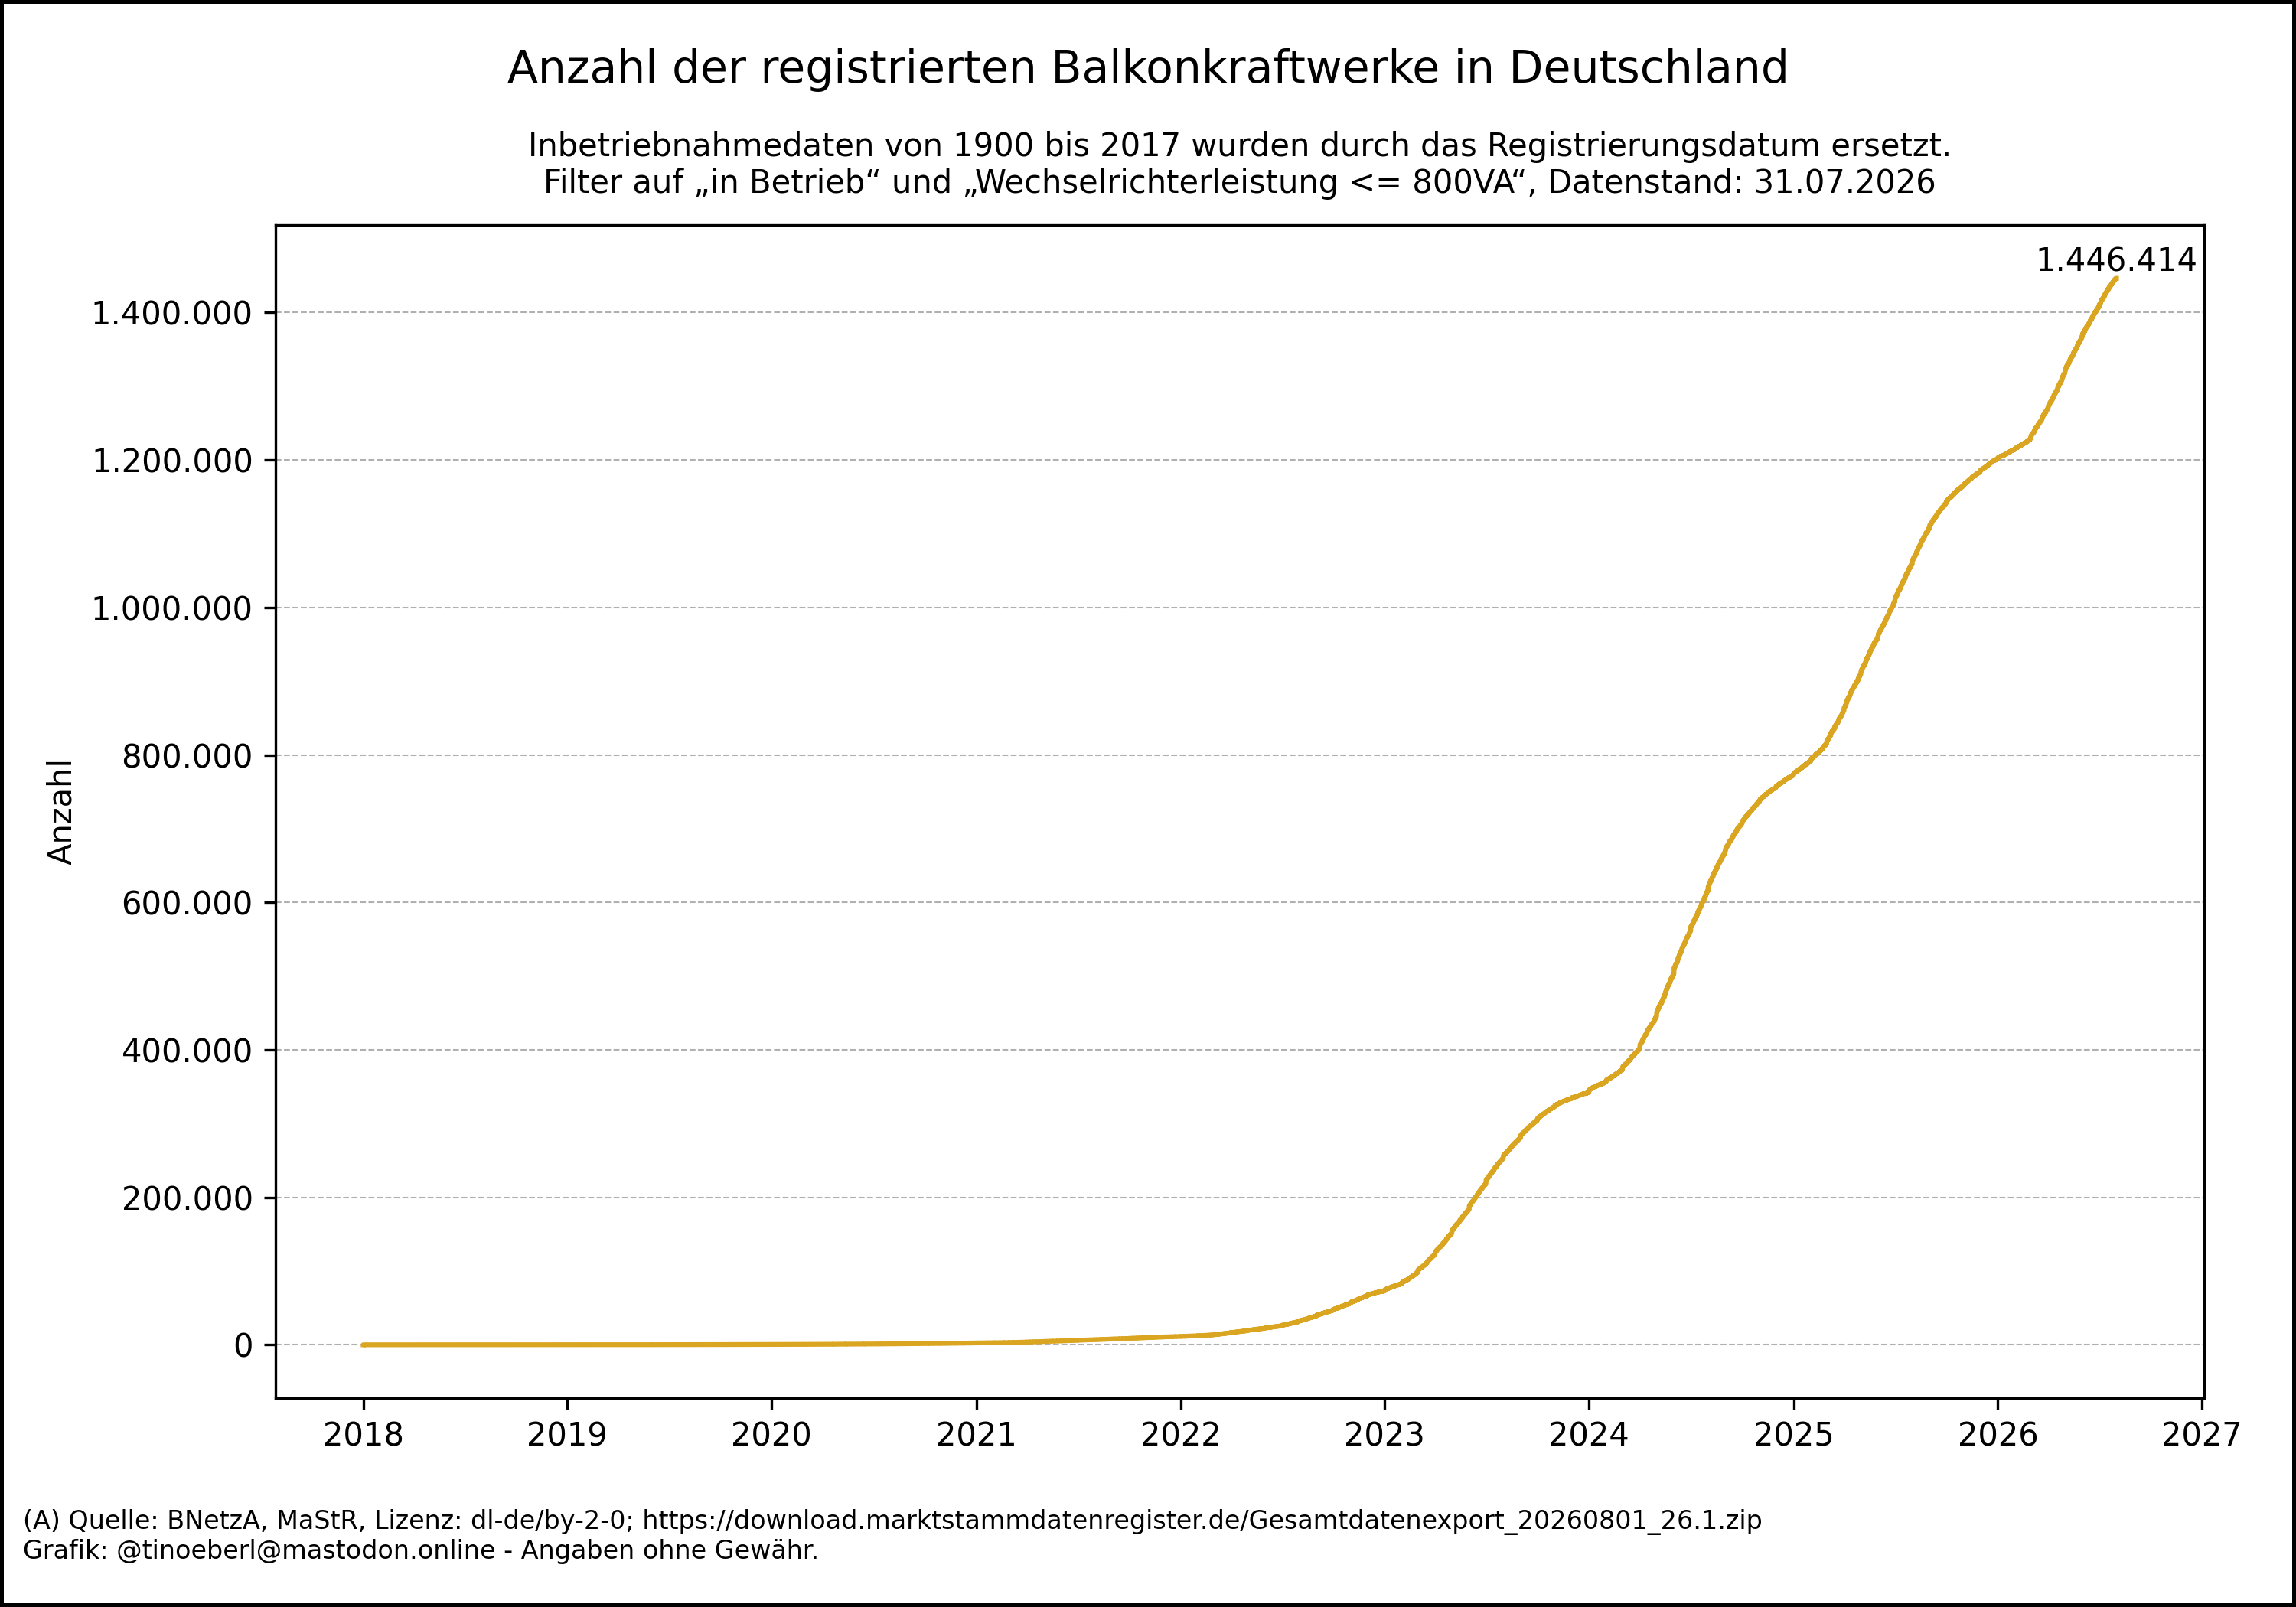
Anzahl der registrierten #Balkonkraftwerke in #Deutschland mit Stand vom 31.07.2026.
Der aktuelle Höchststand liegt bei 1446414 registrierten Anlagen.
Unplausible Inbetriebnahmedaten von 1900 bis 2017 wurden durch das Registrierungsdatum der
Capital One bank has asked a federal judge to dismiss a lawsuit from the Trump Organization over the closure of hundreds of bank accounts back in 2021,
arguing in new papers that the shutdowns were the product of a monthslong anti-money-laundering review
— not retaliation for the Jan. 6 Capitol riot, as the Trump family businesses have claimed.
In a motion to dismiss the case filed Friday in a Florida federal court,
Capital One's lawyers wrote that the bank's …
Themis Consensus Extension v1: MEV Mitigation by Randomized Delayed Execution and Intent-Hiding Transactions in Application-Specific Blockchains
Shoeb Siddiqui, Mateusz Nowakowski, Stanislav Vozarik, Gleb Urvanov, Peter Kris
https://arxiv.org/abs/2607.21406 https://arxiv.org/pdf/2607.21406 https://arxiv.org/html/2607.21406
arXiv:2607.21406v1 Announce Type: new
Abstract: Maximal extractable value (MEV) arises when privileged participants select, exclude, insert, or reorder pending transactions for private gain. We specify and analyze the Themis Consensus Extension v1, first published by Mangata in 2021. The design separates value extraction by reordering (VER) from value extraction by denial (VED). For VER, block construction and execution occur across consecutive producers: one producer commits a transaction set, and the next derives a publicly verifiable, deterministic, previously un- predictable seed and executes a seed-determined, dependency-preserving permutation. For selective VED, a user may encrypt a transaction for a designated builder and executor. The builder removes an outer layer and commits the opaque inner ciphertext; the executor reveals and executes the plaintext only after commitment. Under selfish but non-colluding validators, an adversary below the underlying consensus fault threshold, secure cryptography, and accountable role performance, the construction limits unilateral post-commit ordering control and hides transaction intent from relays and the builder. It does not provide send-order or receive-order fairness, complete censorship resistance, resistance to builder-executor collusion, or per-transaction price guarantees. We analyze probabilistic extraction, spam, dependent transactions, decryption liveness, session boundaries, total denial, and threshold coalitions. We also document the initial Aura-based Substrate implementation and its subsequent transition to a BABE-based sr25519/VRF seed path, together with delayed execution, Fisher-Yates shuffling, and Xoshiro256 . The result preserves the original proposal while narrowing its claims to explicit assumptions.
toXiv_bot_toot
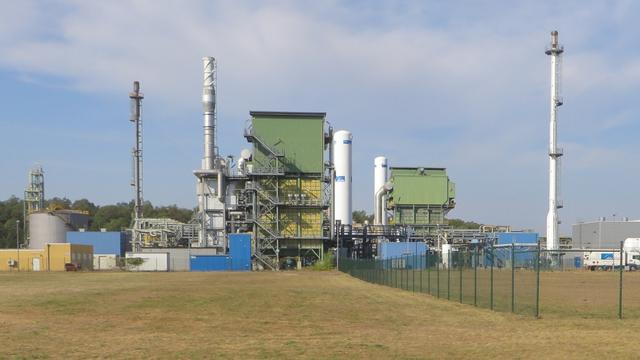
Sicherheitsbedenken, umfangreiche Umbauten und ein Unfall Ende 2025 haben Lindes Produktion von grünem #Wasserstoff im Chemiepark #Leuna um Jahre verzögert.
Der 2021 angekündigte PEM-Elektrolyseur sollte bereits 2022 starten und jährlich rund 3.200 Tonnen Wasserstoff produzieren. Bund und Sa…
Security Vulnerability Patterns in AI-Generated Code: A Cross-Model Comparative Study
Shanna M. Kahn, John D. Hastings
https://arxiv.org/abs/2607.20713 https://arxiv.org/pdf/2607.20713 https://arxiv.org/html/2607.20713
arXiv:2607.20713v1 Announce Type: new
Abstract: LLM-based coding tools enable non-expert users to generate routine automation scripts that may enter enterprise workflows without meaningful security review. This study examines that risk directly. Code was collected from ChatGPT, Microsoft Copilot, and Google Gemini using identical prompts across three automation domains. Claude Code performed a standardized vulnerability review. Each identified vulnerability was scored using CVSS v3.1 and mapped to the OWASP Top 10:2021 and the MITRE ATT&CK frameworks. Every script contained exploitable vulnerabilities. Nine of the 17 identified vulnerability classes appeared in code from all three models, while 14 of the 17 vulnerability classes appeared in at least two models. The weighted CVSS scores across platforms differed by less than 10%. The risk is not tied to any particular model but rather to the task category. Organizations should therefore ask not which tool to trust, but instead whether LLM-generated automation code should be deployed without review.
toXiv_bot_toot
 @Techmeme@techhub.social