 @heiseonline@social.heise.de
2026-10-01 11:43:03
Eine API für Linux: Remote-Verwaltung mit systemd
Neue systemd-Features erlauben Systemverwaltung, die vorher nur mit externer Software möglich war.
https://www.heise.de/news/Eine-API-fuer-Li…
@heiseonline@social.heise.deEine API für Linux: Remote-Verwaltung mit systemd
Neue systemd-Features erlauben Systemverwaltung, die vorher nur mit externer Software möglich war.
https://www.heise.de/news/Eine-API-fuer-Li…
 @cyrevolt@mastodon.social
Just realized that the cmdline arg prefix "rd." used by systemd is for ramdisk.
https://github.com/systemd/systemd/blob/a8e93919c3fd4ff46ce7f1c7a0e73ea0a0a7eaeb/docs/INITRD_INTERFACE.md?plain=1#L62-L63…
@heiseonline@social.heise.demstack: OCI-Container mit systemd ausführen
OCI ist das Format, das Docker, Kubernetes und Konsorten verwenden. systemd bietet nun eine direktere und einfachere Integration von OCI-Containern.
https://www.
@cyrevolt@mastodon.social @vyskocilm@witter.cz
The most surprising aspect of a recent Artix (anti-systemd folks) drama is that Xlibre folks are apparently anti-anti-systemd.
Judean People Front vibes there
@heiseonline@social.heise.desdme: Das eigene Linux als Container klonen
Das eigene Linux-System schnell einmal klonen, um etwas zu testen: Das bietet sdme, der systemd Machine Editor.
https://www.heise.de/news/sdme-Das-eigene-…
 @qbi@freie-re.de
Warum hat @… keine Systemd-Unit? #Offline
#systemd #systemctl
 @dawid@social.craftknight.com
Gdybyście kiedyś sobie zablokowali serwer poprzez wykorzystanie limitu procesów - objawia się to brakiem możliwości zforkowania procesów, czyli w ogóle nawiązanie jakiejkolwiek sesji - to ciekawym rozwiązaniem jest spróbowanie port forwardu na sockecie dbus od systemd :)
SSH port forward nie tworzy nowego procesu, pisanie do dbus systemd po sockecie również - pozwala to na zatrzymanie serwisów i odblokowanie się bez restartu maszyny...
 @izzychambers@vivaldi.net
@… Take a look at this article for possibilities: https://itsfoss.com/systemd-free-distros/
 @michabbb@social.vivaldi.net
⚙️ Per-role backends: claude, codex, copilot or grok. Runs locally, keeps all state in .swarmforge/, prevents host sleep via caffeinate or systemd-inhibit, and opens https://Terminal.app, Ghostty or Windows Terminal through pluggable adapters
🌐
 @stefan@gardenstate.social
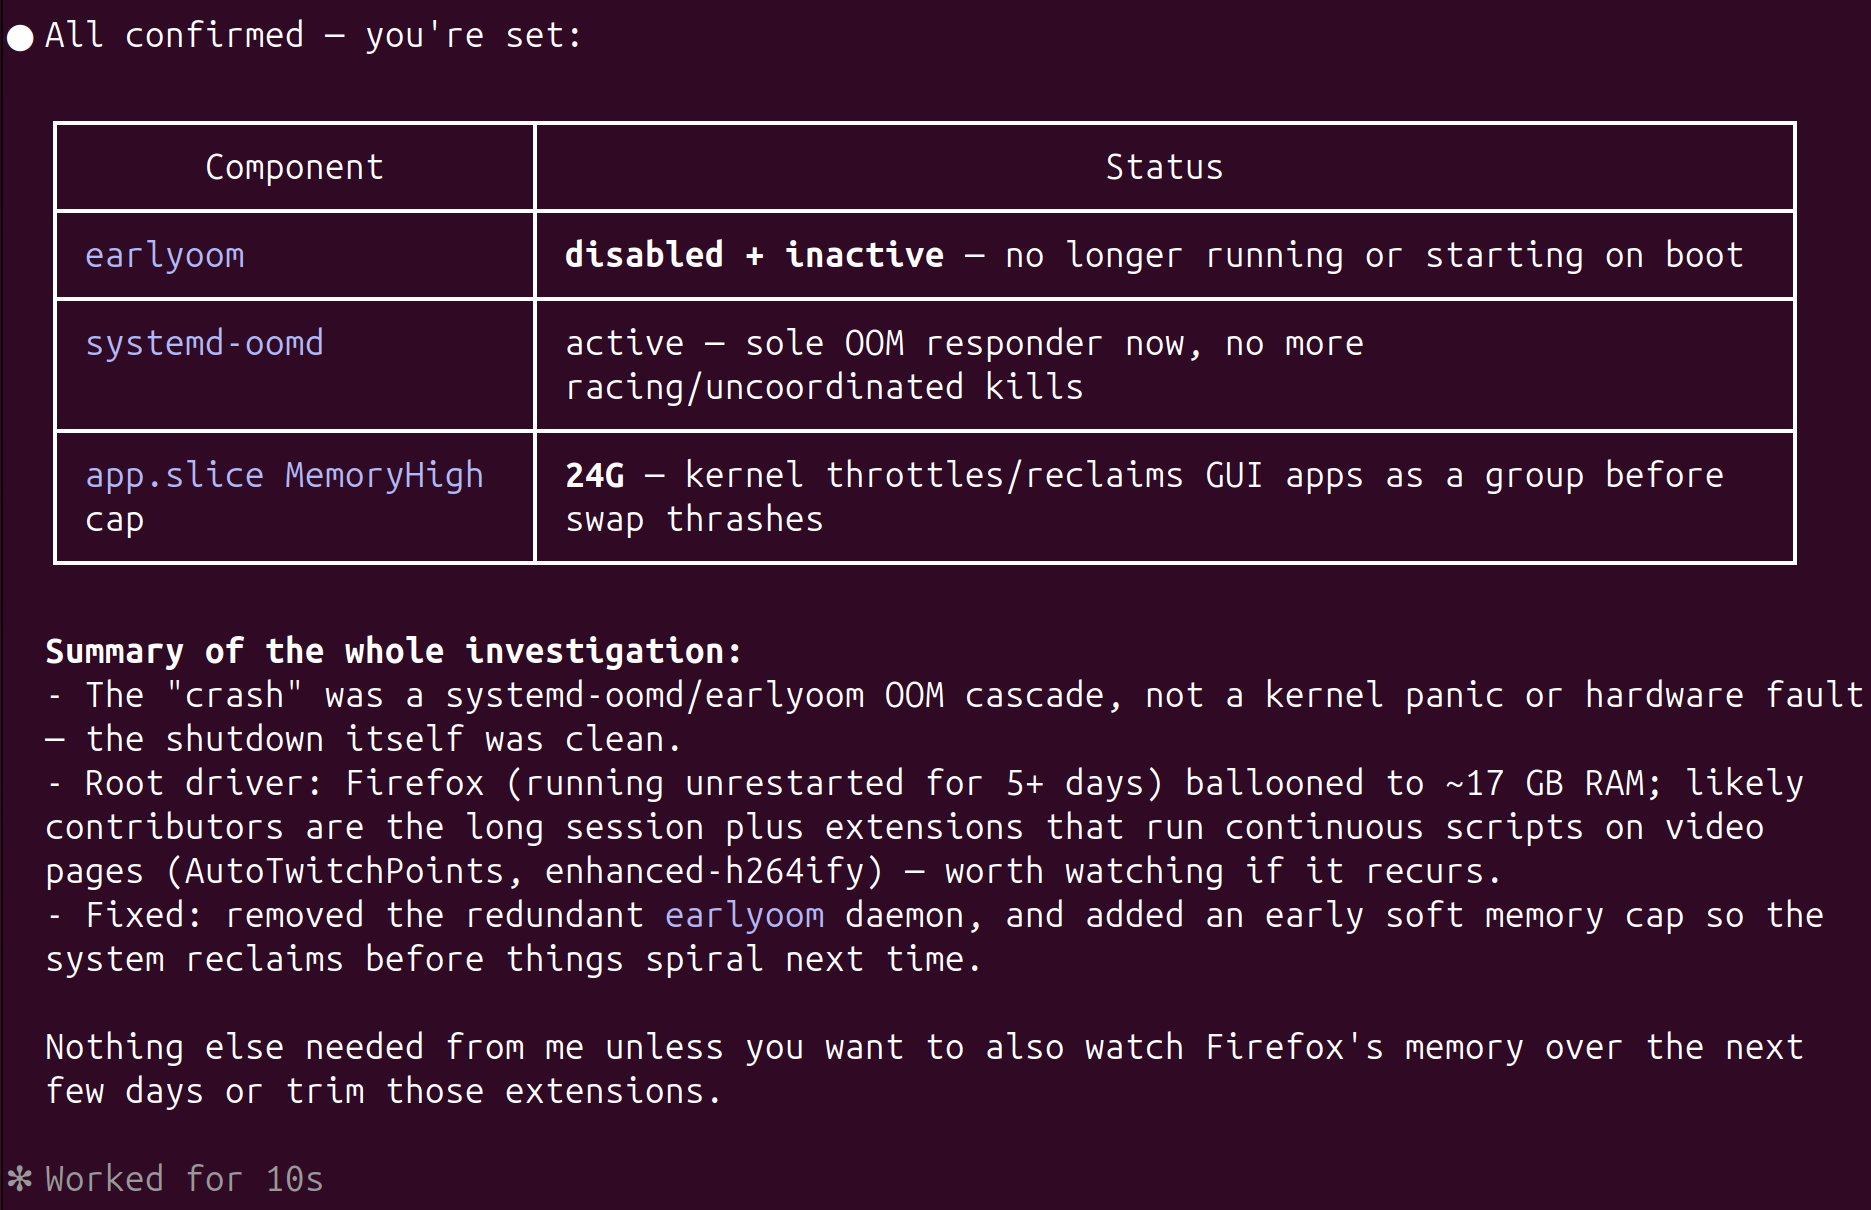
This incite in to what my ubuntu system is doing that would have taken hours of time to research if I ever could have learned it at all had I not used an LLM. I'll continue to caveat that LLMs have many many things about them that are bad on multiple levels.
Using LLMs to fix system problems is doing something I wouldn't be able to do otherwise.
#ai
 @thokall@social.linux.pizza
I am using Fedora server in my homelab setup mainly hosting Nextcloud and Minecraft for family as well as an Forgejo instans. Planning to add Immich as well as Paperless in the near future. I run all services with Podman containers managed via quadlet unit files orchestrated by systemd. My feeling is that this solution fits with nicely with Fedora, but since documentation and deployment instructions is often using docker/docker-compose it often requires me to make adjustments that takes more…
 @fell@ma.fellr.net
If Microsoft keeps extending WSL, let's make systemd-windowsd. Fight fire with fire.
 @luana@wetdry.world
They should make systemd-oom but that actually works
 @theodric@social.linux.pizza
For some reason the arctic_fan_controller module spams dmesg and doesn't expose a debug=0 parameter to STFU. Workaround is `echo "module arctic_fan_controller -p" | sudo tee /sys/kernel/debug/dynamic_debug/control` in a systemd service to persist the setting.
@cyrevolt@mastodon.socialBSDs still need a modern init system that is not a pile of shell scripts. 😬 Now would be a good time to catch up.
https://social.bsdlab.au/objects/29af8064-9c12-4687-87af-701ddde19acd
@cyrevolt@mastodon.socialAre you also using #systemd/#Linux?
https://www.bilibili.com/video/BV1M6Tw6uE4F
 @marcus@hachyderm.io
Small update on this #mobile #nixos pixel 9 pro effort. Most of the hardware still don’t work, but I do have a full uboot->systemd boot chain which makes my life a lot simpler for iteration, no more manual fastboot flashing to try new kernel fixes. Also I put the flake on my forgejo in case anyone want to play along at home. https://code.bas.es/marcus/nixos-pixel-9pro
@luana@wetdry.worldNixOS without systemd!!
#NixOS
 @teledyn@mstdn.ca
my Social app installation in #Nextcloud is giving a strange error:
Firefox can’t establish a connection to the server at wss://nextcloudpi/push/ws.
My config defines a proxy for ws:// and the notify_push:self-test checks ok as does systemctl status, but a grep of the app/social code shows js mentions of wss:// - I also notice the dashboard also logs these errors, likely because Social is active? or because my systemd adds --allow-self-signed?
I tried modifying the ProxyPass to wss: to no avail, double checked installed modules and the reqs from the notify_push git page. I did find mention that wss is the secure version, only recommended where NC and NP are on different machines, which they are not.
maybe it is benign? My only symptom so far is nothing goes out, and nothing comes in to @… and one of these days I'm going to figure out why!