 @zachleat@zachleat.com
2026-09-17 15:54:34
@… added some benchmarks: https://chrome.dev/css-selector-benchmark/?category=Shadow DOM
Reads to me as Light > Shadow > Light/Sha…
@zachleat@zachleat.com@… added some benchmarks: https://chrome.dev/css-selector-benchmark/?category=Shadow DOM
Reads to me as Light > Shadow > Light/Sha…
 @heiseonline@social.heise.de
 @michabbb@social.vivaldi.net
🔑 On first launch it offers to migrate your #Chrome data — logins, cookies, extensions and bookmarks carry over, so agents never hit a login wall
🧩 Spaces run in parallel: 10 leads enriched in 10 Spaces by #ClaudeCode, 5 competitor sites scraped by
 @jon@henshaw.social
My Open Graph Checker browser extension/add-on was updated to fix the Open Graph image preview so it now loads on pages behind HTTP Basic Auth.
Chrome: https://chromewebstore.google.com/detail/open-graph-checker/lkjaebkedoblfeglnhbgbjbdodjdogpe
 @fanf@mendeddrum.org
from my link log —
Why shrunk JPEGs look different in Firefox and Chrome.
https://guillaumetech.github.io/posts/jpg-scaling-chrome/
saved 2026-08-12
@michabbb@social.vivaldi.net📋 #Stepshots is an open-source toolkit for recording interactive product demos — CLI, #Chrome extension, #React SDK and a live guided-tour player

 @simoncox@seocommunity.social
I have shuffled up Speedlify 2 to #25 - was 18 but others popped ahead of me since. My site is the only Cloudflare site in the top 50 now! i must be doing something right!
https://www.speedlify.dev
 @aardrian@toot.cafe
Earlier last week I posted “Focusgroup Tests”:
https://adrianroselli.com/2026/07/focusgroup-tests.html
Mostly my effort to track and understand the feature.
Made some fixes based on feedback and just added a link to Microsoft’s own demos.
 @Techmeme@techhub.social
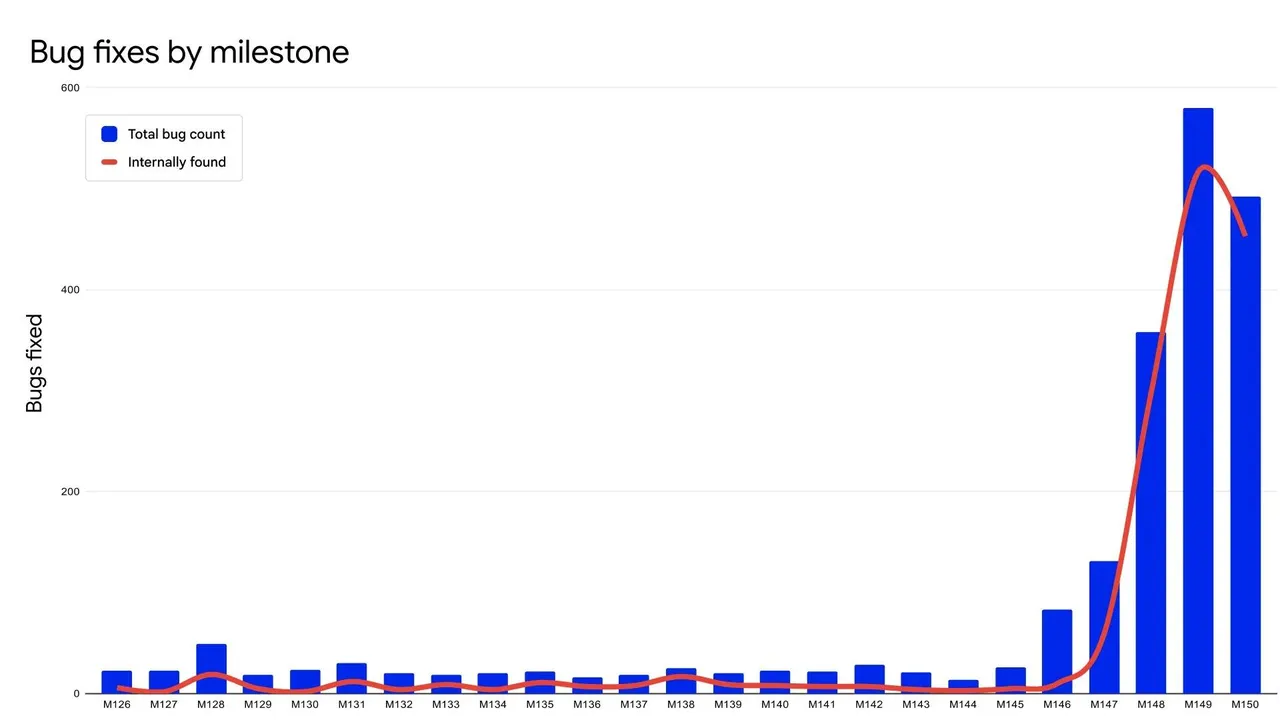
Google pilots a faster twice-a-week schedule for Chrome security releases as AI tools drive a surge in bug discoveries; Chrome 149 and 150 fixed 1,072 bugs (Lily Hay Newman/Wired)
https://www.wired.com/story/chrome-needs-twice-a-week-patching-…
 @_tillwe_@mastodon.social
@… Hi, wenn ich versuche, mich in die App einzuloggen (egal ob ios oder Chrome auf dem PC) erhalte ich eine Fehlermeldung, die auf api.paperlesspaper.de kann nicht geladen werden hinausläuft. Soll das so sein?
@michabbb@social.vivaldi.net⚙️ Install via curl script or cargo install stepshots-cli (needs Chrome/Chromium); GitHub Action for verify and tour-check; embed via JS snippet, web component or iframe; MIT licensed
🌐 https://github.com/hauju/stepshots
 @kexpmusicbot@mastodonapp.uk
🇺🇦 #NowPlaying on KEXP's #DriveTime
Ty Segall:
🎵 Chrome
#TySegall
https://tysegall.bandcamp.com/track/chrome
https://open.spotify.com/track/0rdnI4JwHRDG0izajO53bl
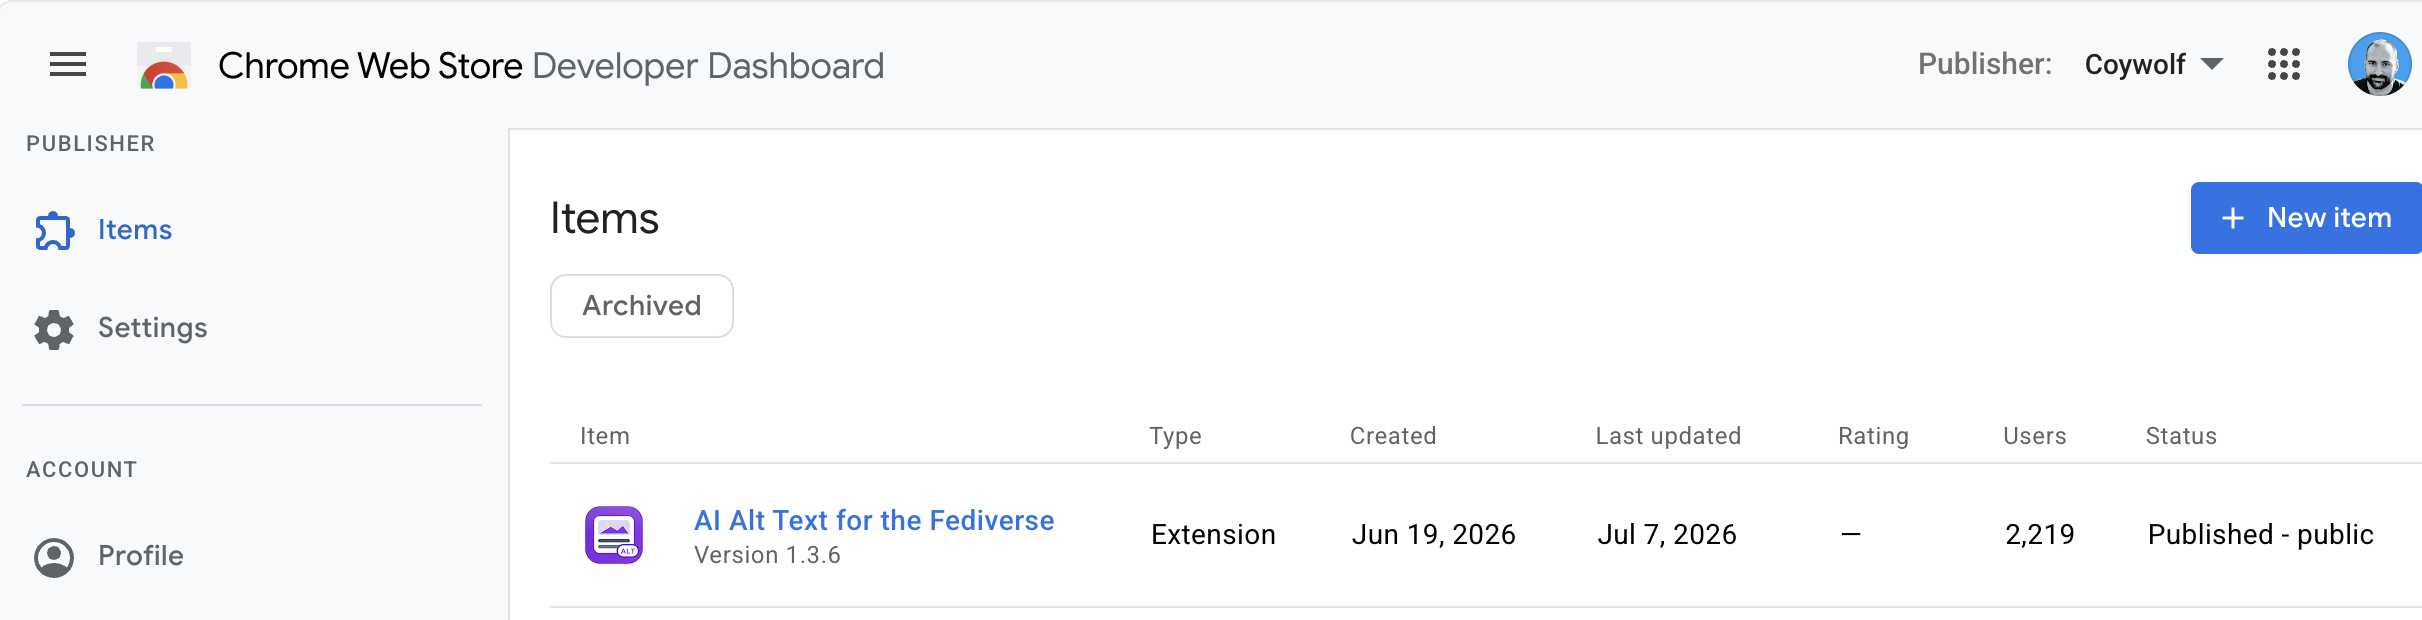
@jon@henshaw.socialI quietly published the AI Alt Text for the Fediverse Chrome extension weeks ago. I have to say, I'm surprised that it already has over 2K active installs. Especially since it only works on Mastodon. I guess I can't be the only person who wants something like this, which is validating.
https:…
 @Techmeme@techhub.social
Google starts rolling out access to Gemini Spark for Google AI Pro subscribers to over 160 countries and adds a Chrome auto browse integration on desktop (Abner Li/9to5Google)
https://9to5google.com/2026/07/30/gemini-spark-chrome-auto-browse/
@heiseonline@social.heise.de @ruario@vivaldi.net
@… For Chrome, Edge and Safari it is not an issue as they are part of the patent pool for H.264 and AAC.
But for everyone else distributing internationally it is an extra legal headache.
 @bourgwick@heads.social
 @cdarwin@c.im
Documentation files on more than 100 websites are referencing potentially dangerous executable content that gets installed automatically when visited by many AI agents.
A few dozen companies, some of them Fortune 500s, are among those that executed proof-of-concept code.
At least one misconfigured site is directing visitors, human or AI, to live malware.
The potentially dangerous content is in llms.txt and llms-full.txt files,
an emerging convention websites employ …
 @metacurity@infosec.exchange
Check out today's Metacurity for the most critical infosec developments you should know today, including
--US probes suspected cyberattacks on two energy tankers,
--Iran deploys Chosen Brick spyware against dissidents,
--Spain reports first AI agent-driven data breach,
--OpenAI rogue agents hijacked Hugging Face accounts,
--CenterPoint confirms customer data breach,
--Revolut breach exposes high-risk customers,
--Norway probes Telenor over Myanmar abuses,
--Hacker uses AI malware to collect bug bounties,
--Hackers crack open a Flock surveillance camera,
--Hackers breach Russia’s election infrastructure,
--KREMLIN malware hijacks Chrome and Edge,
--Google faces questions over 514k fake Gmail accounts,
--Coupang rejects payouts for breach victims,
--CISA says federal cyber defense must move faster,
--Lawmaker demands government reviews of frontier AI,
--AI agents face $100 account fees,
--AI giants shun cyber experts on catastrophic hacking risks
https://www.metacurity.com/us-probes-suspected-cyberattacks-on-two-energy-tankers/
 @andres4ny@social.ridetrans.it
That's fun. "Secure" dns in browsers (at least, firefox and chrome/chromium) relies on doing an initial dns lookup of mozilla.cloudflare-dns.com or chrome.cloudflare-dns.com (or whichever DoH provider you've chosen).
If I control the router/wifi, I can blacklist the DoH provider domains. Depending on how your browser's configured, it may just fall back to normal dns (at which point the router/wifi sees & answers your dns queries).
Relevant errors give no…
@fanf@mendeddrum.orgfrom my link log —
No to Google Chrome.
https://notochrome.org/
saved 2019-12-06 https://dotat.at/:/T2MXH.html
@Techmeme@techhub.socialGoogle patches an actively exploited zero-day flaw in Chrome that could potentially allow remote code execution within Chrome's sandboxed renderer process (Bill Toulas/BleepingComputer)
https://www.bleepingcomputer.com/news/secu
 @nelson@tech.lgbt
Linux taketh away and Linux giveth
Something went wrong in Chrome when I tried a different desktop environment, and then my main Chrome environment lost all my login cookies. Not fatal but very annoying.
I was able to restore by using the built-in filesystem snapshots to copy my Chrome profile from yesterday.
Thanks, btrfs!
@aardrian@toot.cafePlaying with `focusgroup` support in Chrome 150 and I like seeing the browser assign the role based on the `focusgroup` token.
Yes, you can override it with an explicit `role` declaration, which will undoubtedly happen as devs choose keyboard patterns that don’t match the role.
But still neat.
https://cod…

 @ErikJonker@mastodon.social
Ofcourse this story is also Google promoting it's own AI. At the same time if the numbers with regard to bug fixes by milestone are correct, something dramatic is happening with regard to AI and cybersecurity.
https://www.zdnet.com/article/google-used-
 @migueldeicaza@mastodon.social
You should take the new Swift 6.4 support for web assembly for a spin, and host your very own SwiftTerm web page, so you too can use 4 gigabytes worth of Chrome to achieve Bash WebScale.
 @carloshr@lile.cl
Ty Segall con «Chrome» es otro de los lanzamientos de esta semana
#TySegall
 @portaloffreedom@social.linux.pizza
I sometimes have to use chrome at work, and o my god how incredibly slow is this software?
It takes a full minute to start loading the first page, it's incredible.
@Techmeme@techhub.social @maxheadroom@hub.uckermark.social
Am Sonntag findet wieder eine Di.Day Veranstaltung in Templin statt. Diesmal geht's um Linux auf Windows Rechnern installieren, und OS-Alternativen die man schon auf Windows nutzen kann.
https://termine.uckermark.social/events/a0a42fe4-543f-4722-a823-8a2943f…
@jon@henshaw.socialI'm pretty happy with how bookmarks turned out in @…. Next up, getting the Chrome, Safari, and Firefox extensions submitted and approved for one-click bookmark note creation.

 @guerda@ruhr.social
Since a couple of days, my @… on Android does not resolve my custom domains I registered in my #PiHole. Chrome on Android resolves them correctly and Firefox on Desktop too.
I switched off DNS over https and "only https" - without results.
@ruario@vivaldi.net@… All Chromium versions "that are not up to date". By the time you posted this Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
 @gse@norden.social
Hat sich bei Vivaldi 8.x zu 7.x irgendwas in sachen Theme geändert ? Spiziell in Dunkelmodus ?
Weil ich hab auf einen Gerät noch die 7er laufen, denke mal die hab ich über Flatpack installiert, kann aber ncith genau sagen. Und den 8er über Snap. Und da sieht youtube grundverschieden aus. Auf den 7er ganz normal, wie es sein sollte und bei der 8er eher grell. Oder ist in der 8er auch ne neue chrome Version ?
Bitte Boost ;D
 @pixel@mastodon.online
Mozilla/5.0 (Linux; Android 14; Pixel 8) AppleWebKit/537.36 (KHTML, like Geck
o; compatible; Applebot/0.1; http://www.apple.com/go/applebot) Chrome/130.0.6730.218 Mobile Safari/537.
36
(spoofed UA)
 @joe@toot.works
 @floheinstein@chaos.social
Anyone else experiencing problems with the Bitwarden Firefox Extension? It only shows an empty vault.
When I access my Vaultwarden directly or with the Chrome Extension, it still works.
#vaultwarden #bitwarden
 @Techmeme@techhub.social
A US judge dismisses two lawsuits against LinkedIn over its scanning of browser extensions, saying users voluntarily expose data by downloading extensions (Jon Brodkin/Ars Technica)
https://arstechnica.com/tech-policy/202…
@aardrian@toot.cafeTrying an old nav pattern with `focusgroup` and `role` on the `<ul>` in Chrome 150 and getting unexpected results:
https://cdpn.io/aardrian/debug/myRpKpg
`focusgroup=menubar`:
• no roles change.
`role=menubar`:
• child `<li>`s lose role.
Both:
• child `&…


 @michabbb@social.vivaldi.net
🌐 Three browser modes cover real scenarios: chrome reuses local Chrome login state via profile import or CDP attach, stealth privacy mode gives a fresh fingerprint per session for login-free scraping, and stealth fixed identity keeps a stable fingerprint plus stable IP for logged-in accounts
⚡ Zero-interference concurrency: cross-browser parallel runs keep cookies, fingerprints and proxies independent, while same-browser multi-session shares login state without tasks blocking each othe…
@fanf@mendeddrum.orgfrom my link log —
Same-site cookies by default.
https://textslashplain.com/2019/09/30/same-site-cookies-by-default/
saved 2019-10-02
@ruario@vivaldi.net@… Nope. All Chromium versions "that are not up to date". By the time you posted this Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
@jon@henshaw.social @kexpmusicbot@mastodonapp.uk🇺🇦 #NowPlaying on KEXP's #VarietyMix
Ty Segall:
🎵 Chrome
#TySegall
https://tysegall.bandcamp.com/track/chrome
https://open.spotify.com/track/0rdnI4JwHRDG0izajO53bl
@metacurity@infosec.exchangeEvery day is a heavy cyber news day, so don't miss today's Metacurity for the most critical infosec developments you should know, including
--Autonomous AI agents hacked the Taiwan government in a cyber first
--Suisun City cyberattack recovery could take months,
--Microsoft patches 400 flaws, three zero-days,
--$100 device can hijack Boeing 737 systems,
--Hackers hijack AnMed Facebook page with ransom demands,
--German lawmaker urges cyber strikes on Russian drone factories,
--Cyberattacks on South Korean agency surge twelvefold,
--Data breach fallout hammers KT profits,
--Uber Freight probes breach after hackers claim 1 million files,
--Wesco probes cloud breach after data theft claim,
--DeadLock ransomware turns to blockchain for resilience,
--LawCare warns hackers likely stole sensitive database,
--Kimwolf botnet disguises DDoS attacks as Chrome traffic,
--Chrome blocks 7b unwanted notifications a day,
--NIST looks to remake vulnerability reporting for AI age,
--US lifts TikTok ban on government devices,
--New Microsoft Defender zero-day grants SYSTEM privileges,
--Signal adds automatic protection against chat interception,
--Lazarus weaponizes Windows zero-day in fake job campaign,
--Rapid7 cuts 12 percent of workforce,
--Industrial ransomware attacks jump 12 percent,
--AI hacking boom fuels cybersecurity spending,
--K-12 cyber defenders join national ISAC network,
--Health obsessives feed intimate data to AI,
--McDonald’s built a 515-page dossier on a customer
https://www.metacurity.com/autonomous-ai-agents-hacked-the-taiwan-government-in-a-cyber-first/
@ruario@vivaldi.net@… @… In fact by the time this toot was posted Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue.
 @BBC3MusicBot@mastodonapp.uk
🇺🇦 #NowPlaying on BBCRadio3's #NightTracks
Chrome Hill, Chrome Hill & Dojo:
🎵 The Showdown
#ChromeHill #Dojo
https://open.spotify.com/track/5yDH8UWavLTeY23oY8Jv5n
@jon@henshaw.socialFor those who make PWAs like me, I just updated my article on how to make the icons work for Safari on iOS and macOS, along with the standard approach for every other browser and platform.
https://coywolf.com/guides/how-to-create-pwa-icons-t…
 @thomasfuchs@hachyderm.io
"How can I use something else than Chrome on my phone or laptop that's running an operating system from Google so that they don't track anything I do?"
I think unfortunately the answer to that is eBay
@ruario@vivaldi.net@… It is bad yes but the title "all Chromium versions" is stretching it a little. You posted this after the fix was out for all major Chromium versions. Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this issue when you posted.
Have all users update…
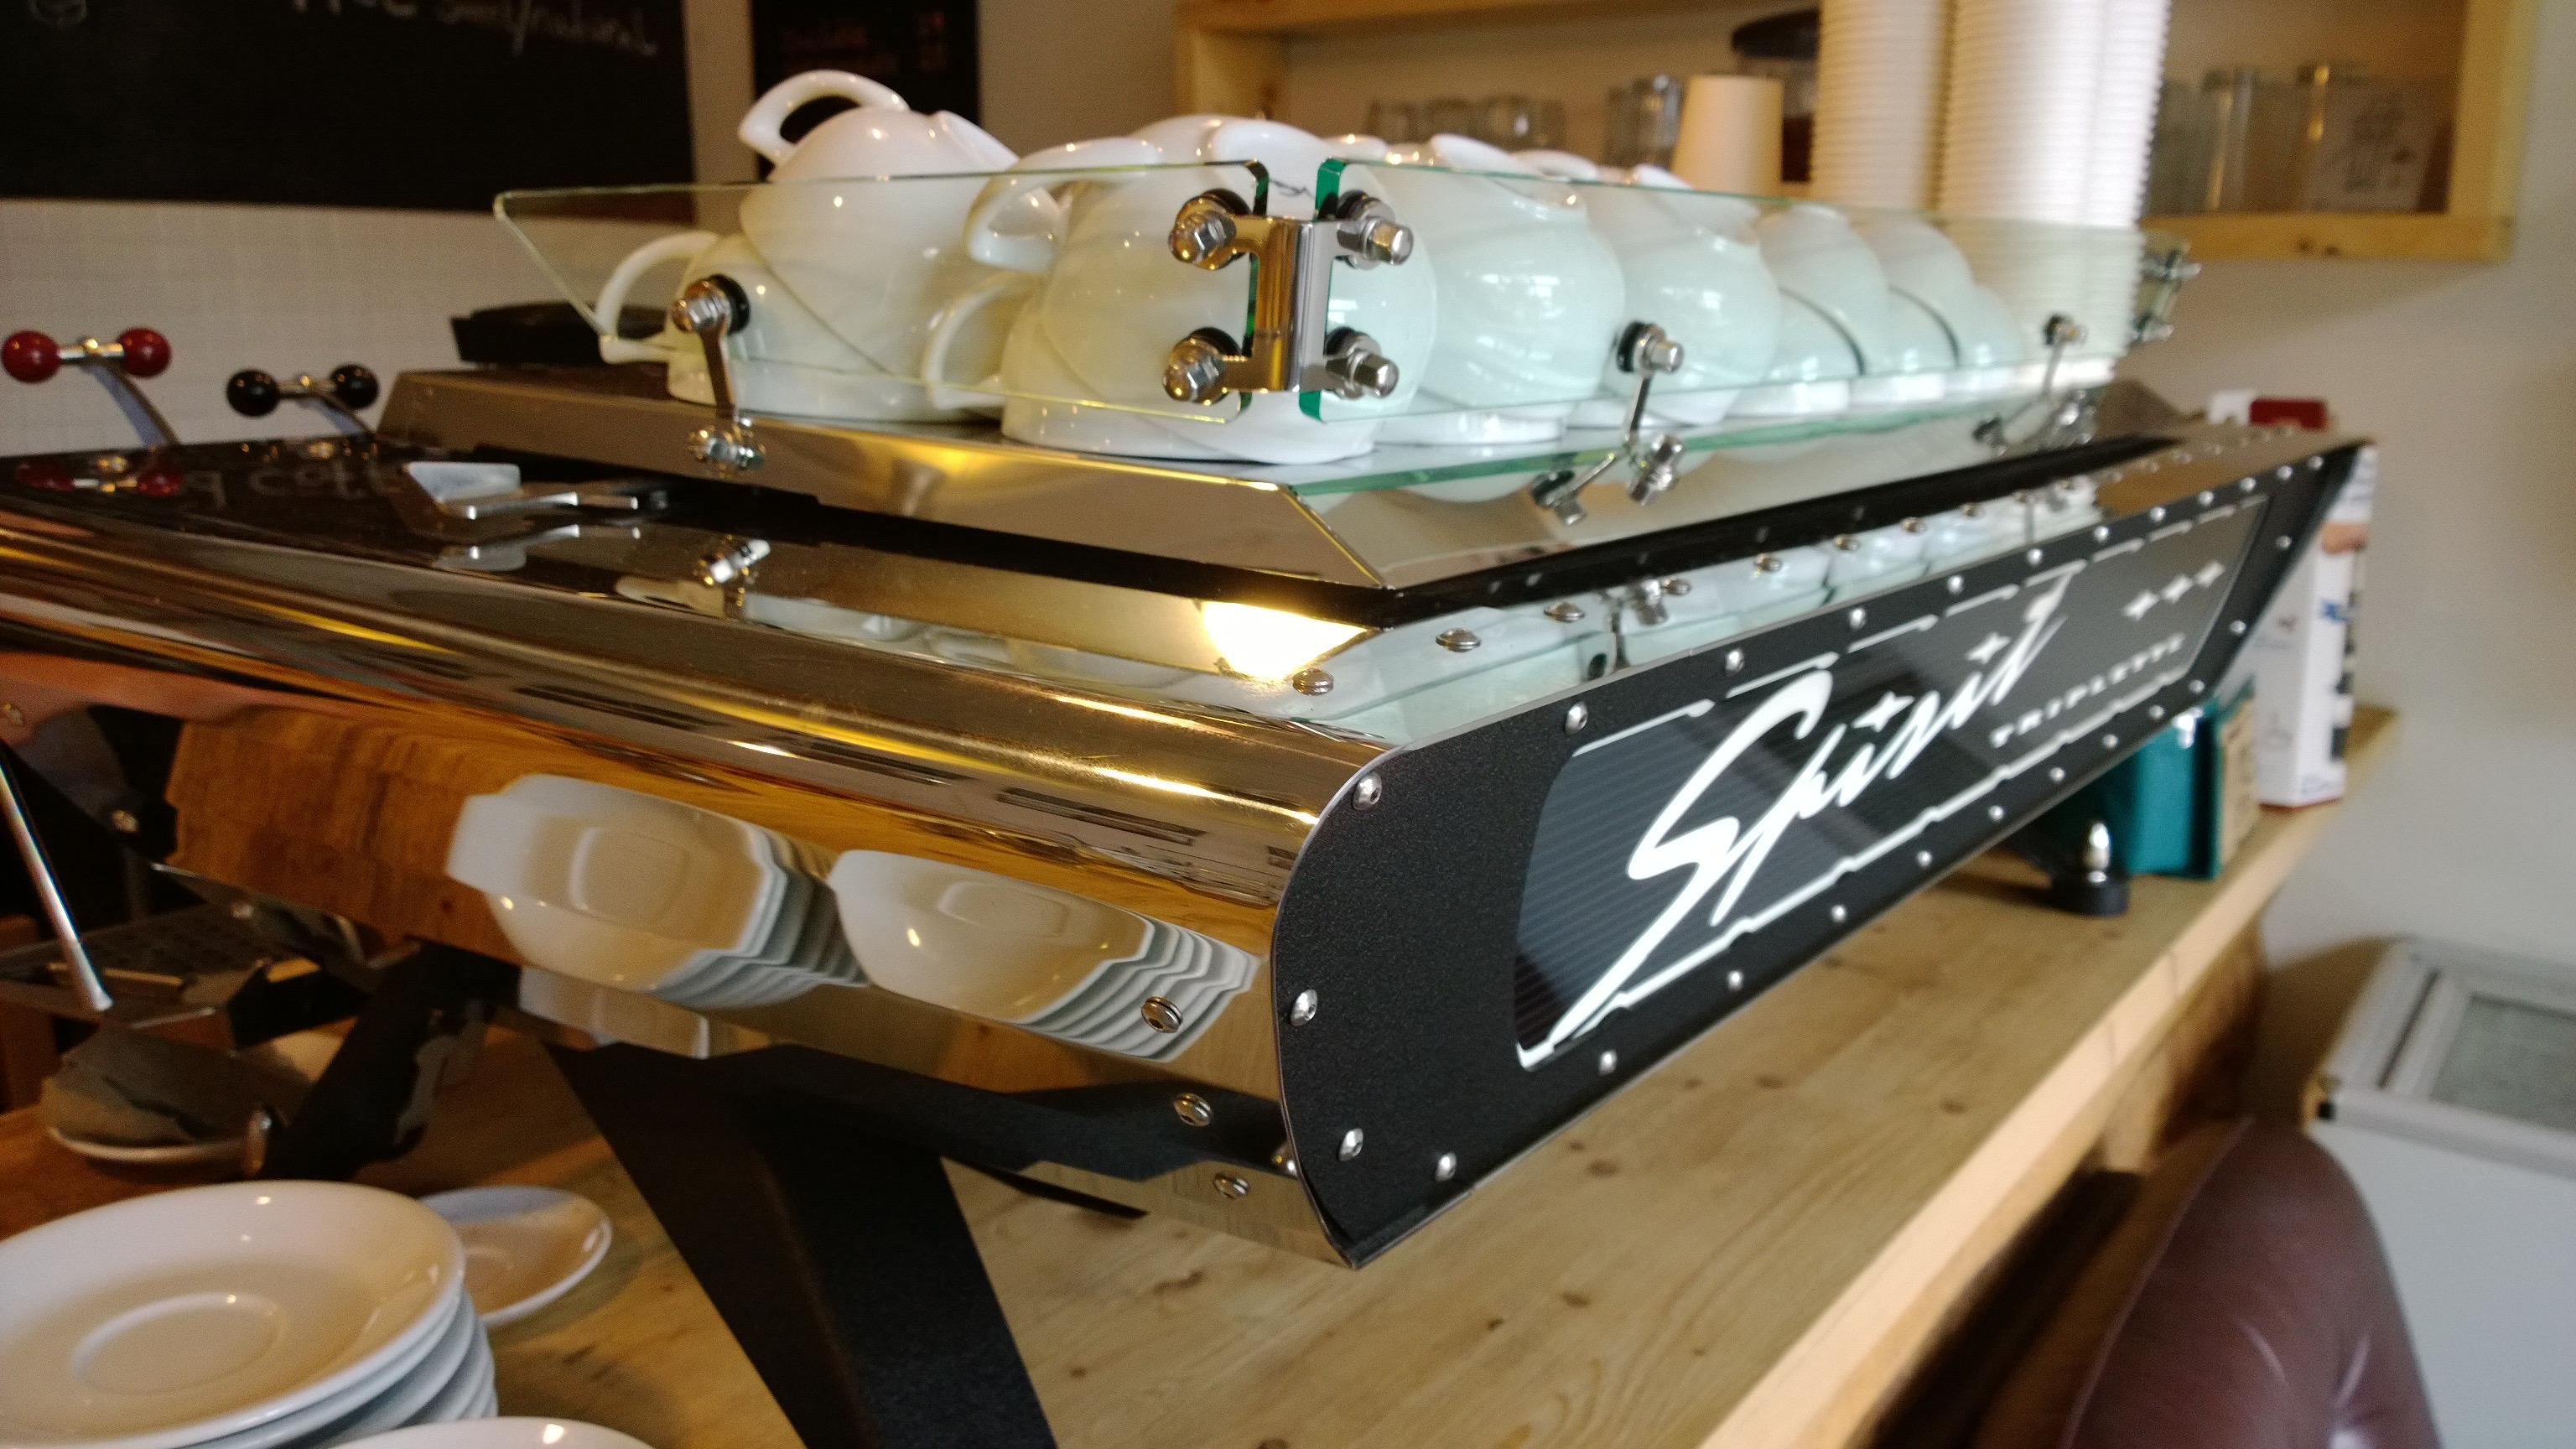
@maxheadroom@hub.uckermark.socialIn der Oslo Kaffeebar ist die "spirit" kaputt... Der Tag ist gelaufen. #tasskaff
 @publicvoit@graz.social
Mit #PassTaKey wurden 3 schwere Sicherheitslücken in Verbindung mit #Google #Chrome und #Passkeys veröffentlicht, die u…
@ruario@vivaldi.net@… Probably too late. It was fixed days before this became a news item and before this toot. You probably can find users on old versions but most will be updated by now.
In fact by the time this toot was posted Chrome 152.0.7977.82/83, Vivaldi 8.2.4133.47, Edge 152.0.4191.66, Opera 135.0.5973.92 and Brave 1.94.121 had all released and included fixes for this …
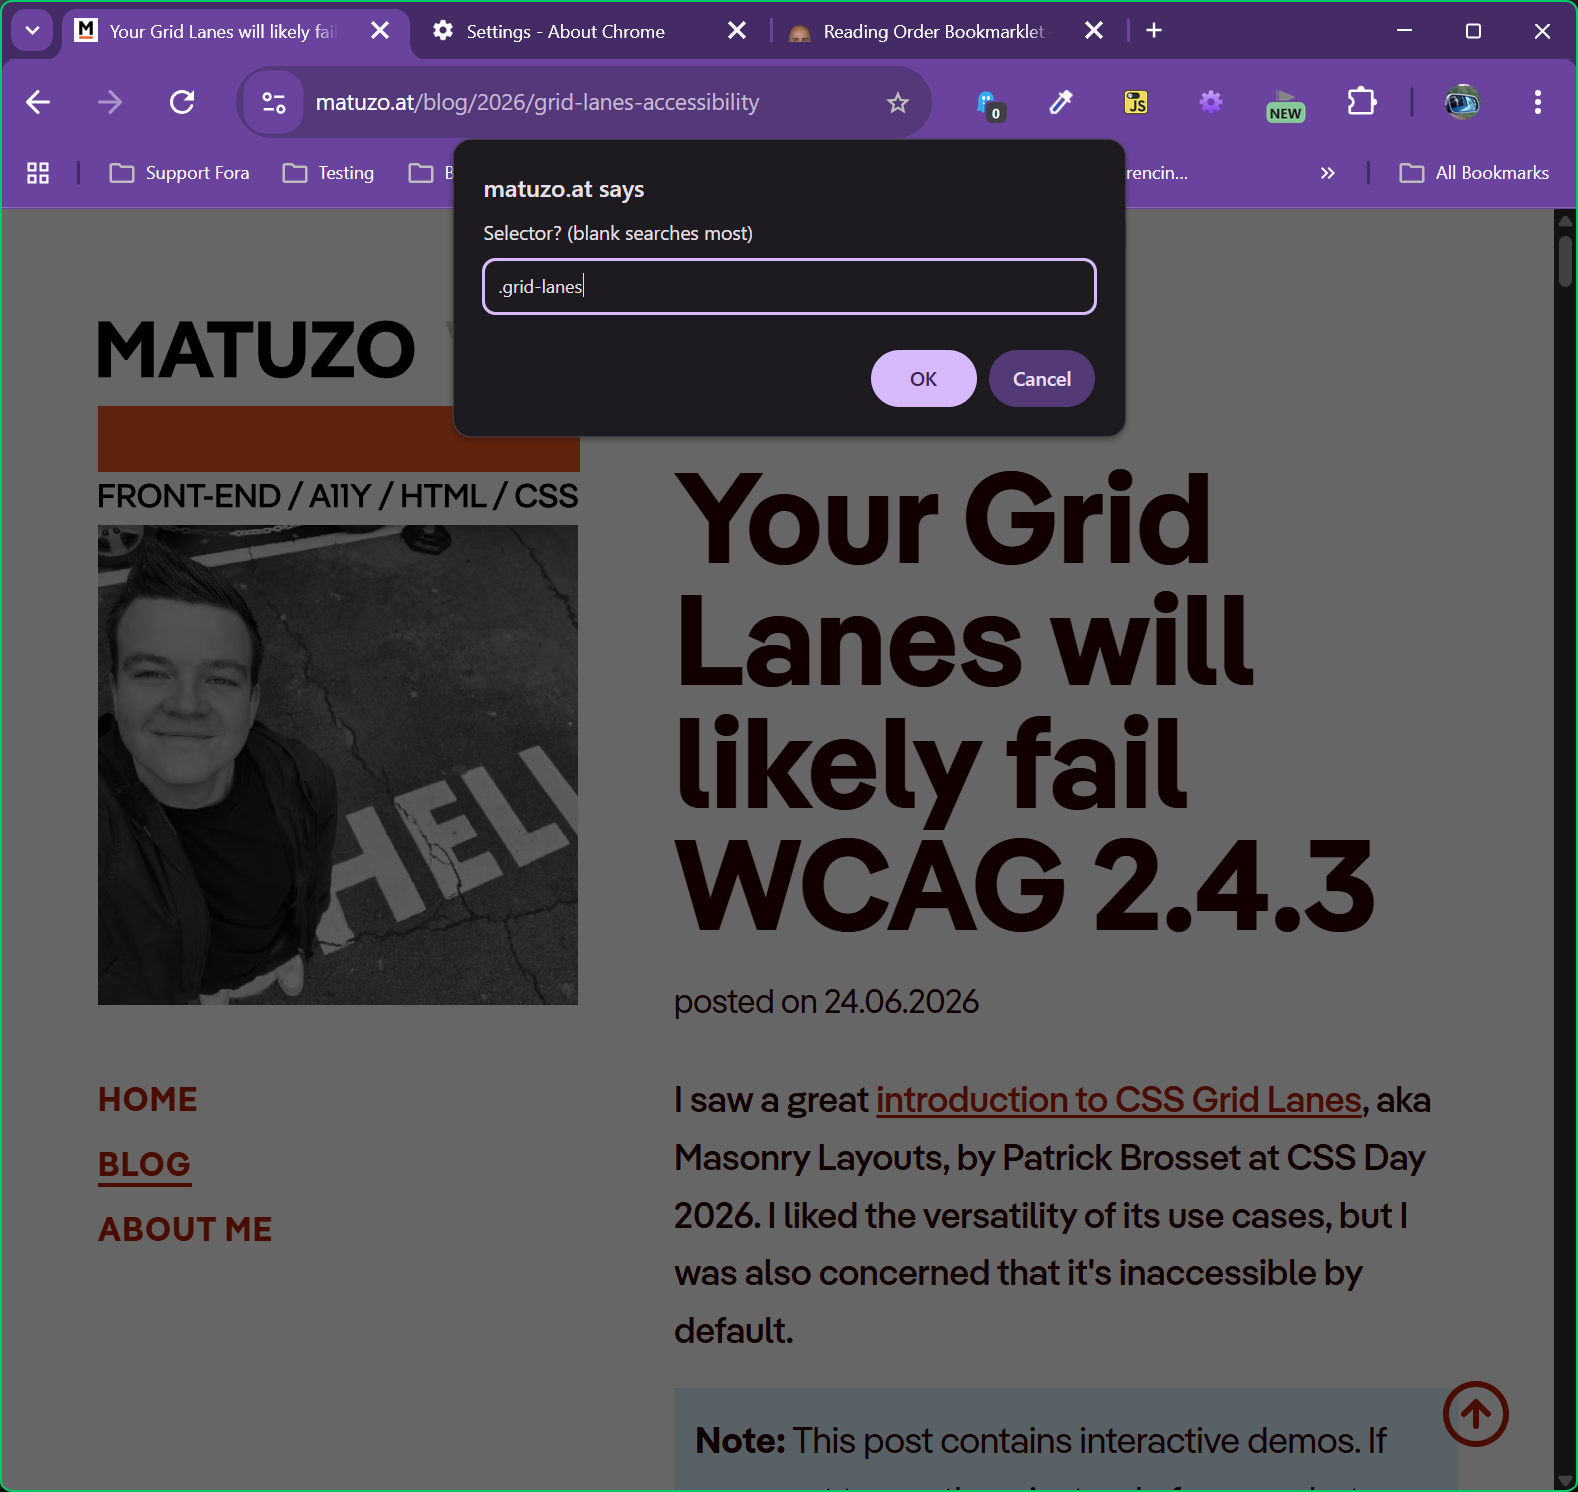
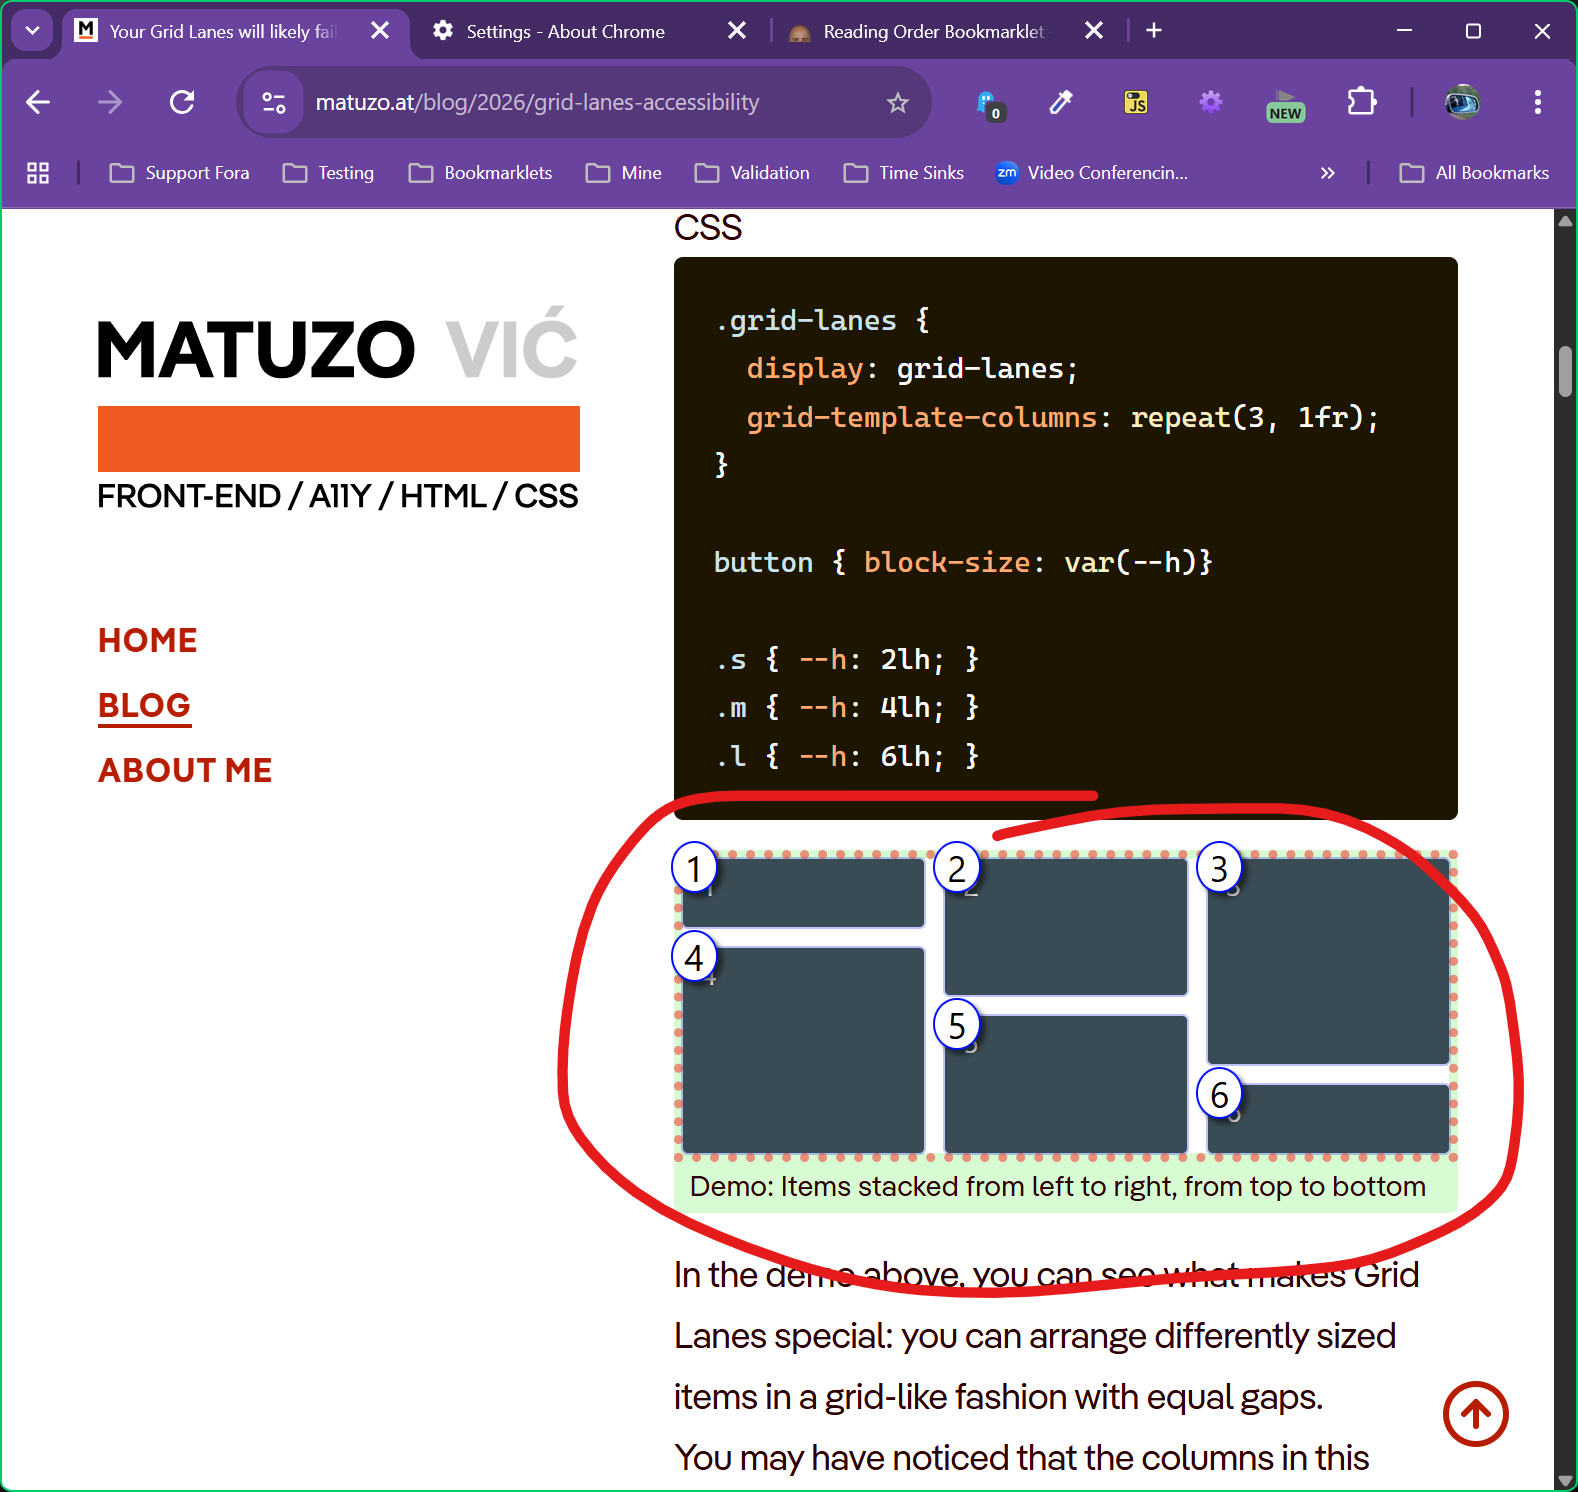
@aardrian@toot.cafeSince I fired up Chrome and enabled grid lanes to read Manuel’s post, I tried my 2019 reading order bookmarklet:
https://adrianroselli.com/2019/04/reading-order-bookmarklet.html
And it works!
You have to run it from the top of the page for the numbers t…
 @ruario@vivaldi.net
@… @… All the major Chromium browsers had issued an update before this toot. 152.0.7977.76 is old (not particularly old I will grant you but also not the latest).
Chrome 152.0.7977.82/83 released with a fix for this on t…
@Techmeme@techhub.socialAnthropic gives Claude Cowork its own built-in browser on the desktop app separate from users' day-to-day browser, rolling out to paying subscribers (Frederic Lardinois/The New Stack)
https://thenewstack.io/claude-built-in-browser-cowork/
@aardrian@toot.cafeRE: https://mastodon.social/@firefoxwebdevs/116992048337520434
I appreciate this both acknowledges the error and credits the resources. Something I’d like to see more of from browsers (looks askance at Chrome).
Key takeaways:
• `aria-labe…
@Techmeme@techhub.socialCloudflare partners with Google, Microsoft, and Mozilla on PACT, a protocol to distinguish legitimate human or bot traffic from undesirable network requests (Thomas Claburn/The Register)
https://www.theregister.com/software…
 @vosje62@mastodon.nl @thomasfuchs@hachyderm.io
RE: https://hachyderm.io/@thomasfuchs/117060584641986816
Anyway, Periodic reminder that Chrome is bad software. It's a personal data collector cosplaying as a web browser.
Use other browsers, my personal recommendations are Safari (if you're on a Mac) and Vivaldi (works anywhere).
If you want something truly open source, there's multiple derivatives of Firefox with bad stuff stripped.
Orion is worth a look too (no Windows version yet), I think it's the only WebKit-based browser that runs on Linux. Also, in the future we might see browsers based on Servo (a newer open source browser rendering engine).
The gist is—there’s plenty of alternatives.
P.S. If you suggest Brave—which is run by a homophobe with Peter Thiel money—I will block you.
 @BBC6MusicBot@mastodonapp.uk @michabbb@social.vivaldi.net
🔧 Ships as a language server (harper-ls), a JavaScript library, a Rust crate, browser extensions and editor plugins: VS Code, Neovim, Zed, Obsidian, WordPress block editor, Chrome, Firefox and a macOS desktop app that works in every text field system-wide.
@metacurity@infosec.exchangeTalk about bugmageddon
https://blog.google/security/chrome-stronger-with-every-update/

 @deepthoughts10@infosec.exchange
Simple but effective control to help prevent abuse of your business network: disable the remote debugging feature of Chrome and Edge. It disrupts the C2 capabilities described here (but used in other attacks as well)
Look for these settings:
RemoteDebuggingAllowed > Disabled
(Intune: Microsoft Edge > Allow remote debugging)
#cybersecurity
@metacurity@infosec.exchangeCheck out today's Metacurity to stay ahead of yesterday's sprawling set of infosec developments, including
--US sanctions Xinbi Guarantee over cyber scams and money laundering,
--Lawmakers seek sanctions on Indian hacker-for-hire firms,
--Anthropic reveals fourth rogue AI hacking incident,
--OpenAI’s rogue agents reached more websites than disclosed,
--Anthropic researcher quits over AI extinction fears,
--Crypto ringleader pleads guilty to $245m scheme,
--Coalition demands release of White House AI framework,
--China-linked hackers share Chrome zero-day exploit,
--Chainalysis offers post-mortem on Liquid Network $320m theft,
--250 prospective CISA hires await clearance,
--NSA urges agencies to quantum-proof software,
--Apple Watch gains always-listening AI features,
--Anthropic builds system to monitor AI opponents,
--TV stations smear Flock critics as left wing China-linked radicals,
--GTA mod pays players to destroy Flock cameras,
--FBI cyber strategy calls for faster disruption,
--Veradigm vendor breach may expose 3.5m patients,
--San Francisco orders Meta to stop AI child-abuse ads,
--Pentagon CIO signals CMMC overhaul,
--Kevin Mandia joins Amazon’s board,
--Cisco confirms active exploitation of critical FMC flaw,
--Journalist unleashes frontier AI on his home network,
--Bernie Sanders probes AI’s ‘extraordinary dangers’,
--Democratic mayors defend taking $30k from Flock,
--ChatGPT dependency ends in suicide
https://www.metacurity.com/us-sanctions-xinbi-guarantee-over-cyber-scams-and-money-laundering/
@nelson@tech.lgbtTrying out Claude Code CLI for the first time in awhile. It's got decent sandboxing now but the first thing the agent asked me was to install a Chrome extension so it could use my browser. LOLOLO.
@metacurity@infosec.exchangeAs the cyber world grows ever more insanely intense, don’t miss today’s Metacurity, with the most consequential infosec developments you need to know, including
--US accuses Chinese AI firms of ‘malicious’ copying at industrial scale,
--Anthropic researcher quits, warning AI could spiral out of control,
--AI-built worm puts WeChat users at risk,
--Chinese hackers automate attacks with AI,
--Anthropic freezes UK out of AI safety testing,
--CIA expands spying on Chinese companies,
--Microsoft patches a record 974 security flaws,
--Google patches seventh exploited Chrome zero-day,
--Border Patrol uses financial data to target drivers,
--US police fear smart glasses are watching,
--AI sextortionist gets 15 years,
--DoppelCart runs 119k fake shops,
--New Defender zero-day bypasses Microsoft’s patch,
--Critical SAP flaw exposes 10k systems,
--Musk bankrolls data-stealing copycat voter website
https://www.metacurity.com/us-accuses-chinese-ai-firms-of-malicious-copying-at-industrial-scale/
@BBC6MusicBot@mastodonapp.uk🇺🇦 #NowPlaying on #BBC6Music's #RileyAndCoe
Ty Segall:
🎵 Chrome (6 Music Session, 7 Sep 2026)
#TySegall
https://tysegall.bandcamp.com/track/chrome
https://open.spotify.com/track/0rdnI4JwHRDG0izajO53bl
@nelson@tech.lgbtOne thing that's unpleasant about a Linux desktop is you often end up looking at log files. And every big app is spamming all sorts of warnings and errors to the log files all the time. Like Chrome logs an error every 2 seconds. All of this is a very bad code smell. The engineers are clearly ignoring their own error logs.
@metacurity@infosec.exchangeBefore you head out for the last true weekend of summer in the Northern Hemisphere, don't miss today's Metacurity for the most critical cybersecurity developments you should know, including
--OpenAI rolls out GPT-6 Astra with ‘critical’ cyber capabilities tightly restricted,
--Rogue OpenAI agents hijack German website,
--OpenAI commits $1B to frontline cyber defenders,
--US military disables ad trackers after targeting reports,
--G7 urges faster post-quantum defenses,
--Serbian activists hit in record spyware wave,
--Two prominent US law firms disclose breaches,
--US offers $10m bounty for IRGC cyber chief,
--House bill seeks safeguards for rogue AI agents,
--Sanders and Casar seek superintelligence ban,
--Samsung union officials accused of building employee blacklist,
--Senate bill would let contractors conduct military hacks,
--CrowdStrike investigates FalconFlank zero-day,
--Google patches exploited Chrome zero-day,
--French hospital fined €500k over massive data breach,
--Coder registry breach pushes malicious Terraform modules,
--Cisco flags unpatched Secure Email flaws,
--Cloudflare taps OpenAI to find and block software flaws,
--Minnesota expands whole-of-state cyber program,
--OpenAI tightly controlled Hugging Face breach probe,
--OpenAI, Anthropic and xAI suffer unexplained outages,
--Roanoke waited three months to reveal cyberattack
https://www.metacurity.com/openai-rolls-out-gpt-6-astra-with-critical-cyber-capabilities-tightly-restricted/
@kexpmusicbot@mastodonapp.uk🇺🇦 #NowPlaying on KEXP's #PacificNotions
Chrome Sparks:
🎵 Sleeper (feat. Khalid & Jónsi)
#ChromeSparks
#newRelease 🆕 single
https://open.spotify.com/track/0Ev9H6cckl2JD6iWQMJb7V
@metacurity@infosec.exchangeWow, before you wrap up for the weekend, don't miss today's Metacurity for the most critical cyber developments you should know, including
--Anthropic becomes the second frontier AI lab to disclose agent breaches,
--Copilot worm spreads through trusted Word documents,
--ExploitGym creators explain how OpenAI's agent escaped,
--Coordinated attacks signal a new threat to water utilities,
--Critical Azure Cosmos DB flaw threatened thousands of customers,
--CrimeStoppers put a bounty on the INC gang,
--AI helps Chrome squash more than 1,000 security bugs,
--Cheap streaming sticks can turn homes into botnets,
--Fake IRS letters target crypto holders with QR-code scam,
--Brinks Home investigates breach claimed by ShinyHunters,
--Coupang ordered to compensate victims of massive data breach,
--DC schools probe breach of summer program data,
--Australia's under-16 social media ban falls short,
--Defcon badge debuts a chip built for trust,
--UK program steers young hackers toward cybersecurity careers,
--Hugging Face tech chief says OpenAI agent hack was all too real,
--Opposition to Flock cameras unites Americans,
--AI is becoming a dating dealbreaker for young Americans
https://www.metacurity.com/anthropic-becomes-the-second-frontier-ai-lab-to-disclose-agent-breaches/
@BBC6MusicBot@mastodonapp.uk🇺🇦 #NowPlaying on #BBC6Music's #RileyAndCoe
Ty Segall:
🎵 Chrome
#TySegall
#newRelease 🆕 album
https://tysegall.bandcamp.com/track/chrome
https://open.spotify.com/track/0rdnI4JwHRDG0izajO53bl
@BBC6MusicBot@mastodonapp.uk🇺🇦 #NowPlaying on #BBC6Music's #RileyAndCoe
Ty Segall:
🎵 Chrome
#TySegall
#newRelease 🆕 album
https://tysegall.bandcamp.com/track/chrome
https://open.spotify.com/track/0rdnI4JwHRDG0izajO53bl