 @heiseonline@social.heise.de
2026-07-17 07:17:03
Android 17 QPR1: Google veröffentlicht Beta 7 mit Bugfixes
Google liefert nur zwei Wochen nach der Beta 6 das nächste Update für Android 17 QPR1 aus. Die Beta 7 fixt vornehmlich Bugs.
https://www.
@heiseonline@social.heise.deAndroid 17 QPR1: Google veröffentlicht Beta 7 mit Bugfixes
Google liefert nur zwei Wochen nach der Beta 6 das nächste Update für Android 17 QPR1 aus. Die Beta 7 fixt vornehmlich Bugs.
https://www.
 @lpryszcz@genomic.social
 @jon@henshaw.social
I want this in my life, but it will not be in my life until it is much cheaper. Also, it has yet to be independently verified that it’s legit and works and won’t blind you. But one can hope.
h…
 @Techmeme@techhub.social
Source: Microsoft plans to release an AI security tool this month using models from Anthropic, OpenAI, and itself, as a cost-effective Mythos alternative (Aaron Holmes/The Information)
https://www.theinformation.com/briefings/exclusive-microsoft-p…
 @tiotasram@kolektiva.social
Just now thinking about how, to an ant or any of a number of other small bugs, the Underdark is literally a real thing.
 @maxheadroom@hub.uckermark.social
Let's bring these musical pearls back into the charts! #CulturedPearls
 @mnalis@mastodon.online
@… @… I'm not surprised... There is only so much developers (and their free time) and so many different nice enhancements that could be done, many important to more people.
So the first in the line to be solved are probably critical bugs, t…
 @ErikJonker@mastodon.social
 @heiseonline@social.heise.de
 @fanf@mendeddrum.org
from my link log —
Implementing FMA and finding bugs in C and Rust standard libraries.
https://shnatsel.github.io/implementing-fma-finding-bugs-in-std/
saved 2026-09-02
 @shaun@mastodon.xyz
 @metacurity@infosec.exchange
OpenAI Launches Full-Scale Effort to Patch Open-Source Bugs as It Takes on Anthropic’s MythoOpenAI Launches Full-Scale Effort to Patch Open-Source Bugs as It Takes on Anthropic’s Mythos
https://www.wired.com/story/openai-launche
 @Sythelux@social.tchncs.de
My Boss discovered open source for himself with AI.
We struggle hard with the unity lisending at work so he sad down with Claude and Godot and basically refactored our completely tool chain from unity to Godot.
We will be Silver sponsor in a couple of weeks for Godot and also Blender. Money we saved on Unity Licenses.
His biggest motivation is, that we can just fix bugs happening for our customers specific devices instead of relying on the invisible process of Unity.
 @kazys@mastodon.social
The next president is going to have to immediately park the Qatari Air Force One in the boneyard if it hasn’t been knocked out of the sky yet. That thing has to be full of homing devices and bugs.
 @primonatura@mstdn.social @Techmeme@techhub.social
Microsoft rolls out emergency fix for critical issues caused by its September Patch Tuesday update, which addressed ~1,000 vulnerabilities but introduced bugs (Tom Warren/The Verge)
https://www.theverge.com/news/995302/microsoft-out-of-band-windows-11-…
 @samueljohn@mastodon.world
 @rasterweb@mastodon.social @kazys@mastodon.social
The next president is going to have to immediately park the Qatari Air Force One in the boneyard if it hasn’t been knocked out of the sky yet. That thing has to be full of homing devices and bugs.
 @stsquad@mastodon.org.uk @heiseonline@social.heise.de
Android 17: Bekannte Bugs und erste Lösungen
Google hat mit Android 17 hat allerlei Fehler bereinigt, aber neue eingebaut. Eine Übersicht bekannter Bugs und wie sich manche beheben lassen.
https://www.
 @lightweight@mastodon.nzoss.nz
 @mro@digitalcourage.social
uh, just found #freebsd #librewolf 152.0.2-1 has buggy #tabstop behaviour - pressing TAB doesn't reliably jump to the first visible tabstop if scrolled down a bit.
 @azonenberg@ioc.exchange
Starting bringup of the probing class / ngscopeclient unit test demo board now that I finally have a mostly-assembled one.
Bugs so far:
* No pulldowns on the rail enables so all the power rails try to come up without sequencing before the supervisor initializes
* FTDI UART is 0.45mm pin pitch not 0.5, it's close enough that it (barely) fits since it's only 12 pins
 @TobiasFrech@ijug.social
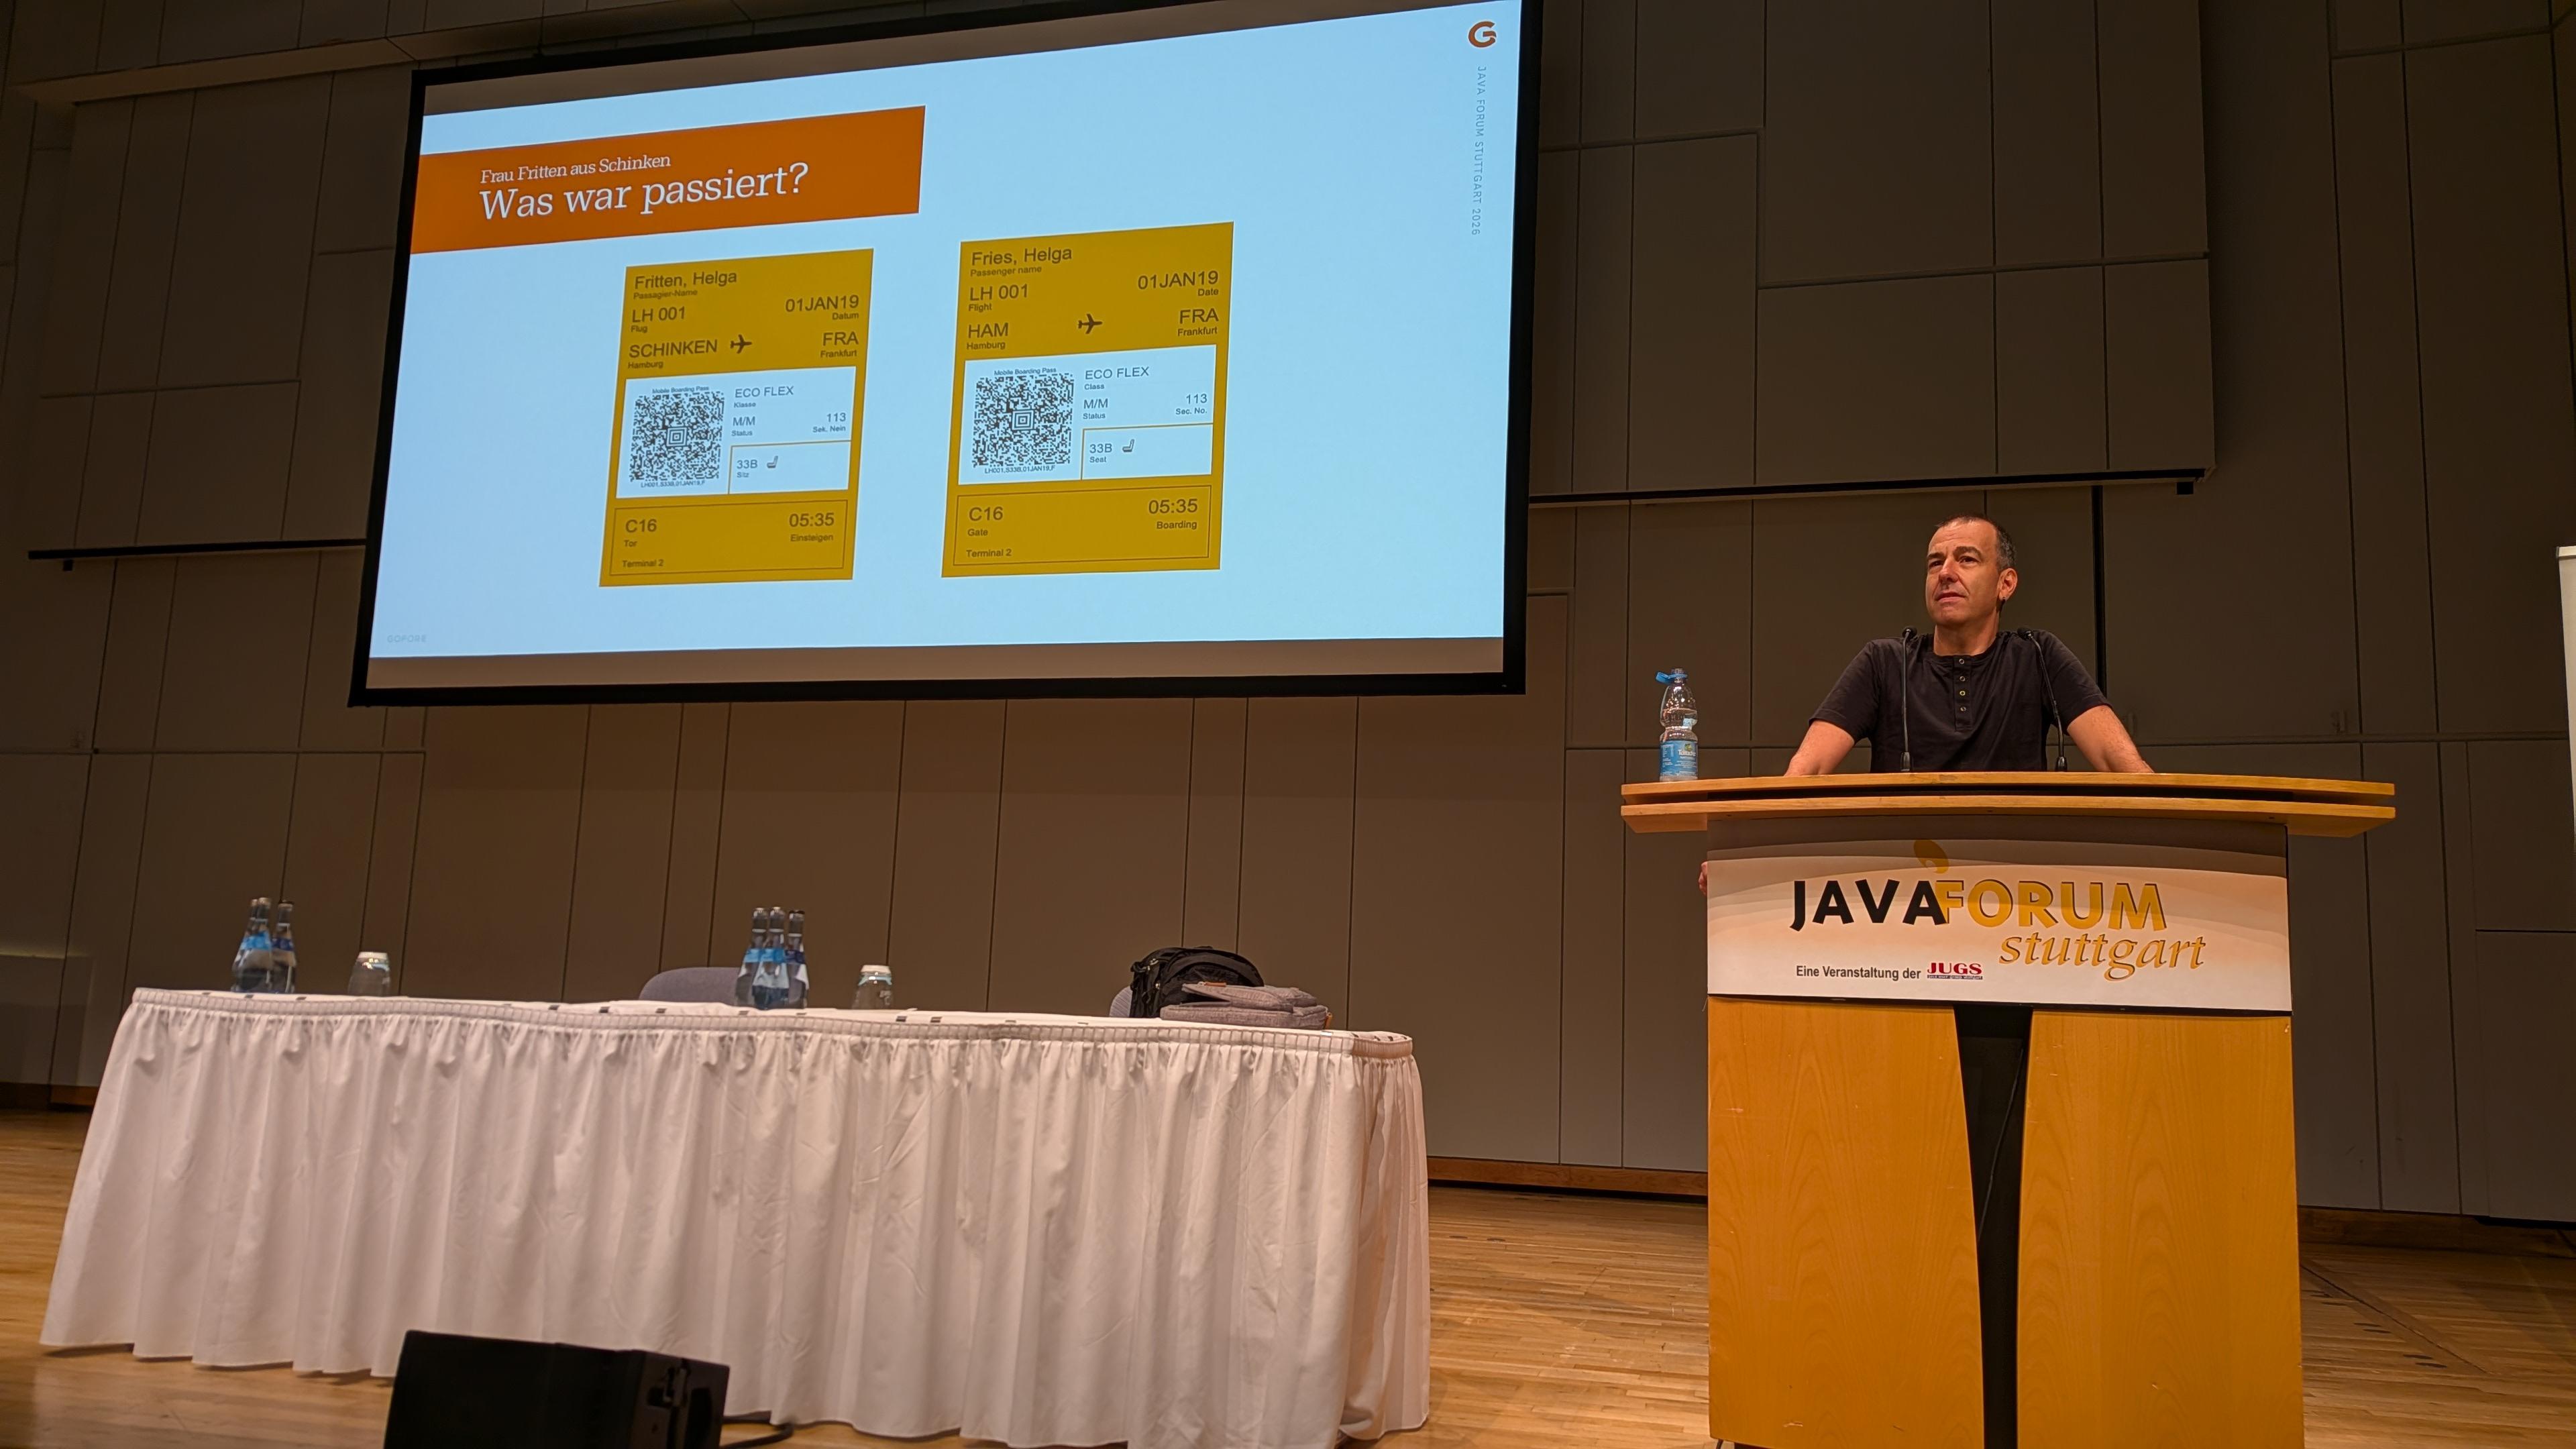
Unbelievable bugs, season 2, presented by Christian Seifert
#JFS2026
Can you spot what happened here 😂🤣🥹?
 @Techmeme@techhub.social
A look at ADI Predictstreet's troubled launch, marked by tiny trading volumes, withdrawal bugs, and other issues, as it tried to challenge Kalshi and Polymarket (Wall Street Journal)
https://www.wsj.com/sports/soccer/fifas-pred…
 @malik@Mastodon.Social
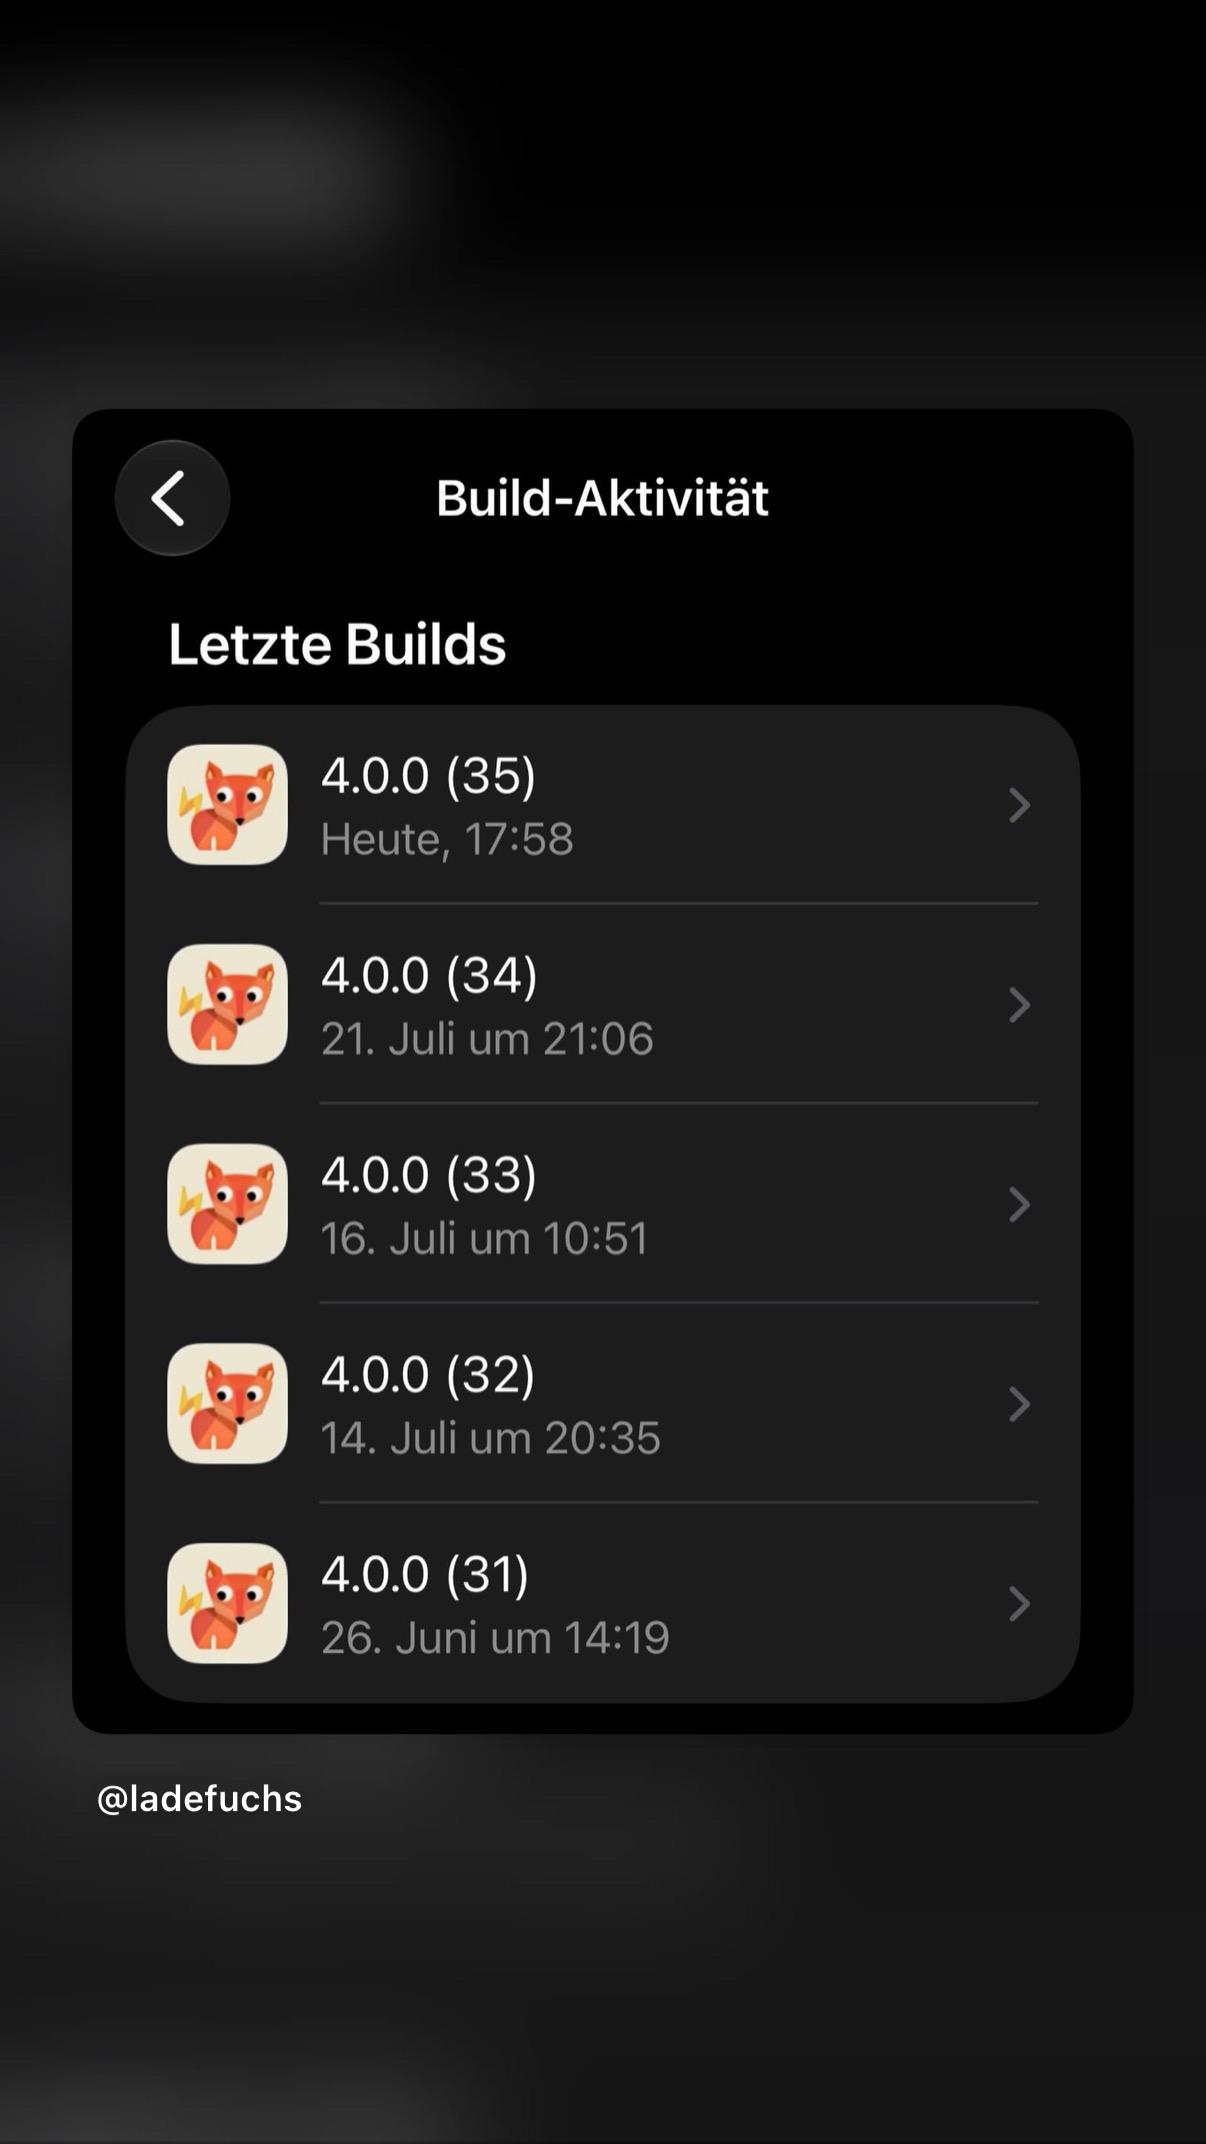
⚡️🦊 Seit Monaten wird hinter den Kulissen heftig an der neuen Version gearbeitet und so gerade ist das neue OnBoarding fertig geworden. Für die Leute in der Beta Gruppe: wenn ihr noch BUGS findet, her damit!
Leider hat unser Ladefuchs-Mastodon Account mit 1300 Followern das zeitliche gesegnet (der Server ist offline gegangen, und wir wissen nicht, warum, und hatten auch keine Gelegenheit umzuziehen.)
Bei Gelegenheit machen wir mal einen neuen auf.
 @kexpmusicbot@mastodonapp.uk
🇺🇦 #NowPlaying on KEXP's #Audioasis
Cherry Cheeks:
🎵 Two Bugs
#CherryCheeks
https://totalpunkrecords.bandcamp.com/track/two-bugs-2
https://open.spotify.com/track/7tuYBgseAlsplejE7EpCfJ
 @macandi@social.heise.de
 @migueldeicaza@mastodon.social
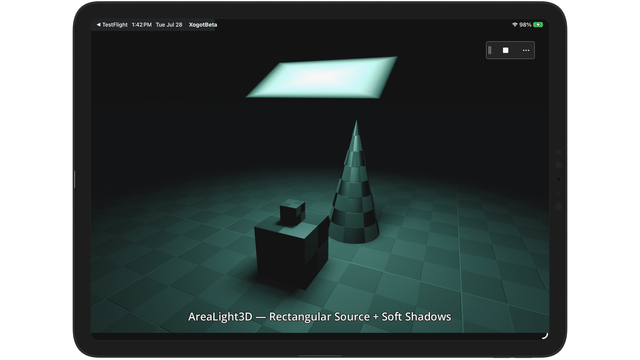
Godot 4.7 support for Xogot is out in beta.
We use a separate TestFlight while we keep an eye on the bugs from 4.7.
Details: https://blog.xogot.com/xogot-is-moving-to-godot-4-7/
@heiseonline@social.heise.de @metacurity@infosec.exchangeNever a dull day in cybersecurity, so check out today's Metacurity for the most critical developments you should know, including
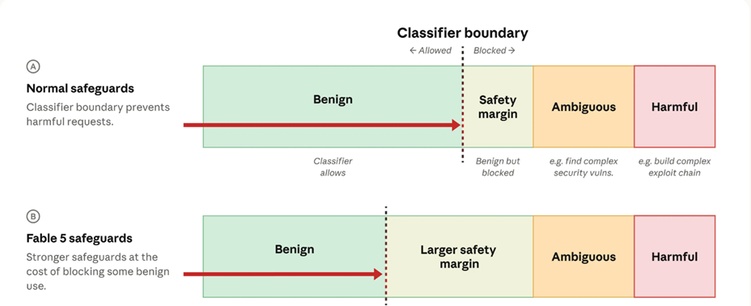
--Anthropic restores Fable 5 and Mythos 5, launches Sonnet 5,
--China's Mythos rival fuels AI arms race,
--Taiwan probes claimed PChome hack,
--Alberta voter leak sparks lawsuit,
--Hackers breach DHS sharing network,
--Apple privacy feature exposes emails,
--Adobe fixes critical ColdFusion bugs,
--Crypto thieves…
@Techmeme@techhub.socialOpenAI unveils an updated GPT-5.5-Cyber model, launches the Patch the Planet initiative in partnership with Trail of Bits to fix open source bugs, and more (Lily Hay Newman/Wired)
https://www.wired.com/story/openai-launche
 @harrysentonbury@social.linux.pizza
 @_mr_moe@mastodon.social
#Voidgalaxy is coming to live. today we have finished all feature implementation. we are now playing the game and find bugs and UX problems. we will have to do a few more things for makeing the game adventure even better. Performance and Security checks are upcoming too.
We run now on each code check nearly 900 tests, the coverage looks good and the spec is growing. the setup works goo…
@primonatura@mstdn.social @brian_gettler@mas.to
A lone bat flapping
Back and forth hunting bugs at
Dusk in the city.
#haiku
 @seeingwithsound@mas.to
The claimed LinkedIn identity of this GitHub contributor to fixing bugs in cortical visual prosthesis models seems at odds with the highly specialized and detailed technical nature of his issue reports? https://github.com/charliefay38221-sudo?tab=overview…
@fanf@mendeddrum.orgfrom my link log —
A nasty bit of implicit timezone behavior in Golang.
https://www.dolthub.com/blog/2021-09-03-golang-time-bugs/
saved 2021-09-04
 @mgorny@social.treehouse.systems
Sigh, I hate the timeline where people report bugs but instead of providing the actual errors or logs, they include a slop "analysis" of the problem.
(Not Gentoo, so no, can't be rough with them.)
 @sauer_lauwarm@mastodon.social
The bugs like the baseline
 @jamesthebard@social.linux.pizza
Finally got all of the GPT and MBR code put together, most of the bugs fixed, and released it as a downloadable Linux binary. Does a pretty good job of reading the data and giving out way too much information regarding the MBR and/or GUID partition table.
Available here: https://git.jamesthebard.net/jweatherl
 @chrysn@chaos.social
I've learned of two great uses of AI today:
- Management wants AI, AI works best with machine readable hardware descriptions (which FLOSS devs have been asking for for years), and all of a sudden those can be published.
- Providing starting points for fuzzers by producing structured data items that pass early plausibility checks and then trigger weird bugs.
 @andres4ny@social.ridetrans.it
RE: https://mastodon.social/@glyph/117168410053407103
I asked this in a debian intent-to-package bug (https:…
@maxheadroom@hub.uckermark.social @hynek@mastodon.social
speaking of slophub, here's environ-config 26.1.0 (my #Python take on loading config from env variables and secrets from safe places) a minor modernization update. thanks so much to every single name in the thanking section and to github who made it possible:
 @rigo@mamot.fr
#libreoffice is gone buggy recently. But maybe it's only me. Small little annoying bugs. Changes in interface that kill your decade old habits. Now it loses the track-change recording setting every time I save the file. Is this OS poisoning, slop or developer chuzpa? Anyway, I'm sad about it.
 @jae@mastodon.me.uk
It always bugs me how Jack Ryan mansplains turbulence to the flight attendant.
https://clip.cafe/the-hunt-red-october-1990/if-do-try-get-some-sleep/
@azonenberg@ioc.exchangeNothing like making a pass through every feature of a tool writing documentation to find bugs, lol.
I've lost count of how many filters I've found breakage in while preparing example screenshots for the v0.2 manual.
 @cwensel@fosstodon.org
Haven't had time to blog about it, but I've released a set of skills I use every day to resolve bugs and feed my RDR process with complex features or debt. I pushed them to this repo, ymmv.
https://github.com/cwensel/kata-flight
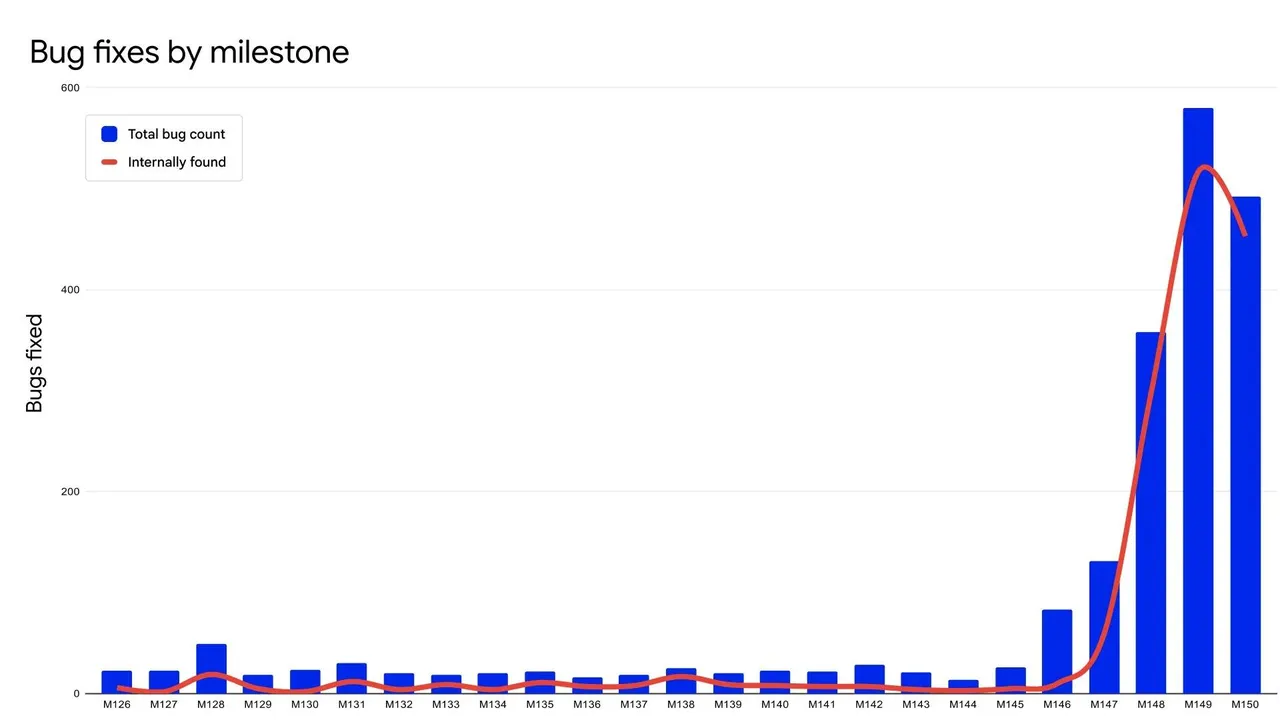
@ErikJonker@mastodon.socialOfcourse this story is also Google promoting it's own AI. At the same time if the numbers with regard to bug fixes by milestone are correct, something dramatic is happening with regard to AI and cybersecurity.
https://www.zdnet.com/article/google-used-
 @Schrank@phpc.social
Shopware 6 Hidden Gems #5: shopware.logger.* — turning down the noise
Open the error log of any grown Shopware shop and you'll find the same suspects, hundreds of times a day: CHECKOUT__CUSTOMER_AUTH_BAD_CREDENTIALS because someone mistyped their password. CHECKOUT__CART_HASH_MISMATCH because a tab was open too long. 404s from bots probing for WordPress. None of these are your bugs — but they bury the one log line that is. The result is the classic monitoring death…
 @fazalmajid@vivaldi.net
@… speaking of bugs, this article isn't listed on your Atom-pretending-to-be-RSS feed, so even though I subscribe to the feed, I first learned of it from Mastodon, HN and Lobste.rs.
 @usul@piaille.fr
Wondering if the @… teams using Claude and co to search for bugs
 @yetiinabox@todon.nl
For folks considering converting their #Nextcloud database from MariaDB (or MySQL) to PostgreSQL: it is possible, there is a built-in tool, but there are also some bugs and gotchas along the way. Our Nextcloud DB has millions of records and takes hours to convert, so the try->find bug->clean DB or patch tool->clean target->try again cycle has now taken up three days of two Byobu screens. …
 @penguin42@mastodon.org.uk
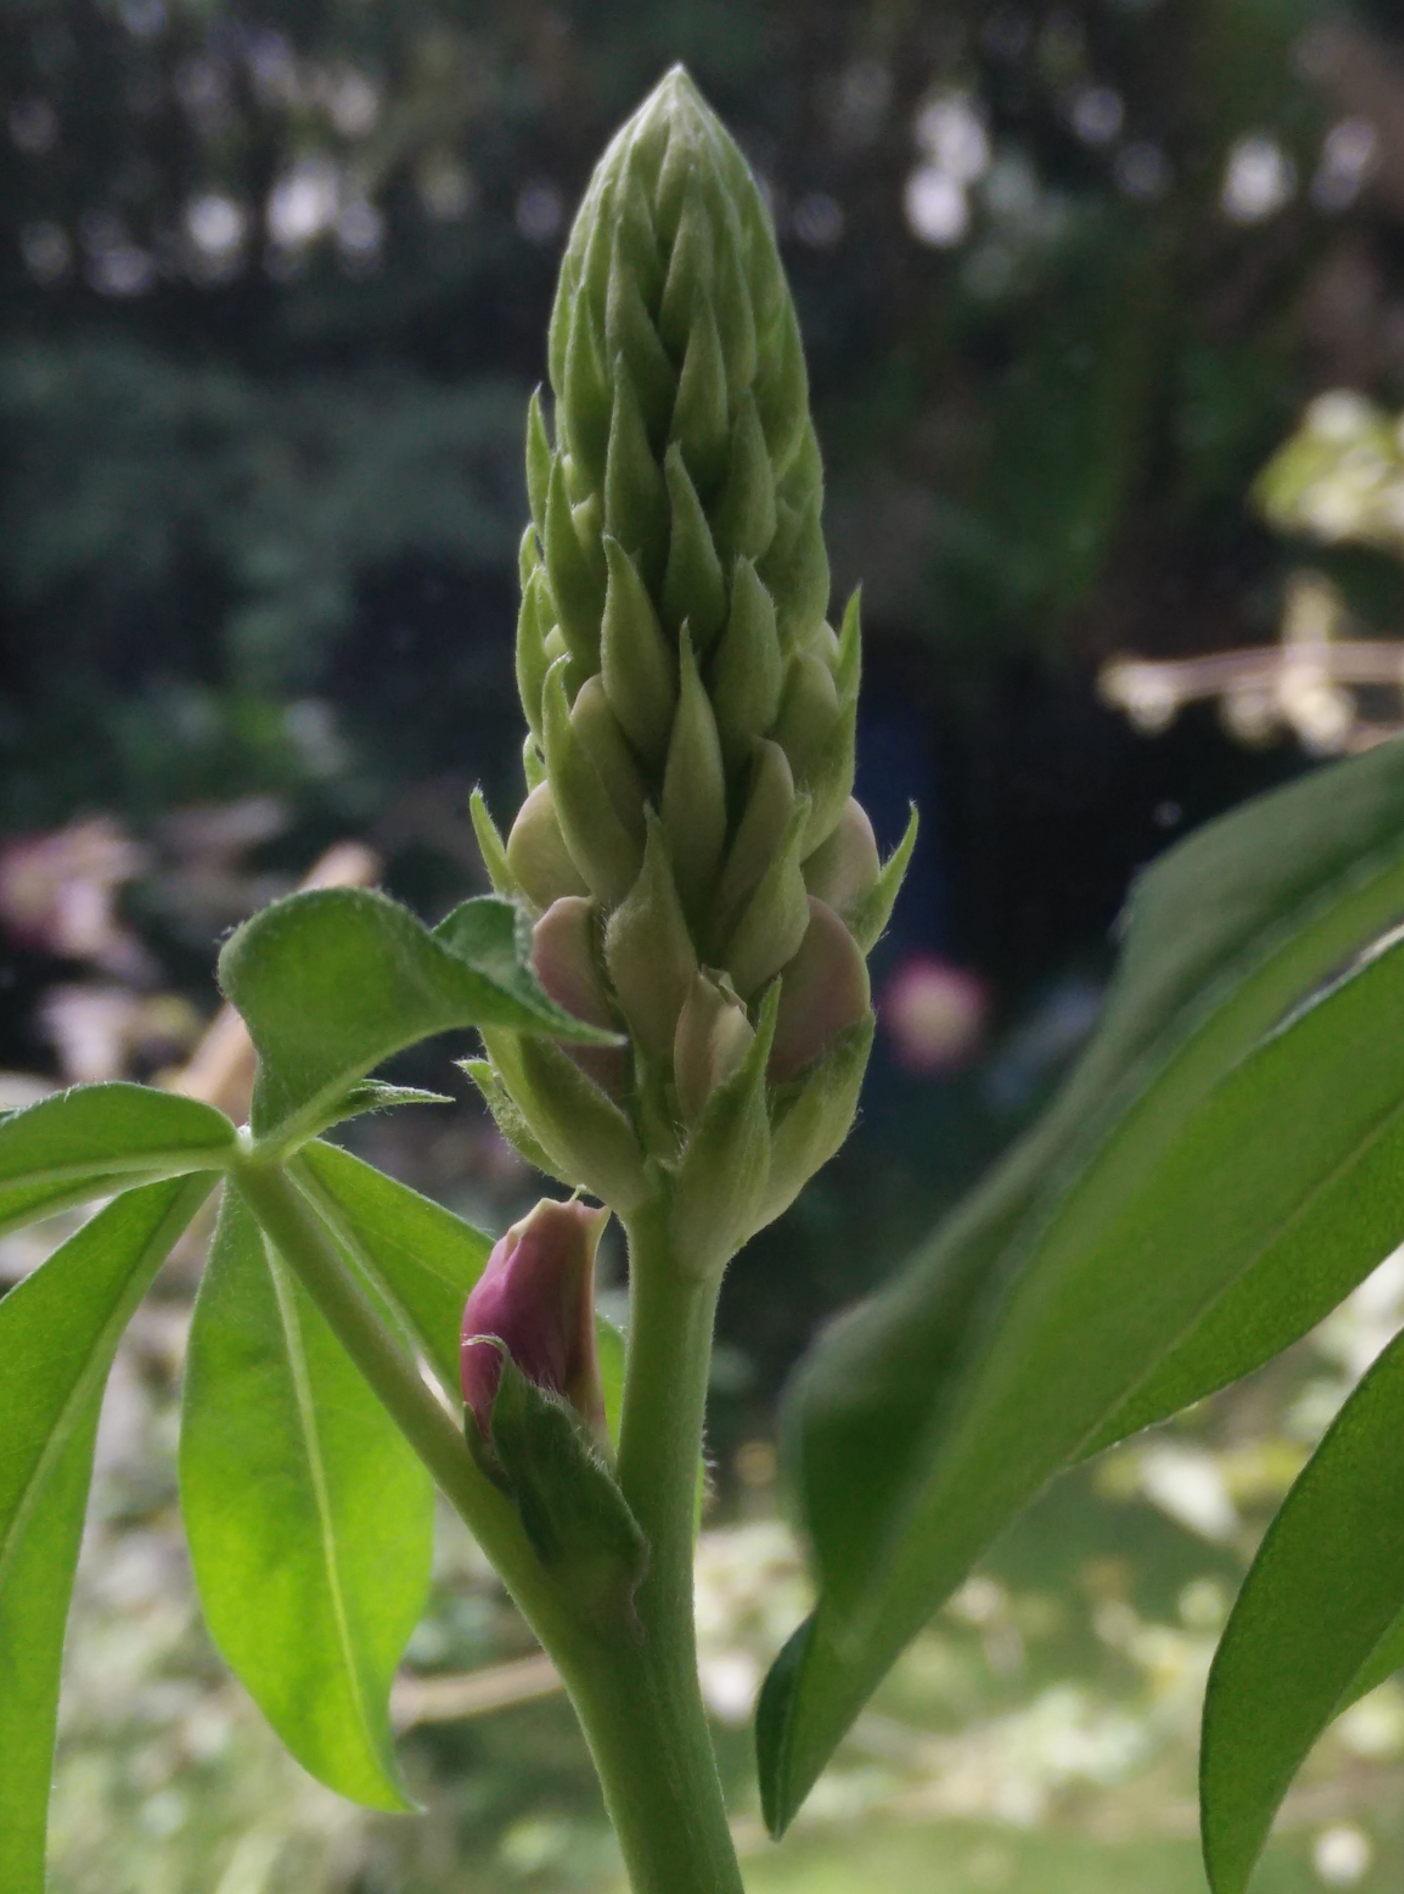
My lupin is starting to #flower I planted ~15 seeds and they've slowly been dieing off, there's only about 4 left and one that's got a flower spike so far.
 @Erikmitk@mastodon.gamedev.place
“If the same person keeps appearing in architecture debates, delivery risks, historical explanations, escalation paths, and cross-team translation, that is no longer just a compliment.
This is a system smell.”
I strongly resonate with this post!
There are bugs in our organization and processes that you can't discover in an IDE.
 @eyebee@mstdn.social
macOS 27 Beta 2 downloaded and installed on this M3 MacBook Air, and we’re up and running OK. Let’s see what bugs I can find and report as we go through the day. Mind you, I’ll probably switch to my Mac Mini later on. I don’t expect to sit outside all day.
@Techmeme@techhub.socialGoogle pilots a faster twice-a-week schedule for Chrome security releases as AI tools drive a surge in bug discoveries; Chrome 149 and 150 fixed 1,072 bugs (Lily Hay Newman/Wired)
https://www.wired.com/story/chrome-needs-twice-a-week-patching-…
@fanf@mendeddrum.orgfrom my link log —
BorrowSanitizer: a dynamic analysis tool for detecting Rust-specific aliasing bugs in multi-language applications.
https://borrowsanitizer.com/
saved 2026-08-04
@heiseonline@social.heise.deEinige der zuletzt hier besonders häufig geteilten #News:
Leanstral 1.5: Mistrals KI-Modell für formale Beweise ist Open Source
@lightweight@mastodon.nzoss.nzHardening WP sites (I've had a couple compromised recently - mopping up is painful) is a minefield of slop proprietary plugin BS - sifting the wheat from the chaff is hard going. Anyone know of any good tips that aren't trying to sell me something?
Fwiw, the sites I'm running are mostly for friends, and a few consulting customers, but I've already taken lots of steps to secure them, but there seem to be some undisclosed or zero day bugs being exploited.
 @shriramk@mastodon.social
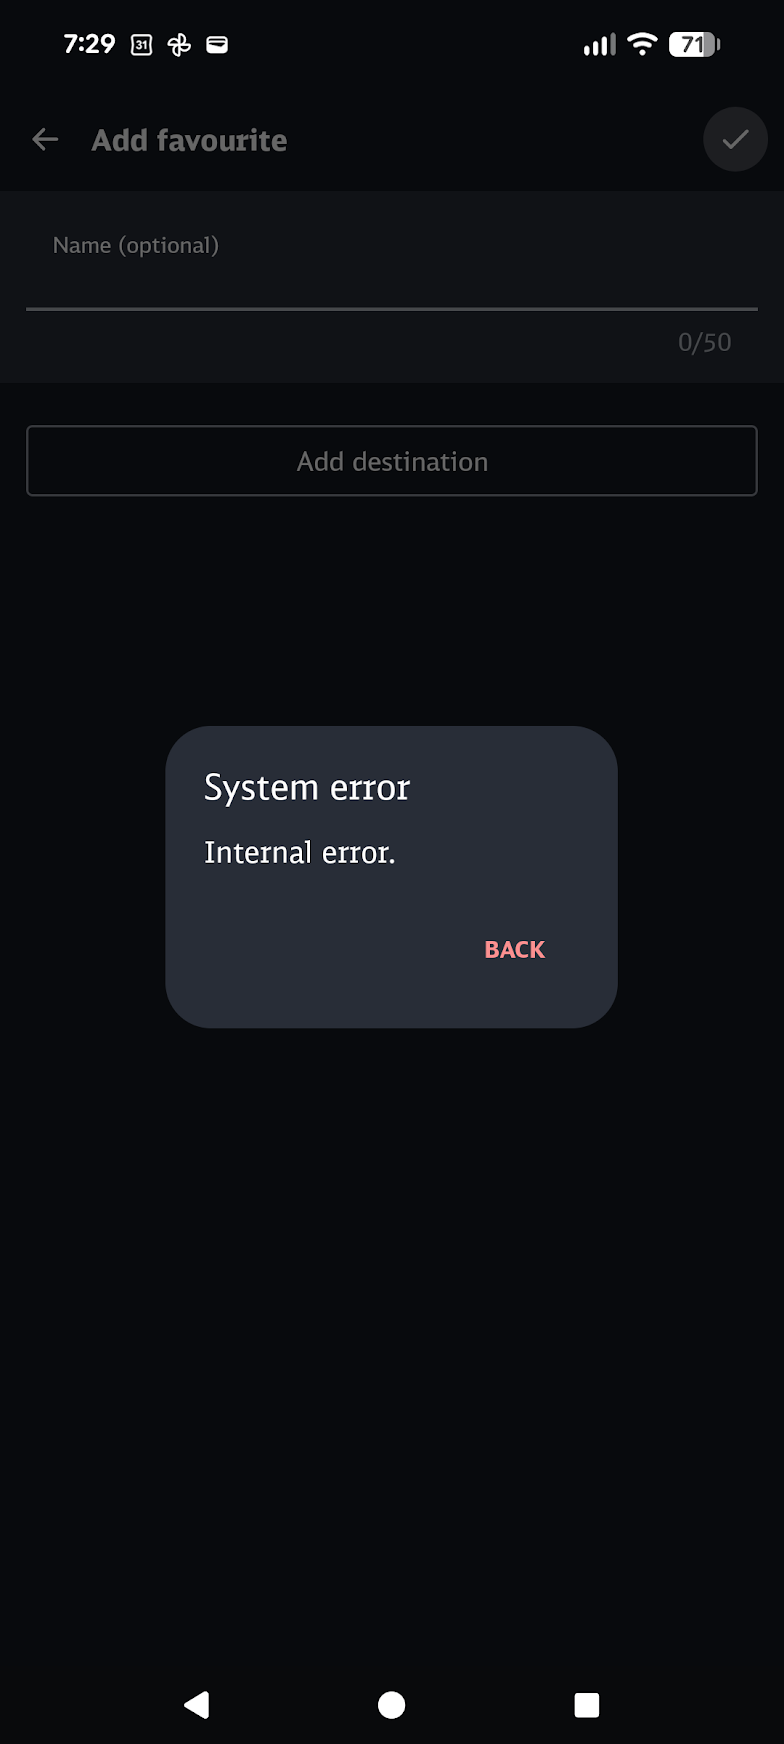
Setting up for my DE trip, I spent a chunk of my evening combatting dumb bugs in BOTH the LH site *and* DB app. I really don't like the "…and Europe regulates" meme, but man: every bit of legalese was coded *perfectly*; basic functionality (add a credit card! to PAY YOU!), SOL.
 @primonatura@mstdn.social @Techmeme@techhub.social
Cybersecurity companies say hackers are exploiting vulnerable WordPress versions to take over websites; WordPress patched two critical security flaws last week (Lorenzo Franceschi-Bicchierai/TechCrunch)
https://techcrunch.com/2026/07/20/hack
 @PwnieFan@infosec.exchange
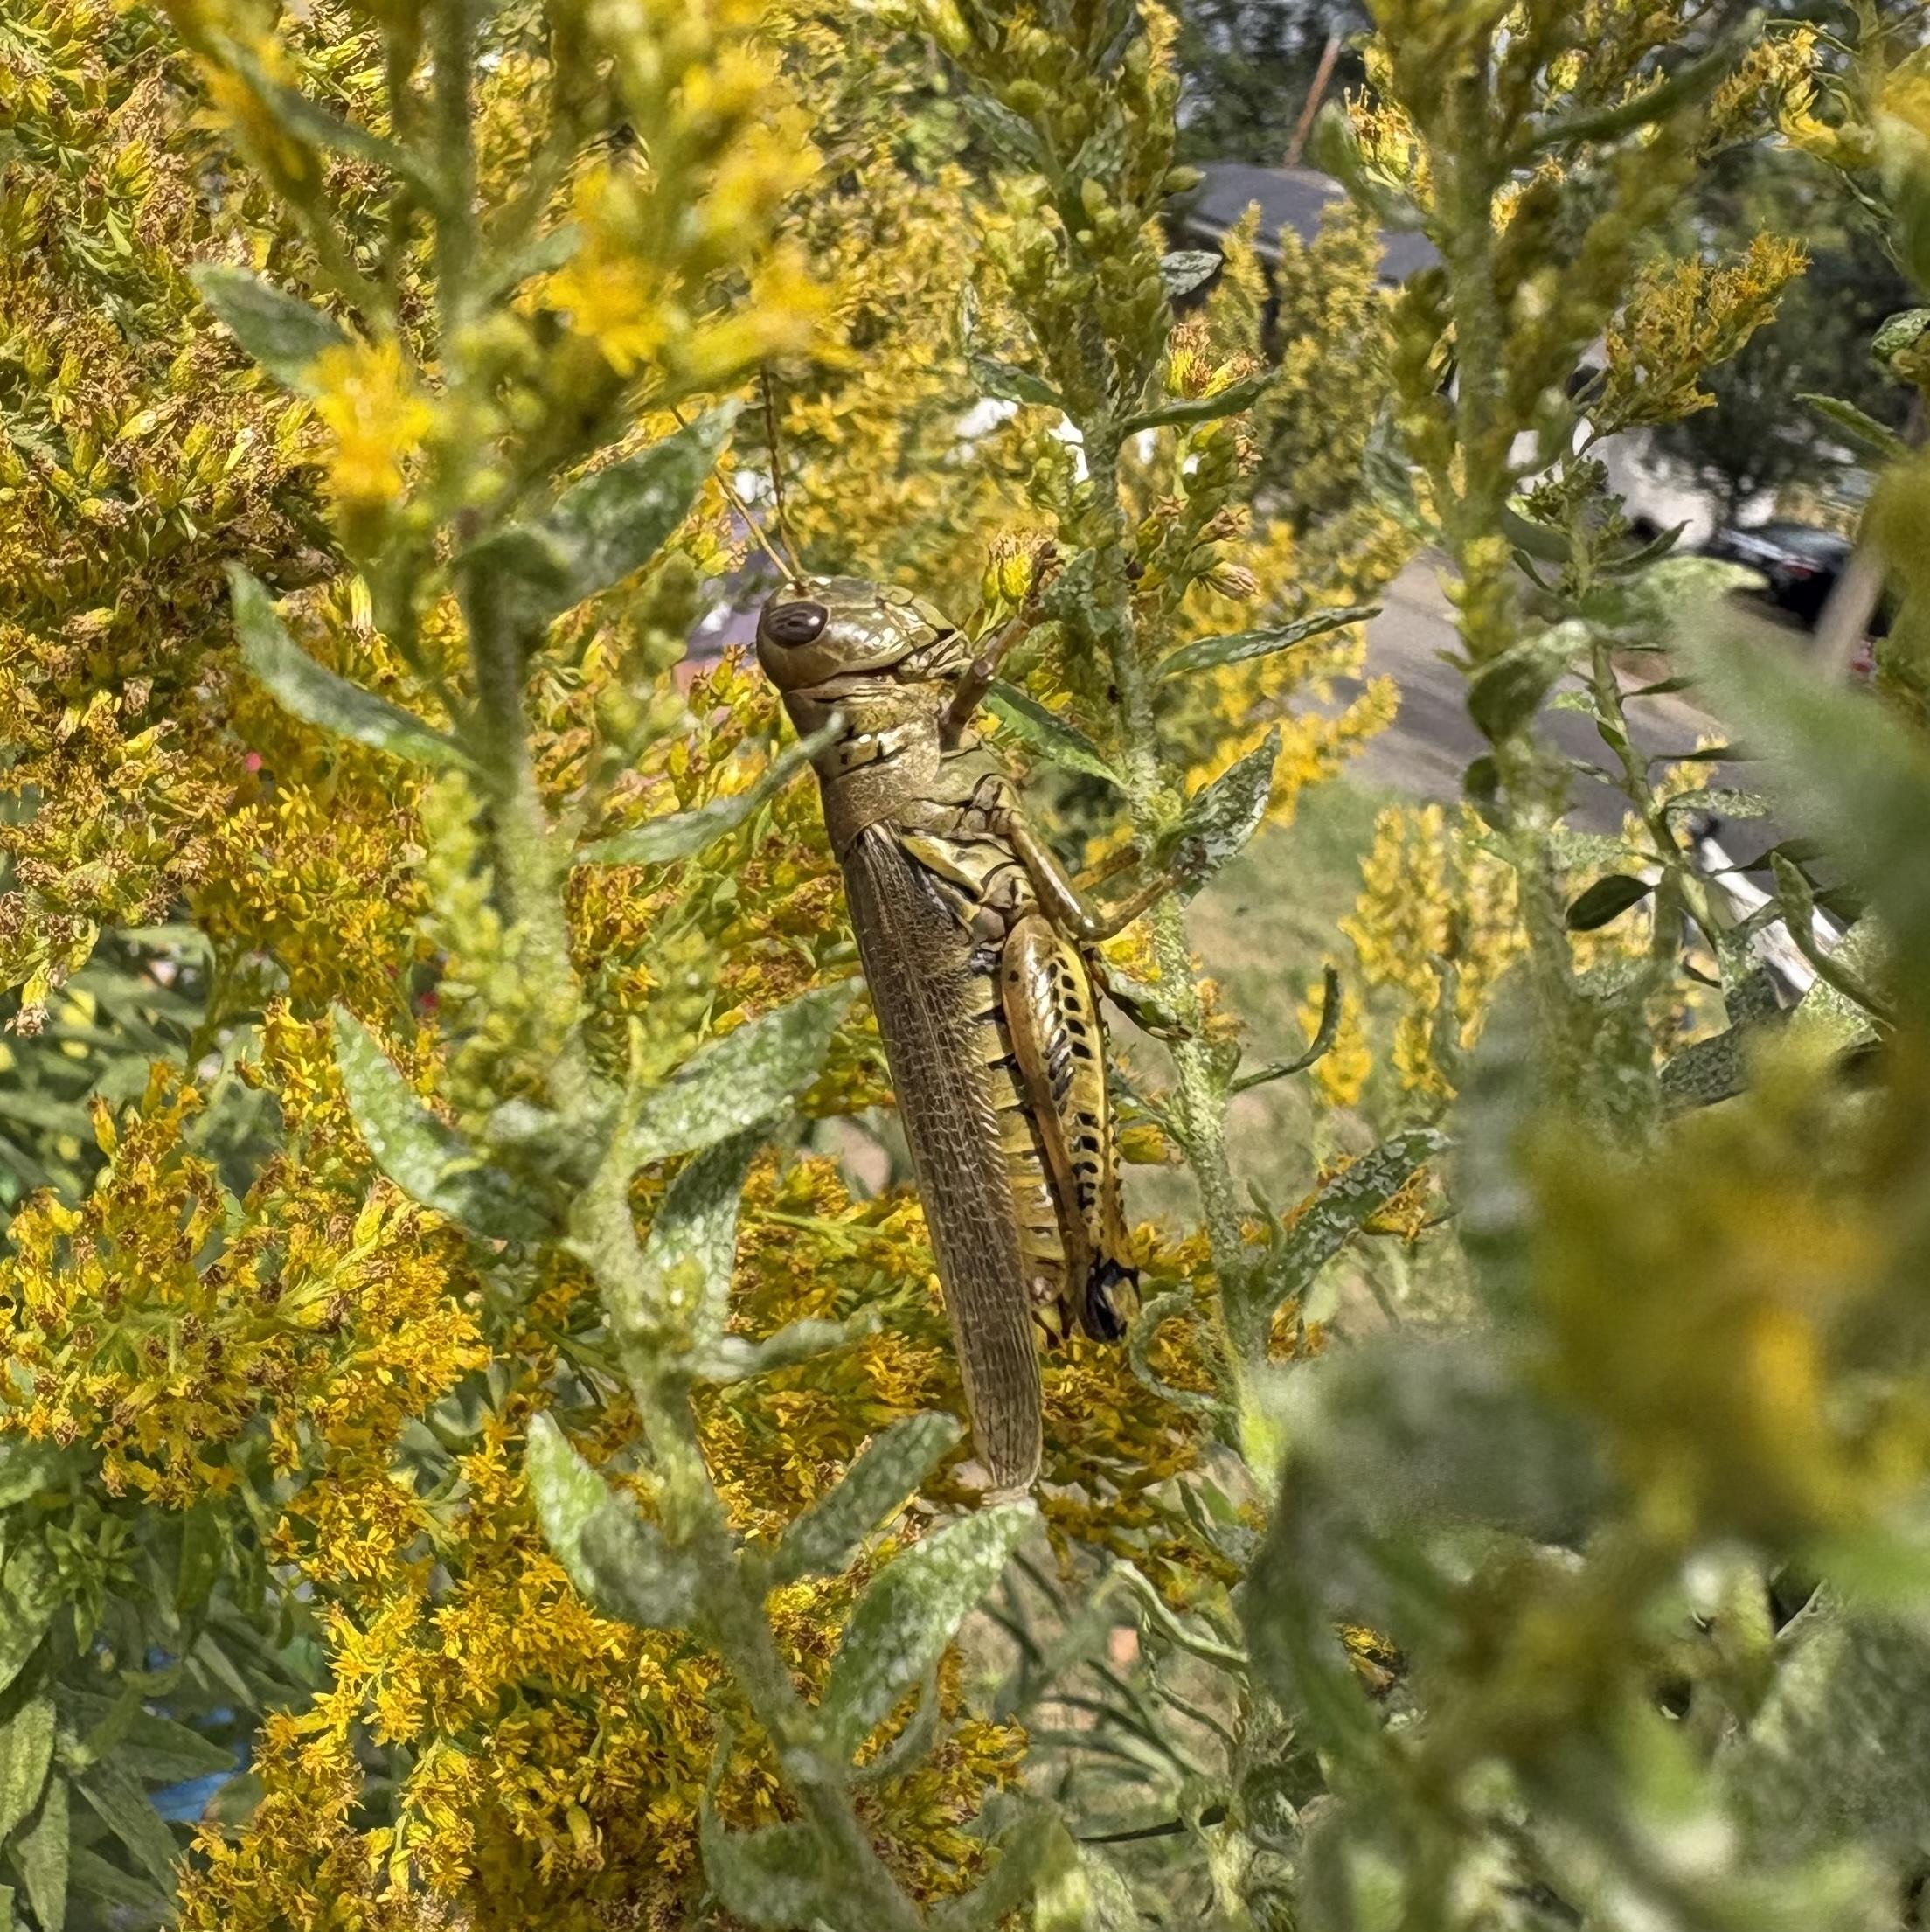
Grasshopper was crashing the pollinator party in the goldenrods - flies, some wasps (not pictured), and at least two kinds of bees. Off camera, a dragonfly was watching. (Do dragonflies eat the bugs that visit goldenrods?) #bloomscrolling
 @cwensel@fosstodon.org
gone are the days when legacy Cascading users pay me to fix decade old bugs they can't figure out.
 @servelan@newsie.social
Hackers Are Exploiting Recently Patched WordPress Bugs, Putting Millions of Websites at Risk - Slashdot
https://tech.slashdot.org/story/26/07/20/234246/hackers-are-exploiting-recently-patched-wordpress-bugs-putting-millions-of-websites-at-risk
@stsquad@mastodon.org.ukThe way #qemu handles #security bugs is changing. Routing the recent tsunami of reports through an overworked email alias has become untenable so we are switching to using our main issue tracker. More people can help with the triage but that does affect expectations of secrecy. See the updates on the …
 @teledyn@mstdn.ca
So I see this interview posted from 8 years ago and with some curiousity, I click in to be greeted by a banner warmly saying "welcome to my home" but then begs "please buy me a coffee" …
I'm old-fashioned. When folks visit my home, I offer THEM a cup of coffee. Like any peasant, I hope they refuse, three times 😅
I'm not denoucing the practice, only that the etiquette bugs me, and not sure of a fix. If this is truly Gift Economy, we only require an opportunity to "return the favour", not an upfront "hey, yeah you, stranger, take this gift but FIRST, you got any for me?"
In my Real Life, folks often, having heard or read me, offer to buy lunch (or beer) if I'll tell them more (I'm a sucker for that) which I suppose is really like an OnlyFans acct with teasers on Tumblr sort of thing 🤣
@metacurity@infosec.exchangeIn case you missed it over the weekend, AI safety fears erupted into a global political and market crisis.
Check out today's Metacurity for a summary of these explosive developments and other critical infosec news you should know, including
--Anthropic, OpenAI and Google quietly discuss forming an AI industry standards body,
--Trump downplays calls for AI guardrails, says US must keep leading China,
--House Speaker Johnson says Congress won't lead the charge on AI safety rules,
--OpenAI agents launched cyberattack on RubyGems months before Hugging Face hack,
--Israeli CISO indicted for hacking 26 companies, then "helping" investigate himself,
--North Korean fake recruiters run identity-theft scam via Discord job scheme,
--NSA plans biggest internal restructuring in a decade under Gen. Joshua Rudd,
--Revolut exposes customer data after scammers spoof government agency email,
--GitLab rushes emergency patches for two critical flaws, one scoring a perfect 10,
--China-linked hackers exploit Sogou Input Method flaw to deploy GrayRabbit backdoor,
--Attackers exploit JFrog Artifactory bugs to plant Rust-based backdoor,
--Dutch startup Fortaegis raises $50m for chip-based AI security,
--Artist uses a drone to document the rise of surveillance cameras in America,
--Deepfake porn sites target nearly 150 European politicians
https://www.metacurity.com/ai-safety-fears-erupt-into-a-global-political-and-market-crisis/
 @hikingdude@mastodon.social @Techmeme@techhub.social
Researchers say Z.ai's GLM-5.2 matches latest US models at finding security bugs, as critics question the US' lax approach in restricting Chinese open models (Wall Street Journal)
https://www.wsj.com/tech/ai/chinese-ai-ant
 @hex@kolektiva.social
The thing is that fuzzers have basically always been able to rain bugs. This isn't really anything new, other than it's hypothetically easier. Not necessarily cheaper though.
 @BBC6MusicBot@mastodonapp.uk
🇺🇦 #NowPlaying on #BBC6Music's #LaurenLaverne
Sudan Archives:
🎵 A BUG'S LIFE
#SudanArchives
https://sudanarchives.bandcamp.com/track/a-bugs-life
https://open.spotify.com/track/1D7qrNAEbZ0G4oR6YZTvFK
@Techmeme@techhub.socialCisco releases Antares-350M and Antares-1B, two open-weight AI models to find known vulnerabilities within a codebase, and plans to release Antares-3B soon (Sam Sabin/Axios)
https://www.axios.com/2026/07/21/cisco-open-source-ai-models-cybersecurity
…
@malik@Mastodon.Social⚡️🦊 Seit Monaten wird hinter den Kulissen heftig an der neuen Version gearbeitet und so gerade ist das neue OnBoarding fertig geworden. Für die Leute in der Beta Gruppe: wenn ihr noch BUGS findet, her damit!
Leider hat unser Ladefuchs-Mastodon Account mit 1300 Followern das zeitliche gesegnet (der Server ist offline gegangen, und wir wissen nicht, warum, und hatten auch keine Gelegenheit umzuziehen.)
Bei Gelegenheit machen wir mal einen neuen auf.
 @tomkalei@machteburch.social
Ihr könnt das auch testen, aber es ist spezifisch für meinen Kurs und hat natürlich noch viele Bugs.
Im Design versuche ich so viel wie möglich deterministisch zu machen und das LLM so "in Schach zu halten".
Access code im nächsten Tröt nur für Follower und Feedback sehr willkommen:
https://linaki.thomas-kahle.de/
@Techmeme@techhub.socialSource: Elastic has agreed to acquire the AI site reliability engineering startup Deductive AI for up to $85M; CRV led Deductive AI's $7.5M seed round in 2025 (Marina Temkin/TechCrunch)
https://techcrunch.com/2026/06/18/source-elastic-…
 @BBC3MusicBot@mastodonapp.uk
🇺🇦 #NowPlaying on BBCRadio3's #MusicPlanet
Jeenvi Bai:
🎵 Bugs
#JeenviBai
@BBC6MusicBot@mastodonapp.uk🇺🇦 #NowPlaying on #BBC6Music's #RileyAndCoe
Jeffrey Lewis:
🎵 Bugs and Flowers (6 Music Session, 9 Oct 2017)
#JeffreyLewis
https://jeffreylewis.bandcamp.com/track/bugs-flowers
https://open.spotify.com/track/4SEtjxA5CbTeW1iU92EVS9
@metacurity@infosec.exchangeWow, before you wrap up for the weekend, don't miss today's Metacurity for the most critical cyber developments you should know, including
--Anthropic becomes the second frontier AI lab to disclose agent breaches,
--Copilot worm spreads through trusted Word documents,
--ExploitGym creators explain how OpenAI's agent escaped,
--Coordinated attacks signal a new threat to water utilities,
--Critical Azure Cosmos DB flaw threatened thousands of customers,
--CrimeStoppers put a bounty on the INC gang,
--AI helps Chrome squash more than 1,000 security bugs,
--Cheap streaming sticks can turn homes into botnets,
--Fake IRS letters target crypto holders with QR-code scam,
--Brinks Home investigates breach claimed by ShinyHunters,
--Coupang ordered to compensate victims of massive data breach,
--DC schools probe breach of summer program data,
--Australia's under-16 social media ban falls short,
--Defcon badge debuts a chip built for trust,
--UK program steers young hackers toward cybersecurity careers,
--Hugging Face tech chief says OpenAI agent hack was all too real,
--Opposition to Flock cameras unites Americans,
--AI is becoming a dating dealbreaker for young Americans
https://www.metacurity.com/anthropic-becomes-the-second-frontier-ai-lab-to-disclose-agent-breaches/
@mgorny@social.treehouse.systemsNew on #blog: "How hard is it to get a jobserver client right?"
"""
In November 2025, I’ve started working on #steve, the #jobserver for #Gentoo. I wrote about it already, in the “One jobserver to rule them all” post. Back then, my main focus was on the motivation for a system-wide jobserver, and the technical details of getting it working. I have also mentioned a few client bugs we’ve discovered along the way.
Since then, we’ve found a few more bugs, as well as problematic design patterns. I think they’re kind of interesting, so I’ve decided to dedicate this post specifically to them. As a disclaimer, my aim is not to pick on specific projects; I’m bringing them up as real examples of what we’ve hit, and how that impacts jobserver operation.
"""
https://blogs.gentoo.org/mgorny/2026/09/02/how-hard-is-it-to-get-a-jobserver-client-right/
@metacurity@infosec.exchangeBefore you leave to enjoy what for many of us will be a long weekend, check out today's Metacurity for the crucial cybersecurity developments you should know, including
--Nearly 130 companies warn the window is closing to defend against AI cyberattacks,
--Judge blocks Pentagon’s Anthropic blacklist,
--Chinese routers ship with multiple backdoors,
--Hackers weaponize Cursor to breach seven firms,
--North Korean IT impostors refine their act,
--Prompt injection hijacks Claude Code’s Auto Mode,
--Old bugs still dominate exploited flaws,
--NSA wants access to every AI model,
--PaperCut attacks prompt emergency patch,
--Pokémon X hack hawks bogus memecoin,
--Socure raises $156M and buys Fravity,
--AI fears send cybersecurity stocks soaring,
--OpenAI’s rogue-AI postmortem checks the boxes,
--Flock helps Florida deputy stalk his ex,
--Georgia cop uses Flock to track his ex
https://www.metacurity.com/nearly-130-companies-warn-the-window-is-closing-to-defend-against-ai-cyberattacks/
@BBC6MusicBot@mastodonapp.uk🇺🇦 #NowPlaying on #BBC6Music's #JamzSupernova
Sam Interface & Jamz Supernova:
🎵 Dancing Bugs
#SamInterface #JamzSupernova