 @macandi@social.heise.de
2026-08-14 14:36:03
@macandi@social.heise.de @primonatura@mstdn.social
 @azonenberg@ioc.exchange
Found a bug in the ThunderScope driver in ngscopeclient v0.2 that could lead to GPU memory leaks in some cases. Will probably be shipping a hotfix v0.2.1 release soon just to get this fix out there officially.
 @aardrian@toot.cafe
Anyone know when the VA pulled its component library?
I was checking a breadcrumb accessibility fix that I linked from a 2023 USWDS bug I filed:
https://github.com/uswds/uswds/issues/5463#issuecomment-2188640853
And the VA appears to have wiped it all…
 @samvarma@fosstodon.org
Running into an #ios27 (27.0.1) bug in the Camera app. Have the default set to main cam at 1.5x (35mm), but it launches into 1x (24mm) every time regardless. Persists after power cycle. Any thoughts?
#iPhone18Pro
 @jdrm@social.linux.pizza
- Dios mío, hacednos casito porque hemos hecho una IA que podría matarnos a todos
- ¿Eso es un bug o una feature?
- ...
- ...
 @fanf@mendeddrum.org
from my link log —
Bug bounty platforms buy researcher silence and violate labor and privacy laws.
https://www.csoonline.com/article/3535888/bug-bounty-platforms-buy-researcher-silence-violate-labor-laws-critics-…
 @cowboys@darktundra.xyz
Cowboys Headlines: More players out with illness; roster moves; can Pettine fix defense? https://cowboyswire.usatoday.com/story/sports/nfl/cowboys/2026/10/13/news-headlines…
 @fortune@social.linux.pizza
System going down at 5 this afternoon to install scheduler bug.
 @stsquad@mastodon.org.uk
 @ruario@vivaldi.net
@… Ok, I know the bug and we fixed it within 24 hours, so you probably did not need to do any of that FWIW. 😉
Also, just so you are aware /opt/vivaldi/update-widevine has not existed since 2021, so your rm command would not have done anything to that.
Also If you ever want to disable the update-ffmpeg from being called on startup for some reason (like this) just …
 @heiseonline@social.heise.de
 @beoz@det.social
 @penguin42@mastodon.org.uk
Git at least encourages useful commit messages. I think I've just fixed a bug (in my code) I've been chasing for ~2 weeks - turns out I really did need to add a copy of that other loop which I don't understand it's purpose of; alas it's 20 year old with CVS tags with no useful commit message.
 @rasterweb@mastodon.social
➡️ Image Not Found — Art as Action
#bookmarks
 @macandi@social.heise.de
Download-Bug gefxit: iOS und iPadOS 26.6.2 verfügbar
Apple hat ein neuerliches Update für den Jahrgang 26 seiner Systeme für iPhone und iPad veröffentlicht. Die kompakte Aktualisierung behebt ein Problem.
https://www.
 @Techmeme@techhub.social
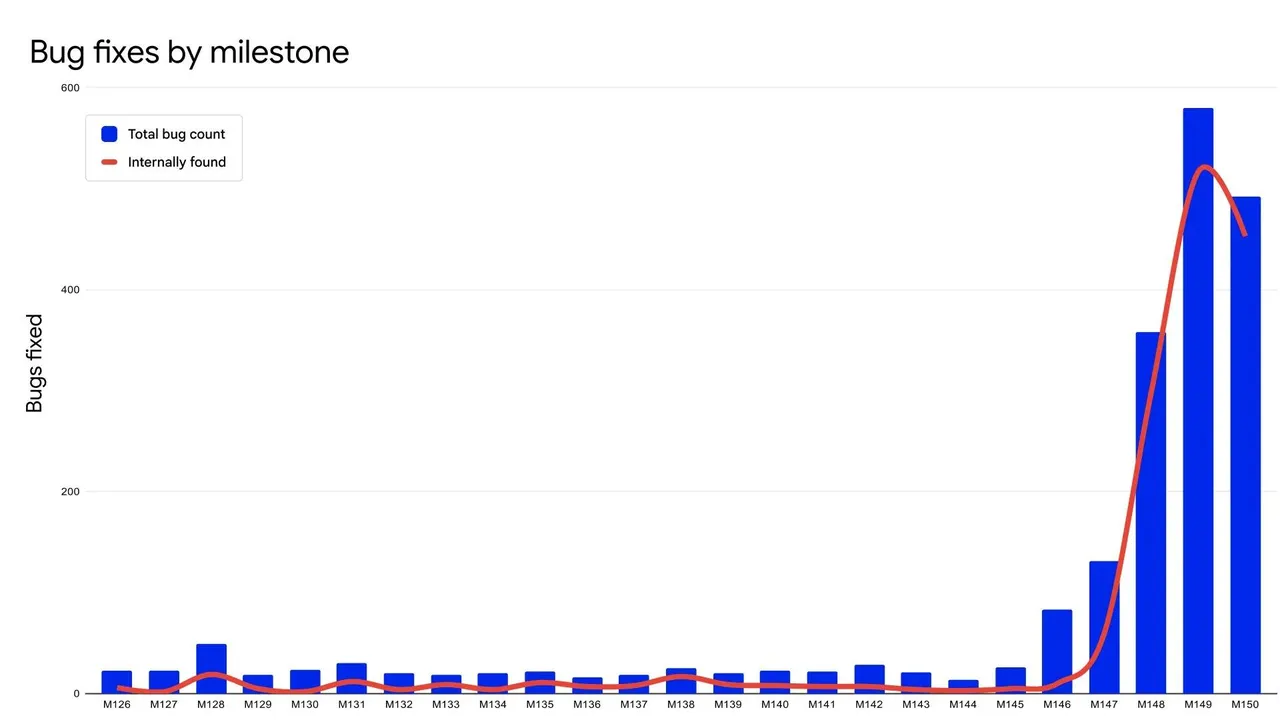
Google pilots a faster twice-a-week schedule for Chrome security releases as AI tools drive a surge in bug discoveries; Chrome 149 and 150 fixed 1,072 bugs (Lily Hay Newman/Wired)
https://www.wired.com/story/chrome-needs-twice-a-week-patching-…
 @aral@mastodon.ar.al
Turns out WebKit cannot store a non-extractable X25519 CryptoKey in IndexedDB.
Kind of a big deal for security/privacy.
If you know anyone at Apple/on the WebKit team, please nudge them about this.
https://bugs.webkit.org/show_bug.cgi?id=312279
@beoz@det.social @niqdanger@social.linux.pizza
Well now, this probably explains my issue the with the "7.2" kernels on Fedora 44 I was having. The latest update the other day (Yesterday?) fixed it. Reboot and GDM shows right up. https://gadgetsnow.indiatimes.com/tech
 @wrog@mastodon.murkworks.net
So, it seems LLMs are really good at generating test cases, that *this* at least is one application they're ideally suited for.
Clearly, the question of whether something is a bug has pretty much *nothing* to do with how it was found, and finding the bug is better than NOT finding the bug.
That even if, say, it turns out that it was Jeffrey Epstein who found the bug, I should not care; it still goes on the list of things to fix.
But then I think about the pressure exper…
 @cheeaun@mastodon.social
(small) #PhanpySocial changelog ✨
🐛 Bug fixes
🔗 https://phanpy.social/
💬
 @neverpanic@chaos.social
Bug of the day: a deadlock between dlopen(3)'s lock and OPENSSL_init_crypto()'s lock when two threads load a new library and initialize #OpenSSL.
https://bugzilla.redhat.com/show_bug.c
 @jswright61@ruby.social
After a month away from coding, I have a new #LeftWordle release up at https://staging.left-wordle.com.
This release is mostly bug fixes. Detailed notes here:
 @lpryszcz@genomic.social @macandi@social.heise.de @Techmeme@techhub.social
Google freezes product flaw submissions to its OSS Vulnerability Reward Program over an influx of invalid AI-driven reports, plans an update by Q1 2027 (Etiido Uko/Tom's Hardware)
ht…
 @makeratschool@kanoa.de
Ich weiss ja auch nicht, aber wenn eines dieser Schließmuskelsymbole in der Liste der Contributer eines OSS Projektes für Home Automation auftaucht, dann werde ich nervös. Das ist z.B. das Repository der Firmware für Home Assistant Voice Preview Edition. Der Hardware Sprachassistent von Home Assistant als Alternative z.B. zu Google Home, dass ja bekanntlich einfach mal so die Funktion seiner Assistenten verändert. Weil du nur das Plastik kaufst, nicht die Funktion. Ist bei deinem Auto übrige…
 @philip@mastodon.mallegolhansen.com
@… @… My wife and I both found this on in the last couple of weeks.
Wat? Where did it come from? Did someone ship a bug in Music recently? (Wouldn’t be surprising of course).
 @grumpybozo@toad.social
Sometimes I run into a bug and it takes me a solid hour or more to convince myself that it’s a bug. I do not want to believe that someone made such a mistake…
https://github.com/freebsd/pkg/issues/2261 for example, has been “fixed” at least twice. but it’s still broken.
 @hynek@mastodon.social
The other day I was shocked that my favorite purveyor of hot sauces and OctoPrint maintainer extraordinaire @… was gone from my following list. Turns out her server had a bug and leisurely stripped her of a large swath of her mastodon.social followers. So if you think you follow her, double-check!
https://chaos.social/@foosel/116251218119152008
 @krone@frawas.de
Maroder Flugzeugträger - „USS Abraham Lincoln“ von Bug bis Heck verrostet #News #Nachrichten
 @Sythelux@social.tchncs.de
I'm working on KMUSuite/Corpostack and am trying it with a 8GB VM. Zulip takes up 3GB of RAM so I looked into the bug reports:
https://github.com/zulip/zulip/issues/12063
the last comment is gold:
"I'm going to close this 2019 issue, since the specific details …
 @paulwermer@sfba.social
RE: https://mastodon.online/@bug_gwen/117360488669173666
Well worth reading. We know what would mitigate many of the drivers, but will we ensure we take action?
Hope this gets taken up by the news media, because too many people won't read the a…
@PaulWermer@sfba.socialRE: https://mastodon.online/@bug_gwen/117360488669173666
Well worth reading. We know what would mitigate many of the drivers, but will we ensure we take action?
Hope this gets taken up by the news media, because too many people won't read the a…
@fortune@social.linux.pizzaThe bug starts here.
 @NFL@darktundra.xyz
NFL Power Rankings, Week 1: Cowboys rising after defensive makeover; Bears drop out of top 10 https://www.nfl.com/news/nfl-power-rankings-week-1-2026-nfl-season
 @publicvoit@graz.social
 @elduvelle@neuromatch.social
Hi @… :)
Just wanted to point out a possible bug: when I have a vivaldi window with lots of tabs open, and I go on Workspace> new workspace, it creates a new window that is empty with the new workspace name ... But it closes the window that I already had open! So I loose all my tabs there 😬
I hadn't noticed t…
@stsquad@mastodon.org.ukHere is another in a series of attempts to divine information from #qemu's issue tracker. I think this is showing that #AI #bugpocolypse reports tend to be verbose, a lot of sanitizer reports are proba…

 @ErikJonker@mastodon.social
Ofcourse this story is also Google promoting it's own AI. At the same time if the numbers with regard to bug fixes by milestone are correct, something dramatic is happening with regard to AI and cybersecurity.
https://www.zdnet.com/article/google-used-
 @andres4ny@social.ridetrans.it
RE: https://mastodon.social/@glyph/117168410053407103
I asked this in a debian intent-to-package bug (https:…
 @padraig@mastodon.ie
@…
I cannot load the ‘For You’ tab and ‘Following’ tab. It just shows this message.
Additionally hashtags in bios don’t work.
iOS 27 Beta 8
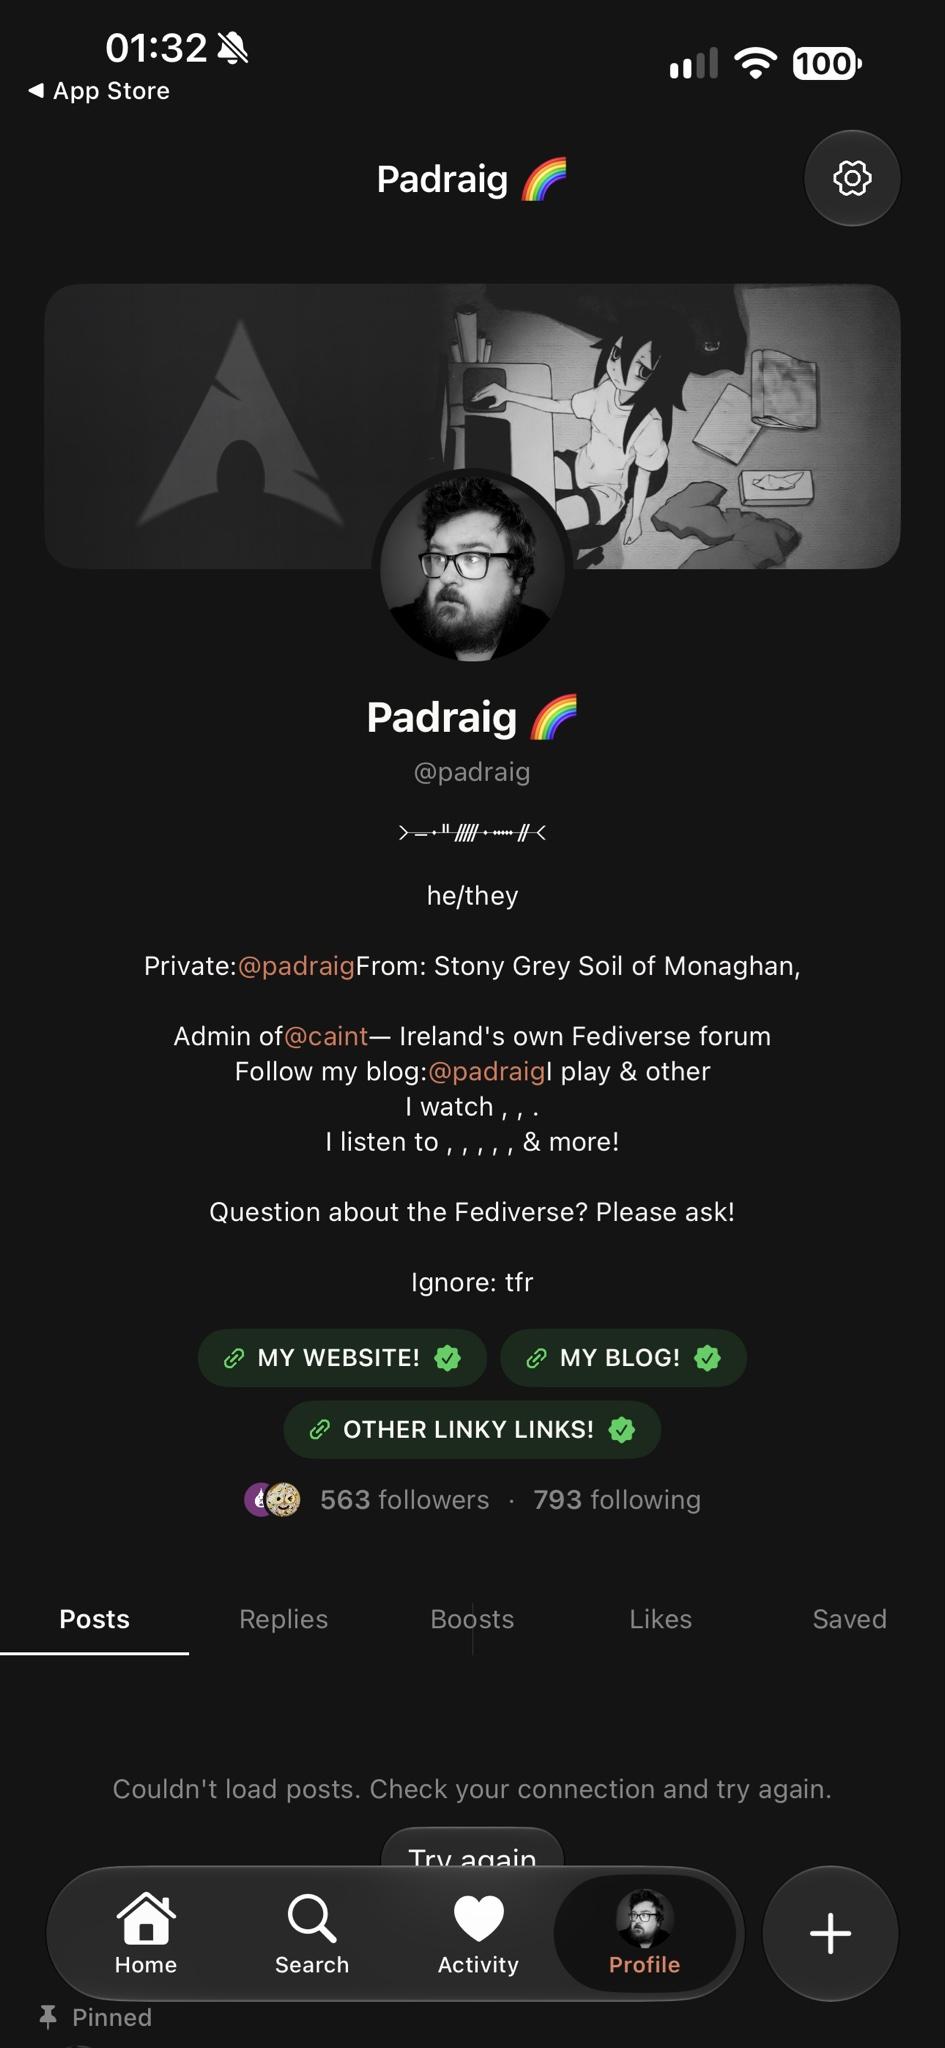
![Error message in MastoDino
Couldn't load the feed
[TootSDK bug] There was an error decoding incoming data:
context: Context (codingPath:
LCodingkey(stringValue: "Index 8', intValue:
8), CodingKeys(stringValue: "filtered", intValue:
nil), _CodingKey(stringValue: "Index 0", intValue: 0), CodingKeys(stringValue: "filter", intValue: nil), CodingKeys(stringValue:
"filterAction", intValue: nil)], debugDescription:
"Cannot initialize Action from invalid String value blurạiunderlyingError: nil).](https://cdn.masto.host/mastodonie/media_attachments/files/117/226/957/033/620/221/original/3ed84da6d24c9f65.jpeg) @beoz@det.social
Ein bemerkenswerter Artikel in der Schweizer Zeitung La Liberté über das Jahr-2038-Problem:
https://www.laliberte.ch/articles/monde/le-bug-de-2038-pourrait-tout-faire-planter-1411046
Besonders erfreulich: Er erwähnt XSTP.epoch, das im…
 @crell@phpc.social
RE: https://mstdn.thms.uk/@michael/117207970827505173
So, let me expand on this.
Taylor has just said that if you want to contribute to Laravel (eg by reporting a bug), you MUST pay some other company to use their coding agent and theft-trained, climat…
@aardrian@toot.cafeTesting a Safari bug fix showed me Firefox & Chromia now behave as Safari did/does (not a bad thing).
So I updated my post “Don’t Turn a Table into an ARIA Grid Just for a Clickable Row” to account for this and the CSS is now simpler (anchor link):
https://
 @mgorny@social.treehouse.systems
In my private projects and in #Gentoo, I have a strict #NoAI policy. Any LLM-assisted contributions are closed immediately and considered tainted. Use for messaging, bug reporting, etc. also gets you a warning and a request to write yourself. And I dare say I have a heavy ban finger on this; you get one warning only. Well, unless it's clearly an automated submission, in which case you get an immediate ban.
In my dayjob and non-Gentoo work, I also follow a strict policy for my own work. I don't use any of these tools. However, I can't really stop others from doing so, even though I cringe whenever I see someone needing to use an overengineered statistical model to make a trivial change. I can't really reject bug reports, reviews, etc.
The really hard part of it is that I'm starting to have doubts. I truly hate slop in all forms, and what these tools have done to the Internet in general, and to #FreeSoftware in particular. However, I've also gotten some good reports. Like, the kind of tricky logic issues in the specification I am developing that I would have never figured out myself, and that may have never came up during the review otherwise. In other words, someone running an LLM on the specification triggered real bugs that would likely slipped through and required a post-approval specification change when someone noticed that we've introduced incompatible constraints in two different parts of the specification, that would eventually be hit in real use.
All the ethical problems are still there. All the harm is still there. However, I can't really claim that these tools vomit pure useless slop anymore. I feel that it's really time for me to retire.
@Techmeme@techhub.socialGitHub plans a two-tier bug bounty system, cutting rewards for public reports and boosting payouts for an invite-only group, amid an AI-powered submission surge (Carly Page/The Register)
https://www.theregister.com/devops/2026/07
@heiseonline@social.heise.deEinige der zuletzt hier besonders häufig geteilten #News:
BMW: Belästigt Mit Werbung
https://www.heise.de/news/BMW-Belae…
 @fazalmajid@vivaldi.net
@… are you able to run Linux on it? For me, no media keys is a feature, not a bug, they always get in the way when I am trying to use F-keys, e.g. to select the BIOS boot menu.
 @draxil@social.linux.pizza
github have broken org-mode markup. Of course, github is an awful site now. But if you wish to make noise about this, these would seem to be the places:
https://github.com/orgs/community/discussions/209313
 @chrislowles@mastodon.social
just the absolute worst etiquette for bug report/feature request responses, they're acting like they're in a mw2 2009 text chat
@fanf@mendeddrum.orgfrom my link log —
A tale of a build system bug. (ninja/gcc/Windows)
https://gist.github.com/Som1Lse/2fbb0e22cb59a158bb8e09bf6f527f7e
saved 2020-10-30
 @aral@mastodon.ar.al
🥳 Just released: Auto Encrypt¹ version 6.2.0
If at first you don’t succeed…
• Transient ACME server failures are now retried up to four times and obey the Retry-After header, falling back to exponential back-off if one isn’t provided.
• Vastly improved error handling.
• Some bug fixes.
Basically, Auto Encrypt now does its very best to provision you that certificate even when things go wrong.
Full change log:
@ruario@vivaldi.net@… LOL, that's a fun bug
@macandi@social.heise.de @lapizistik@social.tchncs.de
Stellen wir uns ganz kurz mal vor der Kalender wäre ein klein wenig verschoben und das Jahr 2000 käme demnächst. Und nun kommen die AI-Techbros und meinen: das mit dem y2k, mit dem Millennium-Bug, das fixen wir einfach mit KI, das ist alles gar kein Problem, laßt uns nur machen…
Ich weiß, wie viele derer, die damals hart dran gearbeitet haben, alles zu fixen, unsicher waren, und mancher hatte dann für lange Zeit Wasserkisten und Konserven. Ich war damals relativ gelassen, aber bei obig…
 @shriramk@mastodon.social
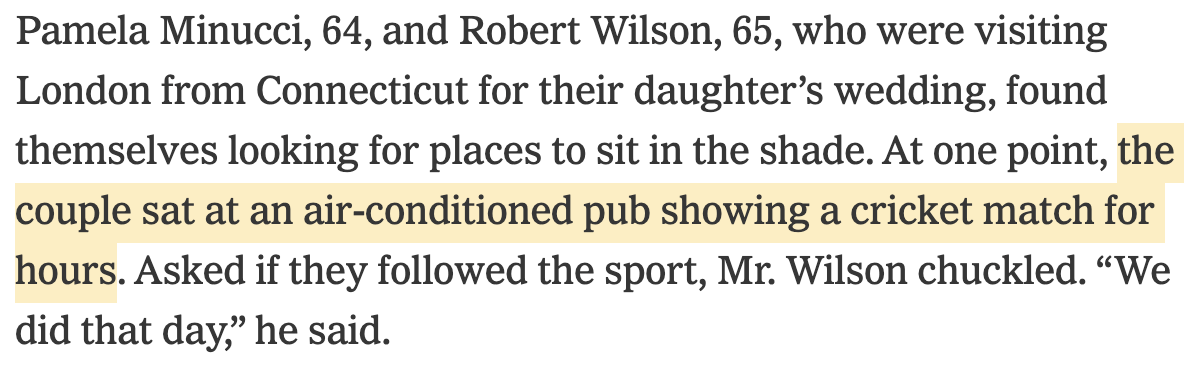
This is called a feature, not a bug, you nits.
https://www.nytimes.com/2026/07/23/travel/europe-summer-heat.html
 @azonenberg@ioc.exchange
Just closed out the last release blocking bug and tagged ngscopeclient v0.2-rc1. Planning to release v0.2 in the next couple of days unless there's any major issues.
Please test and let me know how it works for you! Official (unsigned) release binaries are building now and I'll be pushing to github later in the morning.
 @enriquericos@mastoart.social
Octavia Butler's Bloodchild just unlocked a childhood memory: this guy I read on an interview, got a botfly infection and, instead of getting the larva out with extreme prejudice, he let it grow out. Also said the bug was made of him
It made me question things. My parent's philosophy was: bug=bad=kill it, which I Never accepted, but this guy was on another level
Also, I never saw our own materiality the same way again
I owe a lot to that (maybe not) crazy bastard
#books
 @emd@cosocial.ca
LOL I just found a timezone (of course) bug in a package I maintain, that was introduced 3 years ago (!!) in a PR titled “Fix Timezones (better)”.
#TimezonesAreHard #DevLife
 @schoedland@digitalcourage.social
@… I might have run into a bug in #BSSG. I have assigned image in the frontmatter, and they render on the first page and on the single post page, but fail to render from page 2 onward.
For example,
 @xiffy@mastodon.nl
I opened my Flickr app on Android and noticed that auto-upload had stopped. When going to the settings I noticed I was unable to re-enable auto uploader. I reported a problem, got an answer within the hour, provided some more information and five minutes later the latest update was pulled. I was told to remove the app and yes re-installing the app gave me the previous version. And i was able to back up my photos again. I'd say, that was fast.
Anyone out there using flickr with auto-uploader enabled, check your settings, it might have stopped anywhere in july.
#flickr #bug #backup
 @shanmukhateja@social.linux.pizza
So pamac has this weird case sensitivity bug when searching for apps and landing the app details UI whether for installing or uninstalling apps irrespective of repos or Flatpaks.
I fixed once and sent a patch to Manjaro devs. It took them a few years(yeah, years) to commit them. This was before AI.
That phantom bug still exists today somehow. This time, I used Claude to fix it. I have patches in my local and built a custom version for them.
I don’t plan on upstreaming them …
@aardrian@toot.cafeTesting a Safari bug fix showed me Firefox & Chromia now behave as Safari did/does (not a bad thing).
So I updated my post “Don’t Turn a Table into an ARIA Grid Just for a Clickable Row” to account for this and the CSS is now simpler (anchor link):
https://
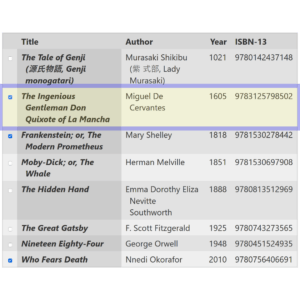
Don’t Turn a Table into an ARIA Grid Just for a Clickable Row
Again, title says it all. However, there is an equally bad opposite approach you might be tempted to use, so let me clarify: Don’t use ARIA grid roles simply to make rows clickable in a table, and Don’t put click handlers on table rows (
 @cdarwin@c.im
UnitedHealthcare, the largest health insurance company in the US,
is allegedly using a deeply flawed AI algorithm to override doctors’ judgments
and wrongfully deny critical health coverage to elderly patients.
This has resulted in patients being kicked out of rehabilitation programs and care facilities far too early,
forcing them to drain their life savings to obtain needed care that should be covered under their government-funded Medicare Advantage Plan.
That…
 @Schrank@phpc.social
 @michabbb@social.vivaldi.net
🔍 Review and analysis skills: interrogate (adversarial panel), arena (parallel candidates, graft the strongest parts), architect, how, why, swarm, blast-radius and reflect
✅ Verification covers project-local verification skills, periodic audits, #TDD bug fixing and a reviewable TSV decision trail for unattended or long-running work
 @thomastraynor@social.linux.pizza
Sigh, another day where I want to have a 'bug report 101' workshop for work. Email to the security account that when they enter data they don't get the expected results.
1. This isn't security issue, it is a data issue.
2. You need to report more than "I have a problem'. At a minimum.
2.1 Full screen print showing the data entered.
2.2 What key did you press to process the data?
3. What account & environment?
4. Any message…
@fanf@mendeddrum.orgfrom my link log —
The problem with function namespaces and Lisp macros.
https://ianthehenry.com/posts/janet-game/the-problem-with-macros/
saved 2021-10-13 …
 @groupnebula563@mastodon.social
@… BUG REPORT:
somehow, both my and @…'s pinned posts are no longer pinned across the bridge
@fortune@social.linux.pizza> I'm an idiot.. At least this [bug] took about 5 minutes to find..
Surely, Linus is talking about the kind of idiocy that others aspire to :-).
-- Bruce Perens in response to Linus Torvalds's
@grumpybozo@toad.socialRE: https://mastodon.online/@bug_gwen/117320872614288989
HOW???
I know Malaria is bad, but it is also well-known and treatable.
@Techmeme@techhub.socialThe attacker who withdrew ~4,000 BTC from Blockstream's Liquid Network federation wallet returns 3,400 BTC after Blockstream said its bridge nodes were patched (The Block)
https://www.theblock.co/news/defi/2026-09-
@aral@mastodon.ar.al🥳 Auto Encrypt: 5.1.1 released
• Fixed: Issue #26¹: Regression: AutoEncrypt HTTPS server does not start using new certificates upon renewal
https://codeberg.org/small-tech/auto-encrypt
Many thanks to zanecodes² for catching this rather fundamental bug.
Here’s a quic…
@chrislowles@mastodon.socialthere's this one guy on a gh repo basically telling people to stfu when they submit feature issues or bug issues and now someone in there just shared a maitenence fork cuz the last actual release for this thing was like 7 months ago and it's time sensitive to keep it up to date and now they've just resorted to good ol fashioned name calling
@fortune@social.linux.pizzaBOFH excuse #378:
Operators killed by year 2000 bug bite.
@azonenberg@ioc.exchangengscopeclient v0.2.2 is released with a few small bug fixes
https://github.com/ngscopeclient/scopehal-apps/releases/tag/v0.2.2
@Techmeme@techhub.socialSource: Microsoft plans to release an AI security tool this month using models from Anthropic, OpenAI, and itself, as a cost-effective Mythos alternative (Aaron Holmes/The Information)
https://www.theinformation.com/briefings/exclusive-microsoft-p…
@ruario@vivaldi.net@… @… The same fix is indeed in both snapshot and stable and we had multiple reports that it was working now for others. I wonder if this is some other bug or an issue with settings.
If you start with a clean test profile, do you see t…
@beoz@det.socialEin bemerkenswerter Artikel in der Schweizer Zeitung La Liberté über das Jahr-2038-Problem:
https://www.laliberte.ch/articles/monde/le-bug-de-2038-pourrait-tout-faire-planter-1411046
Besonders erfreulich: Er erwähnt XSTP.epoch, das im…
@azonenberg@ioc.exchangeJust doubled performance of the ngscopeclient CDR PLL on some workloads by fixing a bug causing it to run twice.
The PLL starts out with a small output buffer (since it doesn't know how much it's oversampling the input) then if it needs to generate more clock edges than the buffer can hold will expand the buffer and re-run. The size of the previous output is saved so next time it can make a better estimate of how much to allocate.
This adaptive sizing step is supposed to …
@aral@mastodon.ar.al🥳 Auto Encrypt Localhost version 11.0.0 released
This is mostly a bug fix, code quality, and modernisation release.
Auto Encrypt Localhost automatically provisions and installs locally-trusted TLS certificates for Node.js https servers in 100% JavaScript (without any native dependencies like mkcert and certutil).
https://
@fanf@mendeddrum.orgfrom my link log —
A 40-year-old bug in BSD unix domain socket inode allocation discovered on the DEFCON 34 main stage.
https://yuvalino.com/how-can-you-not-be-romantic-about-unix-domain-sockets
saved 2026-09-14
@macandi@social.heise.de @Techmeme@techhub.socialApple introduced a cap and a 30-day cool-off period on bug report submissions, citing a deluge of AI-assisted reports; researchers can request higher quotas (Financial Times)
https://www.ft.com/content/4532122d-90f2-4433-9df6-ca99d8a141d2
@aral@mastodon.ar.al🥳 Auto Encrypt version 6.0.0 released
This is mostly a bug fix, code quality, and modernisation release.
Auto Encrypt automatically provisions TLS certificates for Node.js servers – like Kitten¹ – using Let’s Encrypt.
https://codeberg.org/small-tech/auto-encrypt
• 1…
@azonenberg@ioc.exchangeFound and fixed a bug that could cause the MockOscilloscope driver in ngscopeclient to report bogus sample rates and memory depths when working with offline sessions. Unfortunately the bad state is persistent if you save a session when it happens, and it had been lurking for quite a long time.
There's no permanent data loss, since if you have waveform data in the session you can figure out the actual sample rate and memory depth from the channel metadata, but you need to manually p…
@fanf@mendeddrum.orgfrom my link log —
How I made rustdoc 33% faster in one week.
https://noahlev.org/blog/2026/08/27/making-rustdoc-faster/
saved 2026-08-28 h…
@Techmeme@techhub.socialCisco releases Antares-350M and Antares-1B, two open-weight AI models to find known vulnerabilities within a codebase, and plans to release Antares-3B soon (Sam Sabin/Axios)
https://www.axios.com/2026/07/21/cisco-open-source-ai-models-cybersecurity
…
@Techmeme@techhub.socialSecurity researchers in an OpenAI bug bounty program hacked OpenAI, accessing its "monorepo" on GitHub, using a cybersecurity version of Opus 4.8 and Opus 5 (Robert McMillan/Wall Street Journal)
https://www.wsj.com/tech/ai/hackers-used-a