@neverpanic@chaos.social
2026-10-14 09:16:50
11 core #OpenSource packages run on one or two maintainers, e.g. zlib, sudo, bash, and the time-zone database.
#OpenSSL #OpenSSLCon26
 @neverpanic@chaos.social
11 core #OpenSource packages run on one or two maintainers, e.g. zlib, sudo, bash, and the time-zone database.
#OpenSSL #OpenSSLCon26
 @a@paperbay.org
How mature is this repository? My long quest for open-source software metrics
When I discover an open-source software project for the first time, how can I estimate whether it is mature, healthy and usable?
I just released OSSTRL - Open Source Software Technology Readiness Level to help me calculating the maturity of open-source projects.
#opensource
@neverpanic@chaos.socialKajal Sapkota on "Who pays for #OpenSource": the year before Heartbleed, #OpenSSL received $2,000 in donations.
"For reference, that's what I pay in rent each month"
#OpenSSLCon26

 @iam_jfnklstrm@social.linux.pizza
 @michabbb@social.vivaldi.net
🔐 Hermes Vault: a local-first credential broker and encrypted vault for AI agents. It scans for plaintext secrets, brokers policy-gated access and proves audit integrity.
#opensource #security #MCP
 @publicvoit@graz.social
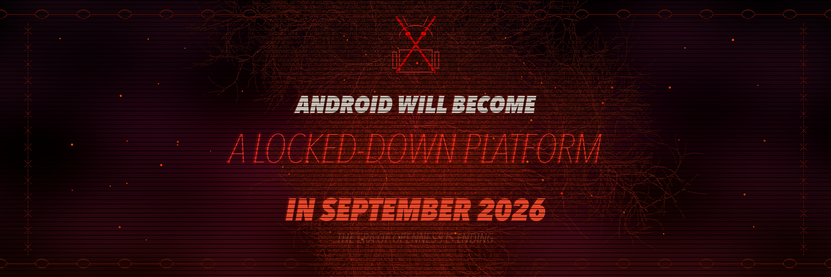
#Google hammers another, extremely petty nail in the #Android #OpenSource Project’s coffin
 @grist@fosstodon.org
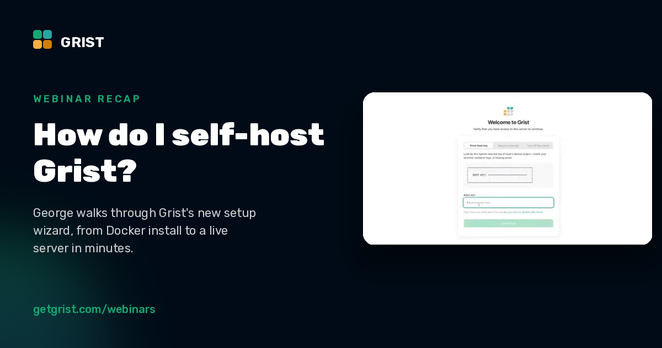
And for questions along the way, the Grist Discord has a dedicated self-hosting channel. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@neverpanic@chaos.social"The question was never whether #OpenSource code is free. It is who pays the reviewers" -- Kajal Sapkota from #OpenSSL Corporation
#OpenSSLCon26
 @frankel@mastodon.top
#OpenSource as We Know It Is Dead
https://jross.me/open-source-as-we-know-it-is-dead/
 @digitalnaiv@mastodon.social
Die Schweiz nennt ihr Anti-Microsoft-Programm BOSS – und trifft damit unfreiwillig den Nagel auf den Kopf: Wer entscheidet, wo die eigenen Daten liegen, ist eben der Chef im Ring. 3000 Beschäftigte, openDesk, Rollout bis Ende 2027. Der US-CLOUD-Act als bester Verkäufer von Open Source, den man sich vorstellen kann. #DigitaleSouveränität #OpenSource #Schweiz https://www.heise.de/news/Schweiz-startet-Open-Source-Arbeitsplatz-fuer-3000-Beschaeftigte-11444842.html?wt_mc=rss.red.unbekannt.unbekannt.atom.beitrag.beitrag
 @dde@social.tchncs.de
Pebble Time 2 – #opensource
@grist@fosstodon.org @michabbb@social.vivaldi.net🧰 #ECC is an #opensource agent harness optimization system that adds skills, instincts, memory, security and research-first development to #ClaudeCode,
@a@paperbay.orghumanizer
"A 12B model that rewrites AI-written drafts (emails, essays, reports, forum posts; English and Chinese) so they read like a person wrote them. It is trained to keep every number, unit, date, name and quote and to add nothing, and it runs locally."
#ai #opensource
 @knurd42@social.linux.pizza
So after the latest redesign even #opensource / #linux company #SUSE has a blog without an #RSS fe…
 @thijs_lucas@norden.social
Was ich noch sehr vermisse: eine Alternative zum Speichern, Kategorisieren, Bewerten und Beschreiben von Orten wie mit #GoogleMaps. Etwas #MadeInEurope und #OpenSource.
 @ubuntourist@mastodon.social
Starting in 2027, a silent update, nonconsensually pushed by Google, will block every Android app whose developer hasn't registered with Google, signed their contract, paid up, and handed over government ID.
https://keepandroidopen.org/
 @thesaigoneer@social.linux.pizza
A tip (unsolicited): if you want to make your Hyprland look stunning use these truly opensource configs. Stephan Raabe has been at it for 3 or 4 years now and he deserves the real credits (and JaKoolit, but he stopped). Highly recommended!
https://ml4w.com/os/
 @ErikJonker@mastodon.social @michabbb@social.vivaldi.net
📋 The PHP Foundation looks at how European public administrations run their #digitalsovereignty strategies on #PHP applications #opensource
 @adulau@infosec.exchange
I don’t like playing the futurologist, but after seeing AI companies warn EU institutions about the supposed risks of open-weight models, I suspect some are lobbying to regain control over genuine open source and open-weight AI.
Don’t fall into the trap: the greater danger lies in opaque, proprietary models, not open-source ones.
#opensource
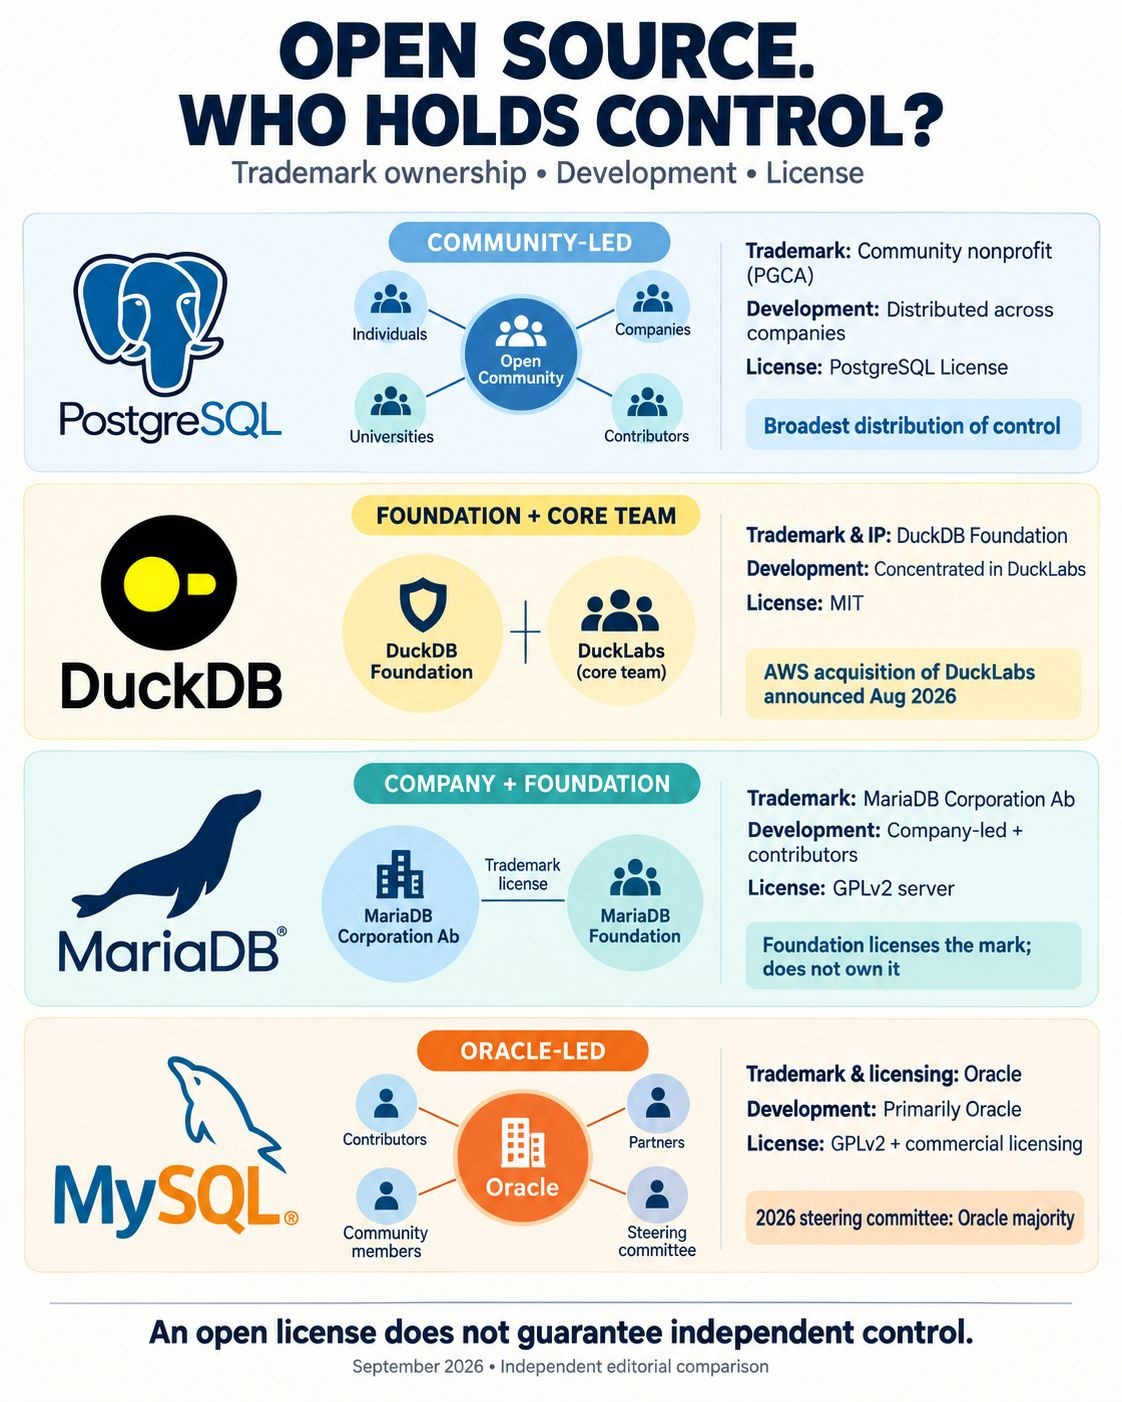
@frankel@mastodon.top#OpenSource - Who holds control?
via Peter Zaitsev on LinkedIn https://www.linkedin.com/posts/peterzaitsev_i-was-asked-how-do-…
 @dde@social.tchncs.de
Distributionsfremde Software – #opensource
@michabbb@social.vivaldi.net @grist@fosstodon.orgHow do I self-host Grist? Recap of our setup wizard webinar #OpenSource
 @rasos@fairmove.net
Soll ich wieder einen Vortrag zum #Linuxday einreichen? #OpenSource #ERP Systeme wäre vielleicht für Unternehmen interessant und mit

 @Szwendacz@social.linux.pizza
The urge to use opensource projects where maintainers have similar worldview to yours is kinda unpleasant, when you tend to always have your own opinion.
One would ask, if it isn't like that with everything then. Um, I don't know? Worldviews seem to be exposed more aggressively here, than around other things, at least by some folks.
#randomthoughts
 @gla@mastodon.social
That's a nice little utility, also available as a #launchbar action
#markdown #html #opensource
 @mgorny@social.treehouse.systems
Too many days working on #FLOSS feel like: "I'm not paid for this shit. I'm paid to do other shit and I have to focus on that shit, but I can't when I have to spend so much time fixing shit that apparently others are being paid to break all the time."
#Gentoo #LLVM #FreeSoftware #OpenSource
@grist@fosstodon.orgUpdating Grist means pulling a new Docker image and restarting the container. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
 @nohillside@smnn.ch
Wieder was gelernt. Aber wer kommt auf die Idee, sowas hinter «OLE-Objekt» zu verstecken?
https://social.tchncs.de/@LibreOfficeDE/116956696624264273
 @opencommit@fosstodon.org
We had an intermittent storage issue. This problem has now been resolved.
#opencommit #git #opensource
@frankel@mastodon.topGuest poster Stefano Fago on a Java Geek today:
"I started with a simple task: I needed an #AI agent to help me compile decision records, structured documents that capture why a team chose option A over B, using the #opensource
@a@paperbay.org"General Resolution: LLM usage in Debian"
When people don’t understand a system, they try to regulate it.
#ai #debian #opensource
@michabbb@social.vivaldi.net📋 #HuntProxy is an #opensource web security workbench built for #AI agents — connect it over #MCP
 @JBrickelt963@framapiaf.org
#VLC4 a enfin une date de sortie officielle pour décembre 2026. Je viens de voir ^^ #VLC #OpenSource #FOSS
J'…
 @dawid@social.craftknight.com @grist@fosstodon.org
Self-managed Grist supports SAML and OIDC, so your team can log in with your existing identity provider. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@frankel@mastodon.top @michabbb@social.vivaldi.net🤖 #BrowserAct is an open-source browser automation CLI built for #AIagents — real browsers, anti-bot bypass and human handoff when the agent gets stuck #opensource
 @freeminded@tooting.ch
Heute bin ich am #SGES in #Winterthur als Redner im Innovationsforum IF.19 zum Thema Digitalisierung und Resilienz: Wie schaffen wir zukunftsfähige Infrastrukturen?
Natürlich dreht sich mein Beitrag um die Rolle von #OpenSource
https://sges.ch/if2026/if19-2026/
Würde mich freuen hier auf andere Fedinaut*innen zu treffen.
@a@paperbay.orgIs there somewhere a good open source software in Python to act as bridge between RSS and ActivityPub act as actor? Before I write something new.
#activitypub #opensource #rss
 @rberger@hachyderm.io
Find and Help your Open Source Friends
- Leonid Bugaev
"So let the large projects close the queue [to LLM contributions]. There is a lot more open source out there.
That was the reason I built Help Wanted in the first place, few years ago. At the time of writing, it has 650,456 issues from 96,576 projects in its index, from the projects who actually WANT help. Most developers will never hear the names of nearly all these projects.”
#OpenSource
@frankel@mastodon.top @michabbb@social.vivaldi.net📋 #queuesql is an #opensource #Laravel package that turns any write query — delete, update, insert, upsert — into parallel batched queue jobs
 @ErikJonker@mastodon.social
Mooi om te zien hoeveel keuze en variatie er is als het gaat om een meer autonome digitale werkplek.
#opensource #foss #mijnbureau
@michabbb@social.vivaldi.net📦 v2 is a ground-up rewrite in Rust of the original Go tool, MIT licensed. Windows support is planned
🌐 #opensource
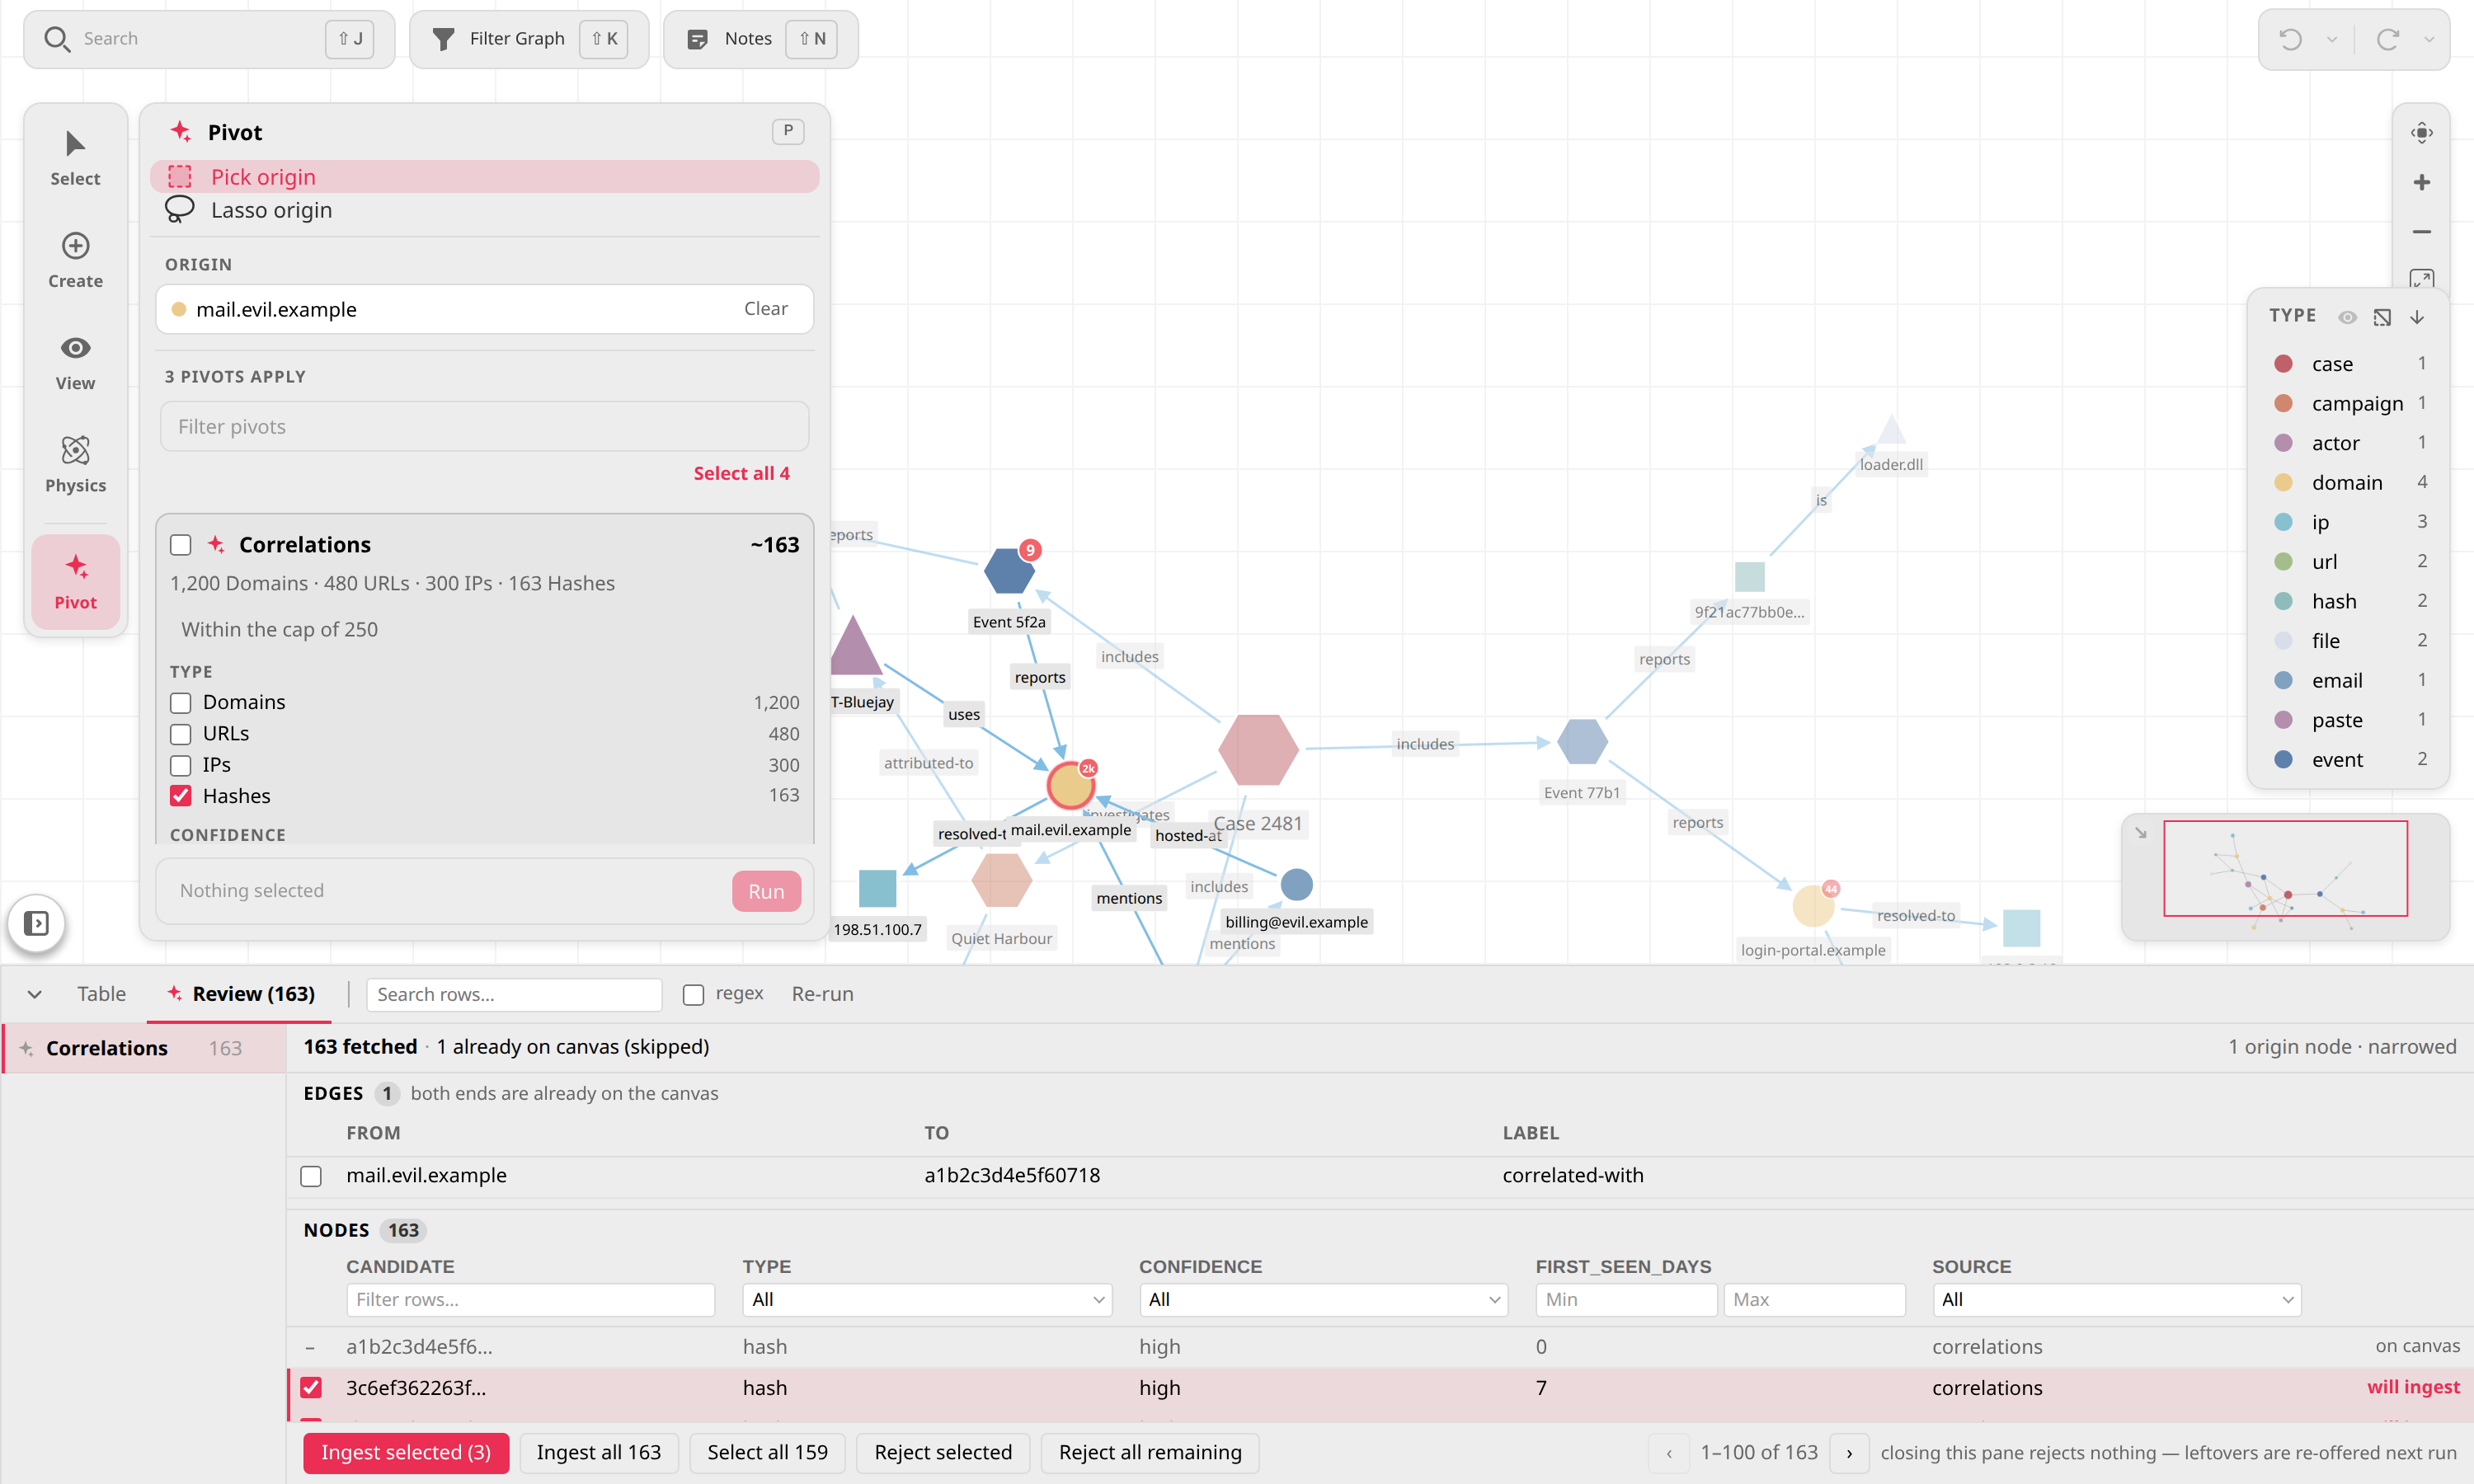
@adulau@infosec.exchangePivotick v2.0.0 has been released.
Pull more graph out of wherever your data lives, and you choose what lands. History is the way back out of anything that does.
Actually you can update, pivot graph and review. This release also includes many new other features.
#graph #library #infosec #opensource #graphing #pivotick #cti #threatintelligence
 @kingconsult@berlin.social
#OpenProductivity: 6 #OpenSource -Hersteller gründen Joint Venture für #openDesk
> Die #openDesk -Komponentenhersteller @… @… #Nordeck #OpenXchange @… und @… haben die Open Productivity Software GmbH gegründet. Das Joint Venture will die Office- und Kollaborationssuite openDesk bei #Unternehmen und Betreibern kritischer Infrastrukturen in internationalen Märkten etablieren.
13. Oktober 2026:
#Kritis #OSS #DigitaleSouveranitat
 @vosje62@mastodon.nl
RE: https://social.overheid.nl/@opensource/117309135841847497
Een toot om in te lijsten (helaas). 😇
Maar het zou inderdaad mooi zijn als bij al die mooie woorden in de praktijk wat laaghangende resultaten geboekt worden.
Berichten delen (doorplaatsen) op Mastodon is geen hoogstaande wiskunde.
@michabbb@social.vivaldi.net🧠 #VoiceMem is an #opensource memory system for real-time #voiceagents, built on a streaming dual-brain architecture
 @frankel@mastodon.top @michabbb@social.vivaldi.net
🔍 #REA (Reverse Engineer Anything) is an #opensource #MCP server that lets #AIagents inspect app…
 @frankel@mastodon.top @michabbb@social.vivaldi.net
🔁 #CompoundEngineering is an #opensource plugin of 33 skills for AI coding agents that turns each task into stored knowledge, so the next unit of work gets easier instead of harder #ClaudeCode
 @michabbb@social.vivaldi.net
📋 #Luvus is an #opensource mission control for your #AI coding agents — one terminal to run, watch, resume and orchestrate
 @ErikJonker@mastodon.social
Looking at and playIng around with Hermes Agent, impressive and relatively easy to install and use.
Also opensource. Hermes Agent — Open-Source AI Agent That Grows With You | Nous Research #AI #HermesAgent #opensource #foss #agents
@digitalnaiv@mastodon.socialKiel macht ernst: Über 200 Beschäftigte der Staatskanzlei arbeiten laut Stefan Krempl bei @… mit Linux. Rund 20 Rechner bleiben vorerst bei Windows – Fachverfahren ohne Alternative. Genau da liegt die eigentliche Baustelle der digitalen Souveränität. Nächste Schritte: Nextcloud, Univention Nubus, Oskar. #Linux #OpenSource #DigitaleSouveränität https://www.heise.de/news/Nachfolger-von-Windows-Staatskanzlei-Kiel-stellt-auf-Linux-um-11460729.html
 @johnleonard@mastodon.social
The SaaSpocalypse might be back on. A developer has used AI to create an alternative to the Adobe Suite and in doing so has put the entire cloud model, with it's hard-to-exit ecosystems, back under scrutiny.
#saaspocalypse #adobe #opensource #technews #ArtCraft
@michabbb@social.vivaldi.net🎨 #Impeccable is a design language for #AI coding agents: 1 skill, 23 commands, live browser iteration and 46 deterministic detector rules for AI-generated frontend design #opensource
 @frankel@mastodon.top @michabbb@social.vivaldi.net
🐝 #SwarmForge is an #opensource agent coordination system that turns swarms of #AI agents into a disciplined engineering team, built on
@adulau@infosec.exchangeSo finally Kimi-k3 is not really open-source
#kimi #ai #opensource
@michabbb@social.vivaldi.net📋 #Autoprompt is an #opensource coding-agent skill that cut failures by 45% on agentic coding tasks #aiagents
@ErikJonker@mastodon.socialKey Takeaways: OSOR Webinar on EU Open Source Strategy.
#opensource #foss #EU
@grist@fosstodon.orgAll data stays local when self-hosting, including anything processed through the REST API or MCP. https://www.getgrist.com/blog/how-do-i-self-host-grist-recap-of-our-setup-wizard-webinar/
@michabbb@social.vivaldi.net📋 #FreeToken is an edge-native #MoE serving engine for running frontier-scale open-weight models on personal, consumer hardware #opensource
@michabbb@social.vivaldi.net @grist@fosstodon.orgStop saying “open source sustainability” #business
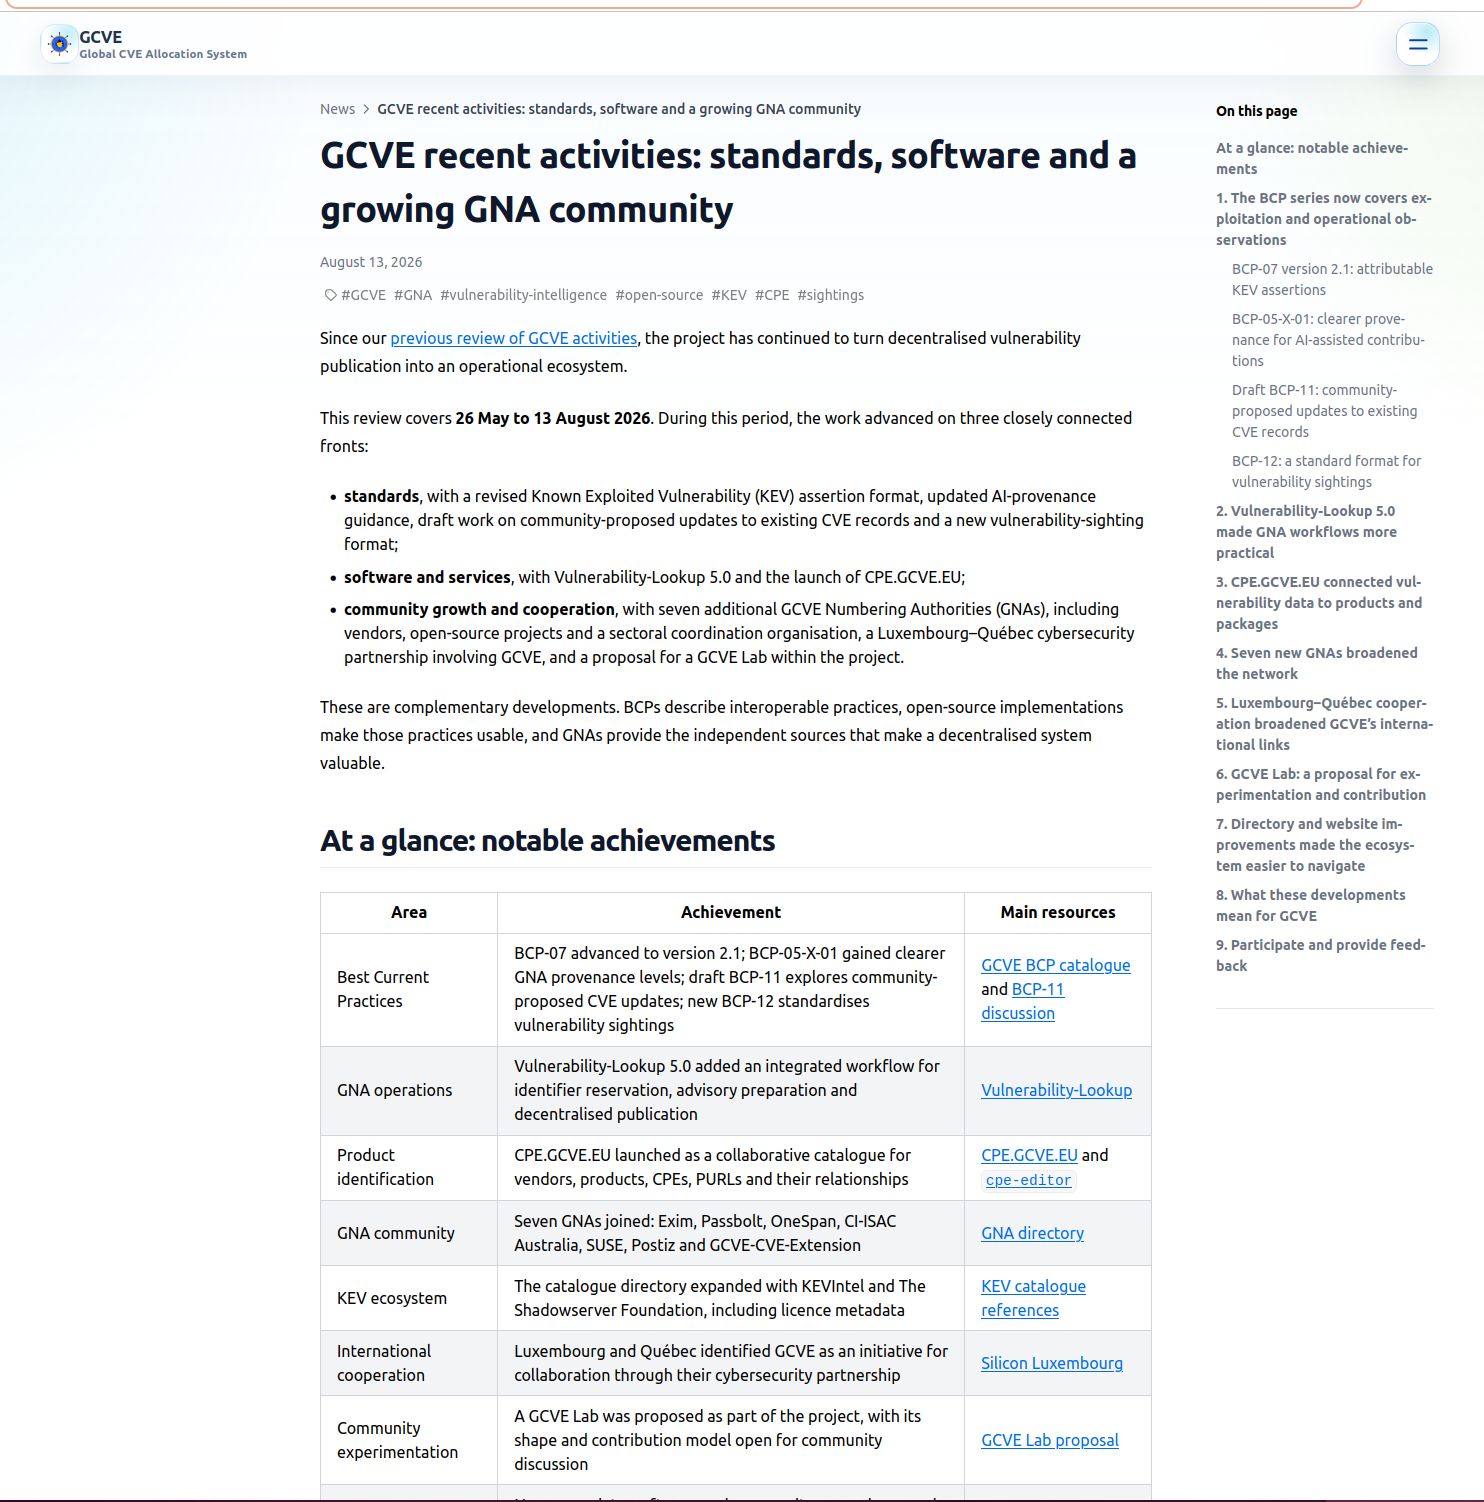
@adulau@infosec.exchangeIf you are curious about (nearly) everything we did the past months at the GCVE.eu initiative:
#gcve #cve #vulnerability #vulnerabilitymanagement #cra #cybersecurity #openstandard #opensource
 @michabbb@social.vivaldi.net
📋 #croc is a CLI tool that transfers files and folders between any two computers, with end-to-end encryption #opensource #golang
 @michabbb@social.vivaldi.net
🔌 #Toolport is a local-first #MCP gateway. Every AI client points at one port and shares the same servers, so you set up and authenticate each server once instead of in every app.
#opensource
 @ErikJonker@mastodon.social @michabbb@social.vivaldi.net
📊 Local-first dashboard for #Codex CLI and #ClaudeCode usage limits #opensource #nodejs
 @michabbb@social.vivaldi.net
🧩 #Laravel LSP announced at #LaraconUS 2026: a first-party language server that teaches your editor about your app #PHP
 @ErikJonker@mastodon.social @adulau@infosec.exchange
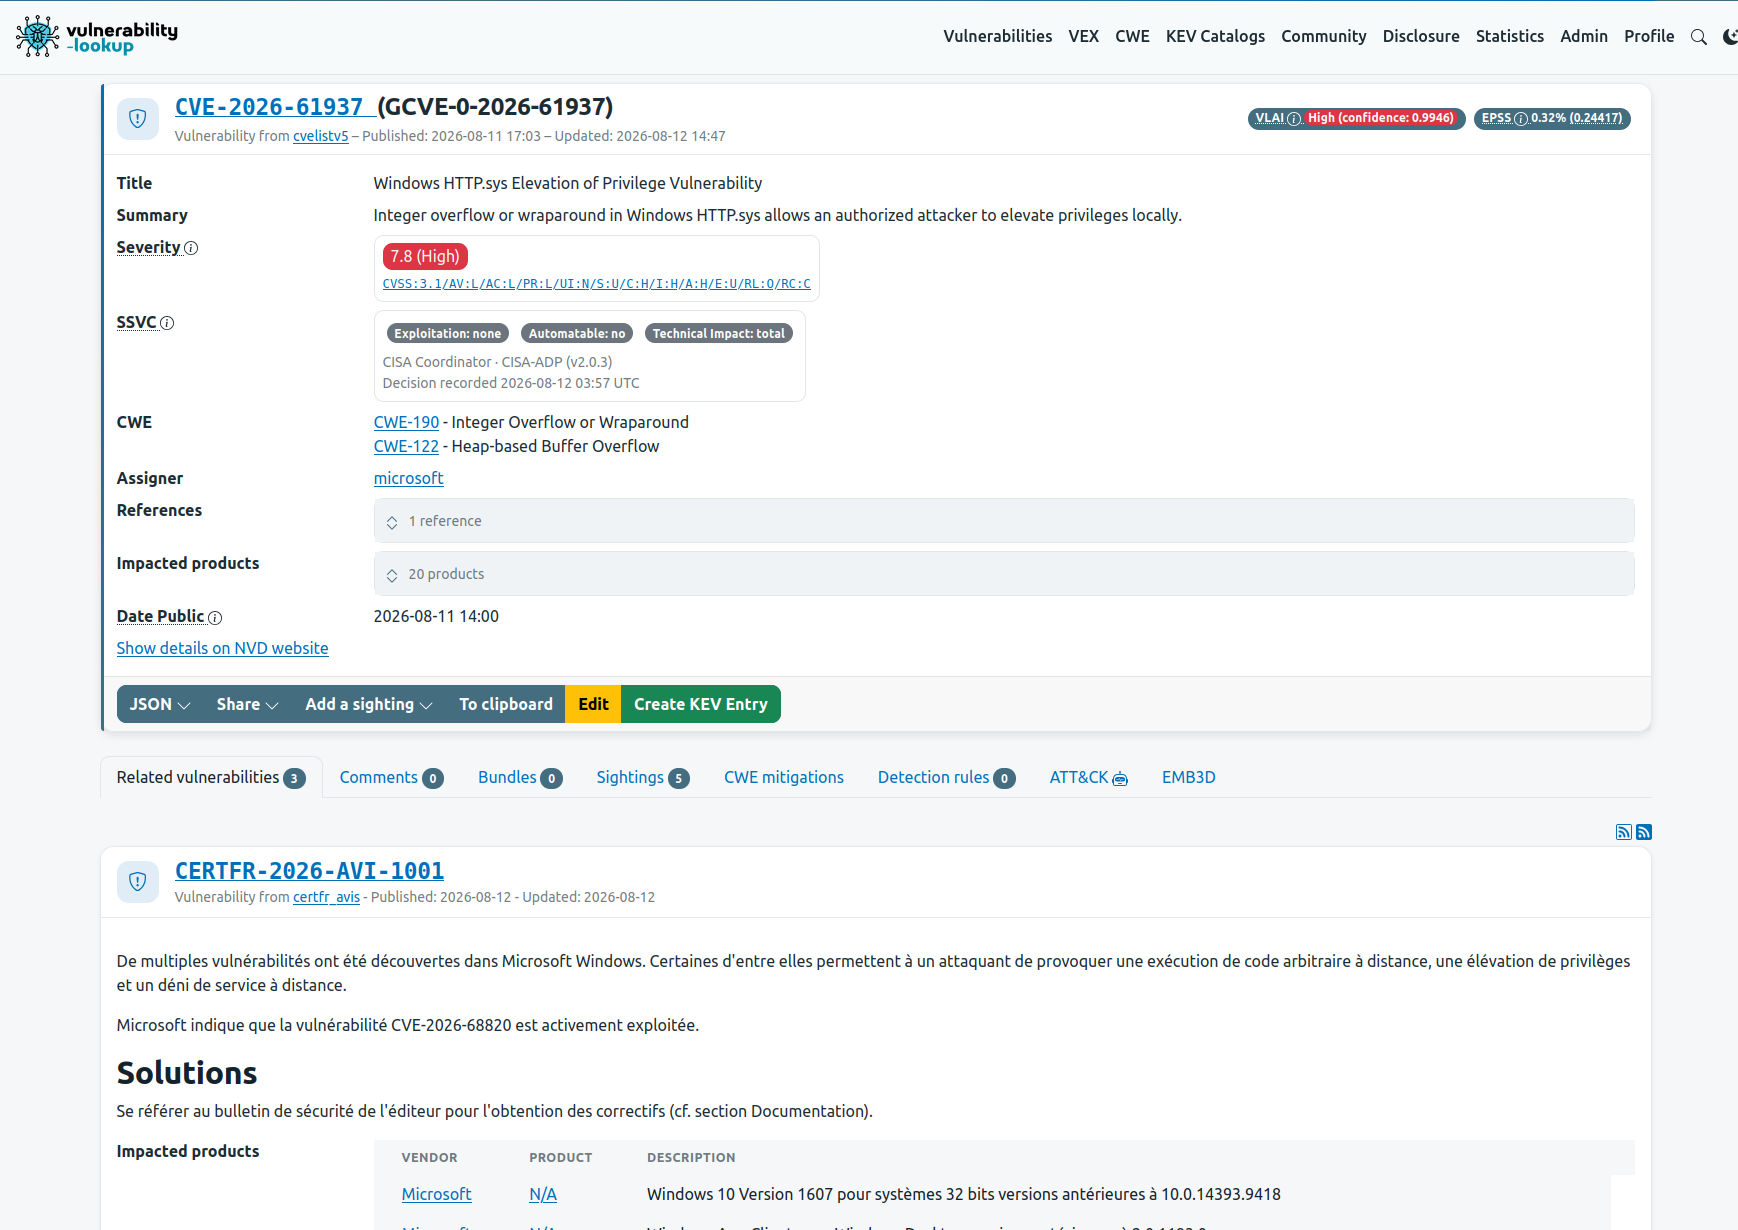
vulnerability-lookup 6.0 will be released this week with many (really, many!) new features.
One of the smaller, but important, additions is support for multiple SSVC views alongside CVSS. When SSVC information is available from an ADP (such as CISA) , or from additional sources such as GCVE, it is now displayed by default.
This allows users to more easily compare the different severity and prioritization assessments associated with a vulnerability.
The CIRCL vulnerability-lookup instance is running the pre-release of 6.0 -
#cve #gcve #opensource #vulnerabilitylookup #opendata #vulnerabilitymanagement #cyberecurity #ssvc
@…
@…
 @ErikJonker@mastodon.social
Geweldige podcast weer. Zo simpel is het niet.
Wel goed te bedenken dat de haast onvermijdelijke lijkende financiele ineenstorting, geheel of gedeeltelijk, niet leidt tot verdwijnen van AI. Ondermeer ook door chinese opensource/openweight modellen.
#NRC #AI #Kaartenhuis
https://open.spotify.com/episode/2757MgogoYAlFzAlzAbbci?si=K1qnC9VlR4G5qsmoA4tDuQ
@michabbb@social.vivaldi.net📺 youtube-subscriptions-ingest pulls video metadata from your real #YouTube subscriptions and turns it into a cross-linked knowledge graph in your #Obsidian second brain, not just a flat list of videos #opensource
@adulau@infosec.exchangeI love to see clever use of the @… ecosystem and @… did a cool GNA which is automatically creating GCVE records and structured security advisories from full-disclosure mailing-list or alike:
🔗 Project details #gcve #cve #vulnerability #vulnerability #opensource #cybersecurity
@michabbb@social.vivaldi.net🧹 shadcn/lint by #shadcn is an agent-first linter for #TailwindCSS design systems: write design system rules that #AI coding agents can verify
@adulau@infosec.exchangeWe had difficulties automatically classifying chats, messaging channels, and forums. So we tested several open-weight large language models for our use case. The benchmark is published below, along with a tool supporting the classification process.
This helps us avoid manually classifying channels collected from dark-web forums and social networks, while reliably identifying which channels can be discarded and which deserve further analysis.
🔗 Publication #ai #llm #cybersecurity #darkweb #osint #opensource
@adulau@infosec.exchangeFrom a research paper to running open-source code in just a few days.
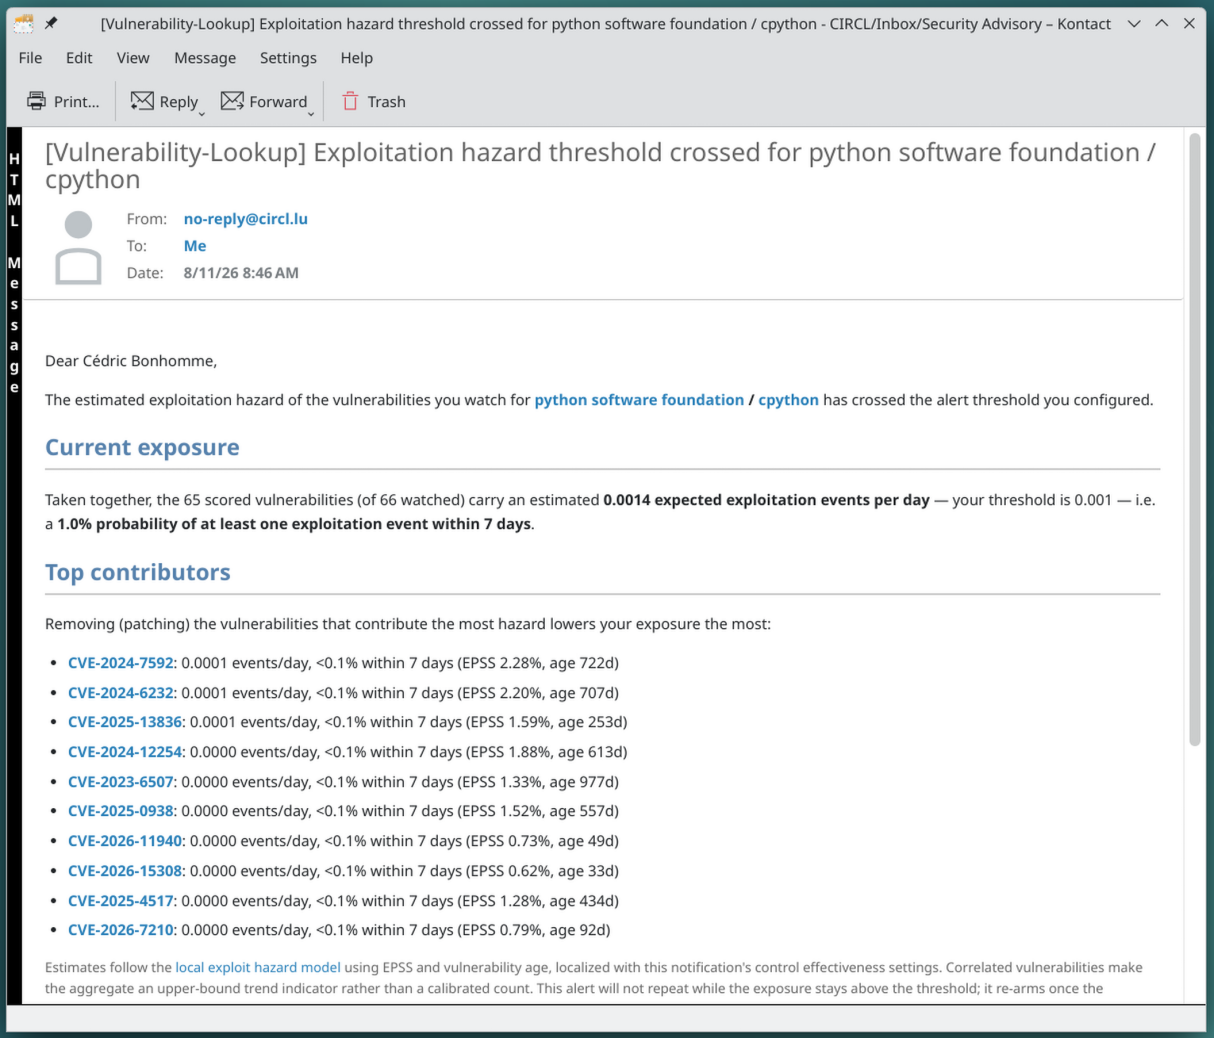
We (with @…) have been experimenting in Vulnerability-Lookup with the concept of Local Exploit Hazard, based on the recent research paper “Modeling Local Exploit Hazard — A Bayesian Framework for Quantifying Exploit Risk and Operational Efficiency” by Stephen Shaffer and Laura Cristiana Voicu.
The idea addresses an important question in vulnerability management:
Not simply “How dangerous is this vulnerability globally?” but “How much exploitation risk does this vulnerability represent in my environment?”
Instead of introducing yet another static vulnerability score, the model starts from exploit likelihood such as EPSS and combines it with local security controls, CVSS attack vectors, vulnerability age and KEV policy to estimate an exploitation hazard.
We implemented an experimental version in Vulnerability-Lookup and connected it directly to operational workflows.
For the full details: #cve #gcve #vulnerabilitymanagement #vulnerability #opensource #opendata
@…
 @michabbb@social.vivaldi.net
🔍 #Hunk is a review-first terminal diff viewer for agent-authored changesets #opensource #git #cli
 @ErikJonker@mastodon.social
The Tax Administration of the Netherlands has decided to move from M365 to opensource and on premis solutions for it's office environment. An important step.
Letter to dutch parliament and news article, in dutch.
#taxadministration #opensource #foss #Microsoft #M365
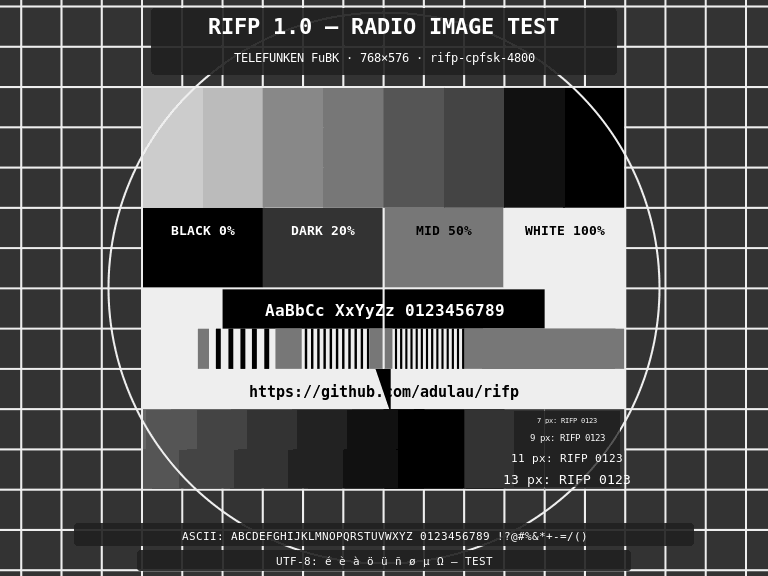
@adulau@infosec.exchangeThe Radio Image Framing Protocol (RIFP) is an experimental, extensible standard for sending images over low-rate radio links. I did a new version 1.1 with an extension to authenticate the images.
The extension is now published as an Internet-Draft.
#rifp #radio #opensource #openstandard
🔗 RIFP source code https://github.com/adulau/rifp#optional-image-authentication
🔗 RIFP Standard https://datatracker.ietf.org/doc/draft-dulaunoy-rifp/
🔗 RFIP Authentication Extension https://datatracker.ietf.org/doc/draft-dulaunoy-rifp-auth/
 @michabbb@social.vivaldi.net
📋 #Archify is an #opensource #AI #agent
 @adulau@infosec.exchange
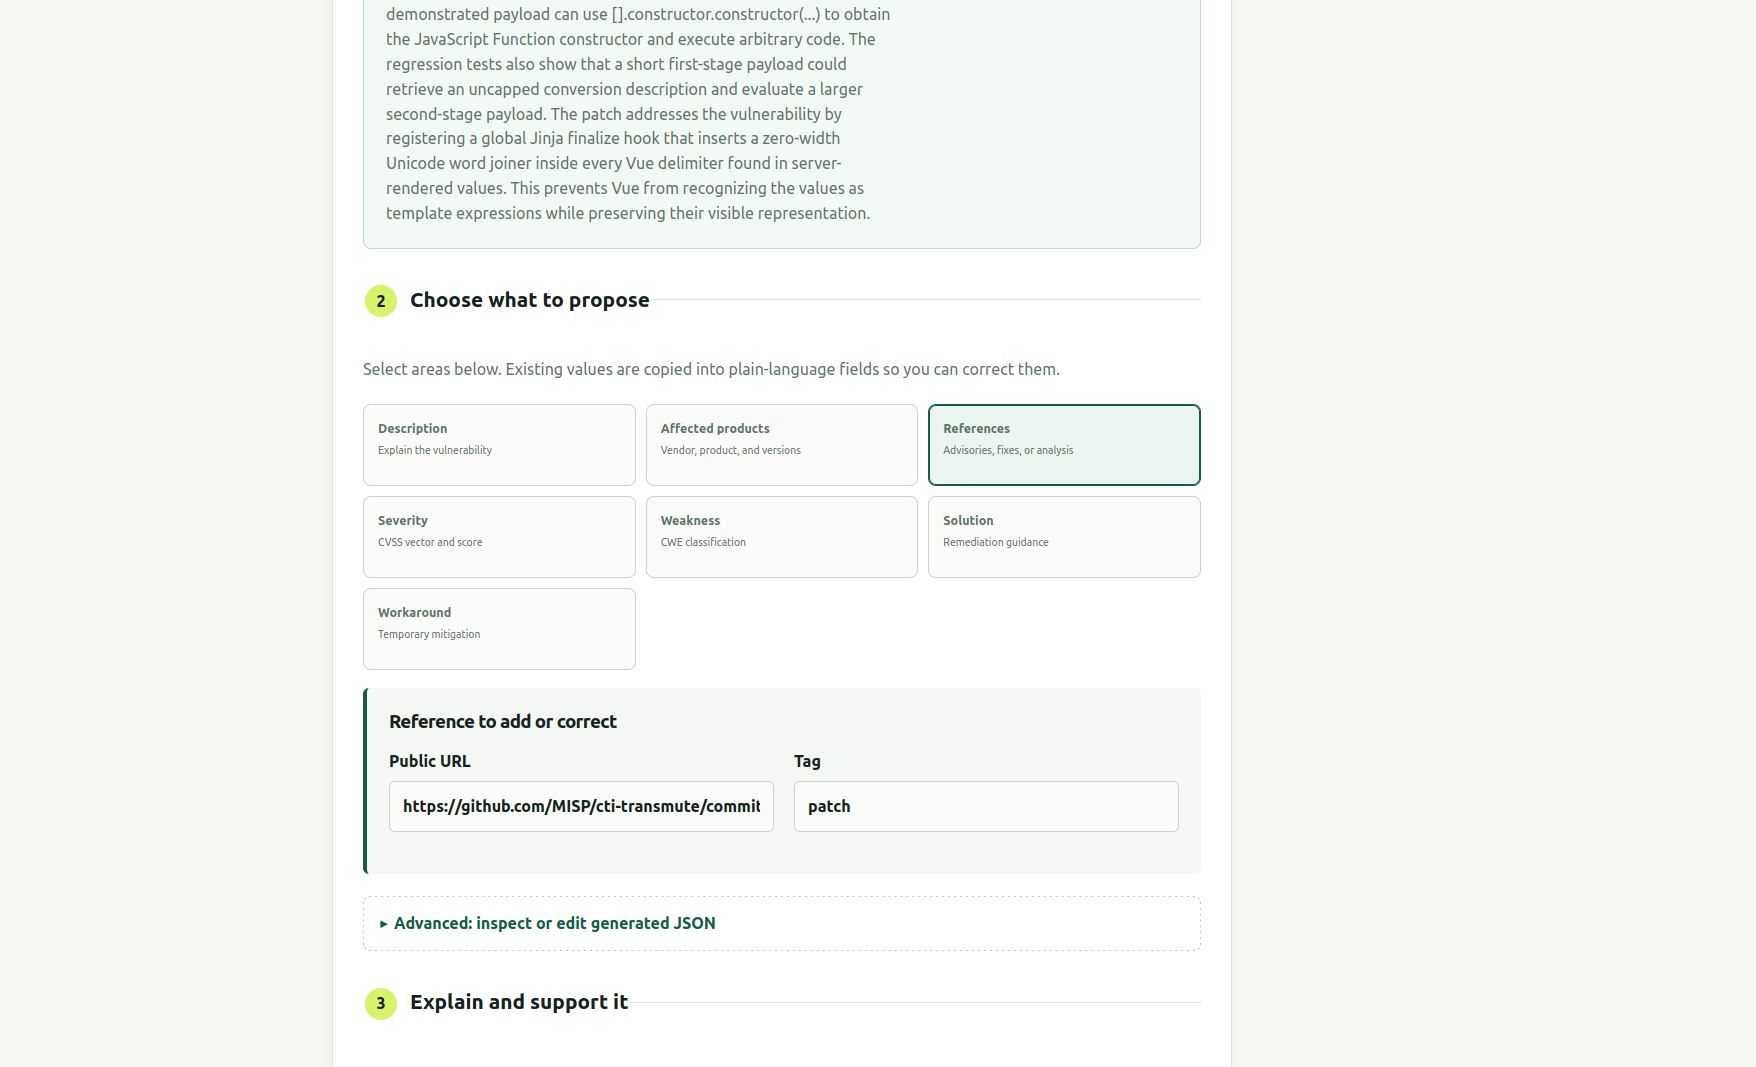
Working on a first super beta implementation of @… BCP-11 "Community-Proposed Updates to Existing CVE Records"
To validate if the BCP-11 can be published.
#cve #gcve #vulnerability #opensource #opendata
Discussions https://discourse.ossbase.org/t/gcve-bcp-11-community-proposed-updates-to-existing-cve-records/1110
 @michabbb@social.vivaldi.net
🔐 #AgentVault is an #opensource HTTP credential proxy and vault from #Infisical that sits between #AIagents
 @michabbb@social.vivaldi.net
📋 #CrabTrap by #Brex is an #opensource HTTP/HTTPS proxy that sits between #AI agents and externa…
 @ErikJonker@mastodon.social
Goed nieuws in deze brief van Stas Eerenberg aan de Tweede Kamer. Hulde aan de @…
#opensource #belastingdienst #onpremis #foss
@michabbb@social.vivaldi.net☁️ #Floci is a free, #opensource local #AWS emulator built with #Quarkus Native — AWS-compatibl…
@michabbb@social.vivaldi.net🎨 Inspo — real production websites your coding agent can study before it writes UI #opensource #MCP #webdev #AI
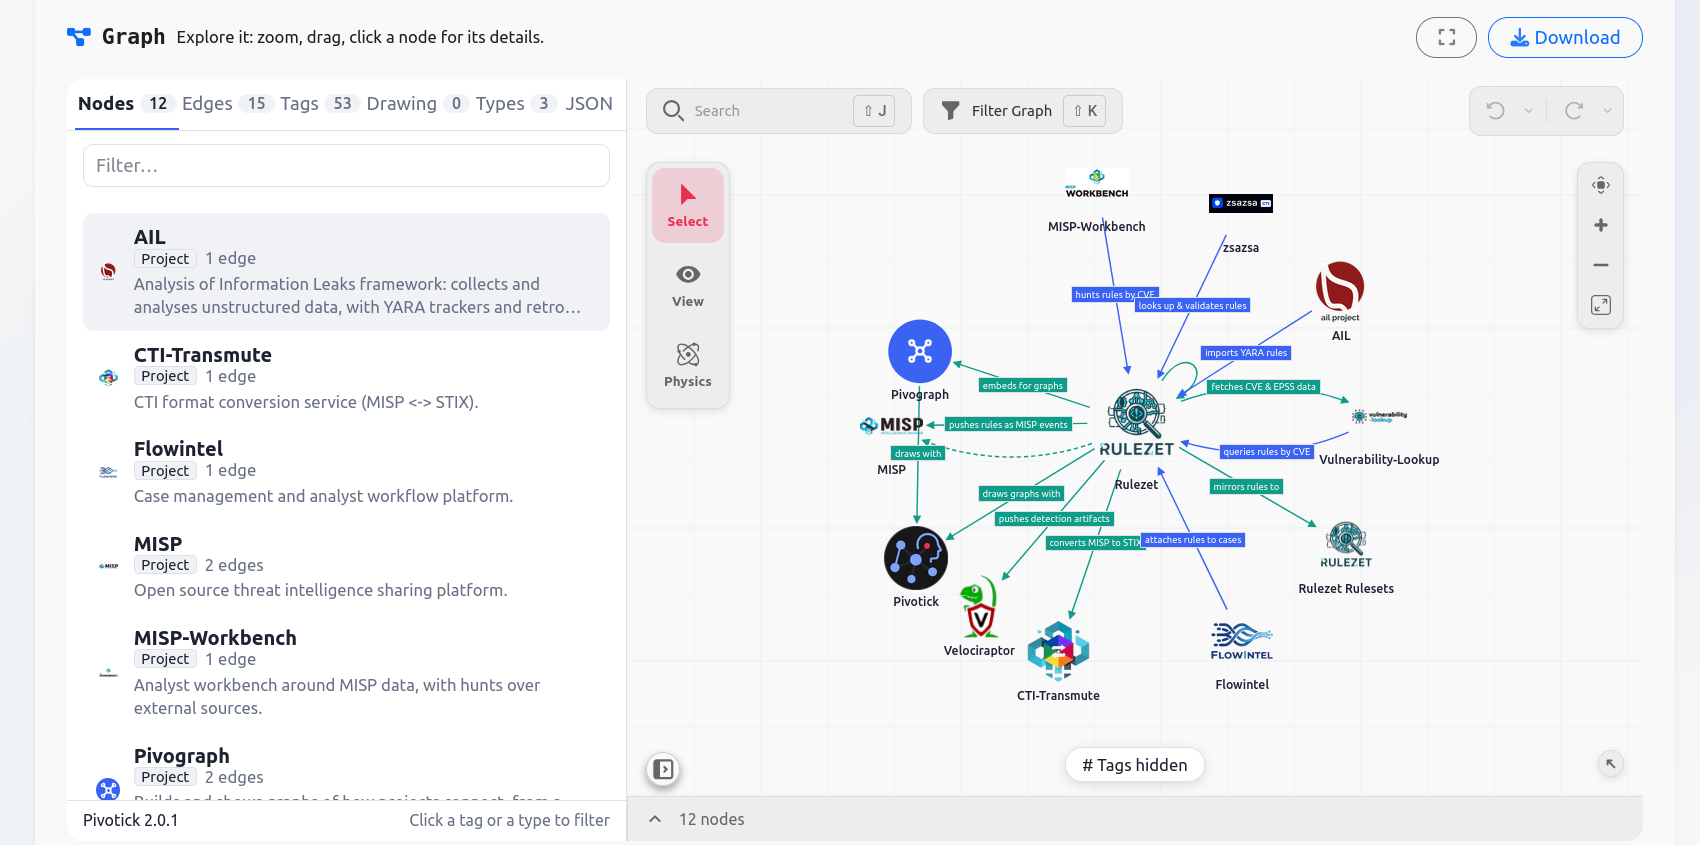
@adulau@infosec.exchangeRulezet and its ecosystem: how detection rules travel between tools.
Vulnerability-Lookup, AIL, Flowintel, MISP, Velociraptor and more: every tool that reads from Rulezet or receives its rules, what each connection does, and an interactive map of the whole ecosystem.
🔗 #threatintelligence #threatintel #rulezet #misp #opensource #cybersecurity #detectionengineering #flowintel #velociraptor #dfir
 @ErikJonker@mastodon.social
Interesting 🤔
#AI #opensource #openweights #china #usa #geopolitics #foss
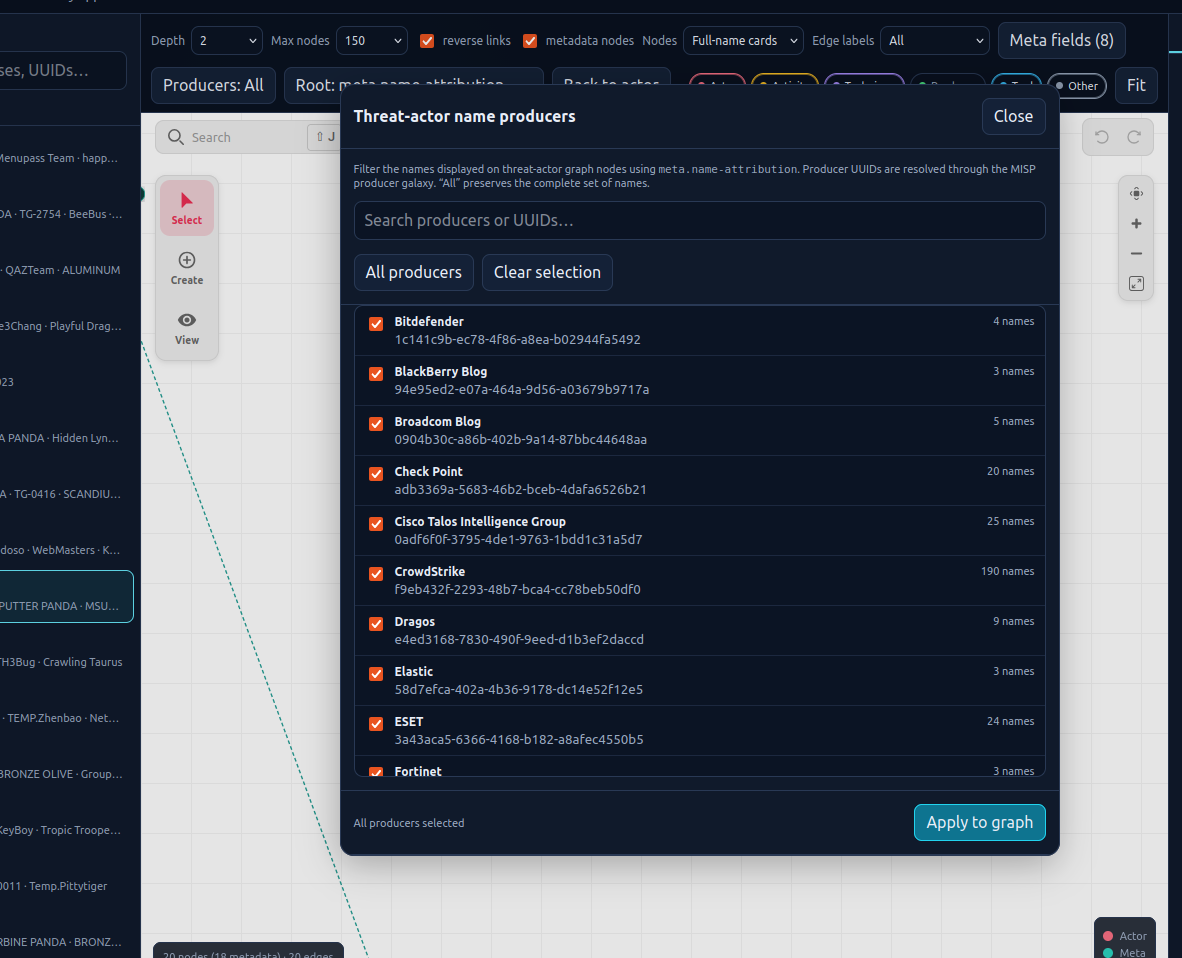
@adulau@infosec.exchangeA standalone, browser-only HTML/JavaScript application for exploring the MISP threat-actor galaxy, UUID-based relationships across every cluster in the MISP Galaxy repository, and shared MISP Galaxy metadata. Graph rendering is performed by Pivotick.
Source code: #misp #cti #threatintelligence #opensource #threatactor #cybersecurity
 @adulau@infosec.exchange
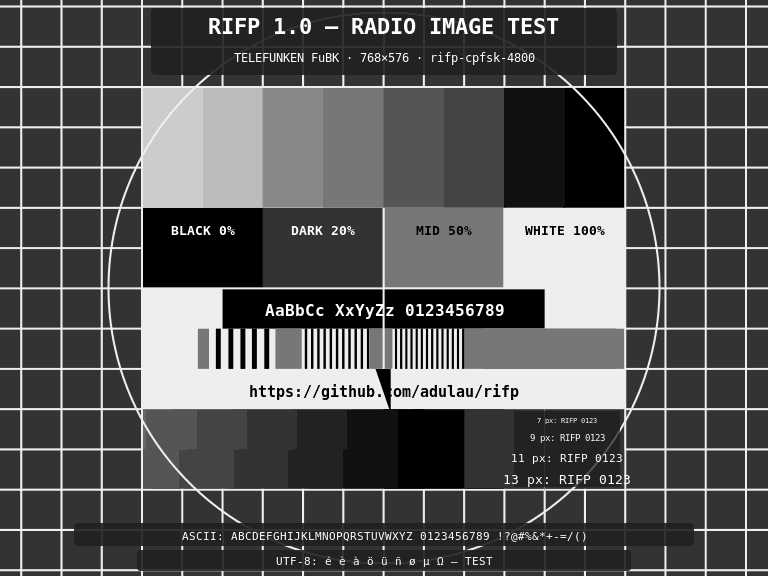
The Radio Image Framing Protocol (RIFP) 1.0 is an experimental, extensible standard for sending images over low-rate radio links.
The default rifp-cpfsk-4800 profile uses binary continuous-phase FSK and can be deployed around 433.92 MHz where local regulation permits it. RIFP itself is not tied to 433 MHz or to FSK and can be used in any frequency bands.
I'm still exploring various low-cost options for a device that can receive and display images on an e-ink screen in emergency areas or similar environments. Python implementation #radio #fax #433mhz #opensource
 @adulau@infosec.exchange
GCVE BCP-07, the Known Exploited Vulnerability (KEV) Assertion Format, has been updated to version 2.2. A key addition is the formalisation of the GCVE KEV Directory, a simple machine-readable directory allowing organisations to announce where their KEV catalogues and exploitation assertions are published.
We particularly encourage software and hardware vendors to publish their own KEV catalogues. Vendors are often in the best position to confirm exploitation affecting their products, and publishing this information in a machine-readable form can significantly improve vulnerability prioritisation for users, CSIRTs and vulnerability-management platforms.
For more details #GCVE #GNA #vulnerabilityintelligence #opensource #KEV #cybersecurity
@…